
CVE-2020-14882
 aleksazatezalo/cve-2020-14882
Exploits Oracle WebLogic Server RCE (CVE-2020-14882) to execute commands on vulnerable targets, capturing output via HTTP listener.
command-and-controlexploitationremote-access-tool+2
aleksazatezalo/cve-2020-14882Exploits Oracle WebLogic Server RCE (CVE-2020-14882) to execute commands on vulnerable targets, capturing output via HTTP listener.
 devengpk/cve-2022-36804
Proof-of-concept exploit for CVE-2022-36804, a command injection vulnerability in Bitbucket Server and Data Center, enabling arbitrary code execution…
 jaysharma786/cve-2021-29003
Proof-of-concept exploit for CVE-2021-29003, a remote code execution vulnerability in Genexis routers, enabling arbitrary command injection via…
 charondefalt/juniper-exploit-cve-2023-36845
Exploit for CVE-2023-36845, a PHP environment variable manipulation vulnerability in Juniper SRX/EX, enabling unauthenticated remote code execution…
 redsiege/c2concealer
Generates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…
 threatexpress/cs2modrewrite
Convert Cobalt Strike profiles to modrewrite scripts
 3v4si0n/http-revshell
Powershell reverse shell using HTTP/S protocol with AMSI bypass and Proxy Aware
 gr1mmie/atlasc2
C# C2 Framework centered around Stage 1 operations
 abhishekkr/n00brat
Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service
 taherio/redi
Automated script for setting up CobaltStrike redirectors (nginx reverse proxy, letsencrypt)
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
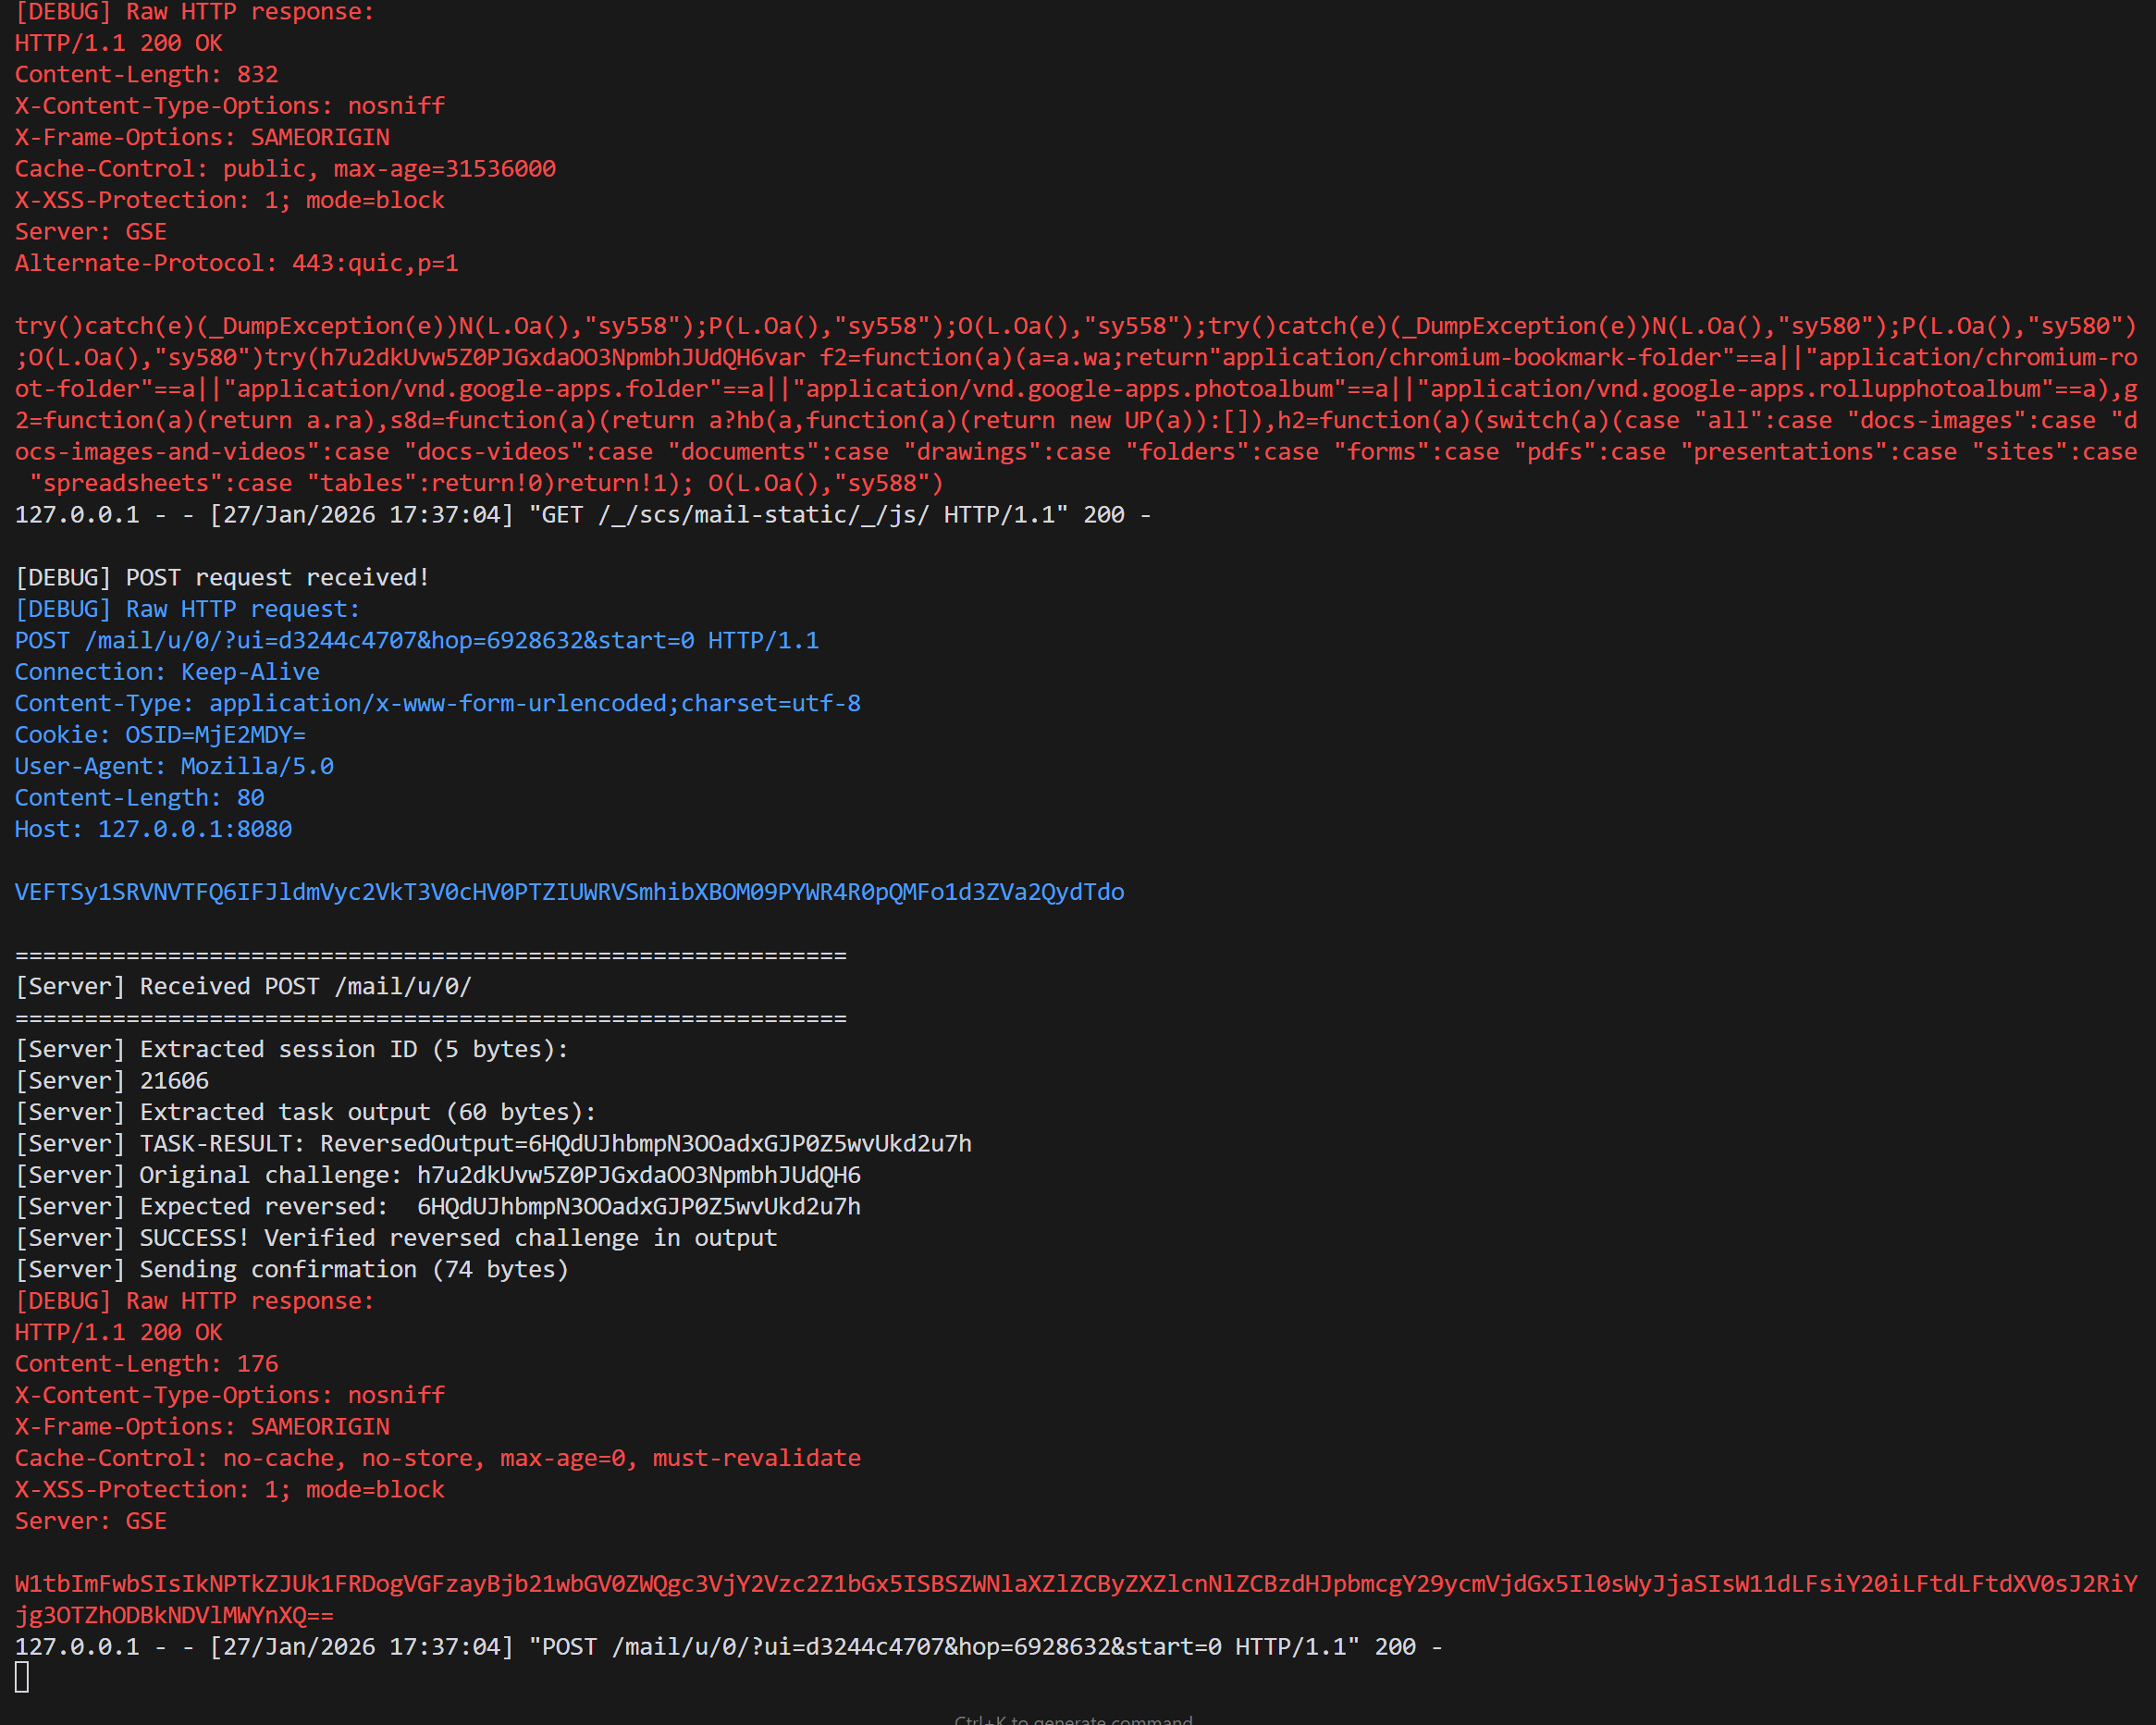 codextf2/openmalleablec2
Open Source Implementation of Cobalt Strike's Malleable C2

 smokeintheshell/cve-2023-20198
CVE-2023-20198 Exploit PoC
 cj1324/cgishell
shellshock CVE-2014-6271 CGI Exploit, Use like Openssh via CGI
 thestingr/cve-2025-25257
Public PoC for CVE-2025-25257: FortiWeb pre-auth SQLi to RCE
 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
 g4sul1n/cisco-ios-xe-cve-2023-20198
Exploit PoC for CVE-2023-20198