

XeytanWxCpp-RAT
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets
command-and-controlinformation-gatheringpayload-development+3
11
melardev/xeytanwxcpp-ratWork in Progress. RAT written in C++ using wxWidgets
 tahmed11/strutsy
Strutsy - Mass exploitation of Apache Struts (CVE-2017-5638) vulnerability
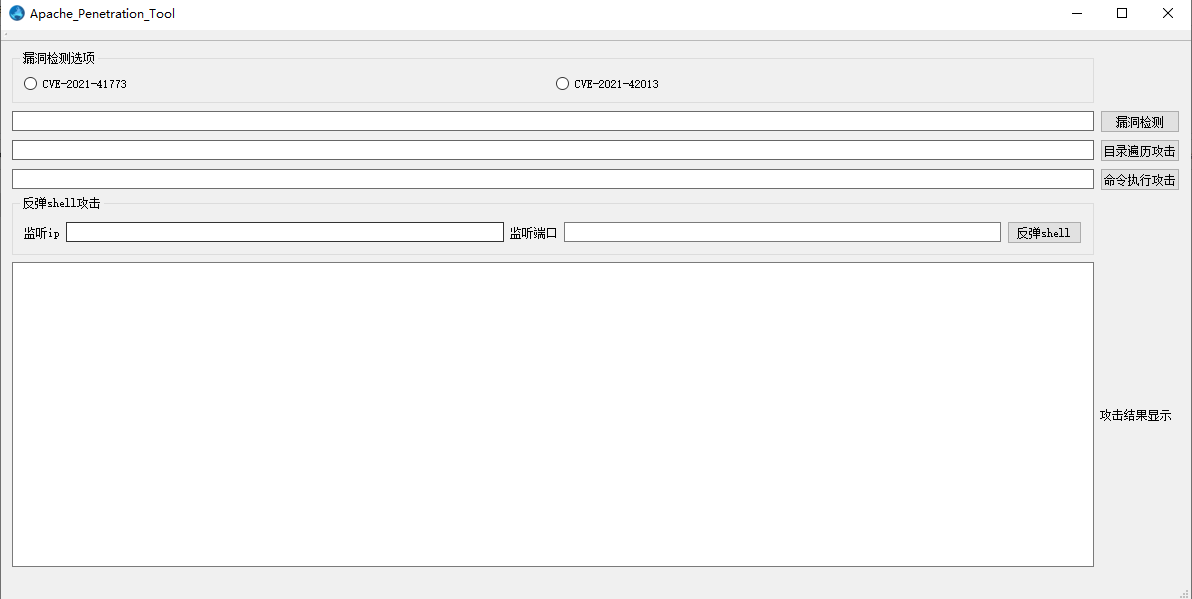 wangfly-me/apache_penetration_tool
CVE-2021-41773&CVE-2021-42013图形化漏洞检测利用工具
 xuemian168/cve-2025-3248
A vulnerability scanner for CVE-2025-3248 in Langflow applications. 用于扫描 Langflow 应用中 CVE-2025-3248 漏洞的工具。
 coldfusionx/cve-2022-36804
Atlassian Bitbucket Server and Data Center - Command Injection Vulnerability (CVE-2022-36804)
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 rix4uni/cve-2025-55182
A command-line tool for detecting CVE-2025-55182 and CVE-2025-66478 in Next.js applications using React Server Components.
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
 shinthink/solrradar
☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE

 yukibtc/redknife
A Swiss Army knife for offensive security.
 grampae/mqxss
Hooked browser communication over MQTT
 gmh5225/github-gato
GitHub Self-Hosted Runner Enumeration and Attack Tool
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…