

CVE-2024-41570-Havoc-C2-RCE
 leo-mitch/cve-2024-41570-havoc-c2-rce
This is a Chained RCE in the Havoc C2 framework using github.com/chebuya and github.com/IncludeSecurity pocs
command-and-controlexploitationpenetration-testing+3
3
leo-mitch/cve-2024-41570-havoc-c2-rceThis is a Chained RCE in the Havoc C2 framework using github.com/chebuya and github.com/IncludeSecurity pocs
 fkasler/dolos_cloak
Automated 802.1x Bypass
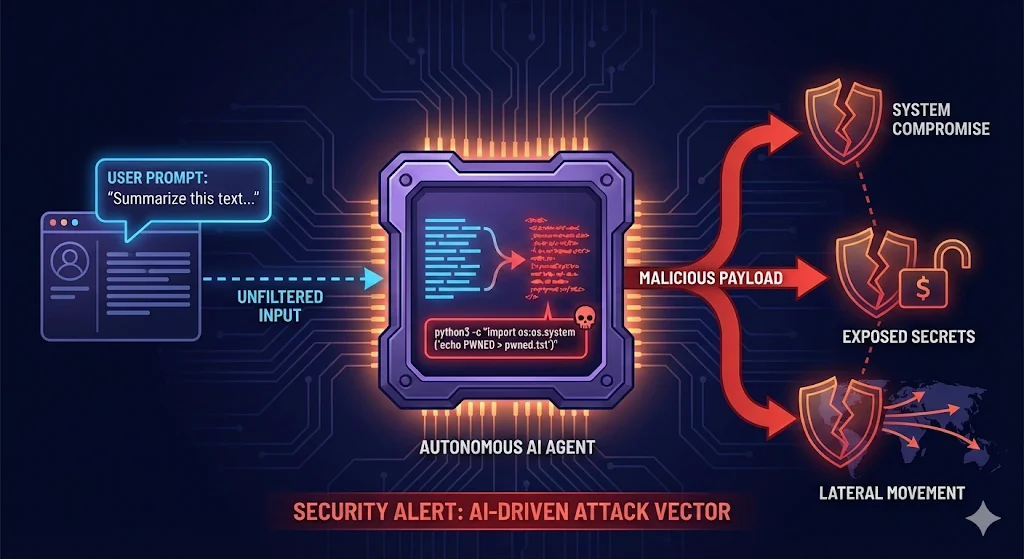 itamar-yochpaz/cve-2026-2256-poc
Proof-of-concept demonstrating a command injection vulnerability in MS-Agent Shell tool, enabling arbitrary command execution and reverse shell via…
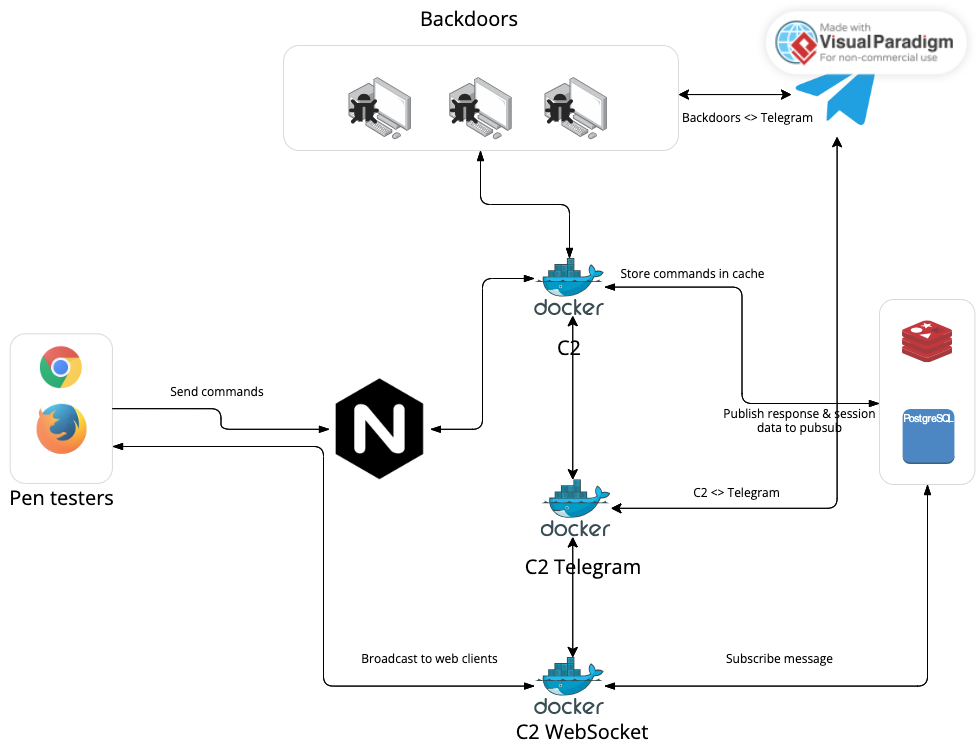 govindasamyarun/c2-cloud
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…
 a-d-team/sharpmemshell
.NET in-memory webshell (memshell) payloads implemented via HttpListener and VirtualPath, compatible with the Godzilla 4.01 post-exploitation…
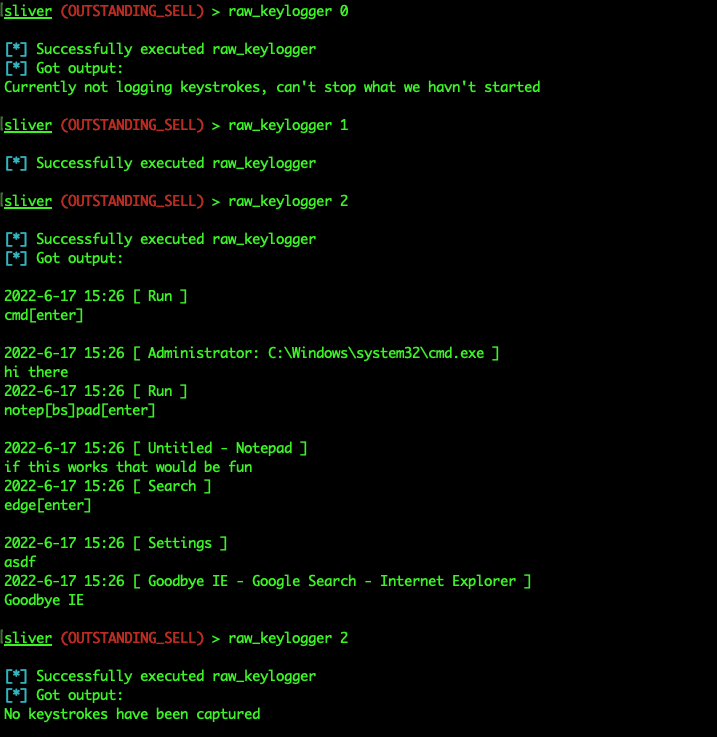 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
 mitre/caldera-crater
C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
 byt3bl33d3r/mitmf
Framework for Man-In-The-Middle attacks
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 empireproject/empire-gui
Empire client application
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 0xtriboulet/revenant
Revenant - A 3rd party agent for Havoc that demonstrates evasion techniques in the context of a C2 framework
 cobbr/covenant
Covenant is a collaborative .NET C2 framework for red teamers.
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
 sastraadiwiguna-purpleeliteteaming/ddos-purple-teaming-offensive-multi-vector-7-tier-defensive-holistic-blueprint-
Replicable Blueprint for advanced DDoS Purple Teaming, engineered for the threat landscape. It integrates a Red Elite Teaming offensive…
 mr-wolf-gb/d-rat_vb.net_mysql_php
D-RAT [VB.NET]+[MySQL]+[PHP]