
CVE-2022-39197
 its-arun/cve-2022-39197
Proof-of-concept exploit for CVE-2022-39197, enabling remote code execution against CobaltStrike <= 4.7.1 via malicious SVG payload served over HTTP.
command-and-controlexploitationpayload-development+3
385
its-arun/cve-2022-39197Proof-of-concept exploit for CVE-2022-39197, enabling remote code execution against CobaltStrike <= 4.7.1 via malicious SVG payload served over HTTP.
 h4x0r-dz/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, a Palo Alto OS command injection in GlobalProtect VPN. Demonstrates file creation and outbound command…
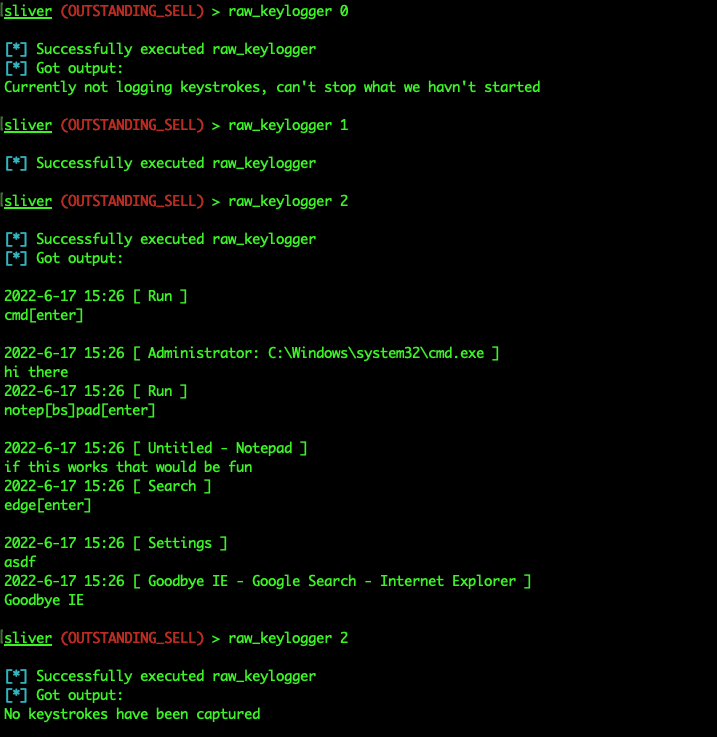 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
 mackleadmire/cve-2018-3191-rce-exploit
Exploit for CVE-2018-3191 targeting Oracle WebLogic servers. Generates a malicious payload via RMI, deploys reverse shell classes on an HTTP server,…
 nanowraith/cve-2024-29973
Proof-of-concept exploit for CVE-2024-29973, a command injection vulnerability in Zyxel NAS devices. Executes arbitrary OS commands via a crafted…
 ludy-dev/weblogic_unauthorized-bypass-rce
Python-based exploit script for Oracle WebLogic CVE-2020-14882 unauthorized bypass RCE. Tests authentication bypass and remote code execution via…
 ianxtianxt/cve-2019-16278
Python exploit script for CVE-2019-16278, a remote command execution vulnerability in Nostromo httpd. Executes arbitrary commands on vulnerable…
 cyy95/cve-2019-0232-exp
Exploit for Apache Tomcat CGI Servlet command injection (CVE-2019-0232) enabling remote code execution via crafted HTTP requests on affected versions.
 y000o/confluence-cve-2022-26134
Proof-of-concept exploit for CVE-2022-26134 in Confluence Server, using OGNL injection to execute commands via crafted HTTP requests.
 yifanzhg/cve-2023-45158
Proof-of-concept exploit for CVE-2023-45158, a command injection vulnerability in web2py. Demonstrates remote code execution via crafted HTTP…
 iveresk/cve-2022-30525
Proof-of-concept exploit for CVE-2022-30525 enabling unauthenticated remote command injection on Zyxel firewalls via HTTP POST requests to the…
 aerchy/cve-2024-29973
Proof-of-concept exploit for CVE-2024-29973, a remote command injection in Zyxel NAS devices, demonstrating arbitrary command execution via crafted…
 naozibuhao/cve-2026-21962_java_gui_exploit_tool
Java GUI tool for exploiting CVE-2026-21962, an unauthenticated RCE in Oracle WebLogic Proxy Plug-In, enabling multi-target command execution via…
 afifudinmtop/mcpjam-inspector-1.4.2-remote-code-execution-cve-2026-23744
Python exploit for CVE-2026-23744 in MCPJam Inspector 1.4.2, enabling remote code execution via reverse shell on target HTTP servers.
 fzbacon/cve-2023-27216_d-link_dsl-3782_router_command_injection
Proof-of-concept exploit for CVE-2023-27216, a command injection vulnerability in D-Link DSL-3782 routers, enabling remote code execution via crafted…
 mbanyamer/cve-2026-22553-insat-masterscada-buk-ts-mmadmserv
Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…
 jackalkarlos/cve-2024-46658
Proof-of-concept exploit for a command injection vulnerability in Syrotech SY-GOPON-8OLT-L3, allowing arbitrary command execution via HTTP request…