
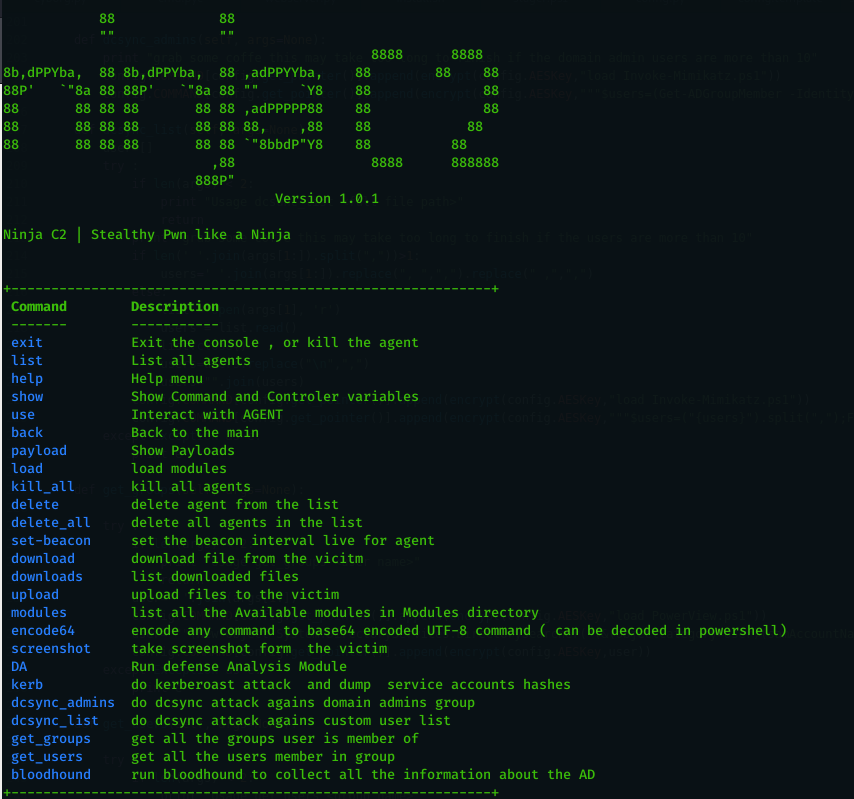
Ninja
 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
command-and-controlexploitationinformation-gathering+6
ahmedkhlief/ninjaOpen source C2 server created for stealth red team operations
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 m8sec/activereign
A Network Enumeration and Attack Toolset for Windows Active Directory Environments.
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
 woj-ciech/daily-dose-of-malware
Script lets you gather malicious software and c&c servers from open source platforms like Malshare, Malcode, Google, Cymon - vxvault, cybercrime…
 ajinabraham/xenotix-xbot
Xenotix xBOT is a Cross Platform PoC Bot that abuse certain Google Services to implement it's C&C
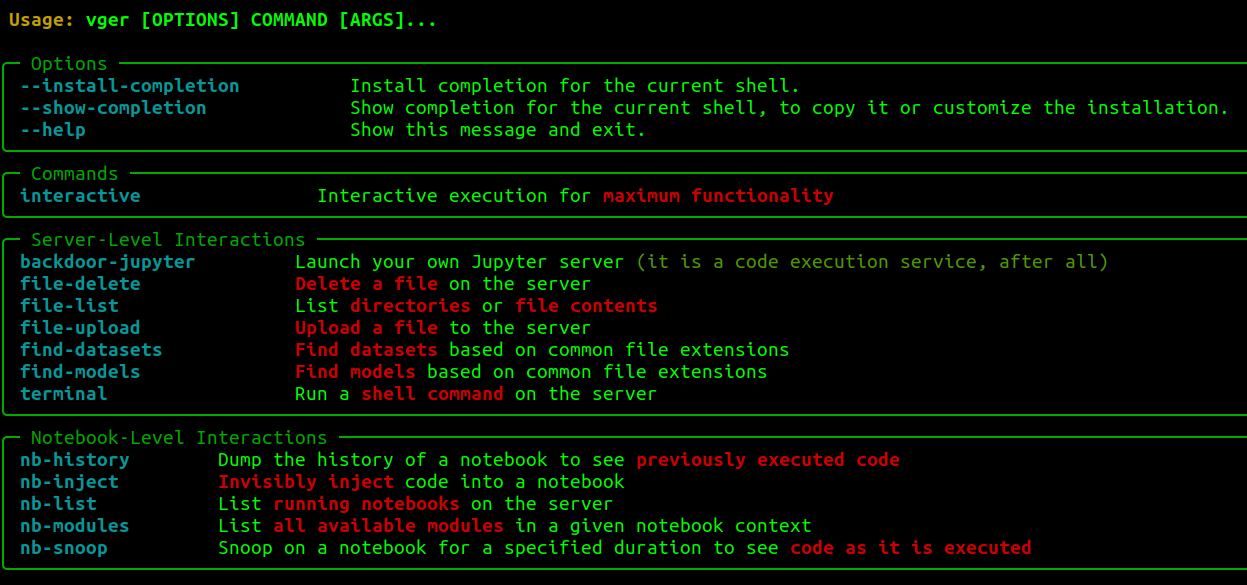 josephtlucas/vger
An interactive CLI application for interacting with authenticated Jupyter instances.
 bigb0x/cve-2024-29973
POC for CVE-2024-29973
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets
 coldfusionx/cve-2022-36804
Atlassian Bitbucket Server and Data Center - Command Injection Vulnerability (CVE-2022-36804)
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
 joelczk/cve-2025-52688
Proof-of-concept exploits for CVE-2025-52688: unauthenticated command injection and arbitrary file read vulnerabilities in Alcatel AP13161 enterprise…
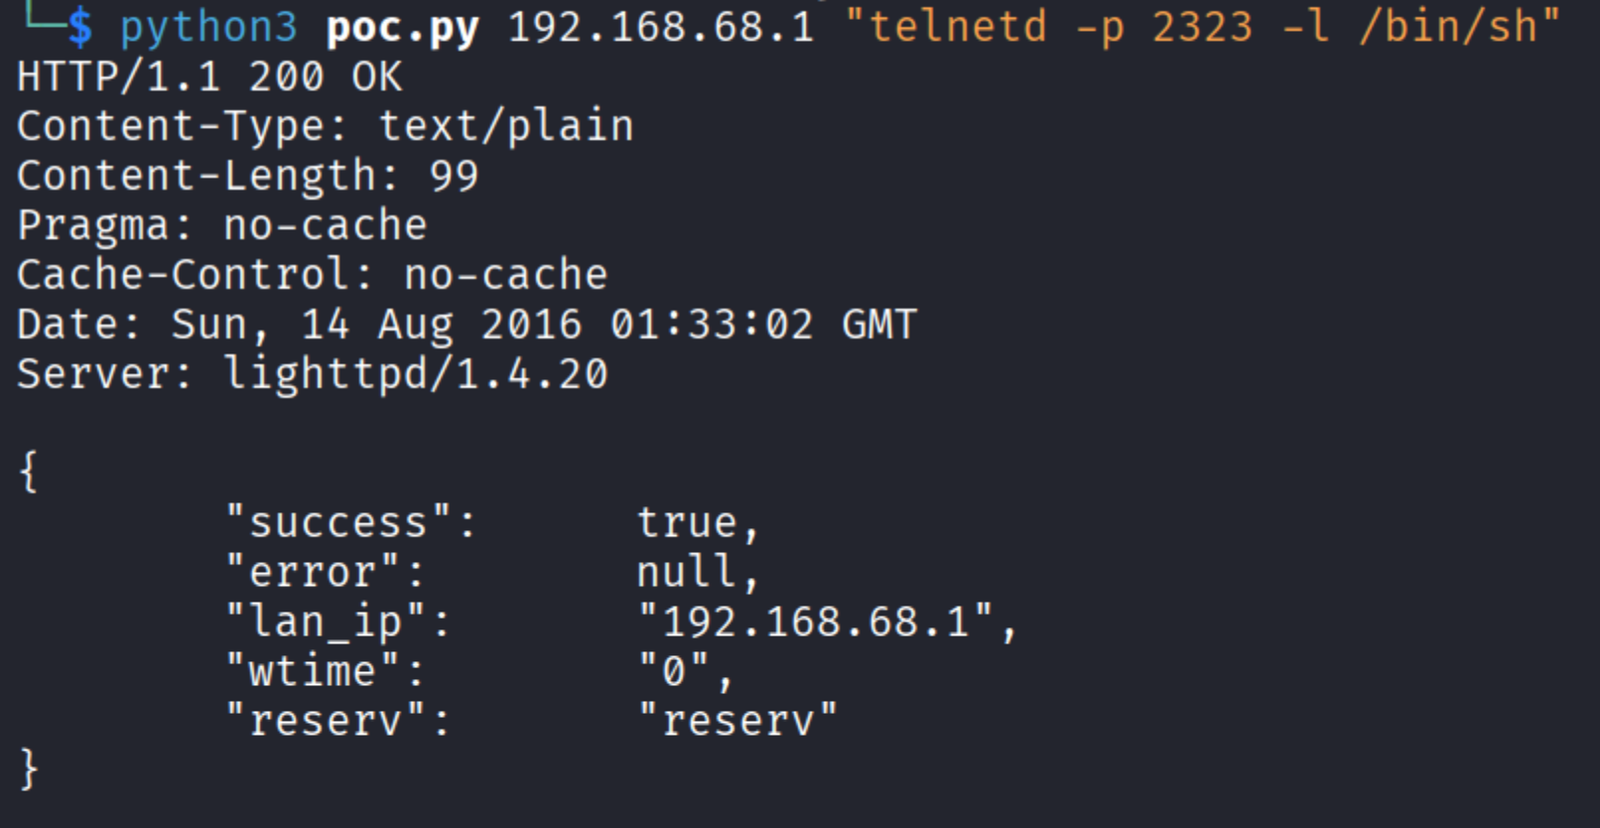 finnvle/cve-2022-28906-poc
Python proof-of-concept for unauthenticated OS command injection in TOTOLINK N600R, exploiting the langType parameter to execute arbitrary commands…
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
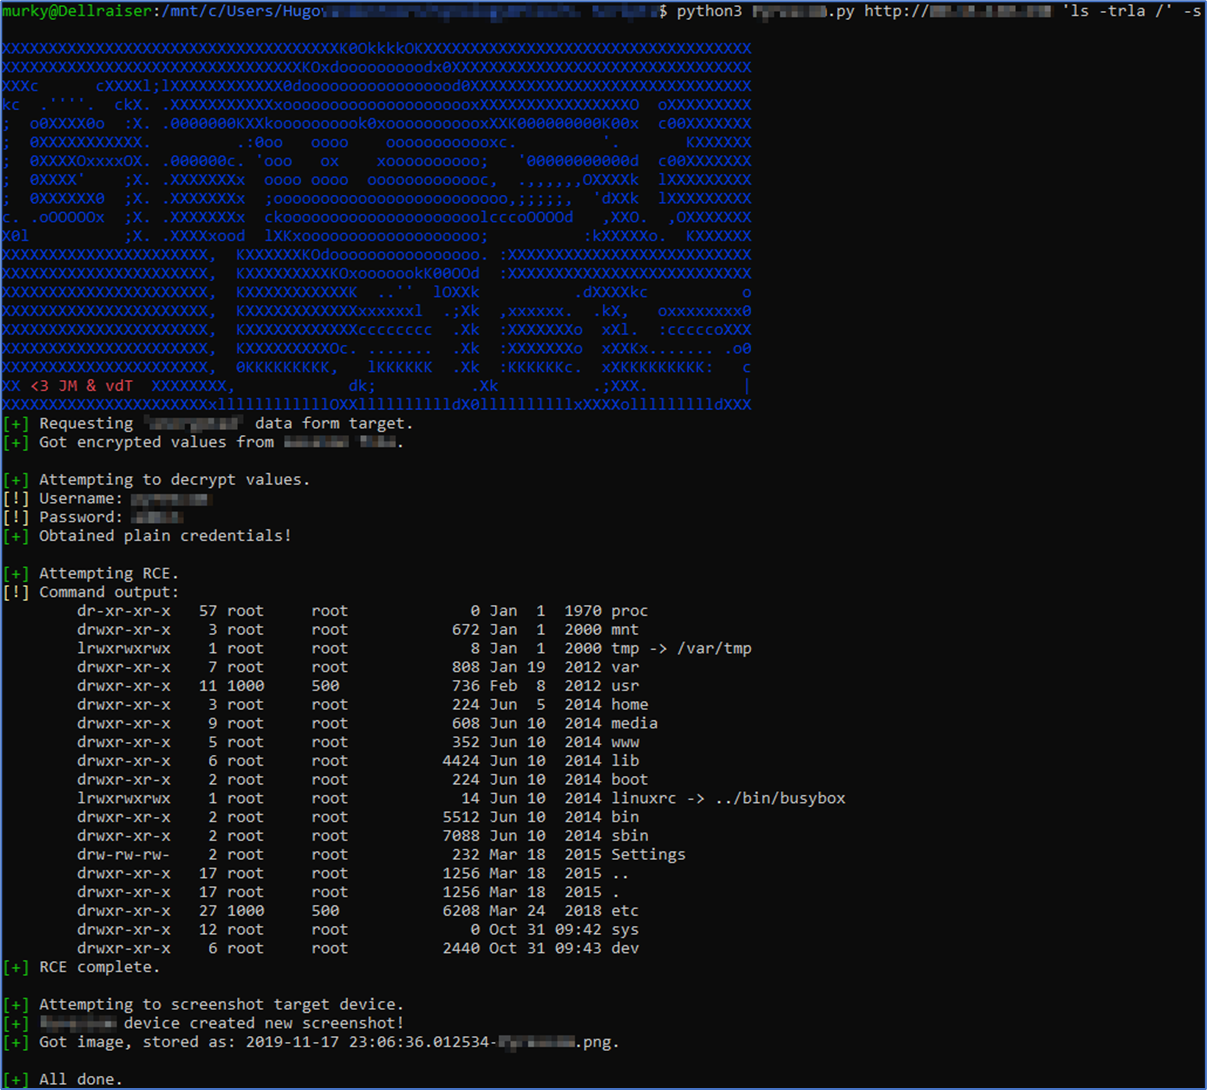 outpost24/pyrescom-termod-poc
Pyrescom Termod proof-of-concept code for CVE-2020-23160, CVE-2020-23161 and CVE-2020-23162
 byt3bl33d3r/crackmapexec
A swiss army knife for pentesting networks
 gmh5225/github-gato
GitHub Self-Hosted Runner Enumeration and Attack Tool
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…