Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
56 results
CVE-2022-36804-PoC-Exploit preview

CVE-2022-36804-PoC-Exploit

GitHubbenjaminhays/cve-2022-36804-poc-exploit

Somewhat Reliable PoC Exploit for CVE-2022-36804 (BitBucket Critical Command Injection)

command-and-controlexploitationpenetration-testing+3
16
2 years ago
CVE-2024-29895-CactiRCE-PoC preview

CVE-2024-29895-CactiRCE-PoC

GitHubstuub/cve-2024-29895-cactirce-poc

CVE-2024-29895 PoC - Exploiting remote command execution in Cacti servers using the 1.3.X DEV branch builds
command-and-controlexploitationpenetration-testing+3
212 years ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
command-and-controlcryptographydigital-forensics+7
1029 days ago
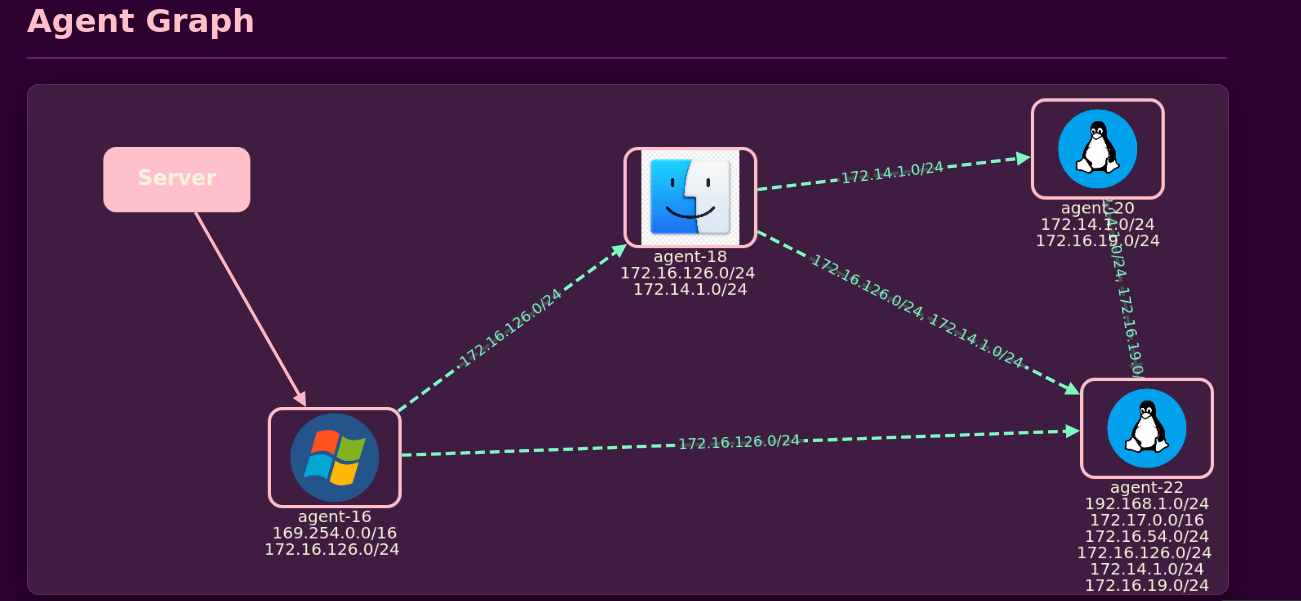
rosemary preview

rosemary

GitHubblue0x1/rosemary

Rosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.
command-and-controldns-analysislateral-movement+4
142 months ago
ls-poc preview

ls-poc

GitHubtruekas/ls-poc

Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.
command-and-controlexploitationpayload-development+3
125 months ago
waybend preview

waybend

GitHubprinciplebreach/waybend

Self-hosted SSRF redirect, payload, callback, and DNS workbench
command-and-controldns-analysisinformation-gathering+9
528 days ago
CVE-2017-5638 preview

CVE-2017-5638

GitHubpayatu/cve-2017-5638

Apache Struts 2.0 RCE vulnerability - Allows an attacker to inject OS commands into a web application through the content-type header
command-and-controlexploitationpenetration-testing+3
89 years ago
CVE-2022-22954 preview

CVE-2022-22954

GitHubb4dboy17/cve-2022-22954

VMware Workspace ONE Access and Identity Manager RCE via SSTI. CVE-2022-22954 - PoC SSTI * exploit+payload+shodan (ну набором)
command-and-controlexploitationreconnaissance+2
54 years ago
CVE-2025-4428 preview

CVE-2025-4428

GitHubxie-22/cve-2025-4428

Ivanti EPMM Pre-Auth RCE Chain

command-and-controlexploitationpenetration-testing+3
40 years ago
Confluence-CVE-2022-26134 preview

Confluence-CVE-2022-26134

GitHuby000o/confluence-cve-2022-26134

Proof-of-concept exploit for CVE-2022-26134 in Confluence Server, using OGNL injection to execute commands via crafted HTTP requests.
command-and-controlexploitationreconnaissance+2
44 years ago
CVE-2025-24893-XWiki-RCE preview

CVE-2025-24893-XWiki-RCE

GitHubhex00-0x4/cve-2025-24893-xwiki-rce

This vulnerability could allow a malicious user to execute remote code by sending appropriately crafted requests to the default search engine…
command-and-controlexploitationpenetration-testing+3
61 year ago
CVE-2026-33017 preview

CVE-2026-33017

GitHubmaxprog-svg/cve-2026-33017

CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
command-and-controlexploitationreconnaissance+3
1 month ago
CVE-2020-7961-Mass preview

CVE-2020-7961-Mass

GitHubcrackercat/cve-2020-7961-mass

CVE-2020–7961 Mass exploit for Script Kiddies
command-and-controlexploitationreconnaissance+2
25 years ago
cupntlm-Automated-Exploit-For-CVE-2025-33073- preview

cupntlm-Automated-Exploit-For-CVE-2025-33073-

GitHubegcupcake/cupntlm-automated-exploit-for-cve-2025-33073-

cupntlm
authenticationcommand-and-controldns-analysis+9
36 months ago
CVE-2022-1388 preview

CVE-2022-1388

GitHubdevengpk/cve-2022-1388

Exploit and mass-check script for CVE-2022-1388 targeting F5 BIG-IP iControl REST unauthenticated remote command execution. Supports single host,…
command-and-controlexploitationpenetration-testing+3
23 years ago
CVE-2024-36401_Geoserver_RCE_POC preview

CVE-2024-36401_Geoserver_RCE_POC

GitHubamoy6228/cve-2024-36401_geoserver_rce_poc

本脚本是针对 GeoServer 的远程代码执行漏洞(CVE-2024-36401)开发的 PoC(Proof of Concept)探测工具。该漏洞允许攻击者通过构造特定请求,在目标服务器上执行任意命令。
command-and-controlexploitationpenetration-testing+3
21 year ago
CVE-2025-3248 preview

CVE-2025-3248

GitHubimbas007/cve-2025-3248

Python-based exploit for CVE-2025-3248 enabling remote code execution on vulnerable Langflow instances. Supports single URL and bulk scanning with…
command-and-controlexploitationpenetration-testing+3
21 year ago
POC_CVE-2026-41940 preview

POC_CVE-2026-41940

GitHubimbas007/poc_cve-2026-41940

Proof-of-concept exploit for CVE-2026-41940 targeting cPanel, enabling account enumeration, command execution, and interactive shell access on…

command-and-controlexploitationpenetration-testing+3
5 months ago
Previous1234Next