
JS-Tap
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
command-and-controldata-exfiltrationinformation-gathering+8
482
hoodoer/js-tapJavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
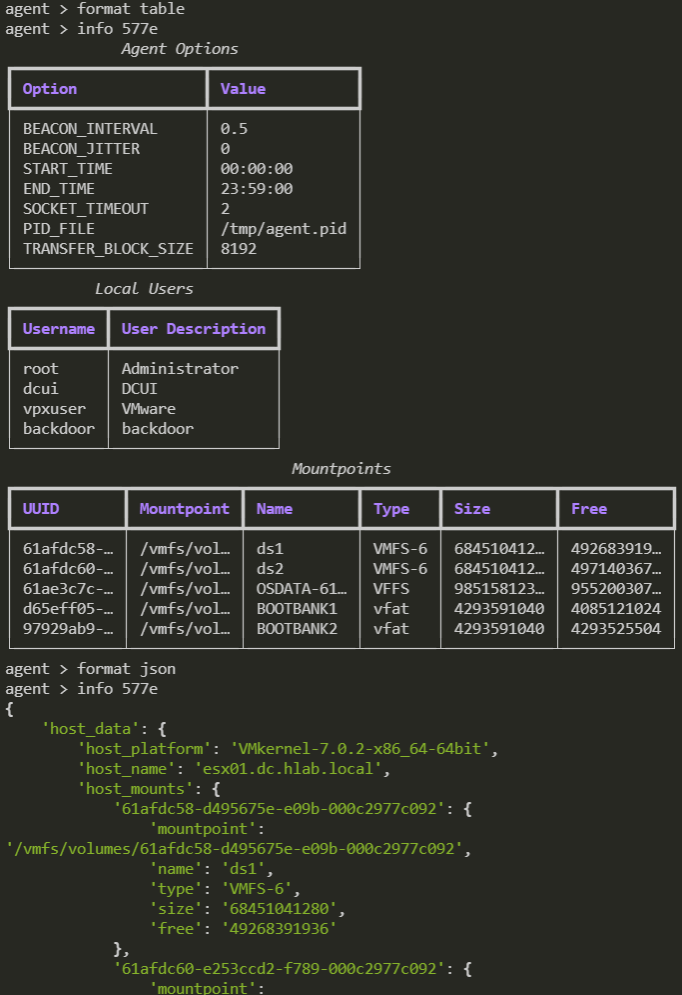 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
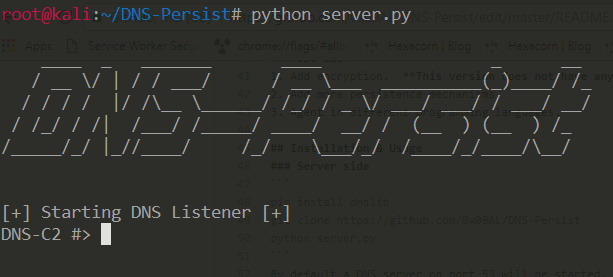 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 cys3c/evilosx
A pure python, post-exploitation, remote administration tool (RAT) for macOS / OS X.
 evillm/cve-2025-49113-poc
Post-authentication remote code execution proof-of-concept for CVE-2025-49113 in Roundcube webmail. Includes a vulnerable Docker environment and…
 0x09al/dropboxc2c
DropboxC2C is a post-exploitation agent which uses Dropbox Infrastructure for command and control operations.
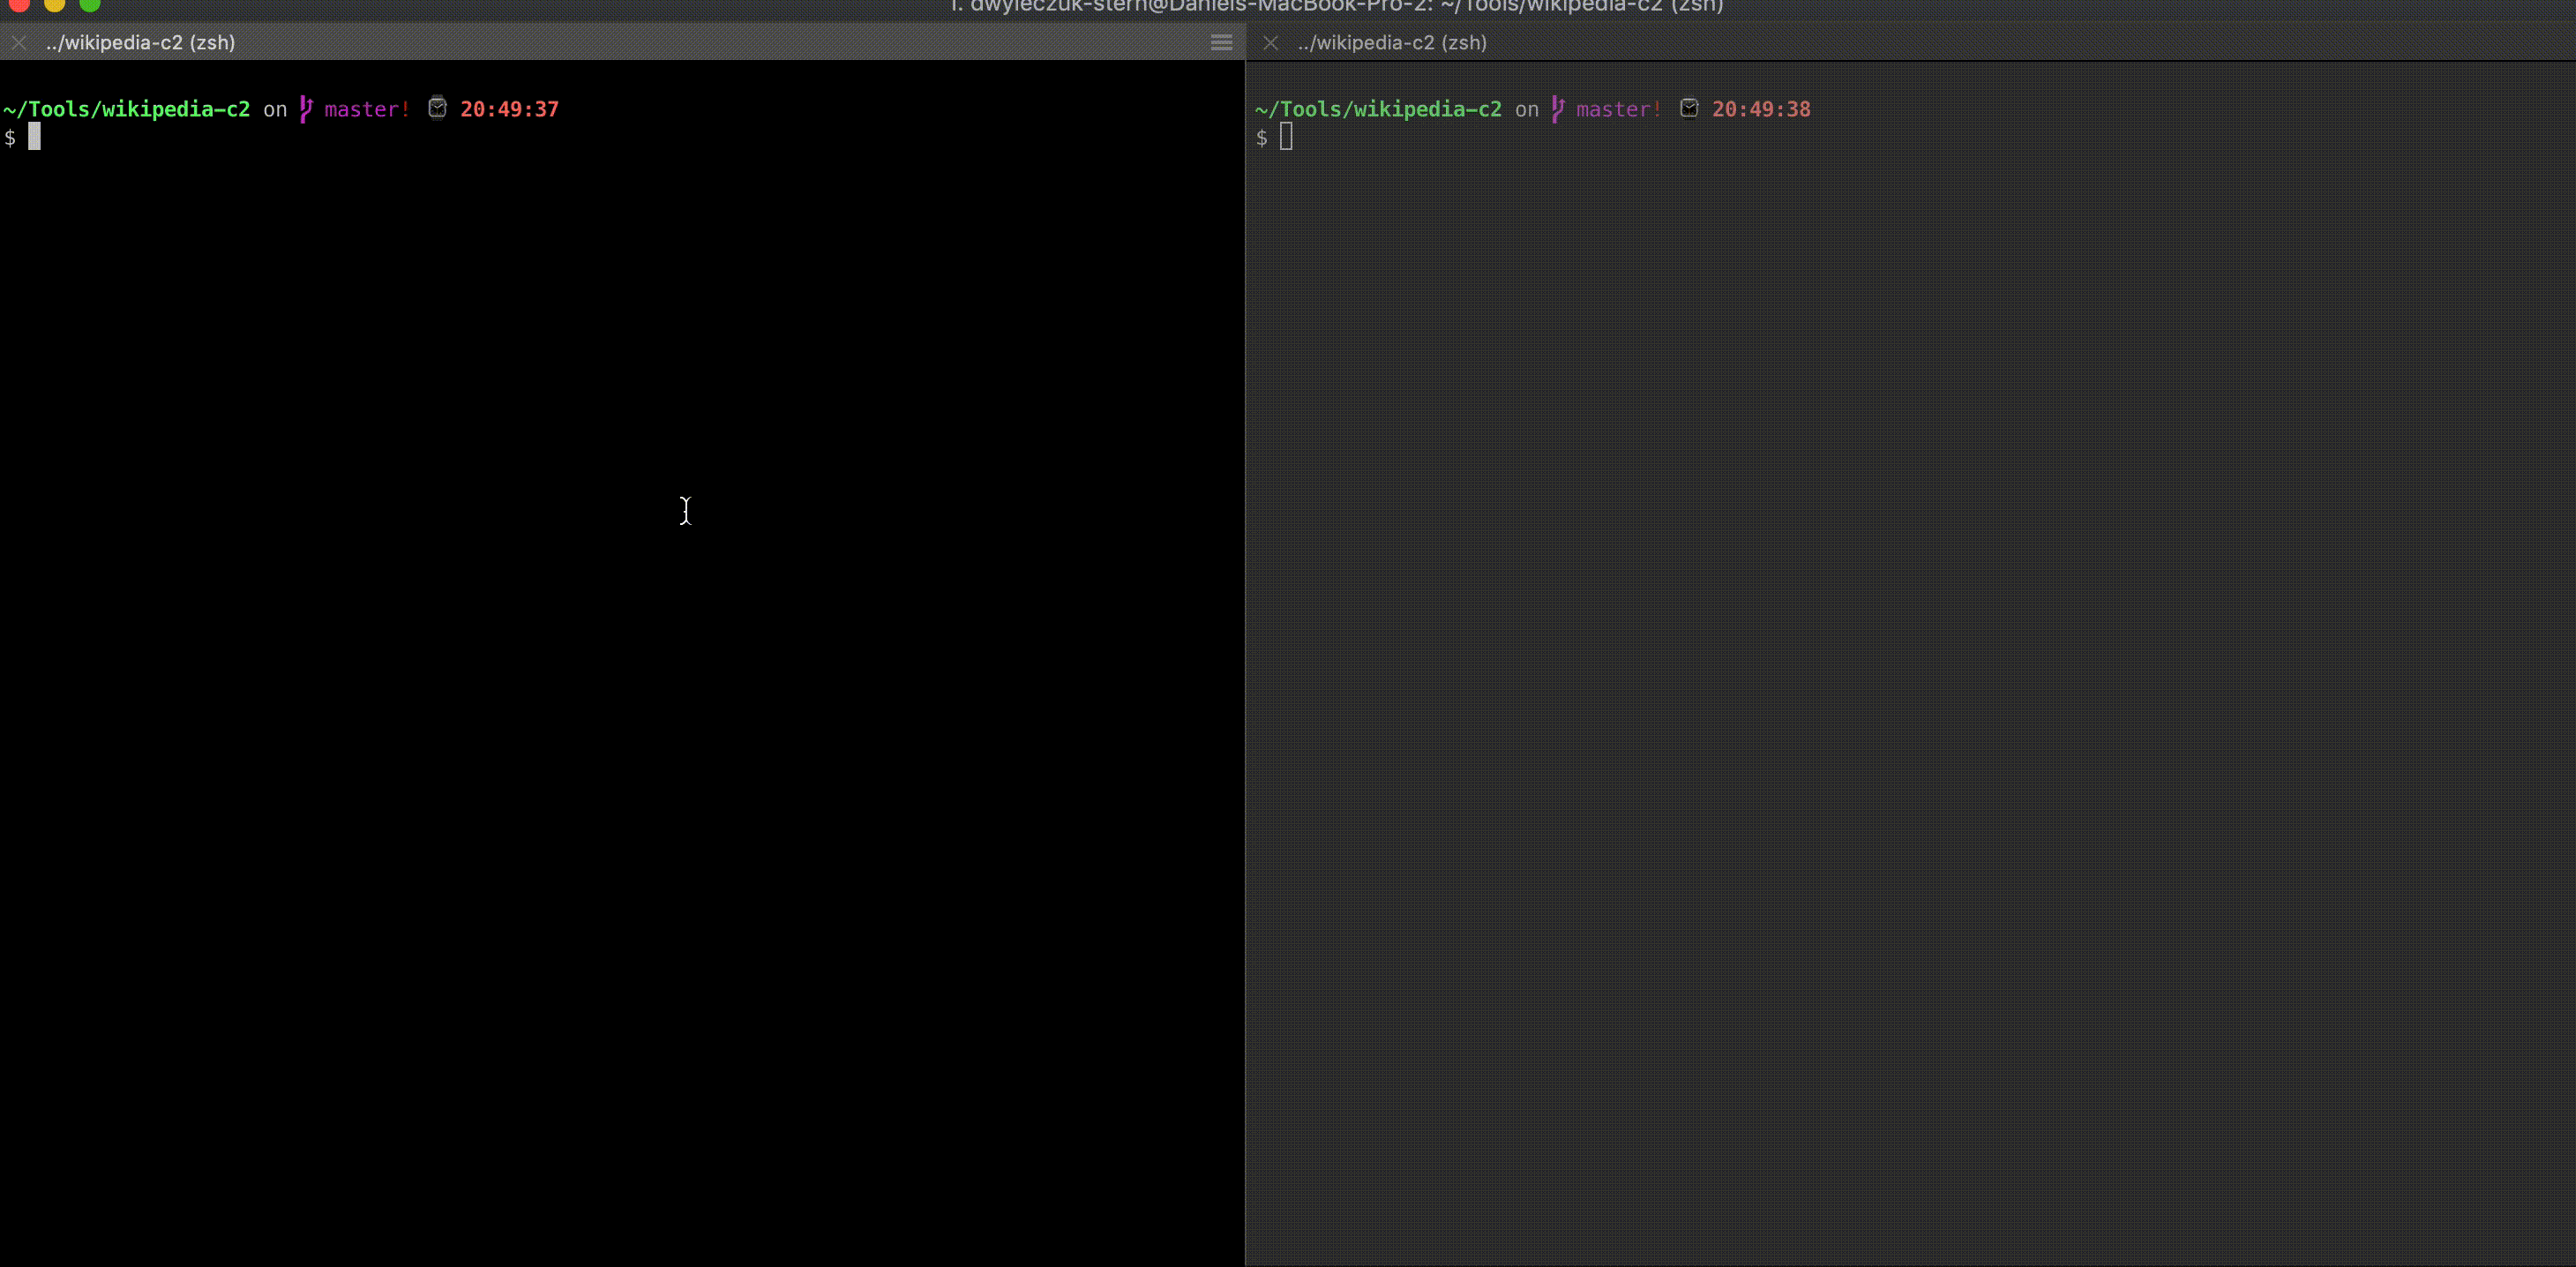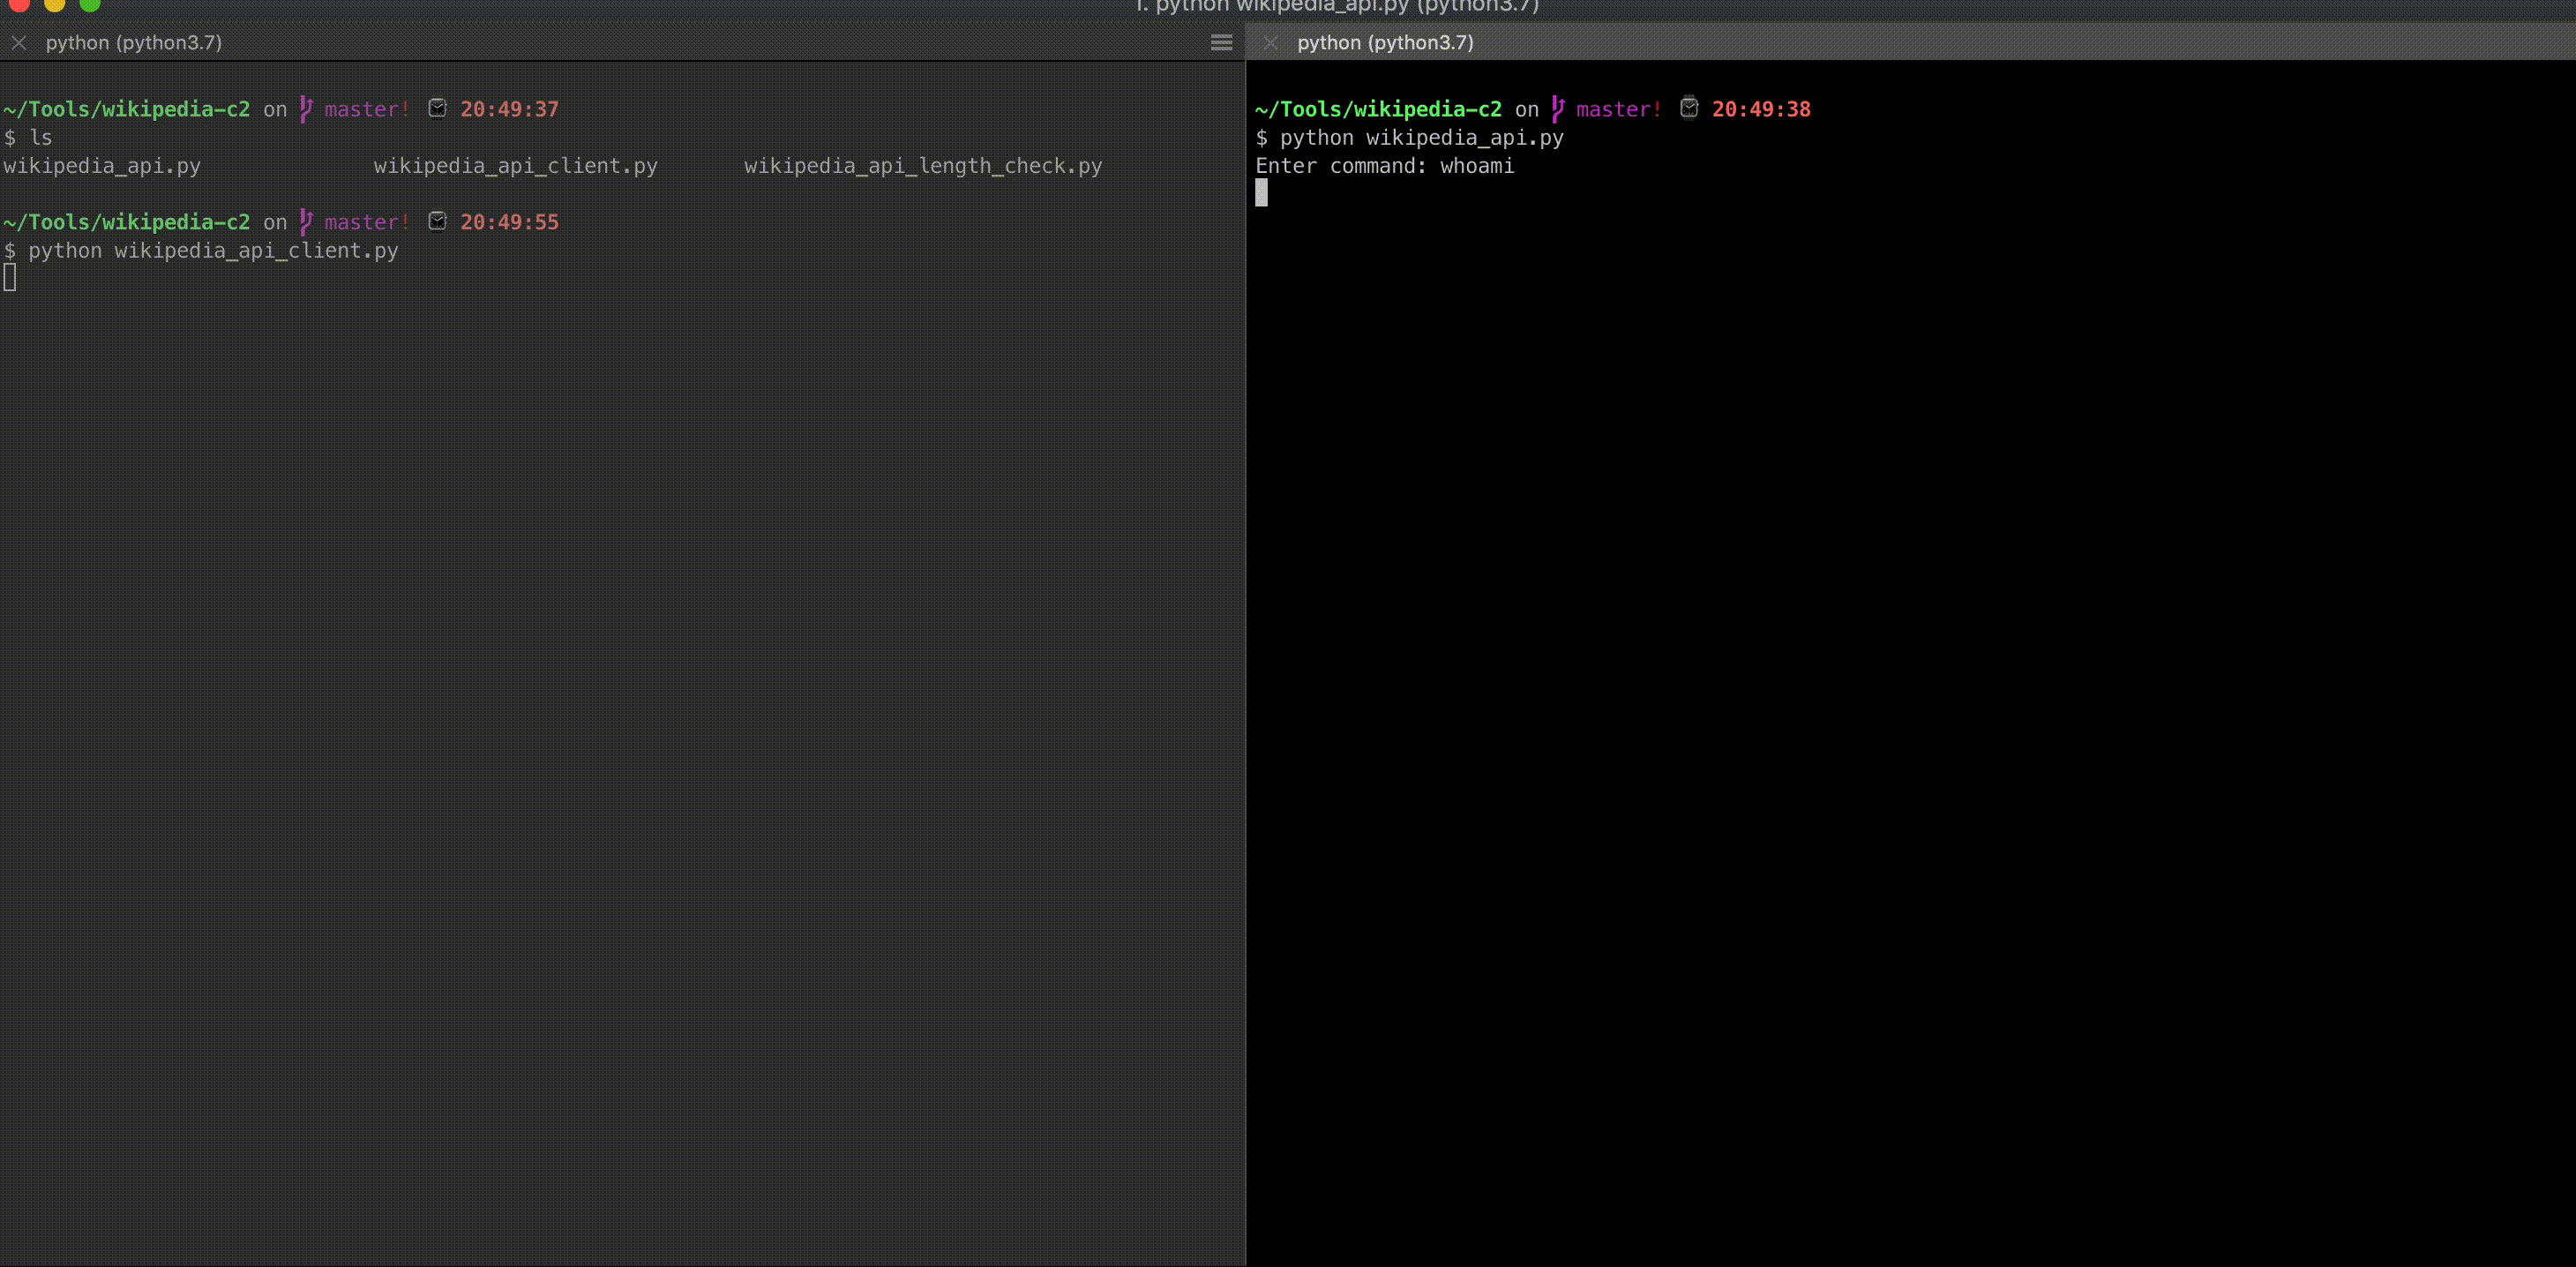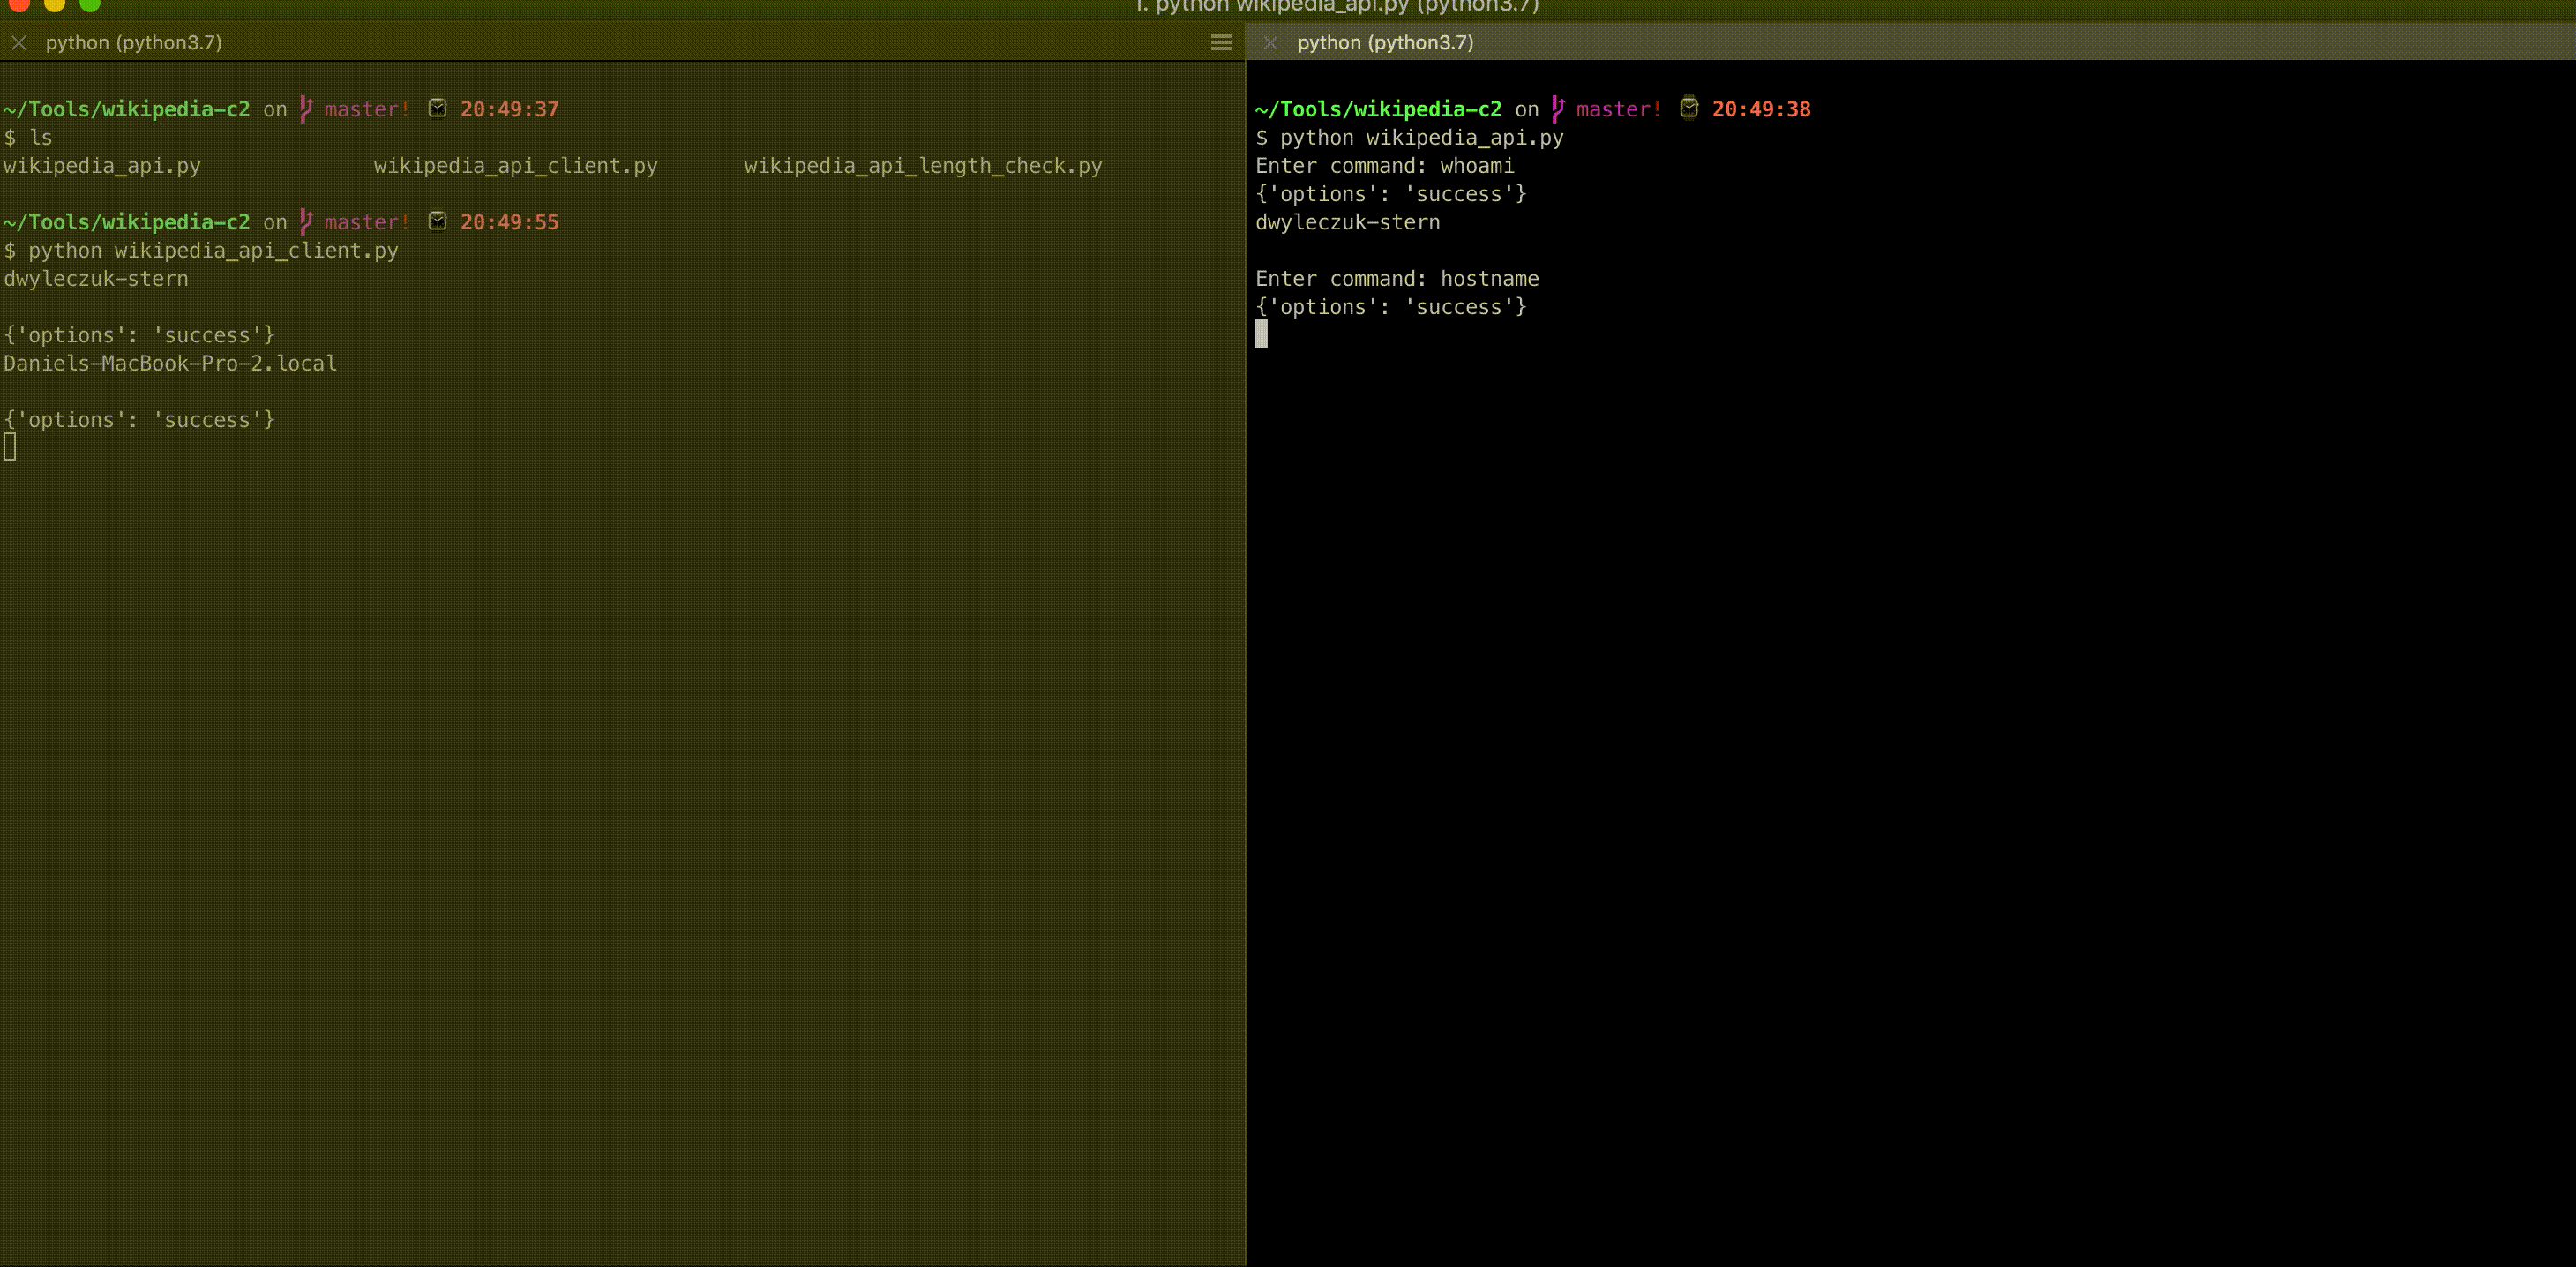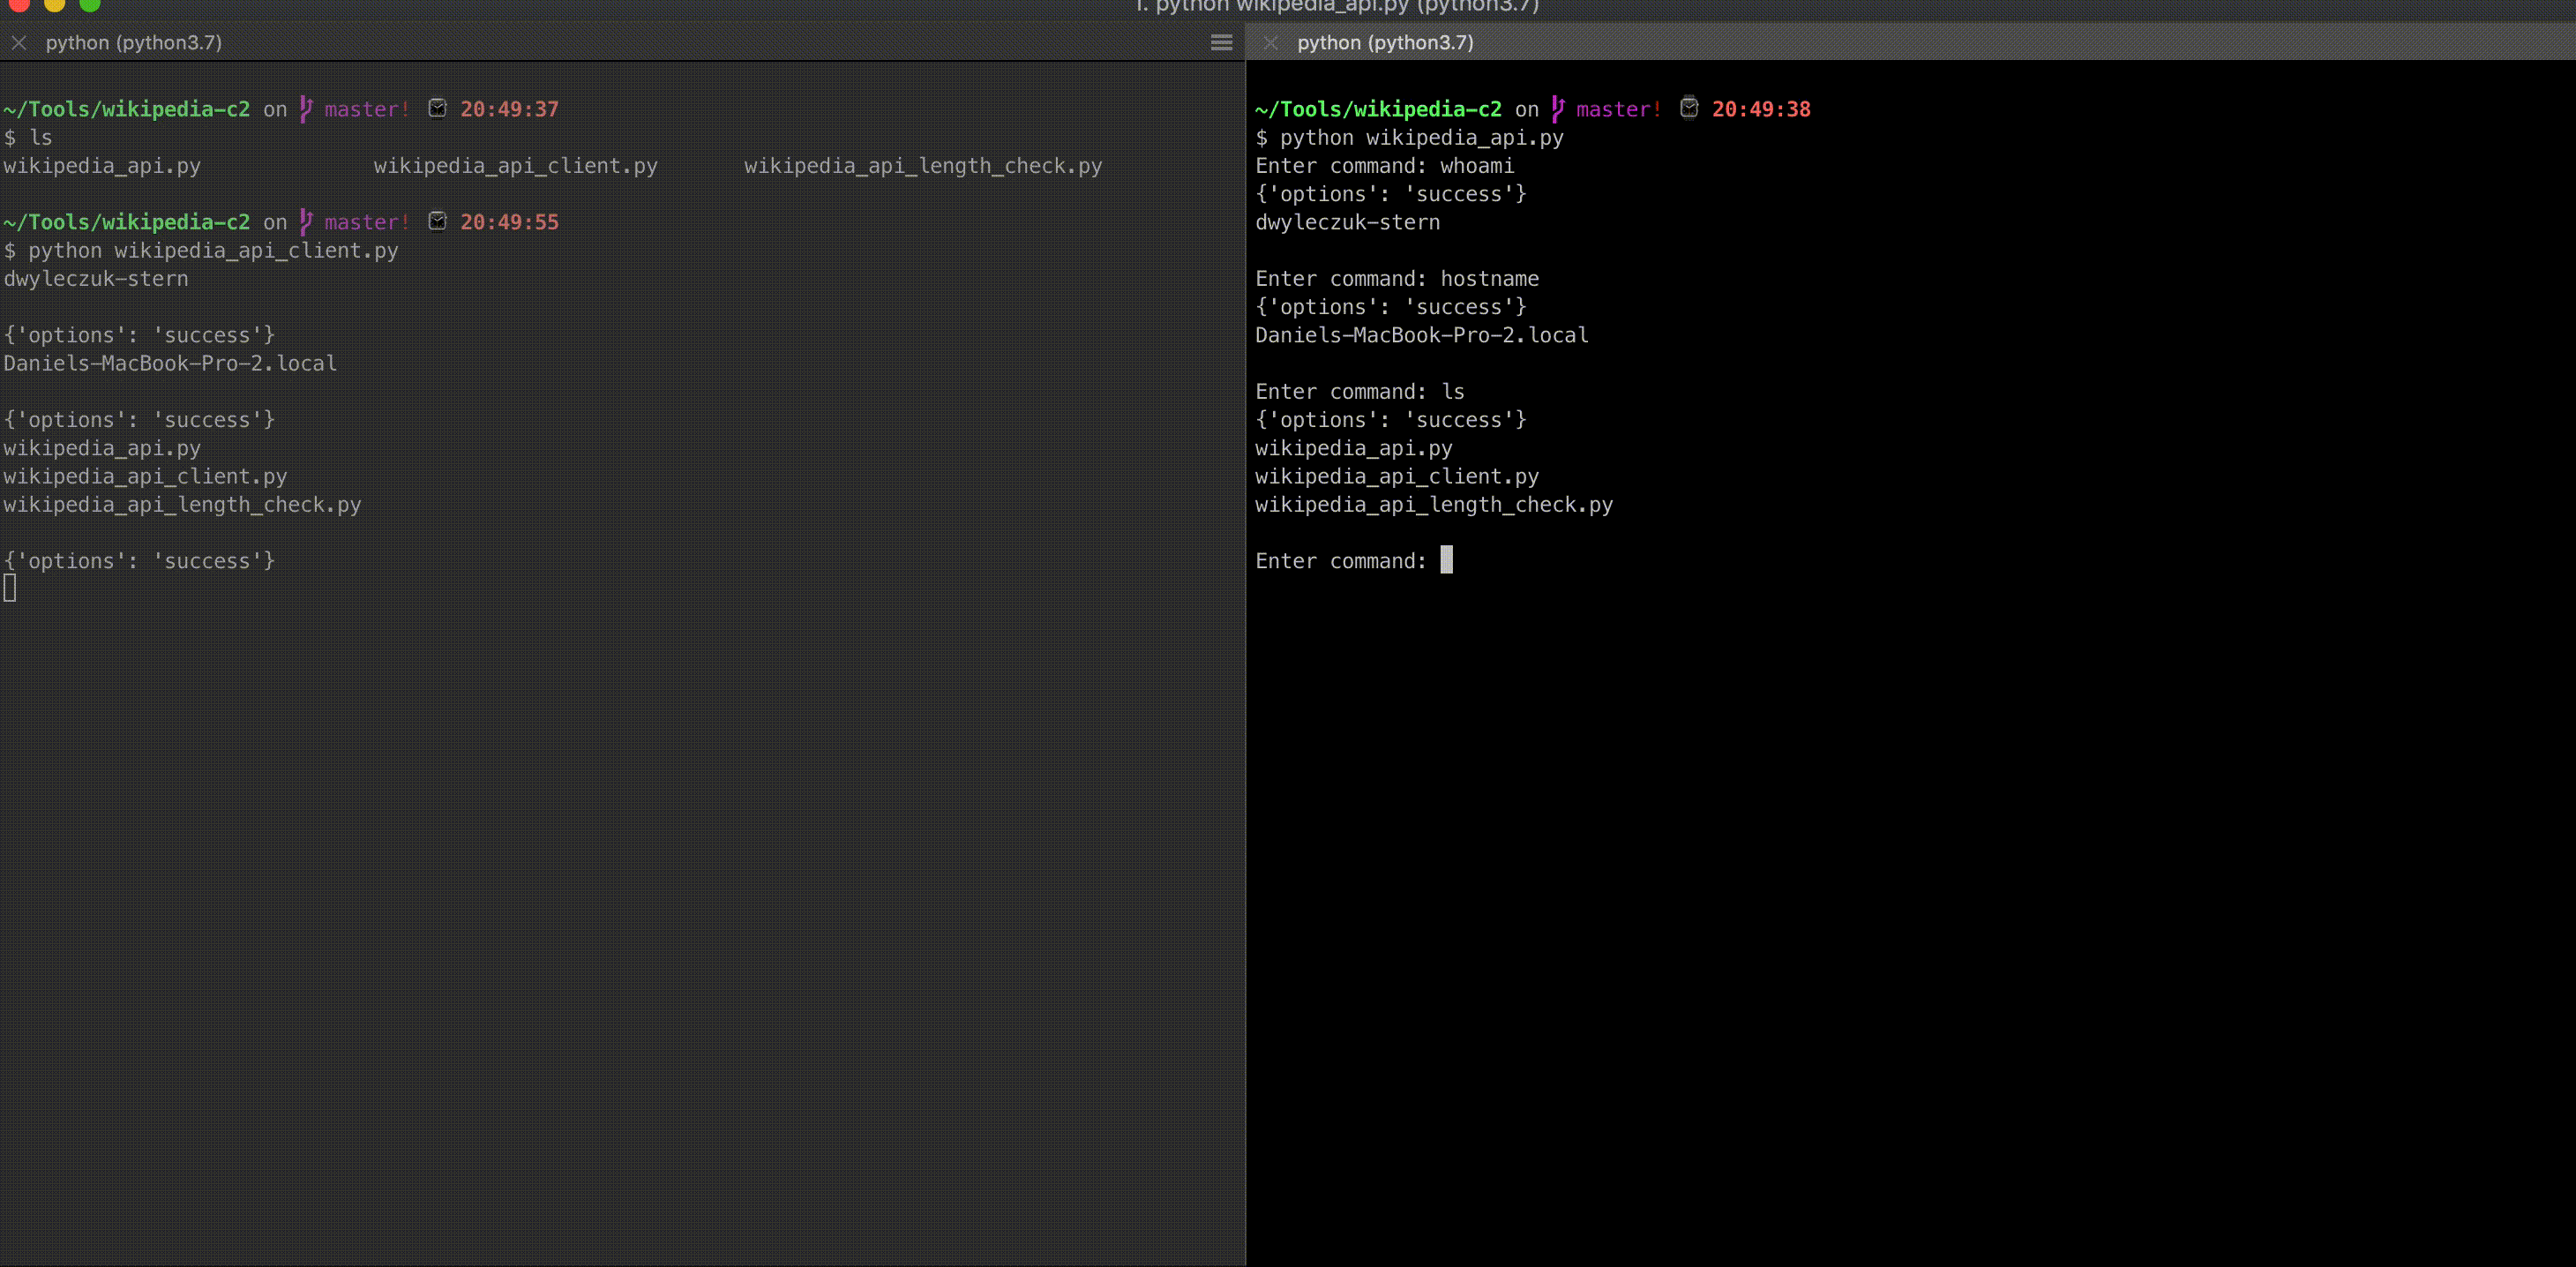 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control
 learner202649/cve-2026-42271-poc
The code for personally reproducing the corresponding vulnerability
 srginebras/cve-2026-23744-rce-for-mcpjam-inspector-v1.4.2
Python exploit for CVE-2026-23744 achieving remote code execution via crafted POST requests to the /api/mcp/connect endpoint in MCPJam Inspector <=…
 here_forawhile/terminalphone
Encrypted push-to-talk voice and text communication over Tor hidden services with end-to-end encryption, configurable ciphers, relay mode for group…
 00xglitch/bella
Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻
 rogdham/cve-2018-11235
PoC exploit for CVE-2018-11235 allowing RCE on git clone --recurse-submodules
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 davidcarliez/mythic_telegram_profile
Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
 iveresk/cve-2022-30525
Proof-of-concept exploit for CVE-2022-30525 enabling unauthenticated remote command injection on Zyxel firewalls via HTTP POST requests to the…
 mbanyamer/cve-2026-22553-insat-masterscada-buk-ts-mmadmserv
Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…
 dustblessnotdust/cve-2024-25180
Python exploit script for CVE-2024-25180, a remote code execution vulnerability in pdfmake, delivering a reverse shell via crafted POST requests.
 leo4j/amnesiac
PowerShell-based post-exploitation framework for lateral movement in Active Directory environments. Executes in-memory with named-pipe command…