EternalBlue-Exploit-Demonstration-MS17-010

Cybersecurity lab demonstrating exploitation of CVE-2017-0144 (EternalBlue) using Metasploit against a vulnerable Windows 7 VM, achieving…

Cybersecurity lab demonstrating exploitation of CVE-2017-0144 (EternalBlue) using Metasploit against a vulnerable Windows 7 VM, achieving…

A complete, modern demonstration lab for CVE-2014-6271 (Shellshock), including architecture, exploitation steps, Burp Suite usage, reverse shells,…

A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…

Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.

Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…

Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor

Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…

KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.

.NET Project for Attacking vCenter

Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)

Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.

Automatically spawn a reverse shell fully interactive for Linux or Windows victim

poc for CVE-2025-24252 & CVE-2025-24132

A Rust template for writing Beacon Object Files (BOFs)

CVE-2023-34362: MOVEit Transfer Unauthenticated RCE

Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…

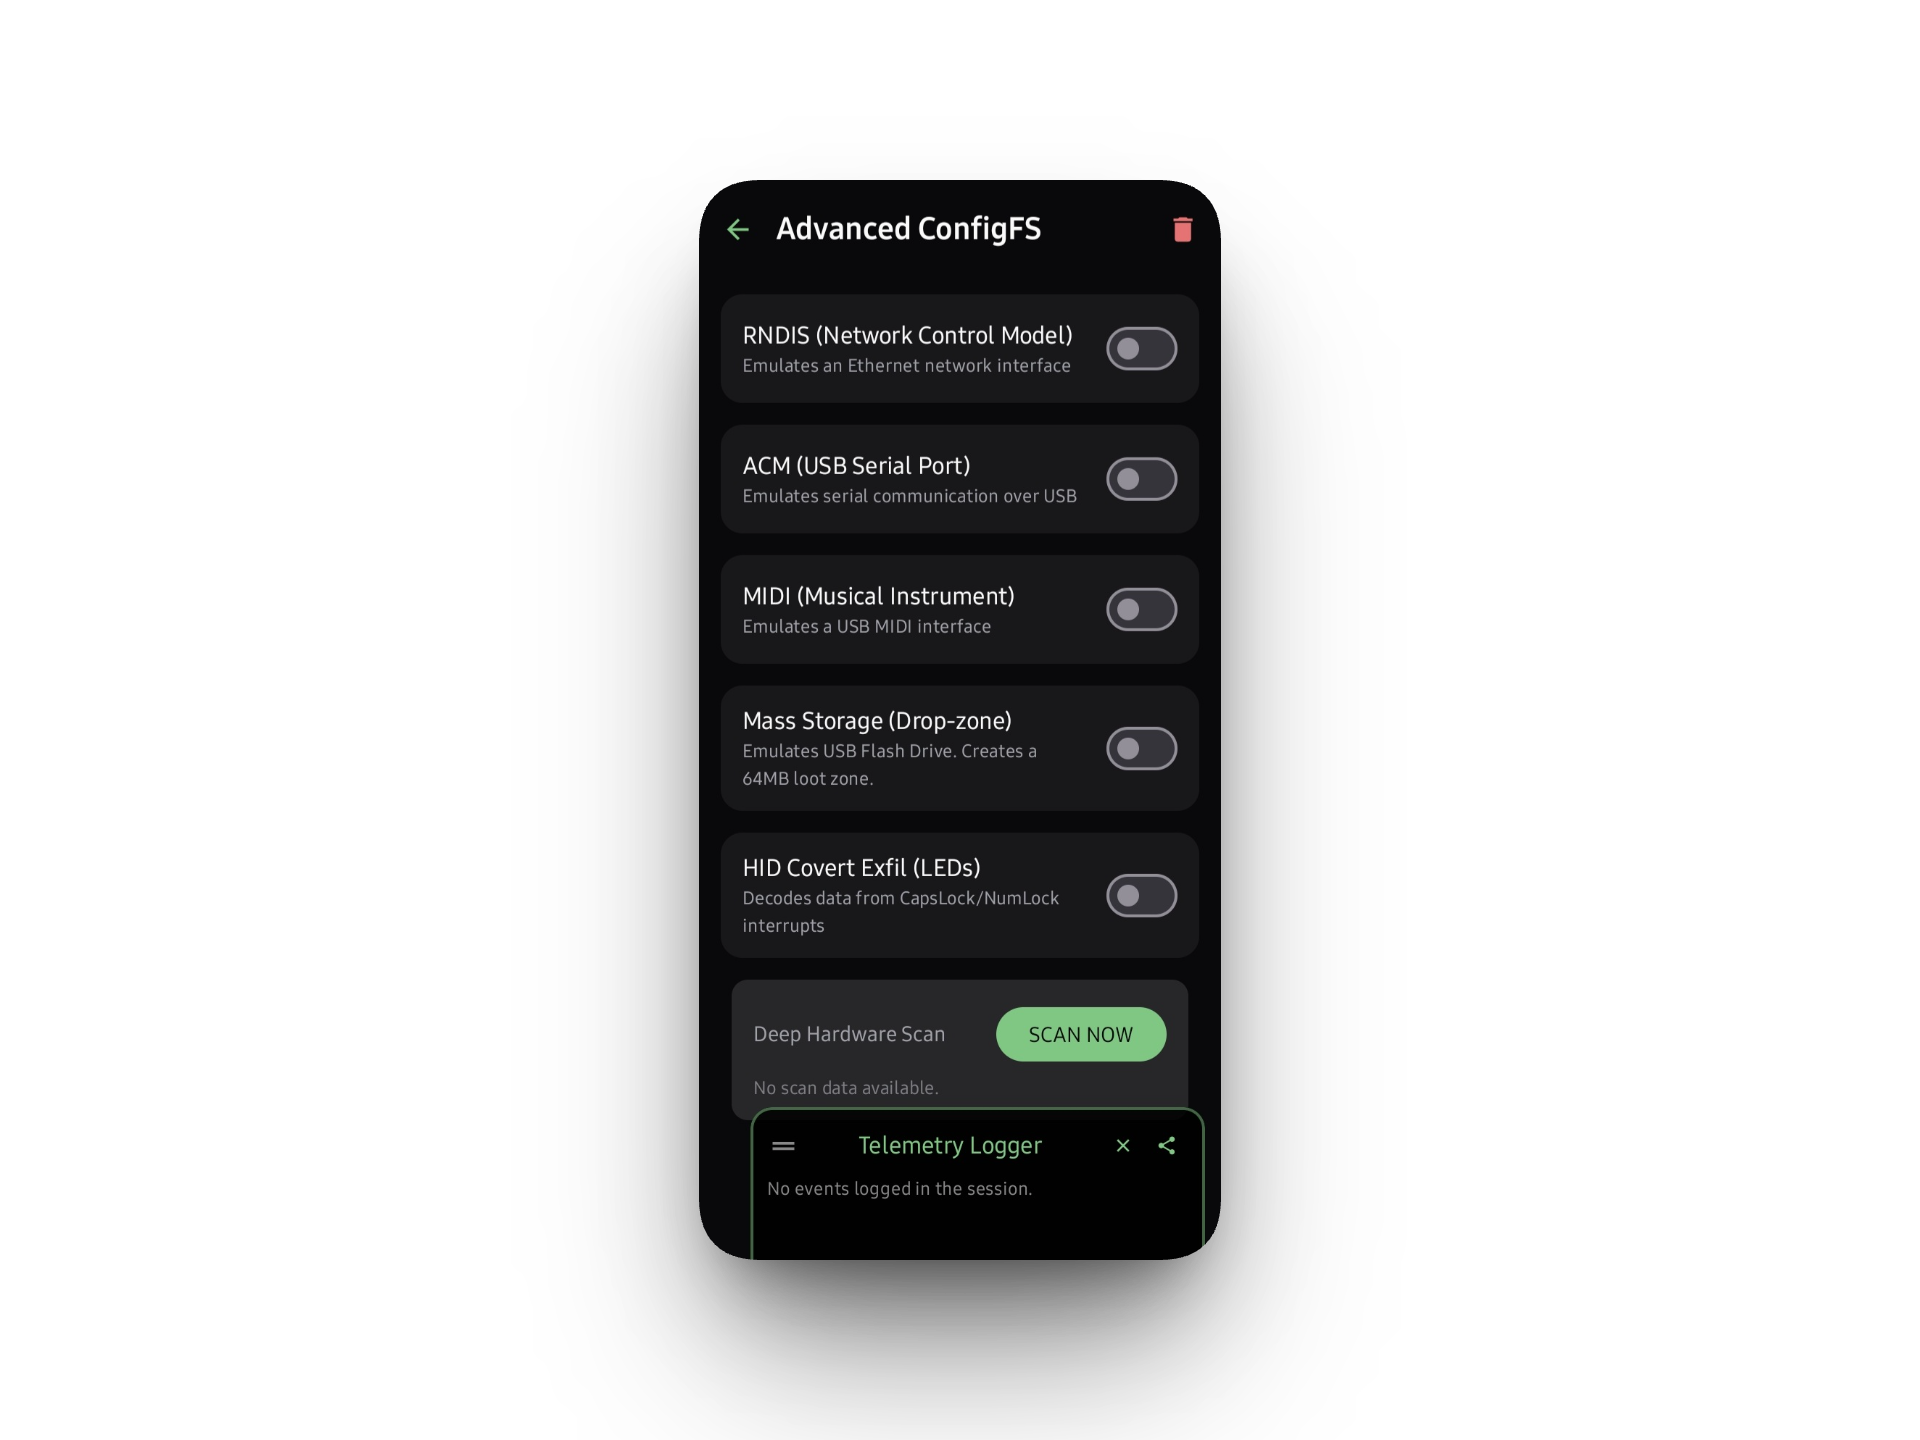
Payload injector and HID emulator for Android like Hak5 and rubber ducky

Multithreaded exploit script for CVE-2022-36804 affecting BitBucket versions <8.3.1