
HTTP-Shell
 joelgmsec/http-shell
Multiplatform HTTP reverse shell providing a shell-like interface over HTTP, with file upload/download, command history, auto-reconnection, and sudo…
command-and-controlpayload-generationpenetration-testing+2
244
joelgmsec/http-shellMultiplatform HTTP reverse shell providing a shell-like interface over HTTP, with file upload/download, command history, auto-reconnection, and sudo…
 komomon/cve-2022-30190-follina-office-msdt-fixed
Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…
 codextf2/burp2malleable
Quick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles
 ariary/queensono
Golang binary for data exfiltration with ICMP protocol (+ ICMP bindshell, http over ICMP tunneling, ...)
 lexfo/sshimpanzee
SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)
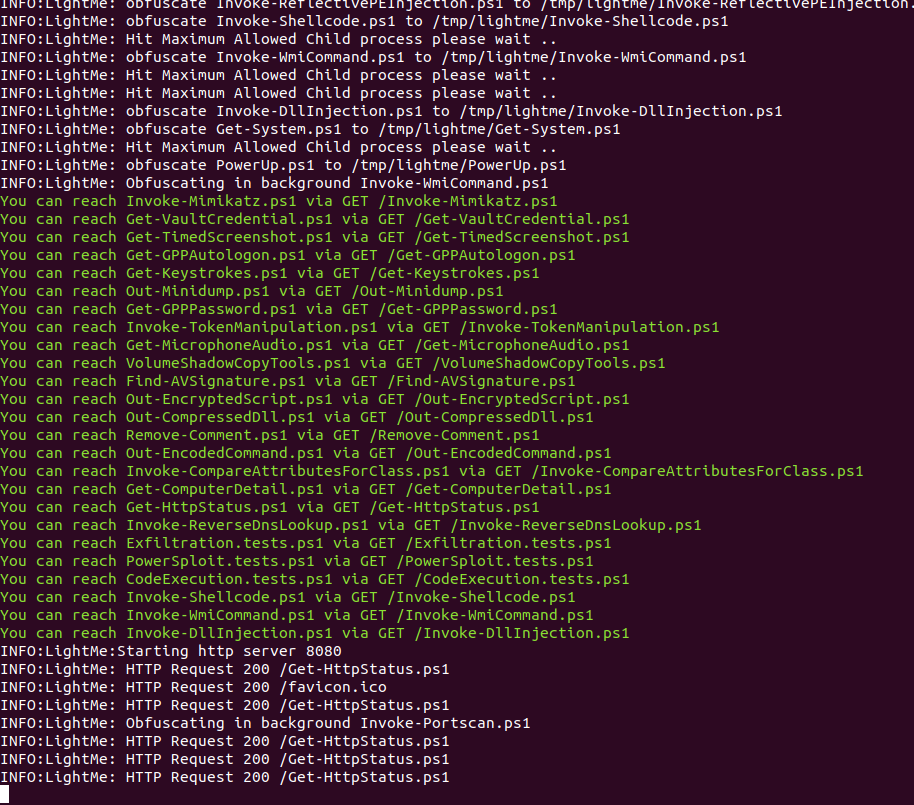 safebuffer/lightme
HTTP Server serving obfuscated Powershell Scripts/Payloads
 jas502n/cve-2018-1273
Python-based exploit for CVE-2018-1273 (Spring Data Commons RCE) with interactive command shell and HTTP POST payload injection for penetration…
 nccgroup/fenrir
PoC to tunnel the Meterpreter reverse HTTP shell over RDP Virtual Channels
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
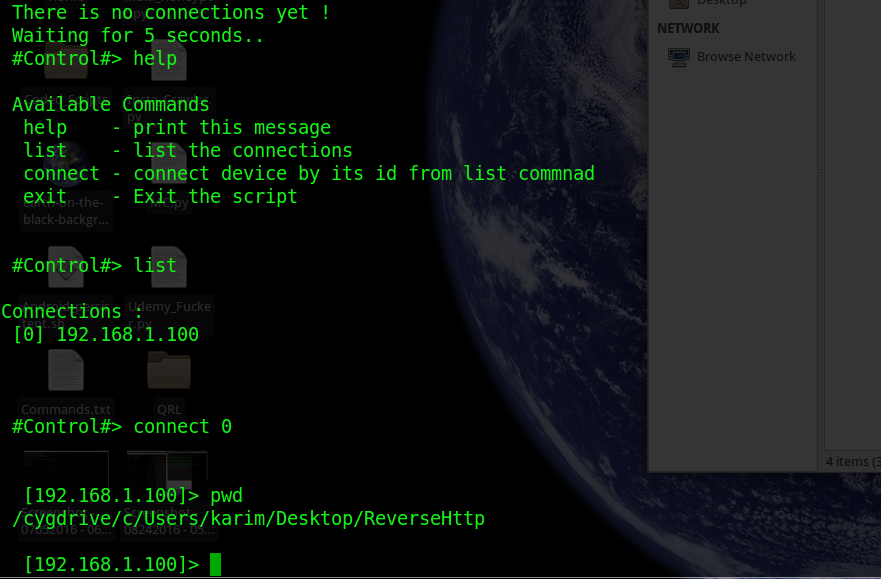 d4vinci/reversehttp
Python backdoor that uses http post/get requests to communicate
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 warferik/cve-2019-3980
Proof-of-concept exploit for CVE-2019-3980 enabling remote command execution via custom C# payload with HTTP callback for output retrieval.
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
 lorddemon/drupalgeddon2
Remote code execution exploit for Drupal CVE-2018-7600 (Drupalgeddon2) with command injection via HTTP requests.
 mackleadmire/cve-2018-3191-rce-exploit
Exploit for CVE-2018-3191 targeting Oracle WebLogic servers. Generates a malicious payload via RMI, deploys reverse shell classes on an HTTP server,…
 nanowraith/cve-2024-29973
Proof-of-concept exploit for CVE-2024-29973, a command injection vulnerability in Zyxel NAS devices. Executes arbitrary OS commands via a crafted…
 ludy-dev/weblogic_unauthorized-bypass-rce
Python-based exploit script for Oracle WebLogic CVE-2020-14882 unauthorized bypass RCE. Tests authentication bypass and remote code execution via…
 ianxtianxt/cve-2019-16278
Python exploit script for CVE-2019-16278, a remote command execution vulnerability in Nostromo httpd. Executes arbitrary commands on vulnerable…