

Android-Projector-C2-Malware
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
android-securitycommand-and-controldigital-forensics+9
18
kavan00/android-projector-c2-malwareBreakdown of a c2-network of chinese beamers - SilentSDK-Analysis
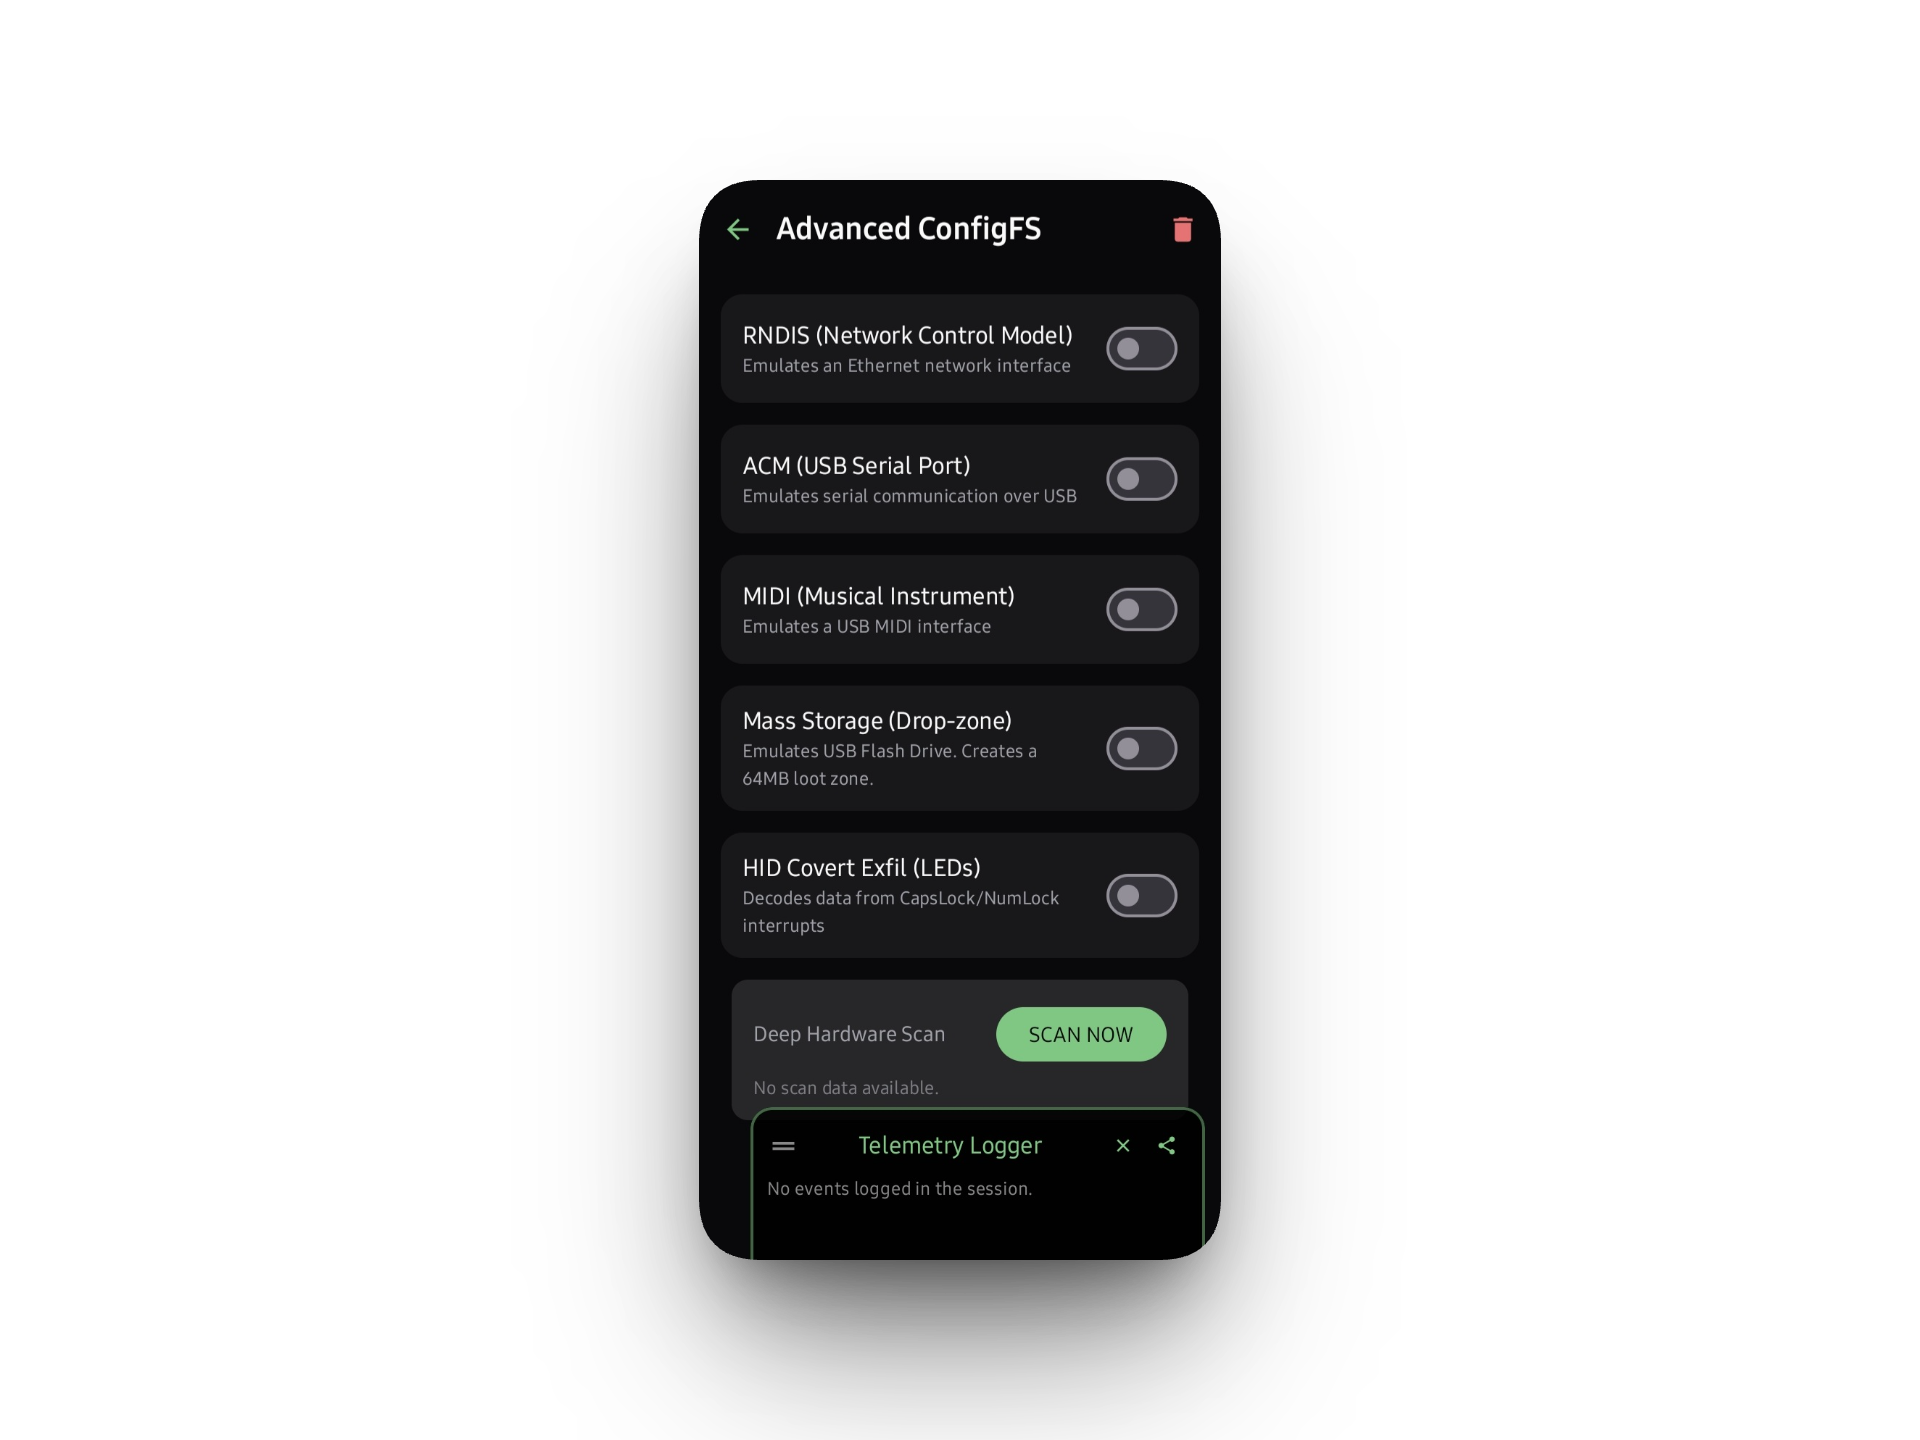 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
 rev-code/androidclient
Android remote administration client
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 kaitokidc500/cve-2024-23700-c2-server
Source code minh họa máy chủ c2 demo kịch bản thực thi của CVE-2024-23700
 fcy10012/cve-2024-31317-deployer
CVE-2024-31317 Android Zygote命令注入漏洞研究与部署工具 | Android 9-13 漏洞利用框架
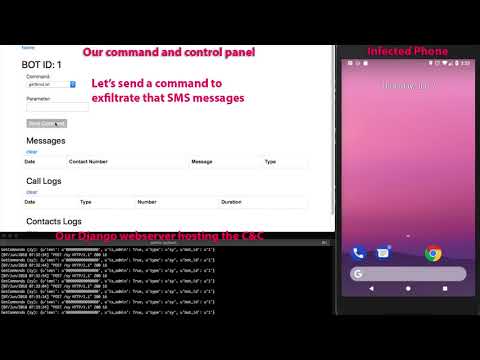 bizdak/silverboxcc
Reverse engineered android malware, and this is a C&C server for it
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 seqred-s-a/cve-2019-14514
Remote code execution in Microvirt MEmu
 kalibb/cve-2024-31317-deployer
Automated deployment tool for CVE-2024-31317, a command injection vulnerability in Android 9-13. Includes reverse shell payload, compile script, and…
 ahmyth/ahmyth-android-rat
Android Remote Administration Tool
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration