CVE-2023-30258-magnus-billing-v7-exploit

Automated Python exploit for CVE-2023-30258, a command injection in Magnus Billing System v7. Sends crafted GET request to icepay.php to execute…

Automated Python exploit for CVE-2023-30258, a command injection in Magnus Billing System v7. Sends crafted GET request to icepay.php to execute…

Proof-of-concept exploit for CVE-2020-8515 command injection in Draytek routers. Includes automated exploitation, reverse shell delivery, and…

Automated exploit for CVE-2025-69212 command injection in OpenSTAManager, featuring admin authentication, malicious ZIP upload, and reverse shell or…

Proof-of-concept exploit for CVE-2022-40127 targeting Apache Airflow RCE via crafted run_id parameter, with automated reverse shell delivery.

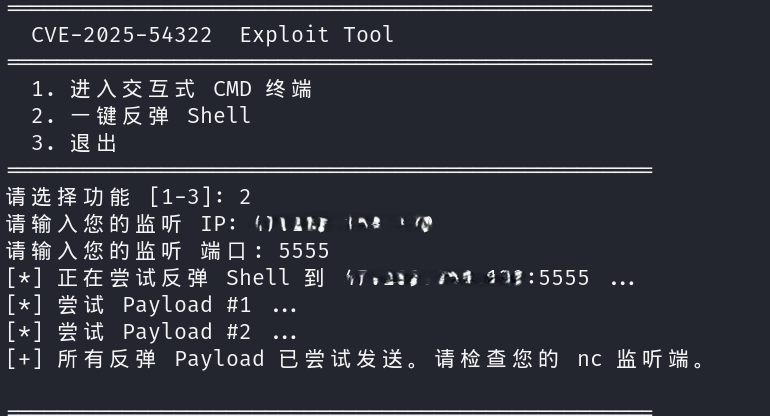
Proof-of-concept exploit for CVE-2025-54322, a critical pre-authentication RCE in XSpeeder SXZOS firmware. Provides interactive shell, reverse shell…

Automated mass exploitation tool for CVE-2019-16920 command injection vulnerability in multiple D-Link routers, enabling unauthenticated remote code…

Automated deployment tool for CVE-2024-31317, a command injection vulnerability in Android 9-13. Includes reverse shell payload, compile script, and…

Modified exploit for CVE-2019-12725 with fixed errors, elevated privilege execution, and removed delays for faster automated exploitation testing.

Automatic SSTI detection tool with interactive interface

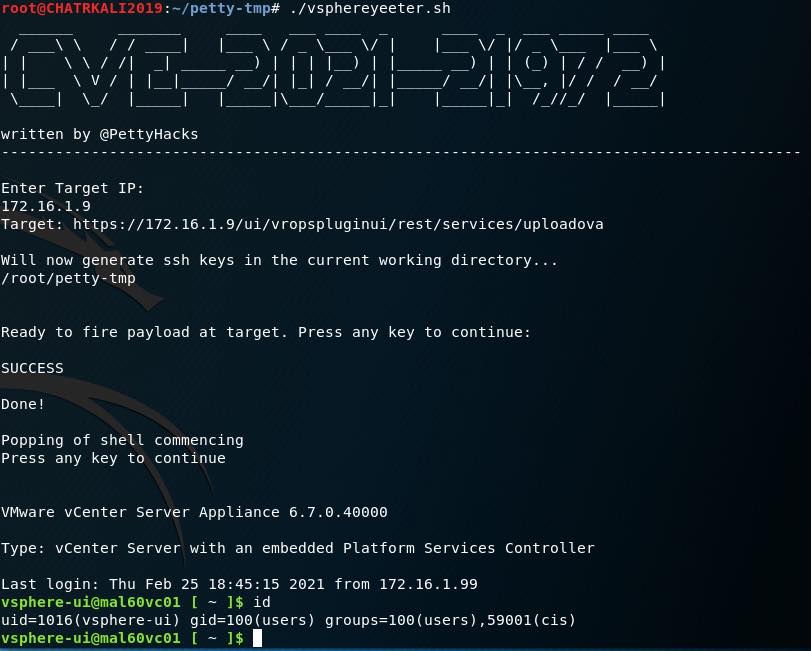
POC exploit for CVE-2021-21972

Scanner and exploit for CVE-2024-12986, a command injection in DrayTek Gateway Devices. Includes a Bash scanner and a Python interactive shell for…

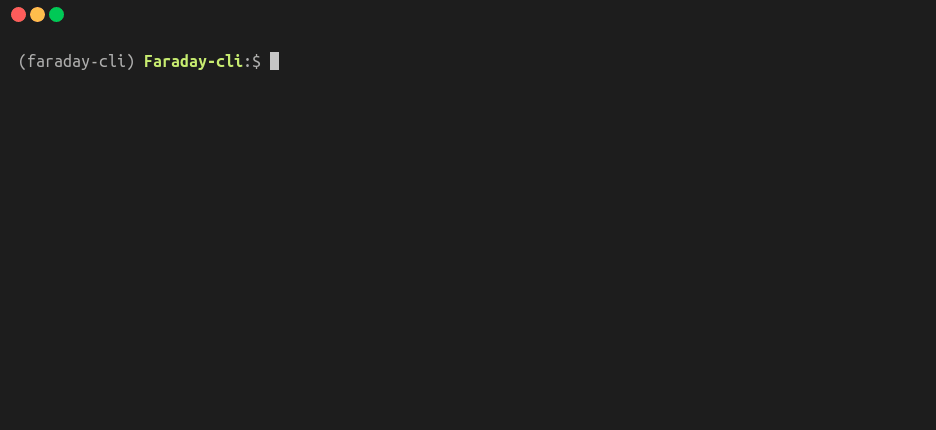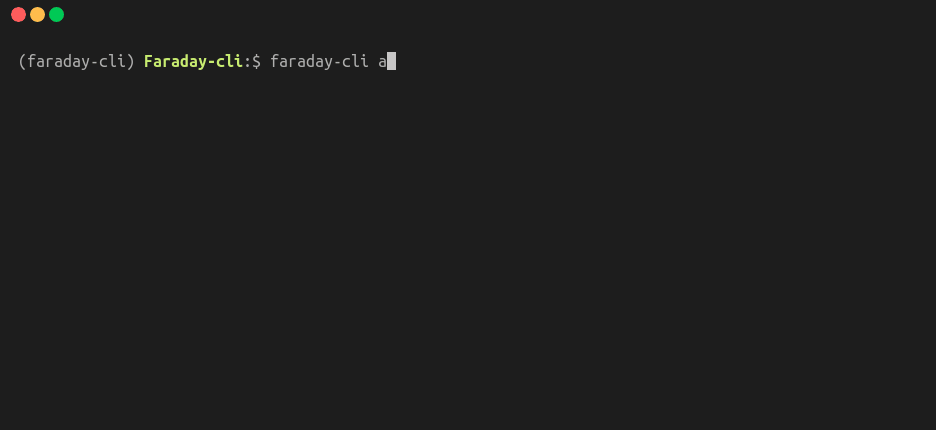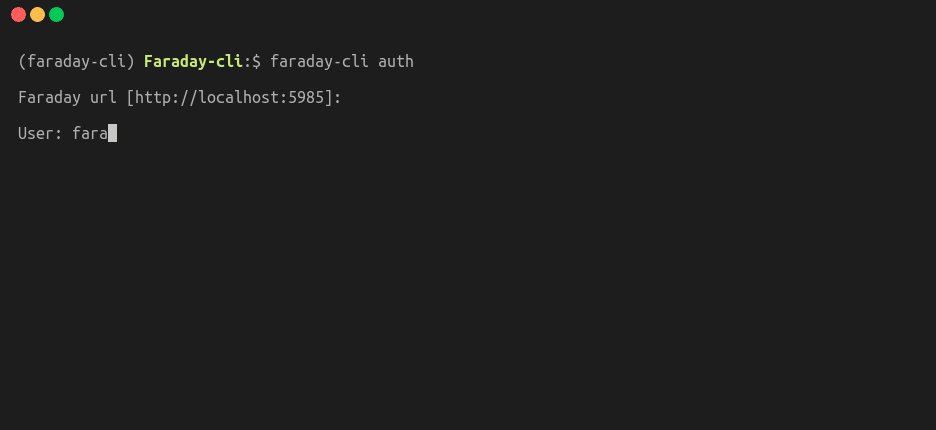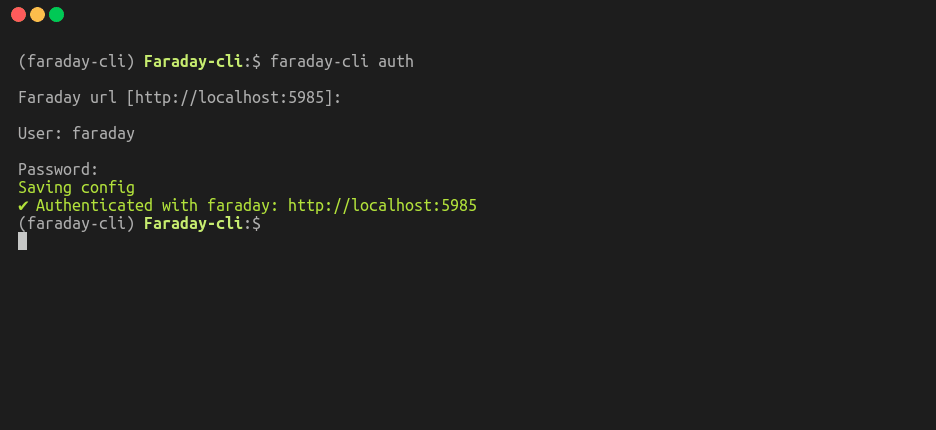
Faraday's Command Line Interface

Mass Hunting & Exploitation PoC for CVE-2025-55182 & CVE-2025-66478

提供批量扫描URL以及执行命令功能。Workspace ONE Access 模板注入漏洞,可执行任意代码

Nuclei Template CVE-2025–24813

Exploit script for CVE-2026-21962, enabling remote command execution on vulnerable web servers with single-target, batch, and reverse shell modes.

Control Web Panel (CWP) vulnerability scenario related to CVE-2026-57517

Python script to detect CVE-2022-30525 OS command injection vulnerability in Zyxel USG FLEX devices by sending crafted HTTP requests and analyzing…