
CVE-2025-55182_liyon
 hujiaozhuzhu/cve-2025-55182_liyon
Python-based exploit for CVE-2025-55182 (React Server Components RCE) with interactive shell, reverse shell, batch scanning, and Docker-based…
command-and-controleducationexploitation+7
hujiaozhuzhu/cve-2025-55182_liyonPython-based exploit for CVE-2025-55182 (React Server Components RCE) with interactive shell, reverse shell, batch scanning, and Docker-based…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 jacobtaylor3/cve-2021-21220
Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.
 opsecramdan/react2shell-cve-2025-55182
Automated exploitation framework for CVE-2025-55182 (Next.js RCE) with subdomain enumeration, vulnerability scanning, payload generation, and…
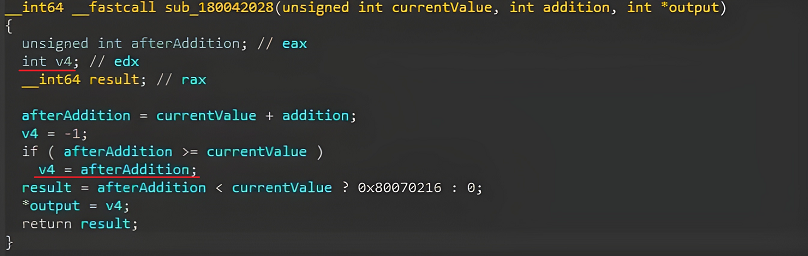 mr-alperen/cve-2022-26810
Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…
 gagaltotal/n8n-cve-2025-68613
Authenticated RCE exploit PoC and vulnerability scanner for CVE-2025-68613 in n8n. Supports command execution, file operations, and reverse shell…
 kayl22/magnus_billing_7.3.0_rce_cve-2023-30258
Exploit for CVE-2023-30258: remote code execution in MagnusBilling 7.3.0 via unsanitized 'democ' parameter in icepay.php, enabling command injection…
 h1sok444/cve-2026-23744-poc
Proof-of-concept exploit for CVE-2026-23744, targeting /api/mcp/connect to achieve remote command execution on Linux systems via reverse shell.
 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…
 cyberquestor-infosec/cve-2019-3980-open_net_admin_v18.1.1_rce
Bash-based exploit for CVE-2019-3980 targeting OpenNetAdmin 18.1.1, delivering unauthenticated remote code execution via command injection and…
 zhulin837/checkmk_cve-2024-0670
Exploit for Checkmk CVE-2024-0670 with automated file transfer, reverse shell, and privilege escalation via RunasCs for penetration testing…
 ccordeiro/cve-2021-22205
Python exploit for CVE-2021-22205, a remote command execution in GitLab CE/EE via image file parsing. Supports vulnerability checking, batch…
 fbm31/audit-blackbox-web-to-root
Audit de sécurité Black Box d'un serveur Drupal 7. Démonstration d'une Kill Chain complète : Injection SQL (CVE-2014-3704) ➔ RCE ➔ Reverse Shell ➔…
 heyholiday067/cve-2024-39943-poc
CVE-2024-39943 rejetto HFS (aka HTTP File Server) 3 before 0.52.10 on Linux, UNIX, and macOS allows OS command execution by remote authenticated…
 imbas007/poc_cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940 targeting cPanel, enabling account enumeration, command execution, and interactive shell access on…
 anonnymous5/1panel-cve-2025-54424-
Exploit tool for 1Panel CVE-2025-54424, enabling certificate bypass and remote command execution via WebSocket, with batch scanning and interactive…
 greenforcenetworks/toolshell_cve-2025-53770
Exploit PoC for CVE-2025-53770 enabling webshell upload to SharePoint, ValidationKey extraction, signed ViewState generation, and remote code…
 10cks/cve-2014-6287
Rejetto http File Server 2.3.x (Reverse shell)