
Archived
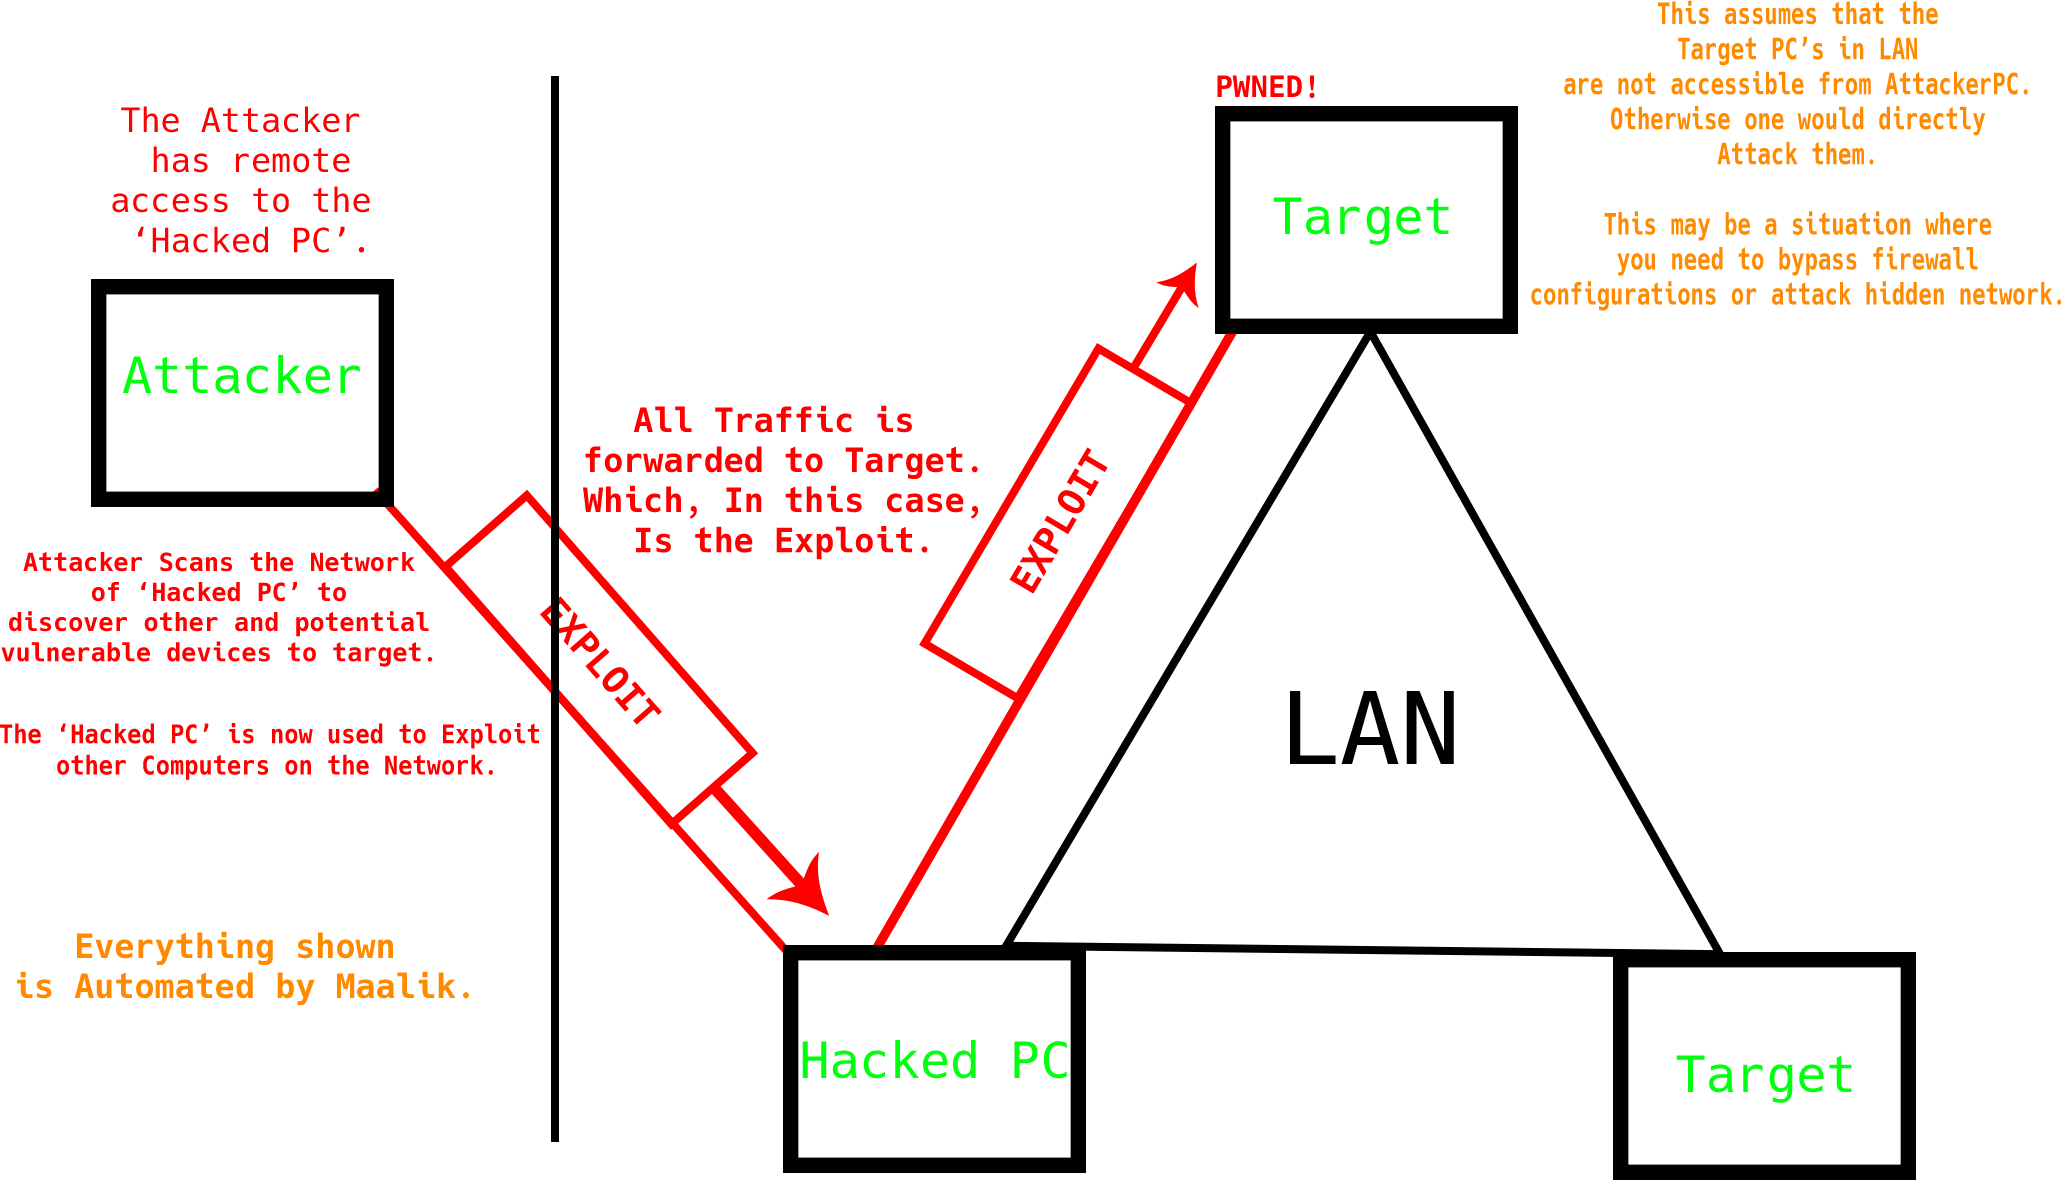
maalik
 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
privilege-escalationpersistence-mechanismsexploitation+6
94
 lukebaggett/google_socks
A proof of concept demonstrating the use of Google Drive for command and control.
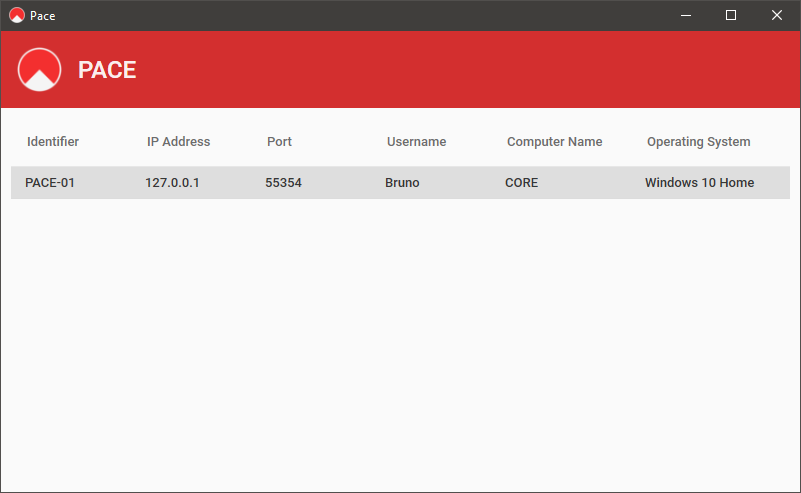 typetrait/pace
Remote Access Tool for Windows.
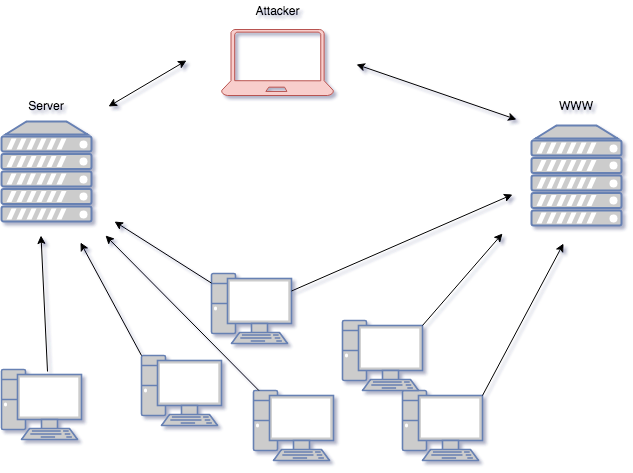 m507/m-botnet
A C2 project that controls a self-propagating MS17-010 worm.
 4n4nk3/tinkerershell
A simple python reverse shell written just for fun.
 conviso-archives/firefox_tunnel
Browser-based C2 tunnel that exfiltrates payloads through Firefox's cookie.sqlite and auto-submitting HTML/JS, enabling stealthy firewall bypass for…
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
 saintly2k/katana
Katana Botnet used for DDoS attacks based on the Mirai Botnet. TEACHING PURPOSES ONLY! I CANNOT BE HELD RESPONSIBLE FOR ANYTHING YOU DO WITH IT! I…
 spiderlabs/firework
Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process.
 shiva108/pentestproxy
Scripts for: How to Build a Covert Pentesting Infrastructure Almost Free
 mitre/caldera-agent
Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…
 alanbaumgartner/aurora
Aurora Remote Administration Tool
 kiwidoggie/oni-framework
Embedded systems C2 software written in C/C#
 0xbbuddha/hermes
A Python agent targeting Linux for Mythic C2
 cinaaaa/hiroo
🔐 HIROO is an FUD Remote Administration Tool (RAT) Generator
 mitre/caldera-crater
C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.