
CVE-2026-4802
 hakaioffsec/cve-2026-4802
Proof-of-concept exploit for CVE-2026-4802, a command injection vulnerability in Cockpit's system logs UI, enabling arbitrary command execution and…
command-and-controlexploitationpenetration-testing+3
4
hakaioffsec/cve-2026-4802Proof-of-concept exploit for CVE-2026-4802, a command injection vulnerability in Cockpit's system logs UI, enabling arbitrary command execution and…
 makavellik/poc-cve-2021-42013-exploit
Una herramienta avanzada de escaneo, explotación e interacción remota diseñada para detectar y aprovechar la vulnerabilidad Apache Path Traversal +…
 deividasterechovas/soc335-cve-2024-49138-exploitation-detected
Documented incident response case for CVE-2024-49138 exploitation, featuring log analysis, hash validation, C2 detection, and containment procedures…
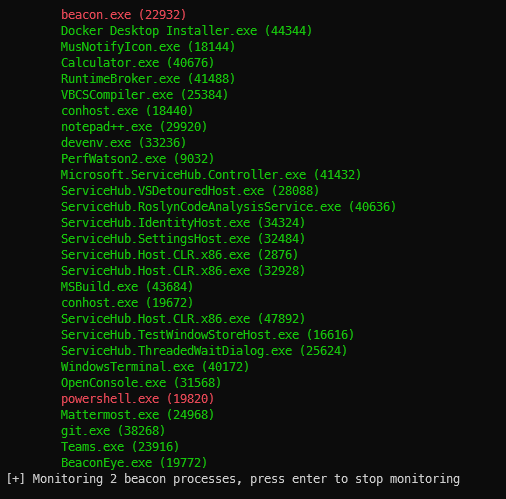 ccob/beaconeye
Hunts out CobaltStrike beacons and logs operator command output
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
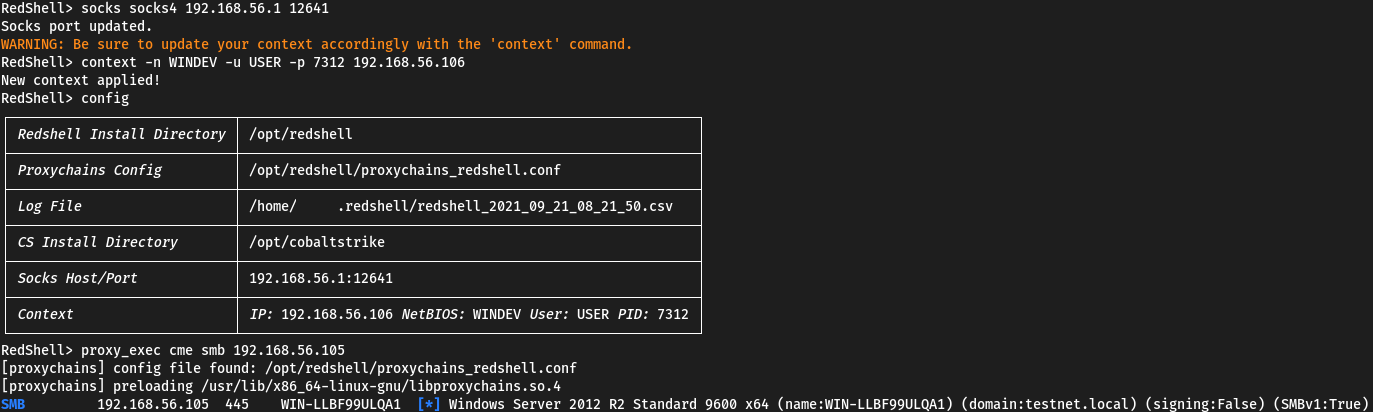 verizon/redshell
An interactive command prompt for red teaming and pentesting. Automatically pushes commands through SOCKS4/5 proxies via proxychains. Optional Cobalt…
 infoskirmish/hive
The CIA Hive source code as released by Wikileaks
 jeffli1024/log4j-rce-test
Quick test environment for CVE-2021-44228 Log4j RCE vulnerability with a built-in exploit server and customizable payload execution.
 ch1nghz/cve-2020-11851
Remote Code Execution vulnerability on ArcSight Logger
 audibleblink/bothan
Is this IP a C2 server?