
CVE-2026-20841
 hamzamalik3461/cve-2026-20841
🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
command-and-controlexploitationpayload-development+3
2
hamzamalik3461/cve-2026-20841🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
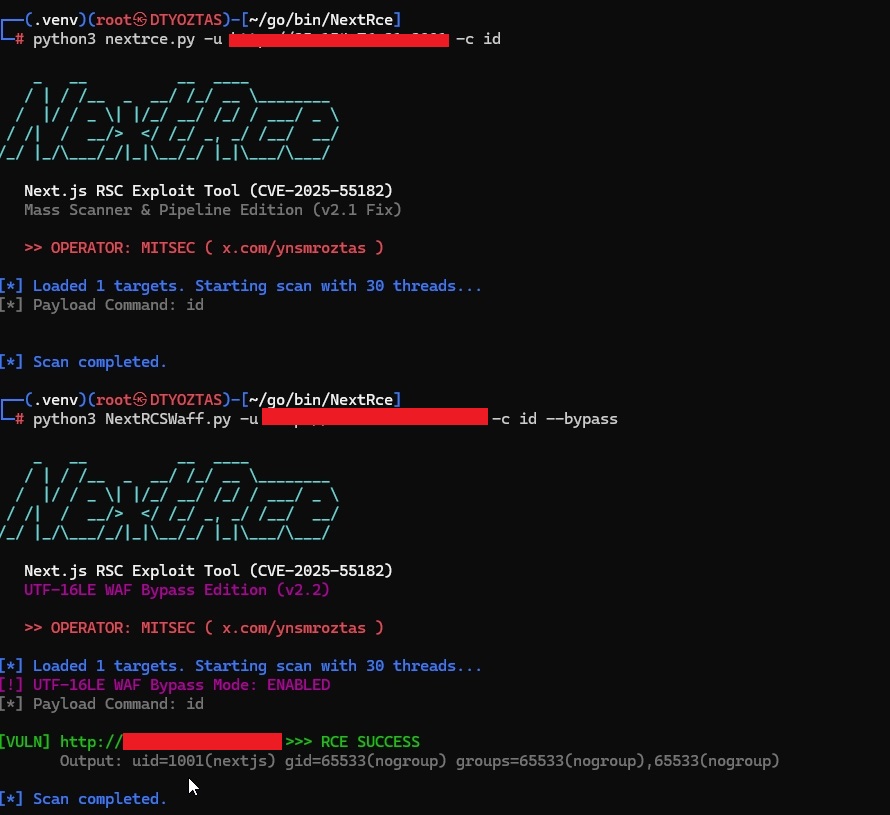 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 rohan-pt/cve-2025-26055
CVE Description
 cotherm/cve-2025-25705
Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…
 cotherm/cve-2025-25706
Detailed CVE-2025-25706 proof-of-concept demonstrating authenticated remote code execution via command injection in ProApps ping functionality,…
 mind2hex/cve-2021-31630-openplc-3-authenticated-rce
OpenPLC 3 WebServer Authenticated Remote Code Execution.
 codelatteid/carina
Webshell, Virtual Private Server (VPS) and cPanel Database
 asang17/cve-2021-40222
Remote Code Execution at Rittal
 ahmyth/ahmyth-android-rat
Android Remote Administration Tool
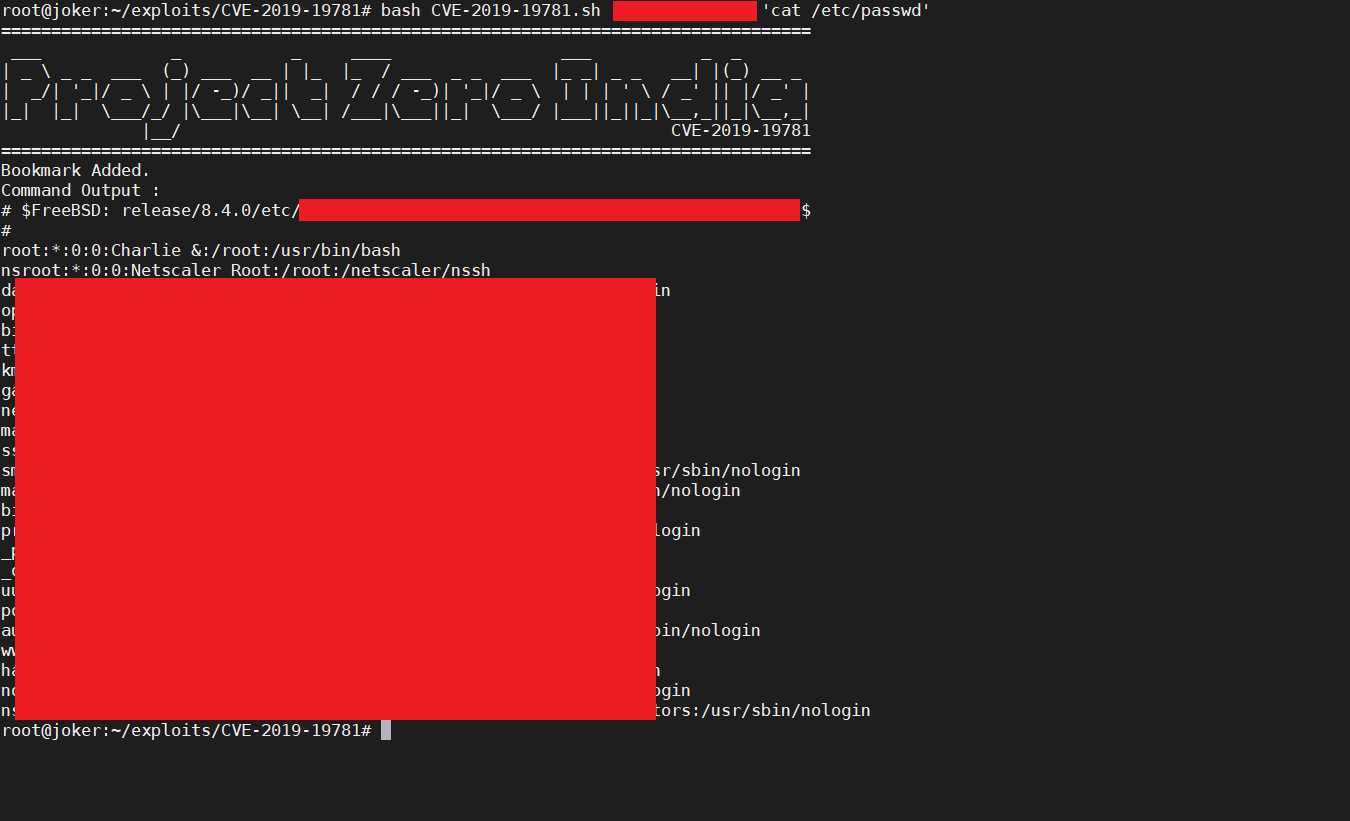 projectzeroindia/cve-2019-19781
Remote Code Execution Exploit for Citrix Application Delivery Controller and Citrix Gateway [ CVE-2019-19781 ]
 ianxtianxt/cve-2019-19781
Shell-based remote code execution exploit targeting CVE-2019-19781 in Citrix Application Delivery Controller and Citrix Gateway. Executes arbitrary…
 rmikehodges/hidensneak
a CLI for ephemeral penetration testing
 empireproject/empire-gui
Empire client application
 chrisallenlane/novahot
A webshell framework for penetration testers.
 payatu/cve-2017-5638
Apache Struts 2.0 RCE vulnerability - Allows an attacker to inject OS commands into a web application through the content-type header
 killswitch-gui/flask_heroku_redirector
flask heroku C2 redirector template