
CVE-2021-21425
 d4ytox/cve-2021-21425
CVE-2021-21425 - GravCMS 1.10.7 Unauthenticated RCE via Scheduler. Improved exploit with CLI args and auto base64 encoding.
command-and-controlexploitationpayload-generation+3
1
d4ytox/cve-2021-21425CVE-2021-21425 - GravCMS 1.10.7 Unauthenticated RCE via Scheduler. Improved exploit with CLI args and auto base64 encoding.
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 portbuster1337/cve-2026-52806
Gogs RCE via argument injection in git rebase (CWE-88) — Python PoC. CVE-2026-52806
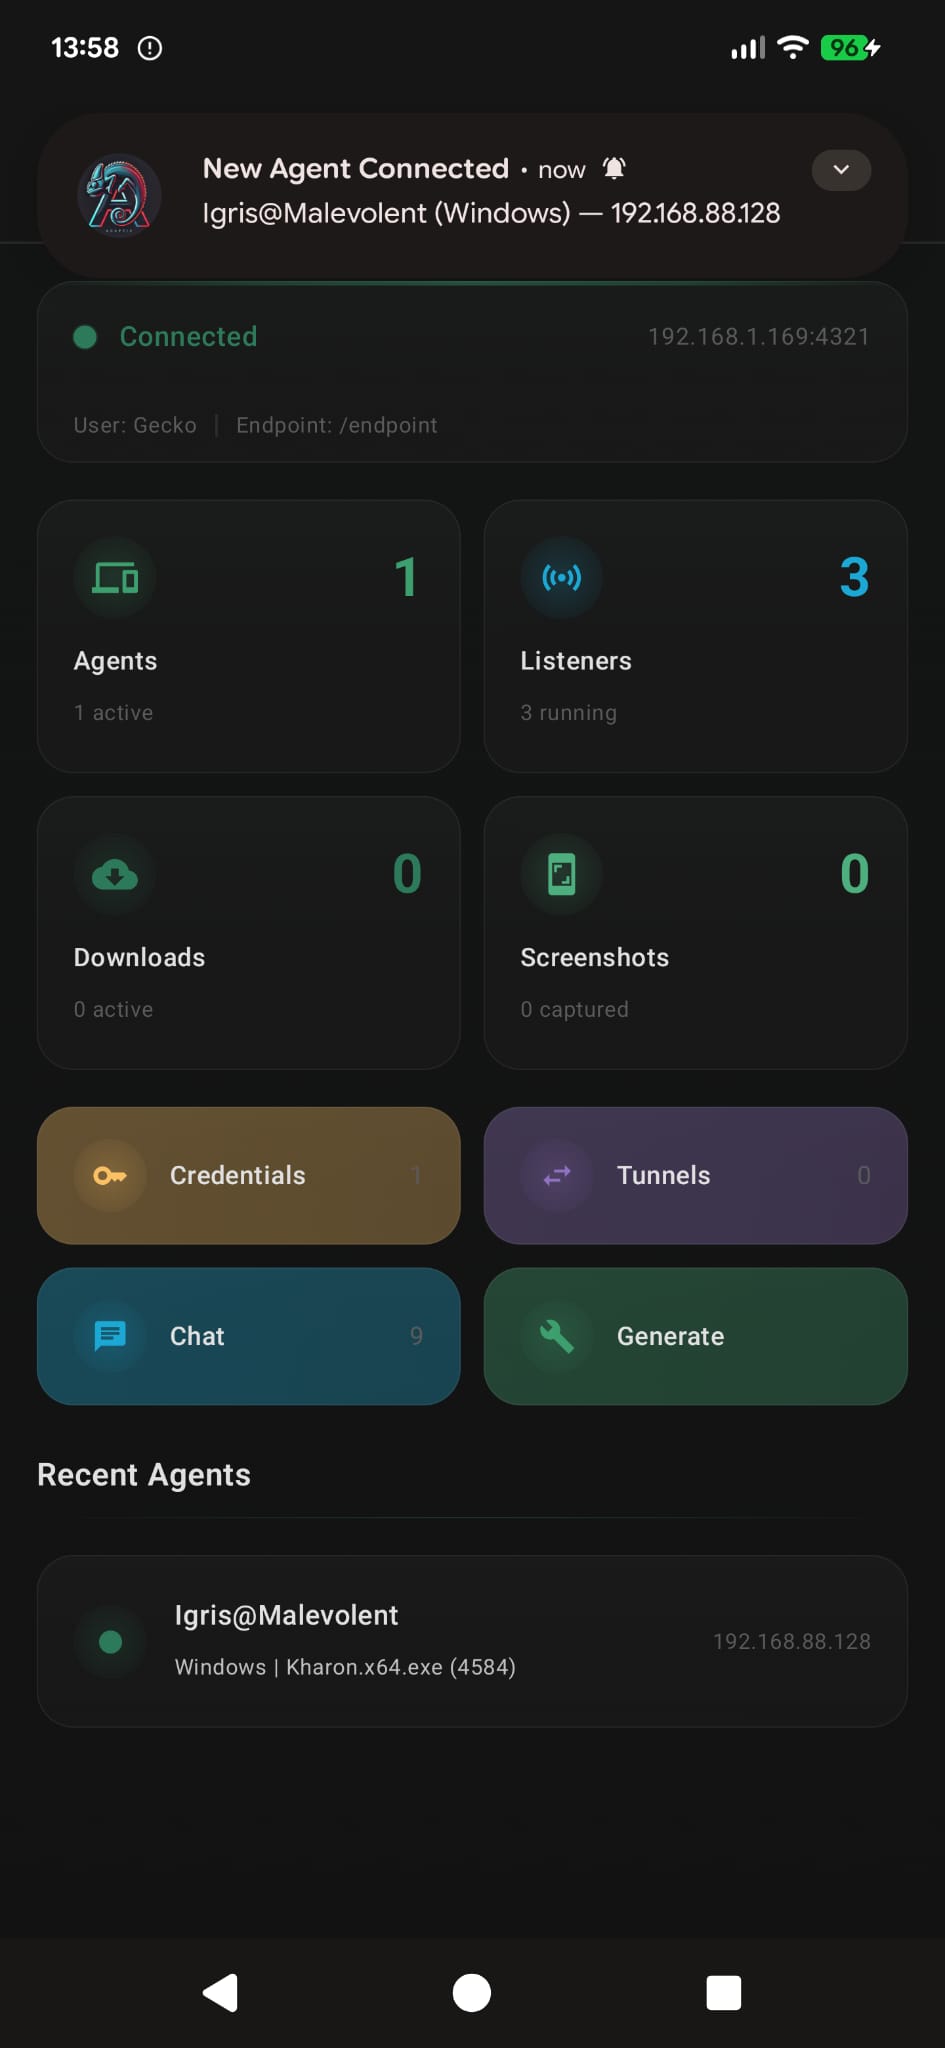 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 mantodkaz/cve-2023-34960
Automated exploit for Chamilo command injection vulnerability (CVE-2023-34960) with auto shell upload capability for penetration testing and…
 nu11secur1ty/sh1mazu
Meterpreter auto exploit program
 yt1g3r/cve-2020-0688_exp
CVE-2020-0688_EXP Auto trigger payload & encrypt method