
CVE-2024-36401-poc
 delt-a/cve-2024-36401-poc
Unauthenticated RCE exploit for GeoServer (CVE-2024-36401) via OGC filter XPath injection. Supports reverse shell and blind command execution with…
command-and-controlexploitationpenetration-testing+4
delt-a/cve-2024-36401-pocUnauthenticated RCE exploit for GeoServer (CVE-2024-36401) via OGC filter XPath injection. Supports reverse shell and blind command execution with…
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
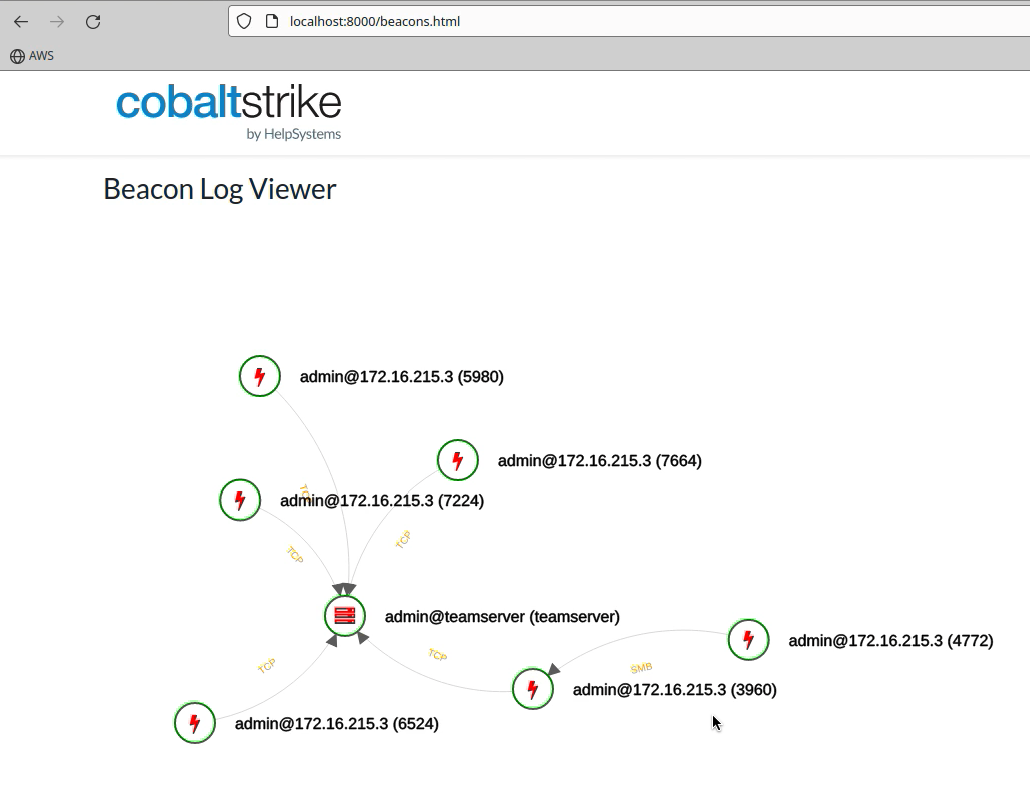 cobalt-strike/sleep_python_bridge
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
 kiexitdispatcher/goredops
🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…

 klezvirus/cve-2021-40444
CVE-2021-40444 - Fully Weaponized Microsoft Office Word RCE Exploit
 embee-research/agenttesla-config-extractor
Config extractor for AgentTesla - Discord/Telegram Variant
 fastmo/cve-2022-28672
CVE-2022-28672 Vulnerabilidad Foxit PDF Reader - UaF - RCE - JIT Spraying
 carbonblack/active_c2_ioc_public
Active C2 IoCs
 emcghee/payloadautomation
Automates Cobalt Strike payload development, testing, and deployment via a Python-to-Sleep bridge; includes artifact inspection, IoC tracking, and…
 navytitanium/eitest-tools-scripts-iocs
IOC feed and analysis toolkit for EITest campaigns, featuring C2 data decryption, victim payload decoding, and sinkhole log processing for threat…