
CVE-2026-31857
 0asylum/cve-2026-31857
CraftCMS has an RCE vulnerability via relational conditionals in the control panel
command-and-controlexploitationpenetration-testing+4
0asylum/cve-2026-31857CraftCMS has an RCE vulnerability via relational conditionals in the control panel
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
 gmh5225/github-gato
GitHub Self-Hosted Runner Enumeration and Attack Tool
 onyks-os/transparenttorproxy
A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
 faizanali8232/cve-exploit-research-development
A professional Python tool designed for educational penetration testing, demonstrating SSH vulnerabilities (CVE-2008-0166 / CVE-2008-1657) with…
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 davidcarliez/mythic_telegram_profile
Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
 whispergate/msteams
Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…
 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
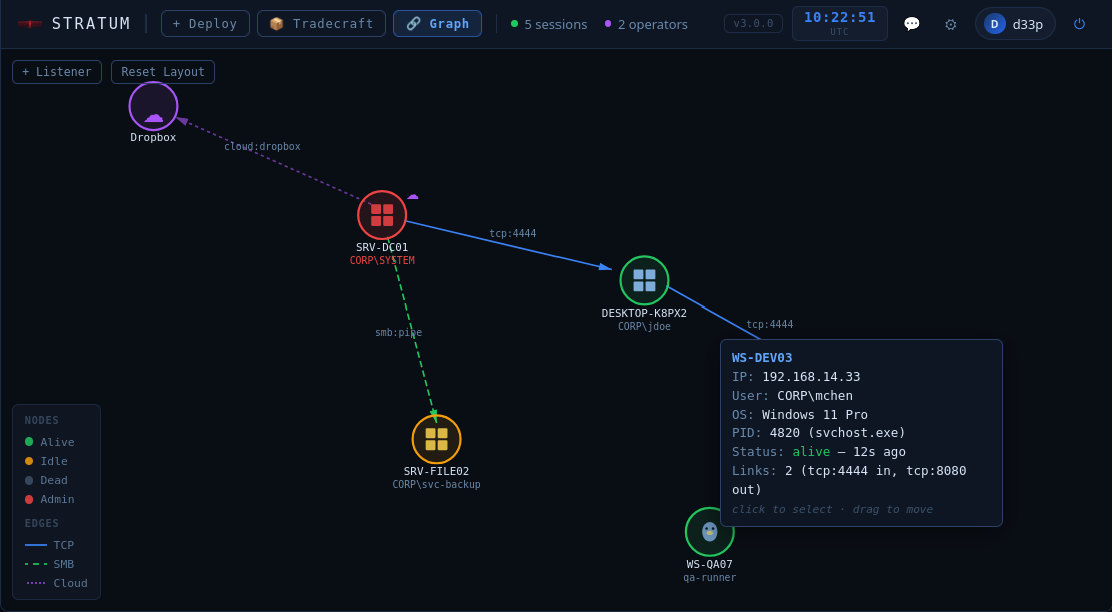 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
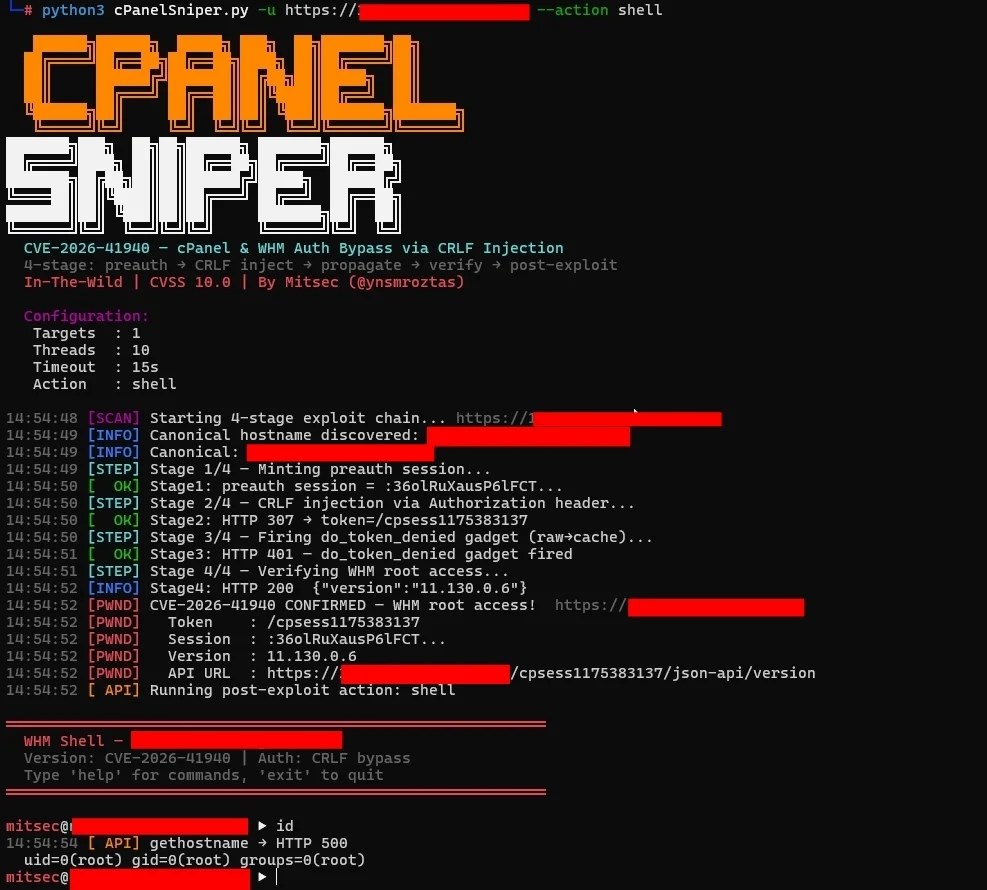 zwanski2019/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
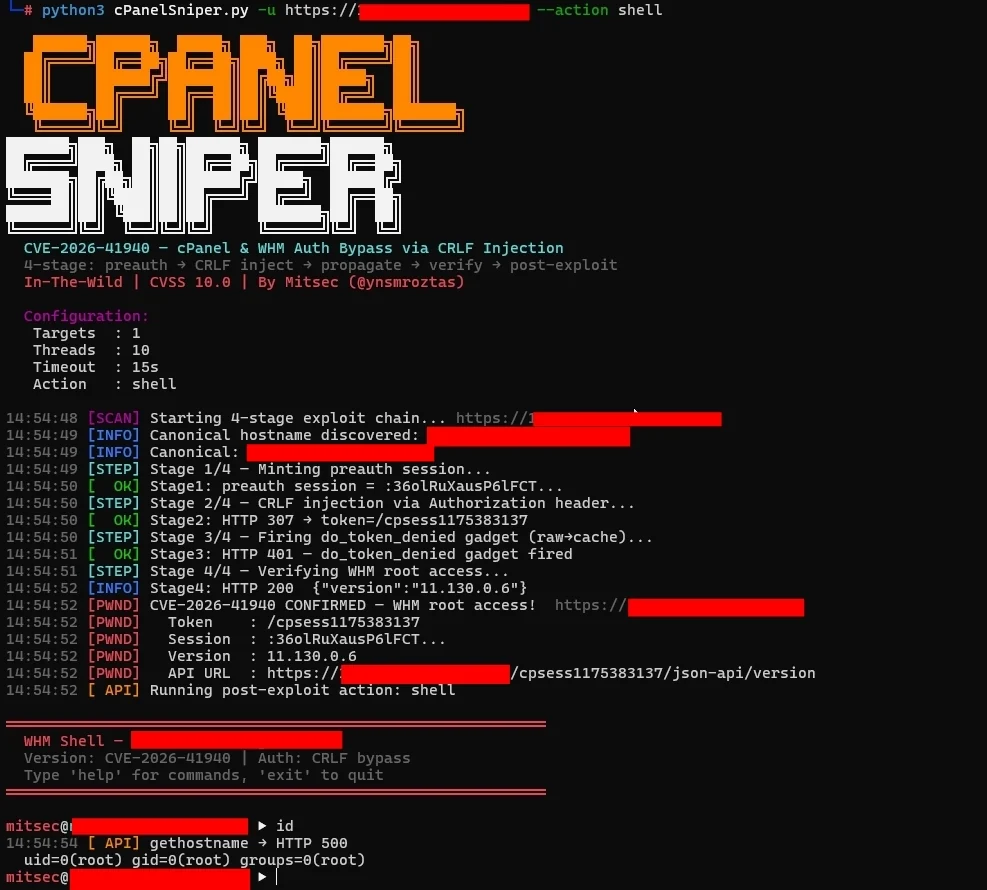 ynsmroztas/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
 rohmatariow/cve-2026-22812-exploit
Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…