mythic_telegram_profile

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…

Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…

CVE-2024-51567 is a Python PoC exploit targeting an RCE vulnerability in CyberPanel v2.3.6’s upgrademysqlstatus endpoint, bypassing CSRF protections.

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Simple PoC Python agent to showcase Havoc C2's custom agent interface. Not operationally safe or stable. Released with accompanying blog post as a…

macOS Initial Access Payload Generator

A PoC for achieving persistence via push notifications on Windows

Decrypted content of odd.tar.xz.gpg, swift.tar.xz.gpg and windows.tar.xz.gpg


Post Exploitation agent which uses a browser to do C2 operations.

DNS-Persist is a post-exploitation agent which uses DNS for command and control.

A pure python, post-exploitation, remote administration tool (RAT) for macOS / OS X.

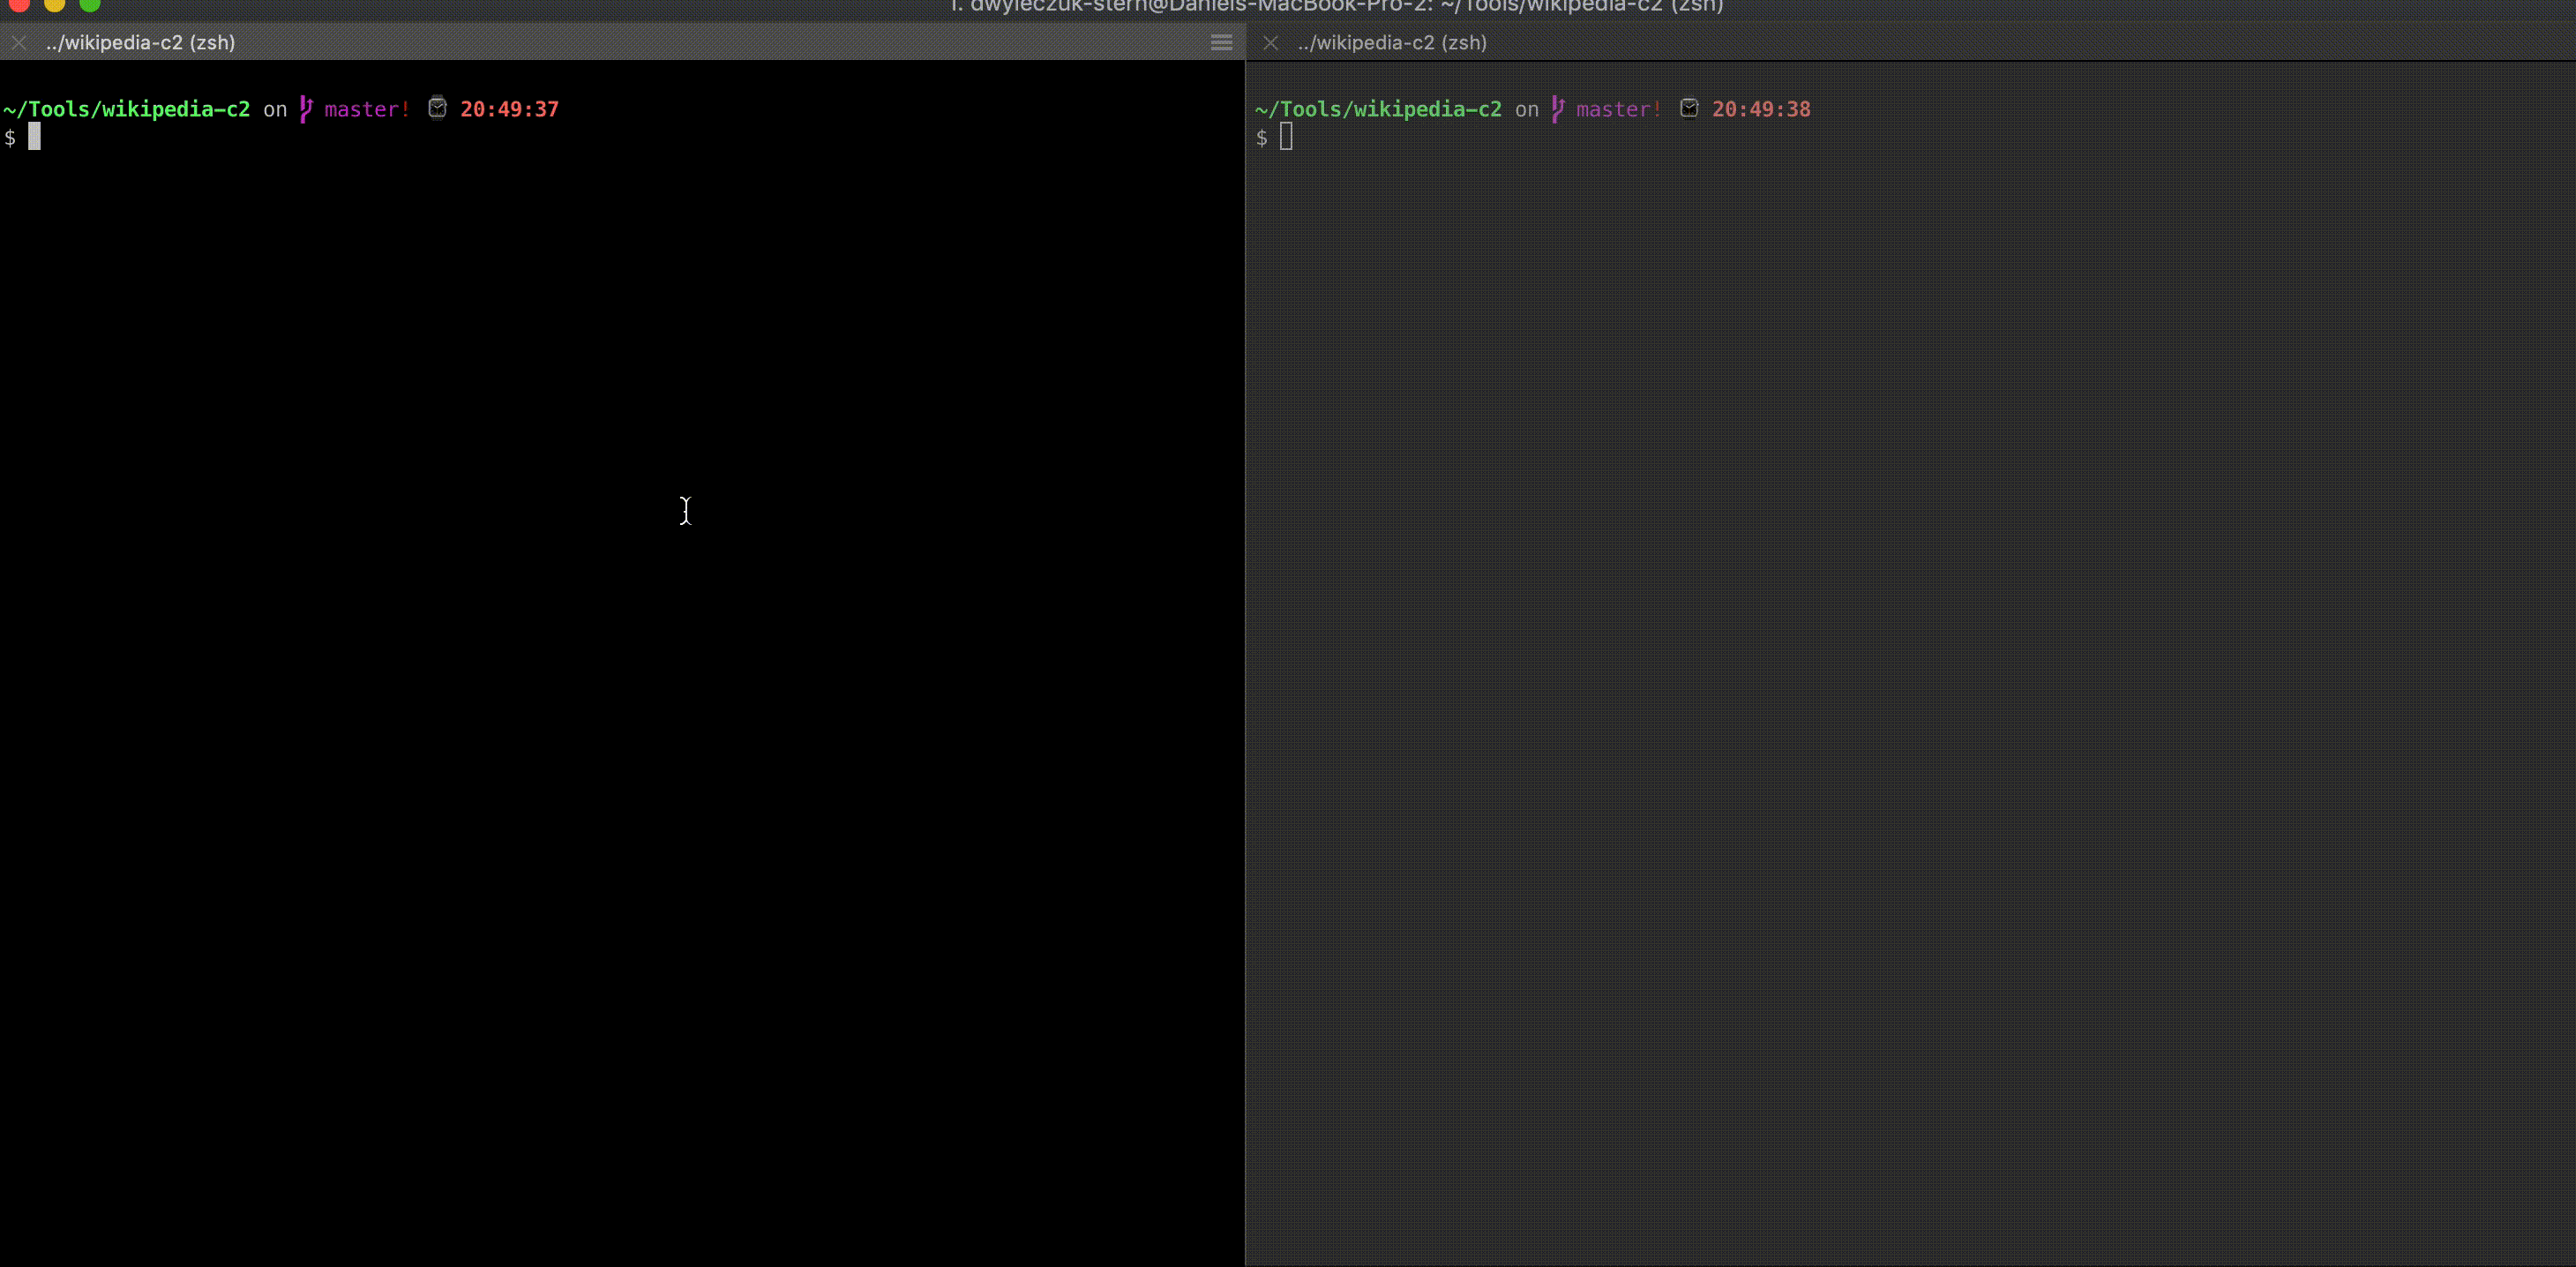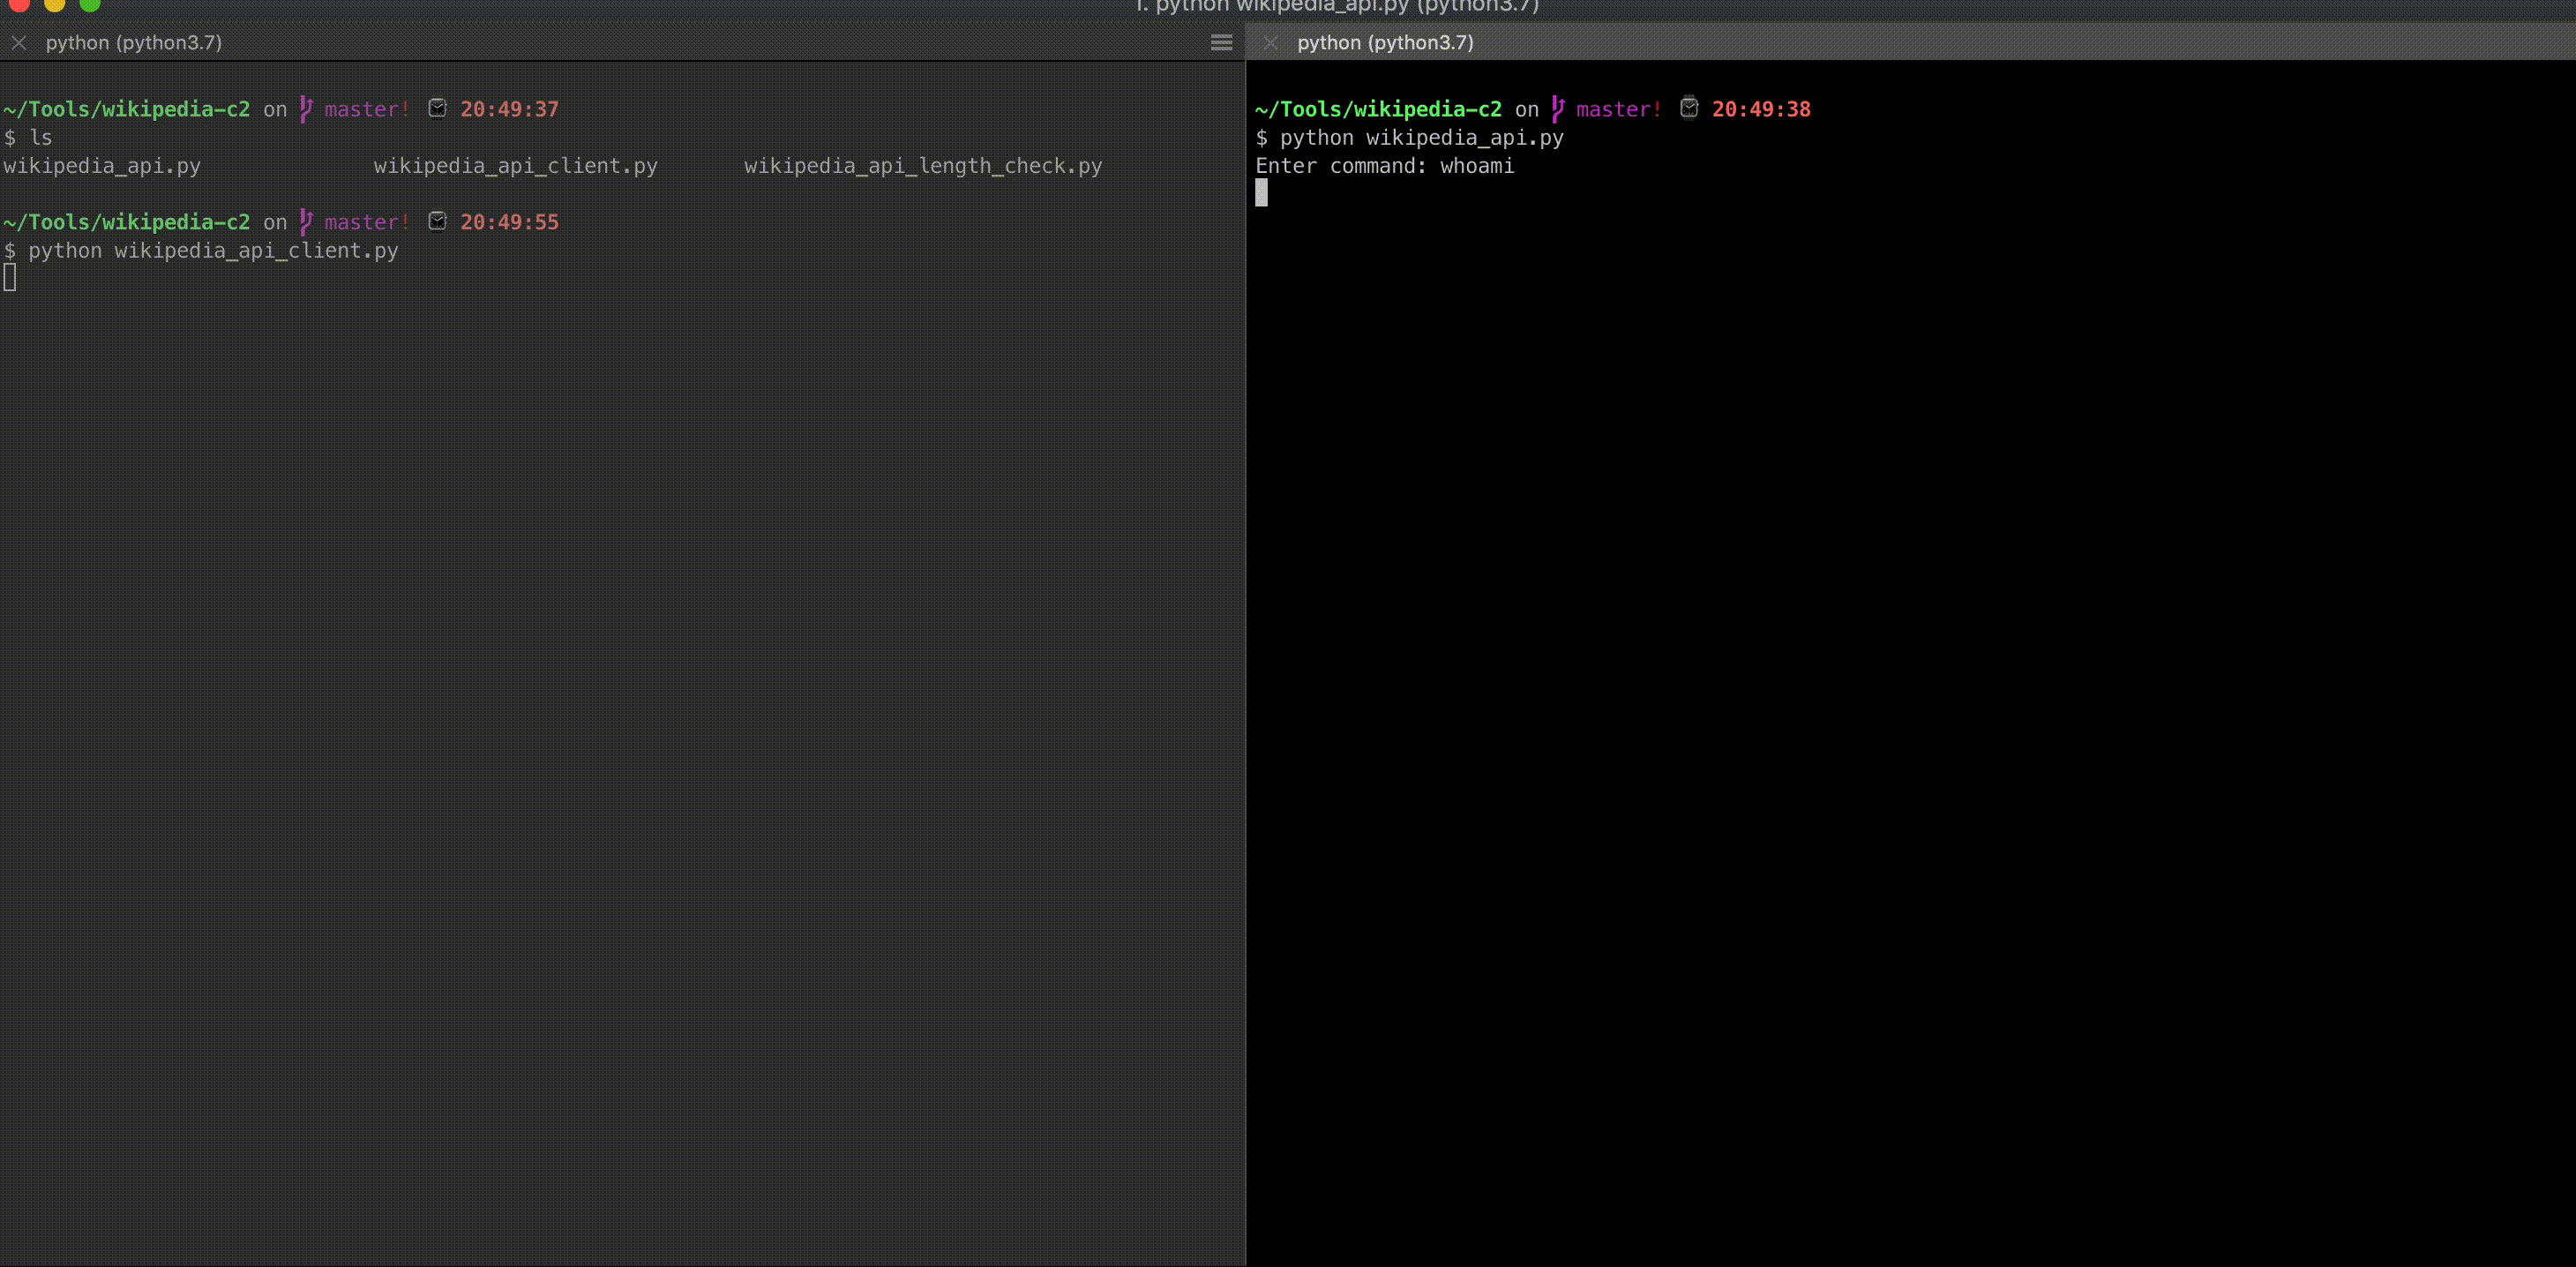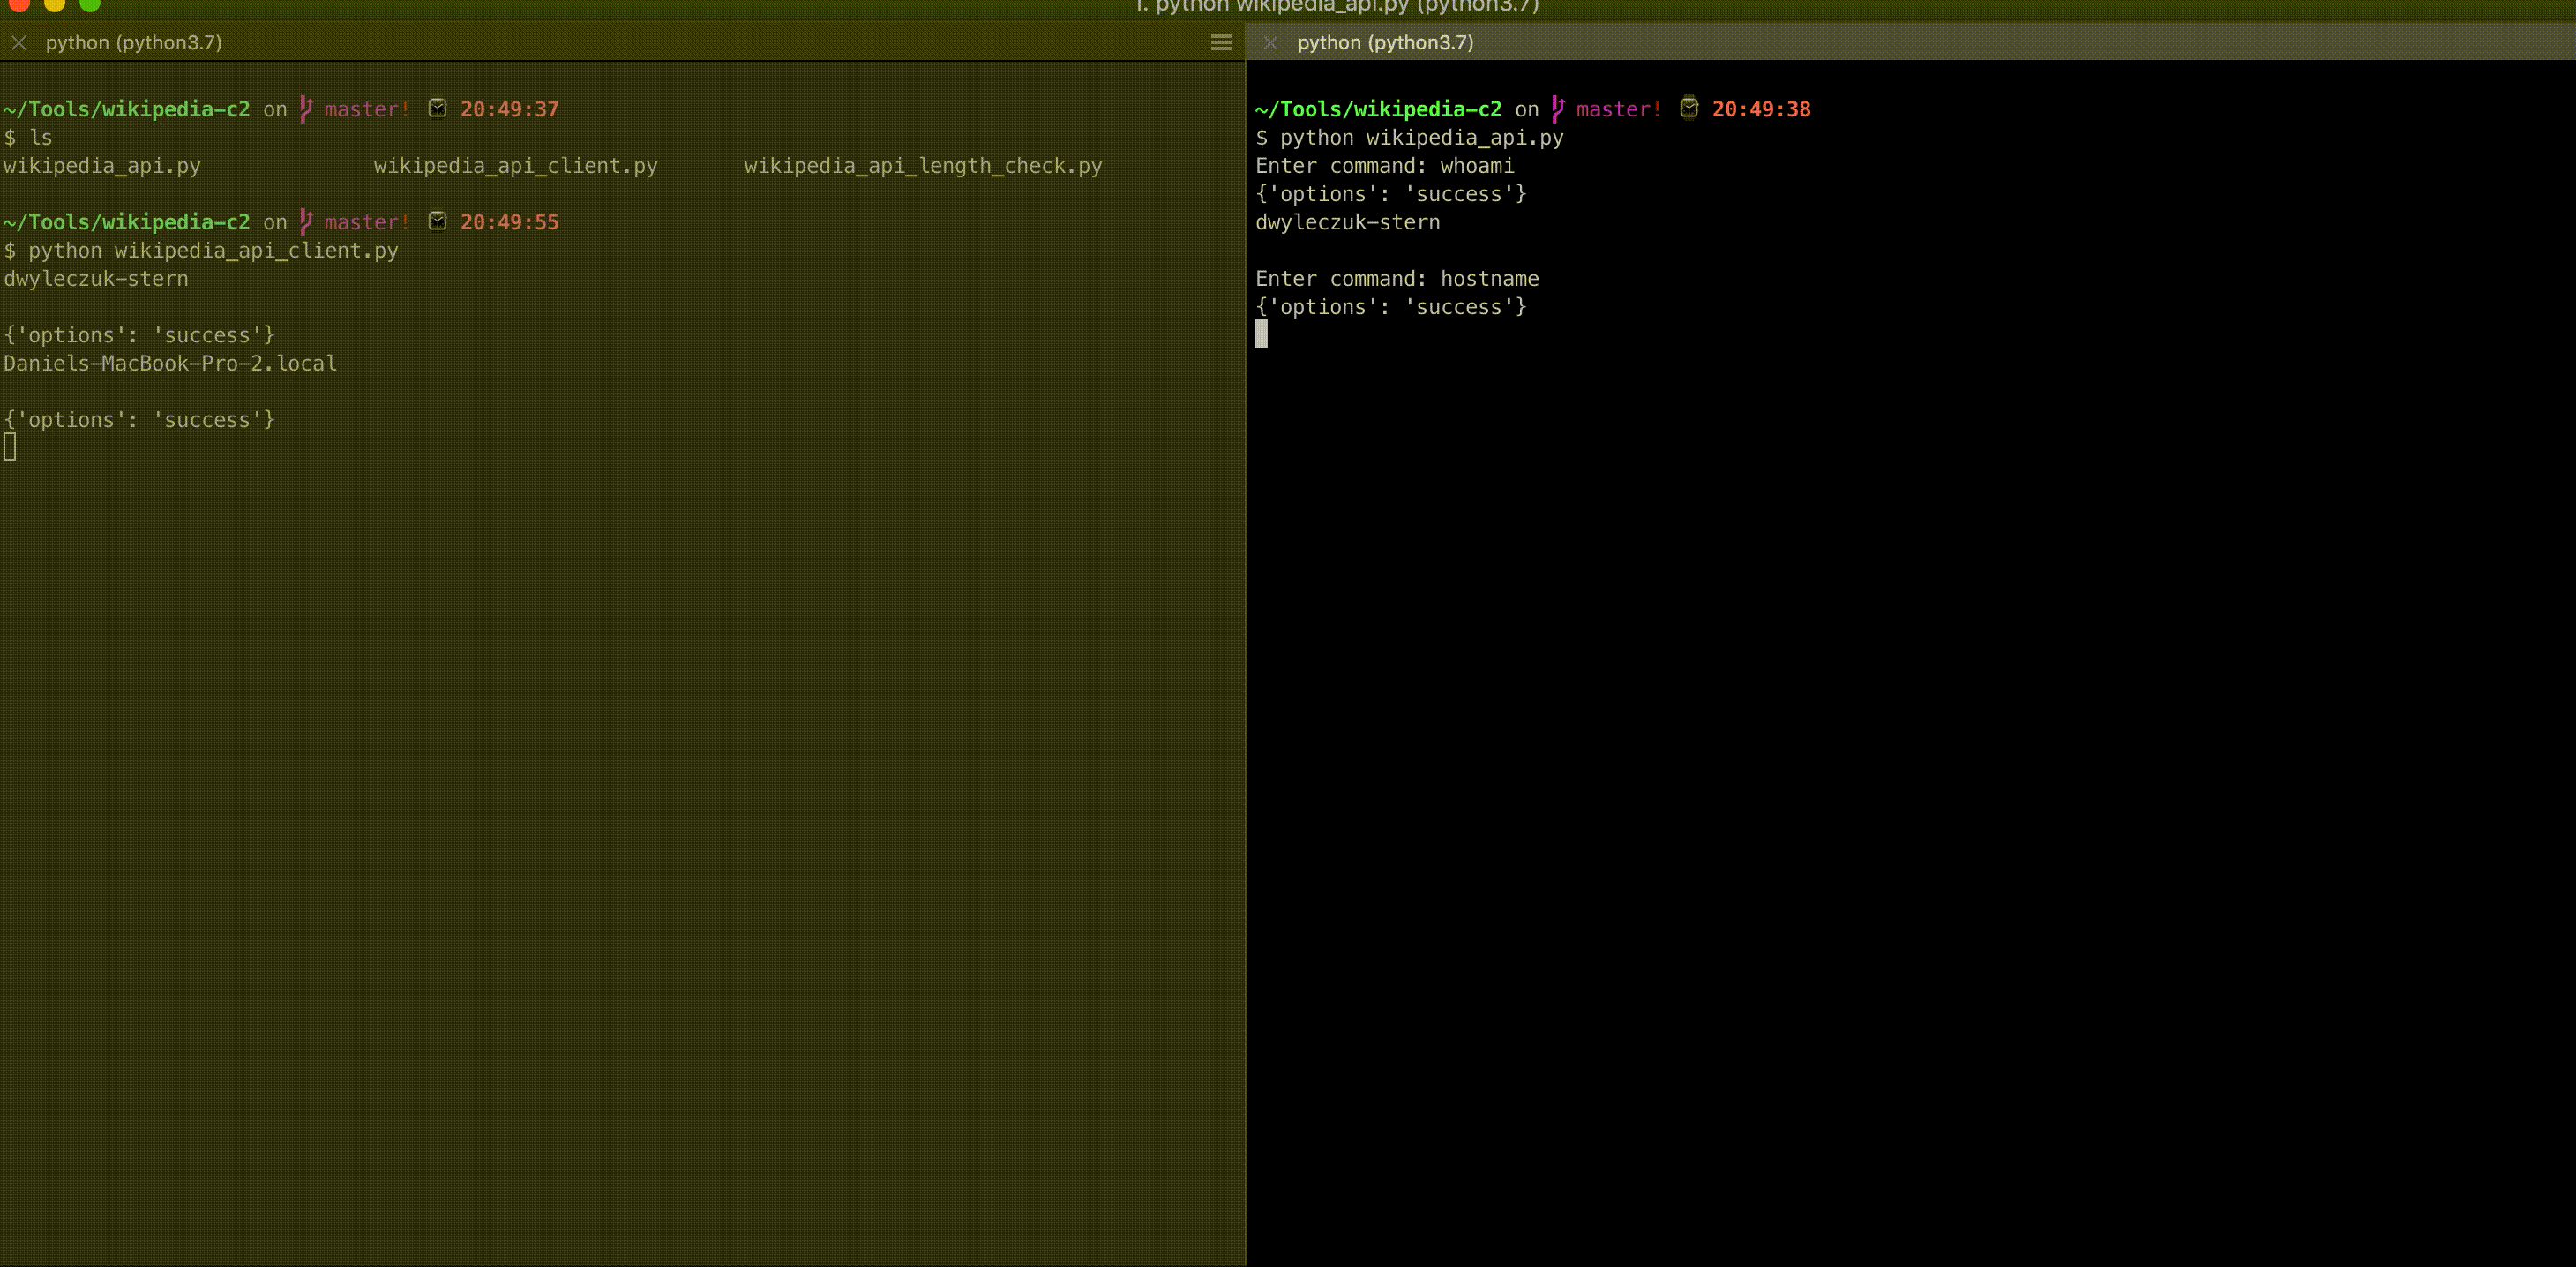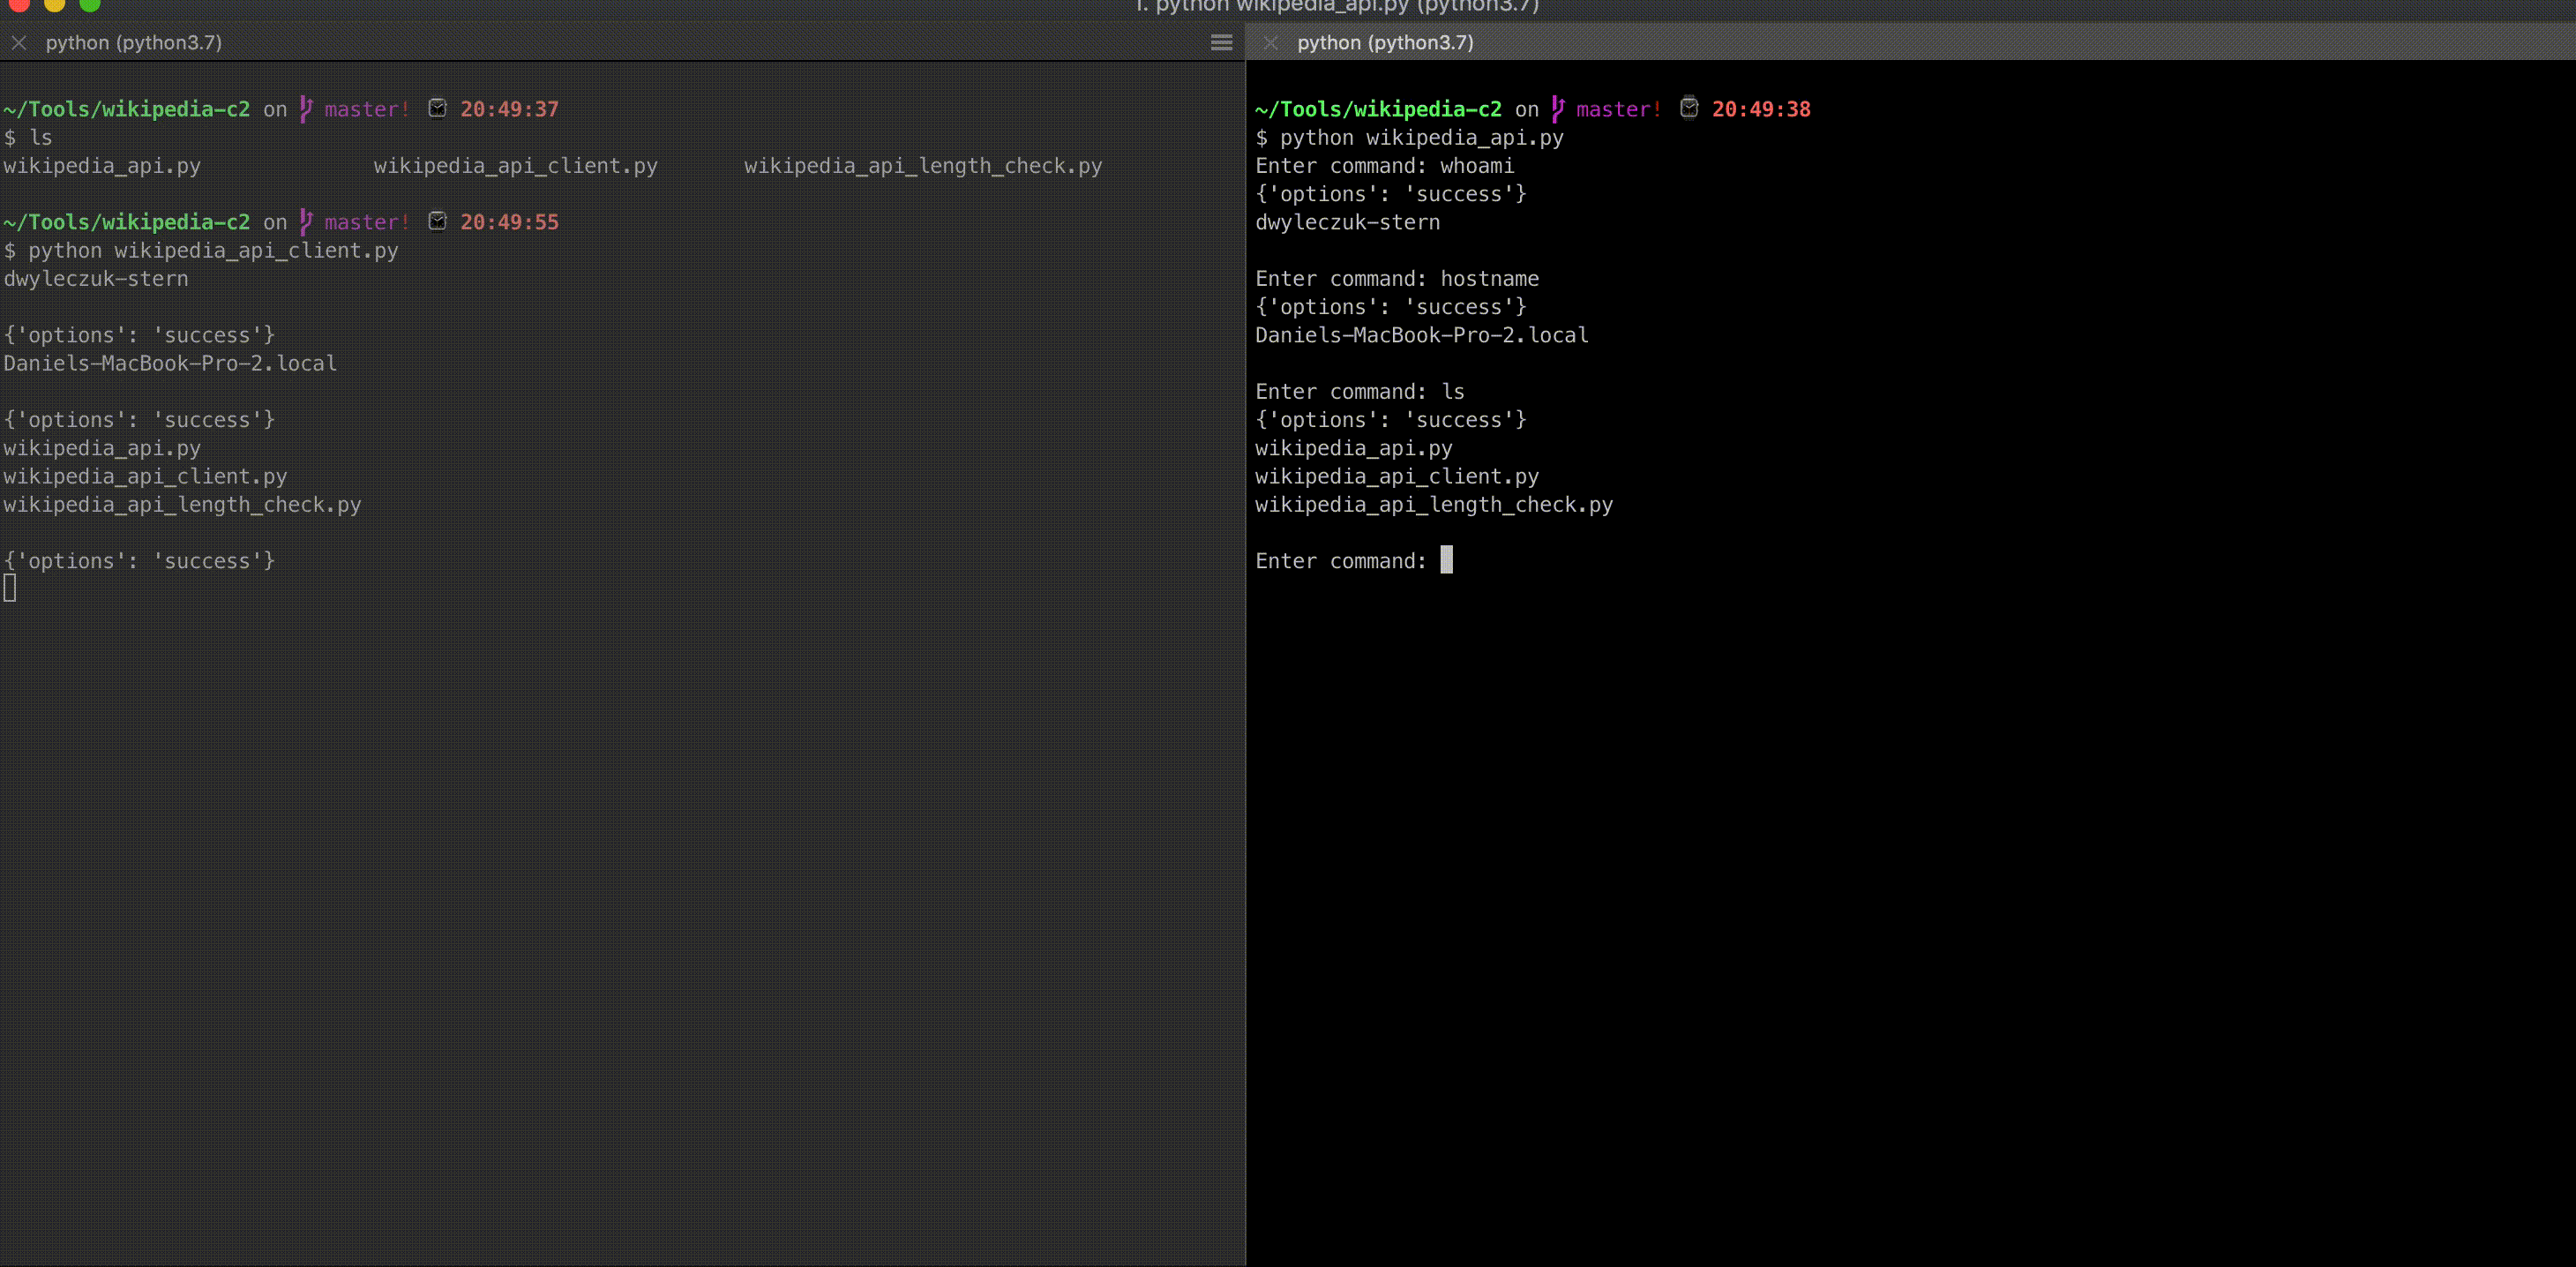
POC for utilizing wikipedia API for Command and Control

Windows Remote Post Breach Tool via Telegram

Powershell C2 Server and Implants

Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on

PoC C&C for the Industroyer malware