
CVE-2026-19586
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
command-and-controlcryptographyembedded-systems-security+6
2
mattgsys/cve-2026-19586Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 hackspeak/cve-2026-93958
Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…
 l0lsec/tapo-c260-rce
PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.
 hackedteam/rcs-db
Database components for RCS backend
 nccgroup/thetick
A simple embedded Linux backdoor.
 gelukcrab/react-server-components-rce
React Server Components 远程代码执行漏洞(CVE-2025-55182)
 passwa11/re11s_1.11-formaccept-commandinjection
CVE-2025-22912
 yezeting/cve-2021-41730
Proof-of-concept exploit for CVE-2021-41730, demonstrating remote command execution in TENDA AC15/AC6 routers via unvalidated formSetIptv()…
 jackdoan/tp-link-archerc5-rce
CVE-2018-19537
 p3ta00/react2shell-poc
CVE-2025-55182 React2Shell PoC - Critical RCE in React Server Components / Next.js. CVSS 10.0. Error-based exfil, reverse shell, interactive mode.
 nathanj60/react2shell-interactive
CVE-2025-55182 Interactive PoC - React Server Components RCE - Educational Security Research
 devvaibhav07/poc-cve-2025-55182
POC-CVE-2025-55182
 ryanhafid/poc_cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182 (React2Shell), a critical pre-auth RCE in React Server Components. Demonstrates insecure deserialization…
 mselbrede/gardyn
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 scumfrog/fiberbreak
React2Shell Exploitation Tool (CVE-2025-55182)
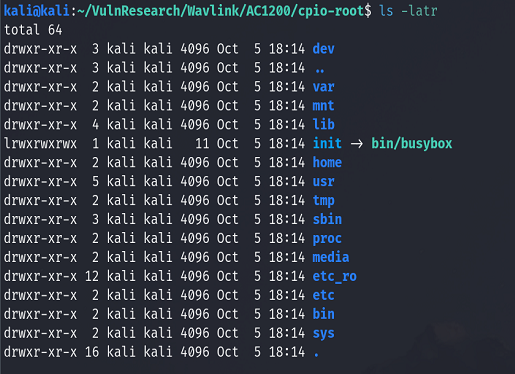 l41kaa/cve-2024-48705
Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
 hadimed/dsl-2750u-full-chain
CVE-2021-3707 , CVE-2021-3708
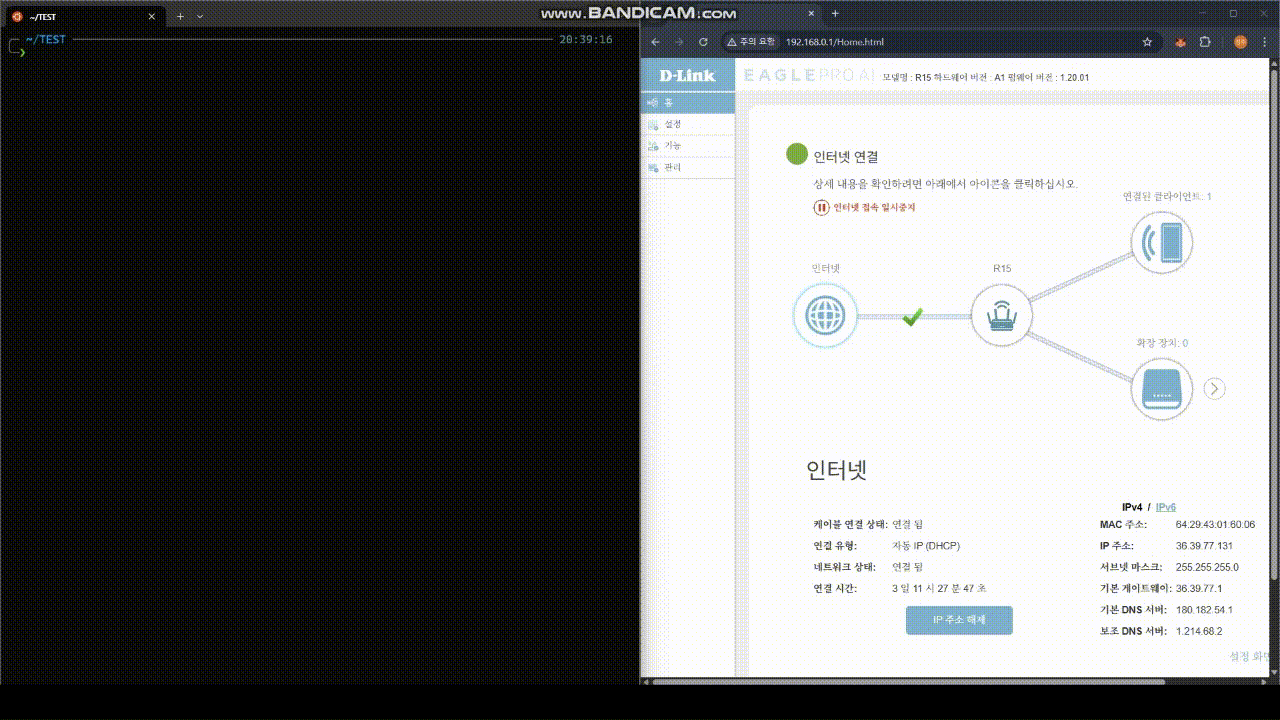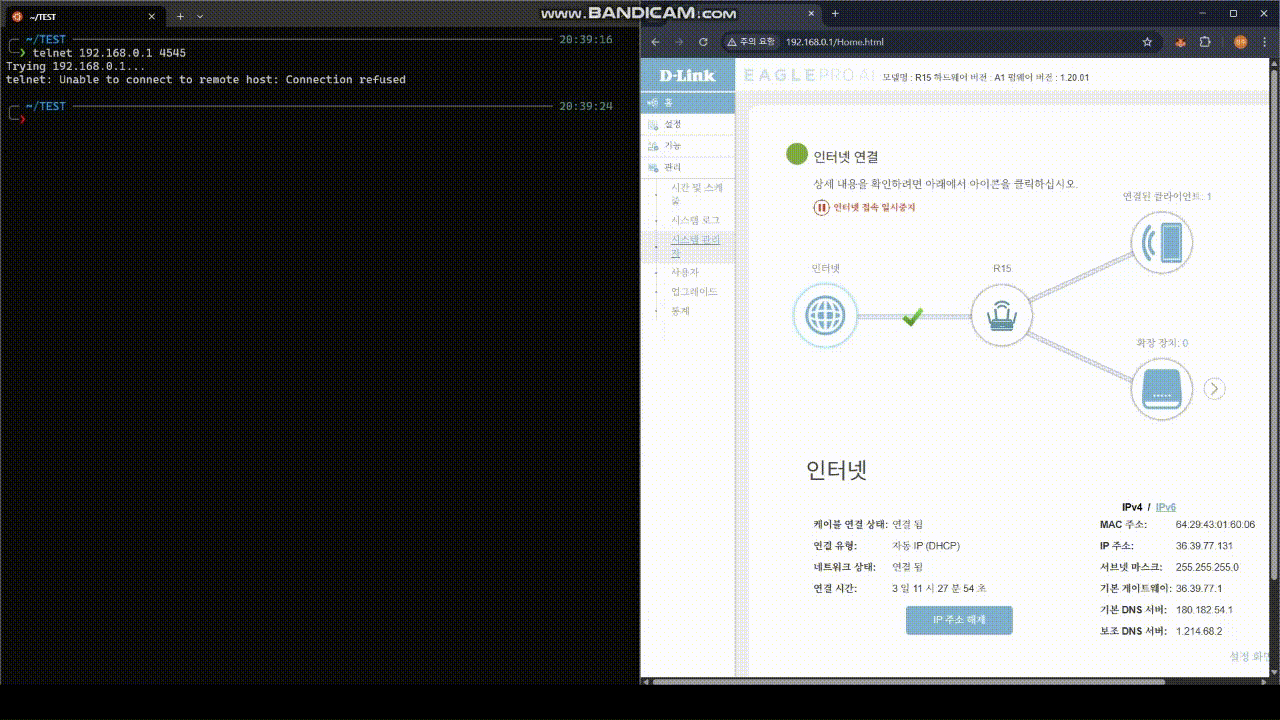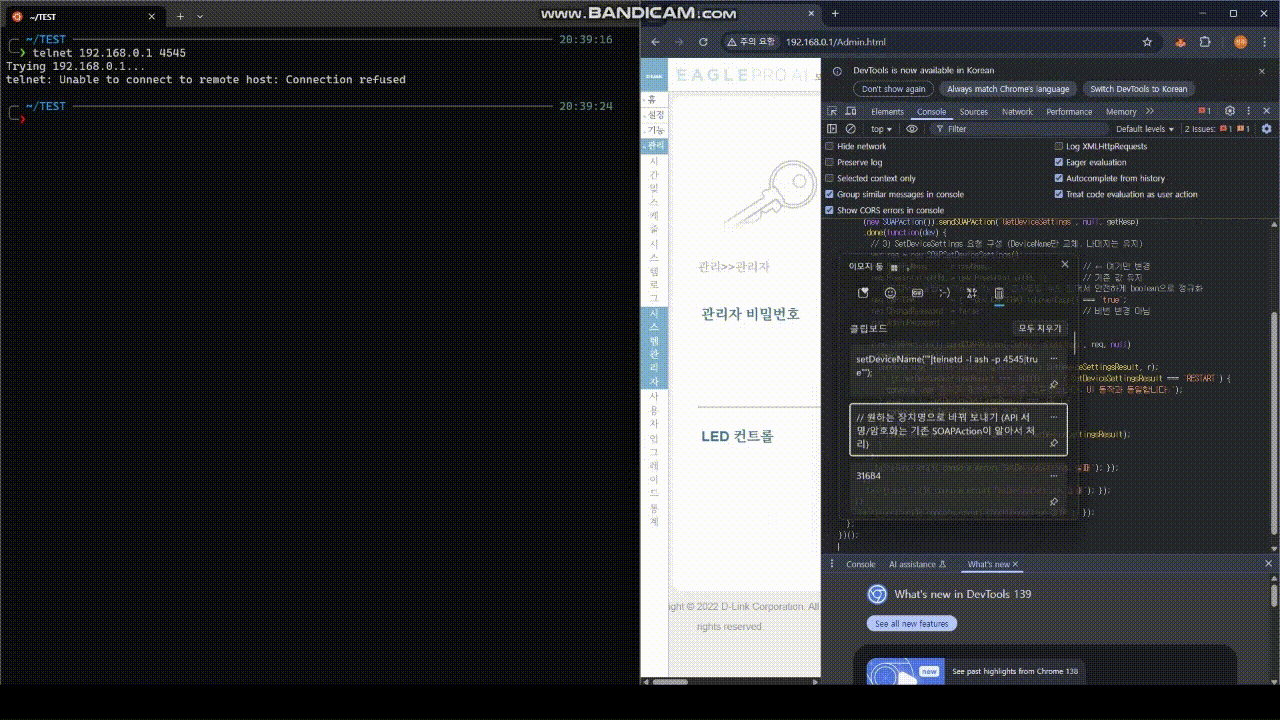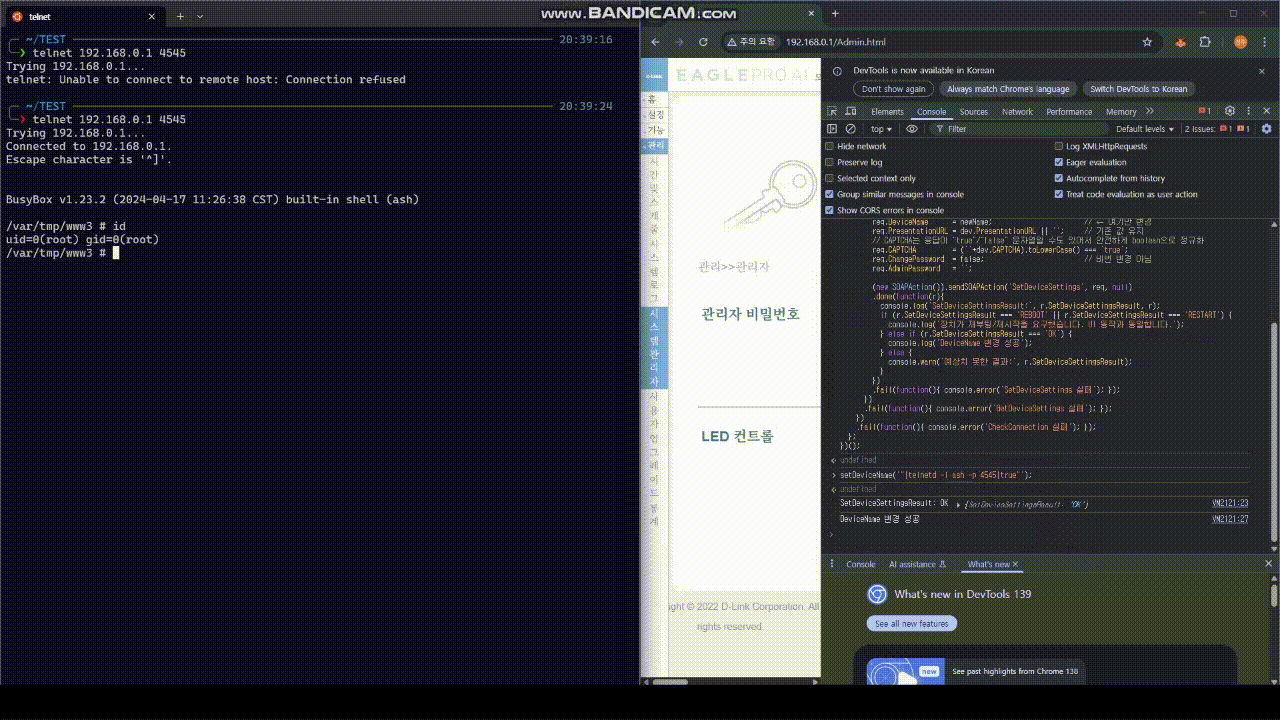 k0n9-log/cve-2025-60854
D-link AX1500 Vulnerability