

Project-CVE-2026-33017
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
command-and-controlexploitationpayload-development+6
1
e4zyy/project-cve-2026-33017CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 hrishikesh7665/follina_exploiter_cli
Exploit Microsoft Zero-Day Vulnerability Follina (CVE-2022-30190)
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 rix4uni/cve-2025-55182
A command-line tool for detecting CVE-2025-55182 and CVE-2025-66478 in Next.js applications using React Server Components.
 falcon-lnhg/strutsshell
Interactive command-line shell for exploiting Apache Struts CVE-2017-5638. Automates HTTP/HTTPS exploitation with real-time shell interaction on…
 abbarhissarh/follinaxploit
A Command Line based python tool for exploit Zero-Day vulnerability in MSDT (Microsoft Support Diagnostic Tool) also know as 'Follina' CVE-2022-30190.
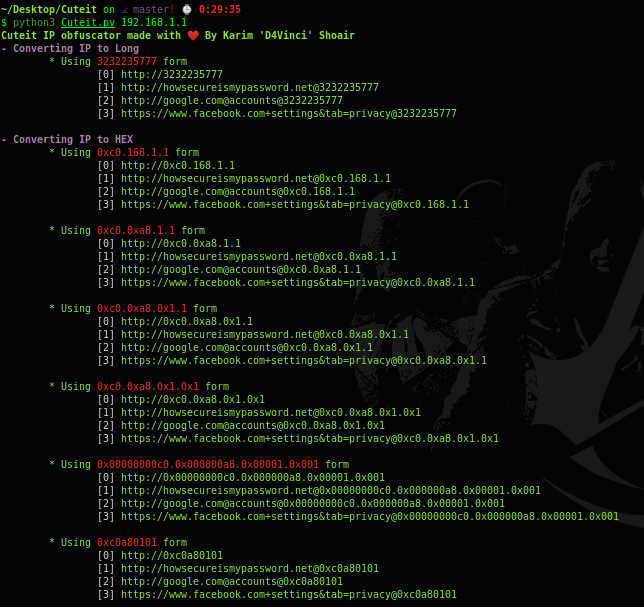 d4vinci/cuteit
IP obfuscator made to make a malicious ip a bit cuter
 d3adzo/shepard
In progress persistent download/upload/execution tool using Windows BITS.
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.