

metasploit-payloads
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
command-and-controlexploitationexploit-frameworks+9
2.1k
rapid7/metasploit-payloadsUnified repository for different Metasploit Framework payloads
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 naozibuhao/cve-2026-21962_java_gui_exploit_tool
Java GUI tool for exploiting CVE-2026-21962, an unauthenticated RCE in Oracle WebLogic Proxy Plug-In, enabling multi-target command execution via…
 mbadanoiu/java-servlets-shell
JSP-less Java Servlets Backdoor inspired by https://www.redteam-pentesting.de/files/redteam-jboss.tar.gz
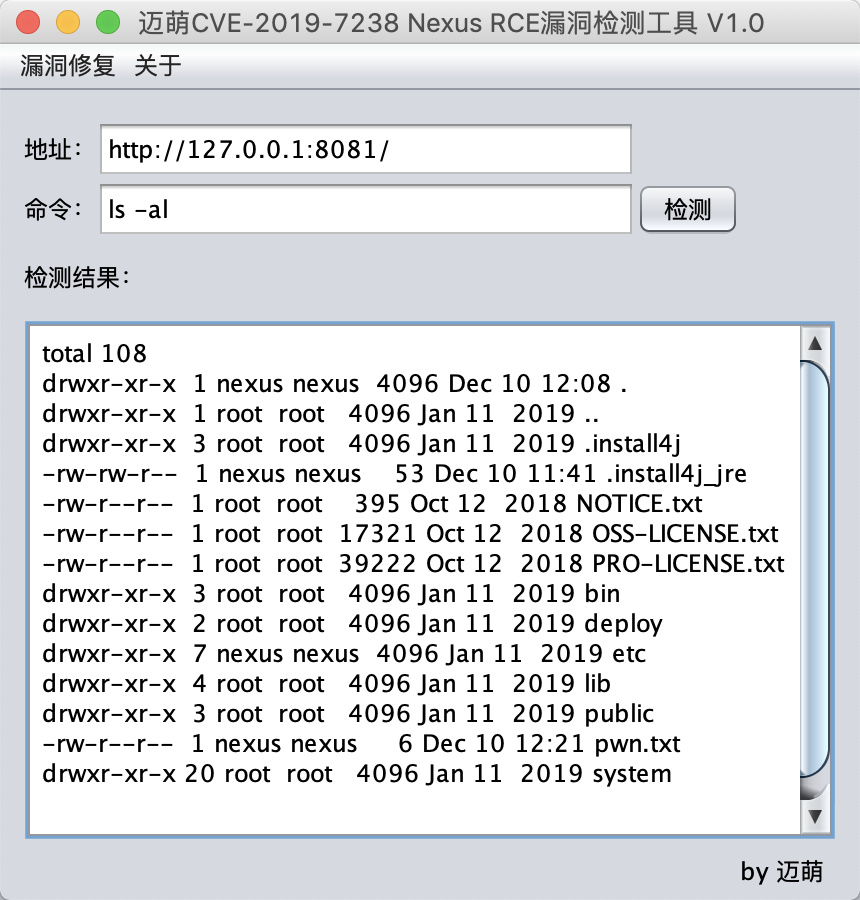 magicming200/cve-2019-7238_nexus_rce_tool
CVE-2019-7238 Nexus RCE漏洞图形化一键检测工具。CVE-2019-7238 Nexus RCE Vul POC Tool.
 libraggbond/cve-2018-3191
CVE-2018-3191 反弹shell
 designativedave/androrat
Remote Administration Tool for Android devices
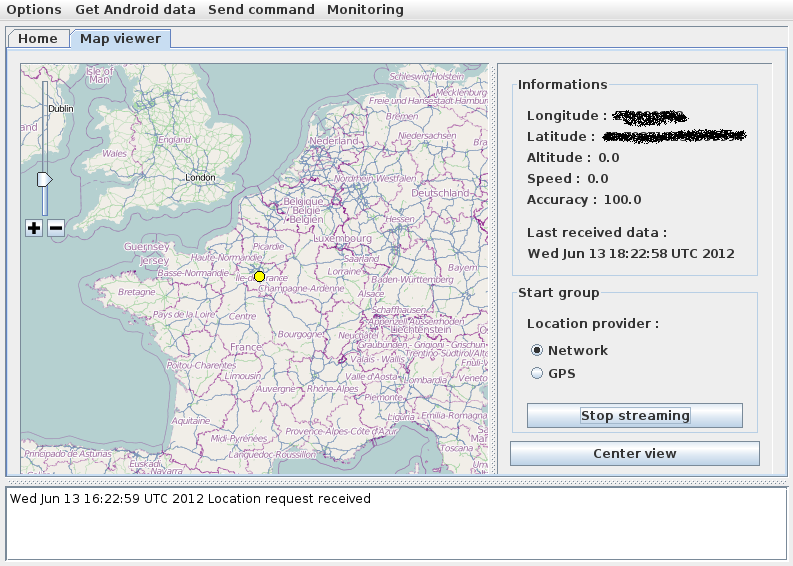
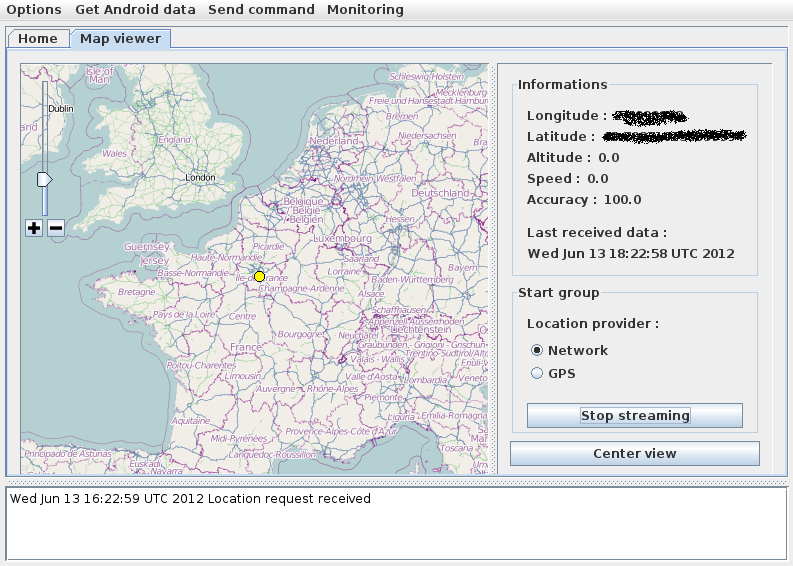 the404hacking/androrat
AndroRAT | Remote Administrator Tool for Android OS Hacking
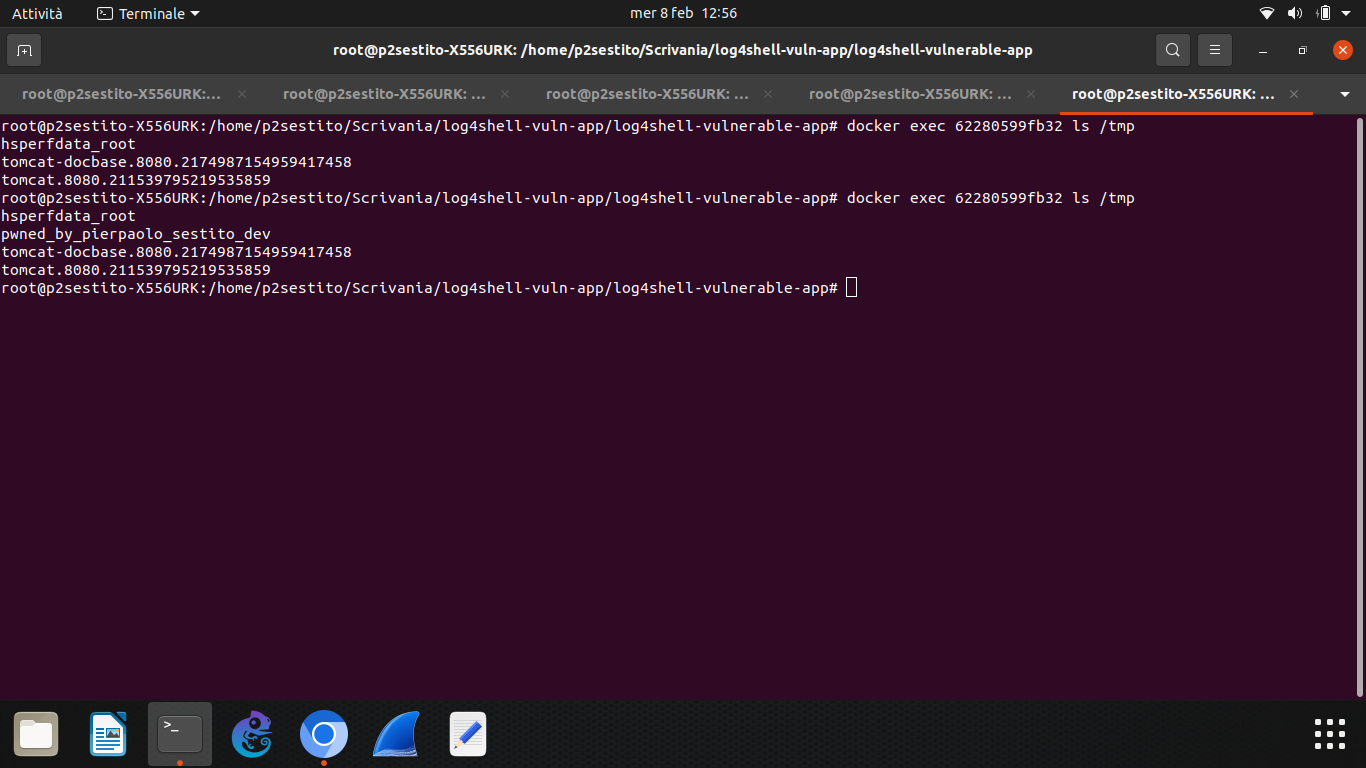 pierpaolosestito-dev/log4shell-cve-2021-44228-poc
CVE 2021-44228 Proof-of-Concept. Log4Shell is an attack against Servers that uses vulnerable versions of Log4J.
 delt-a/cve-2024-36401-poc
Unauthenticated RCE exploit for GeoServer (CVE-2024-36401) via OGC filter XPath injection. Supports reverse shell and blind command execution with…
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 maskcybersecurityteam/cve-2022-26134_behinder_memshell
Java-based exploit for CVE-2022-26134 that deploys a Behinder memory shell on vulnerable Atlassian Confluence servers for remote command execution.
 jeffli1024/log4j-rce-test
Quick test environment for CVE-2021-44228 Log4j RCE vulnerability with a built-in exploit server and customizable payload execution.
 erpscanteam/cve-2018-2380
PoC of Remote Command Execution via Log injection on SAP NetWeaver AS JAVA CRM
 dsibilio/follina-spring
Server to host/activate Follina payloads & generator of malicious Word documents exploiting the MS-MSDT protocol. (CVE-2022-30190)
 guigui237/expoitation-de-la-vuln-rabilit-cve-2022-22965
Python exploit for CVE-2022-22965 (Spring4Shell) RCE vulnerability in Java Spring Core. Injects a JSP webshell via Tomcat log configuration to…
 willian-2-0-0-1/log4j-exploit-cve-2021-44228
Exploit tool for CVE-2021-44228 (Log4Shell) that sets up a malicious LDAP server and delivers a Java payload to achieve remote code execution on…