CVE-2026-26331
 dxleryt/cve-2026-26331
Proof-of-concept demonstrating arbitrary command injection via yt-dlp's --netrc-cmd option, exploiting shell metacharacters in URLs to execute…
command-and-controlexploitationpayload-development+2
1
dxleryt/cve-2026-26331Proof-of-concept demonstrating arbitrary command injection via yt-dlp's --netrc-cmd option, exploiting shell metacharacters in URLs to execute…
 simoesctt/ctt-mailpit-rce-v1.0---temporal-resonance-mail-server-takeover
Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…
 m4rm0k/talkingben
UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
 daniomass/slivermirage
Crystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
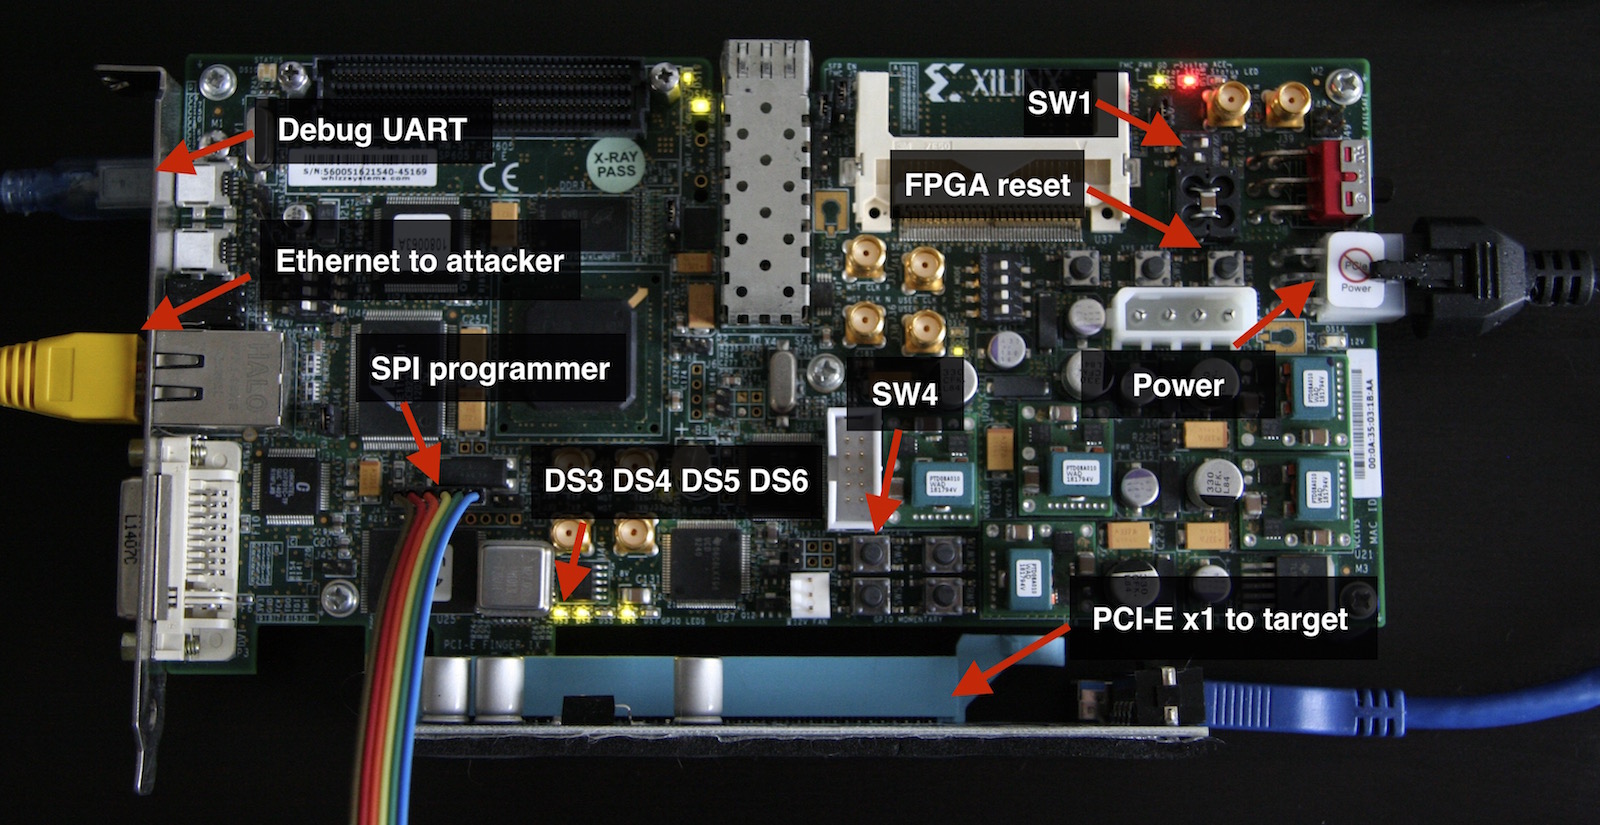 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
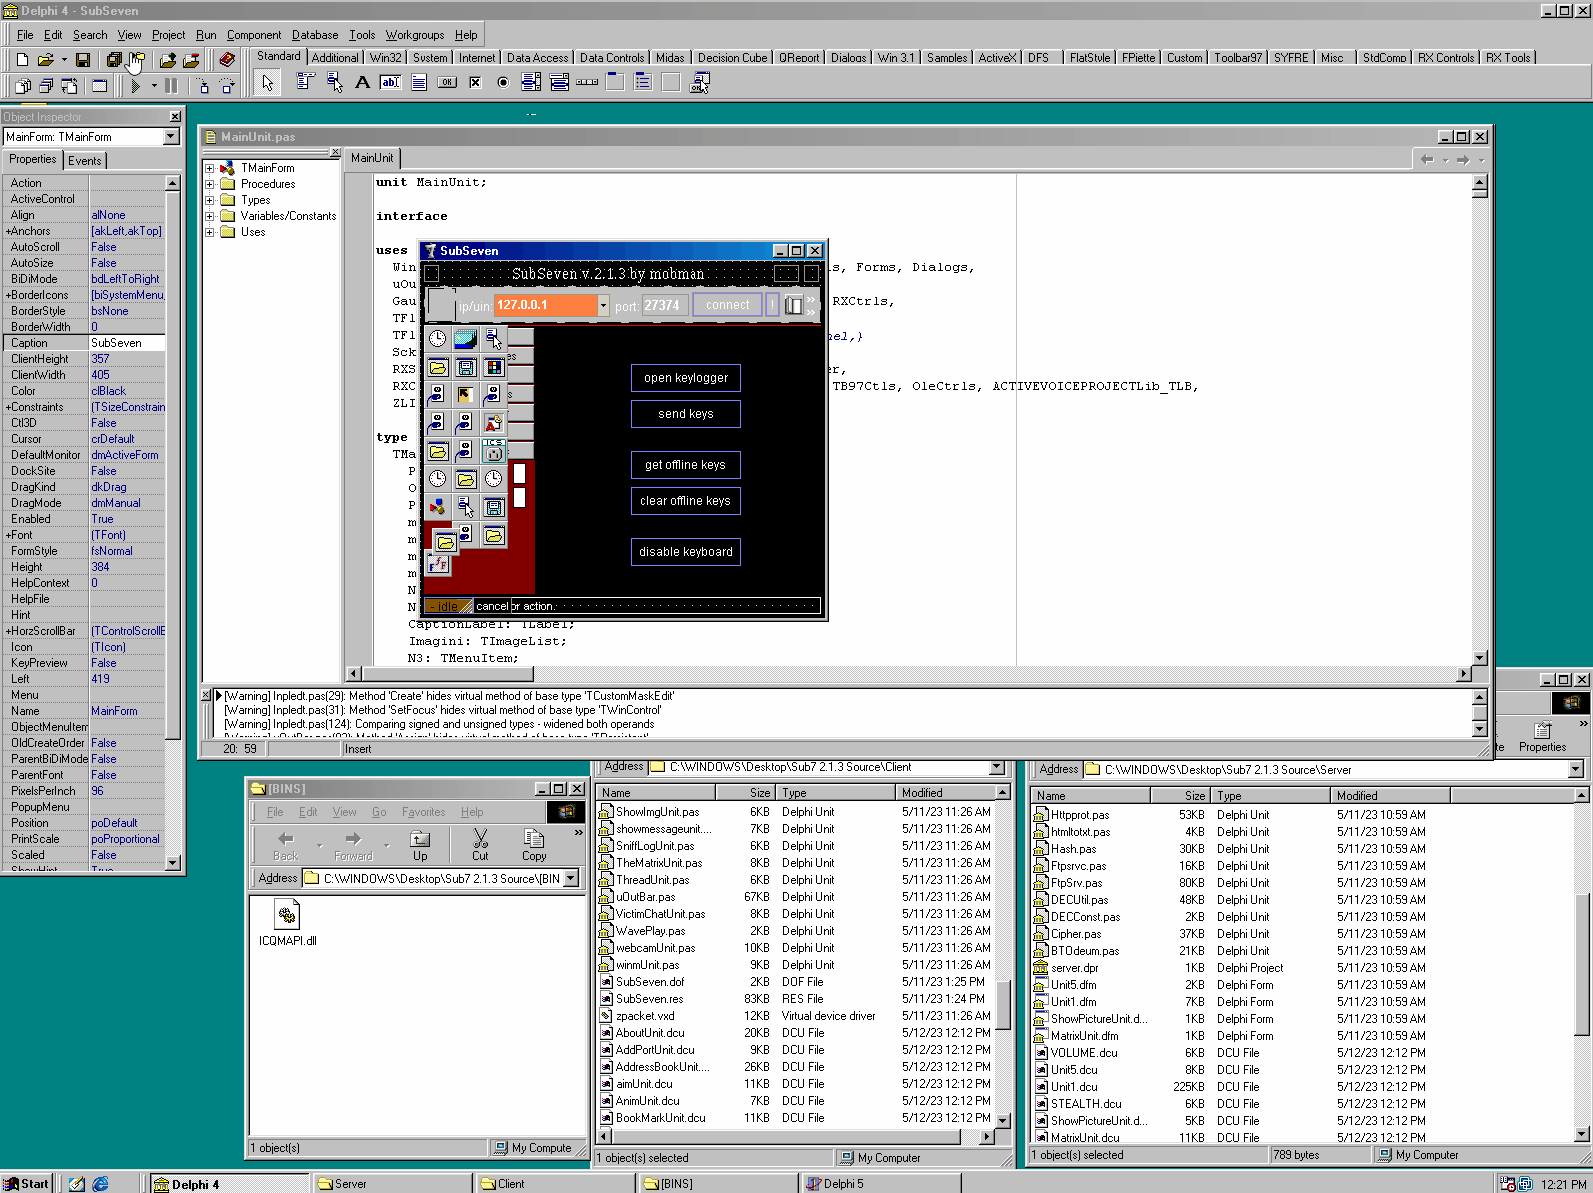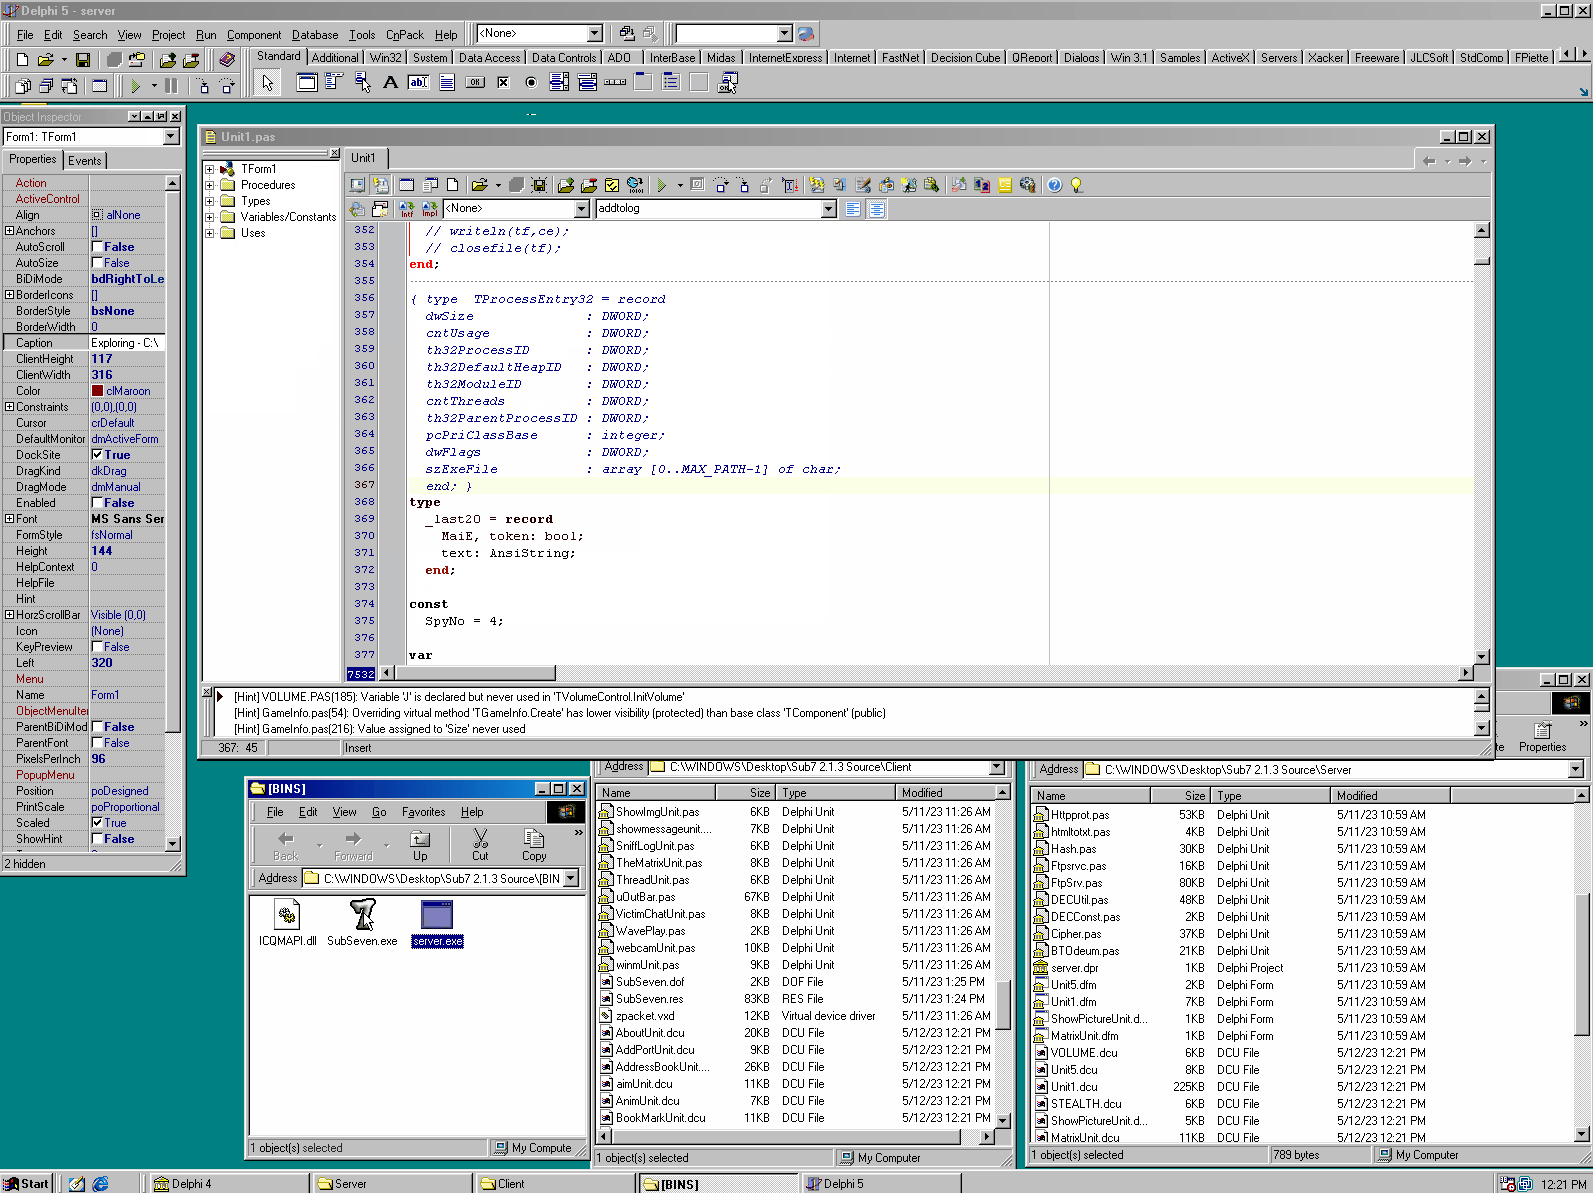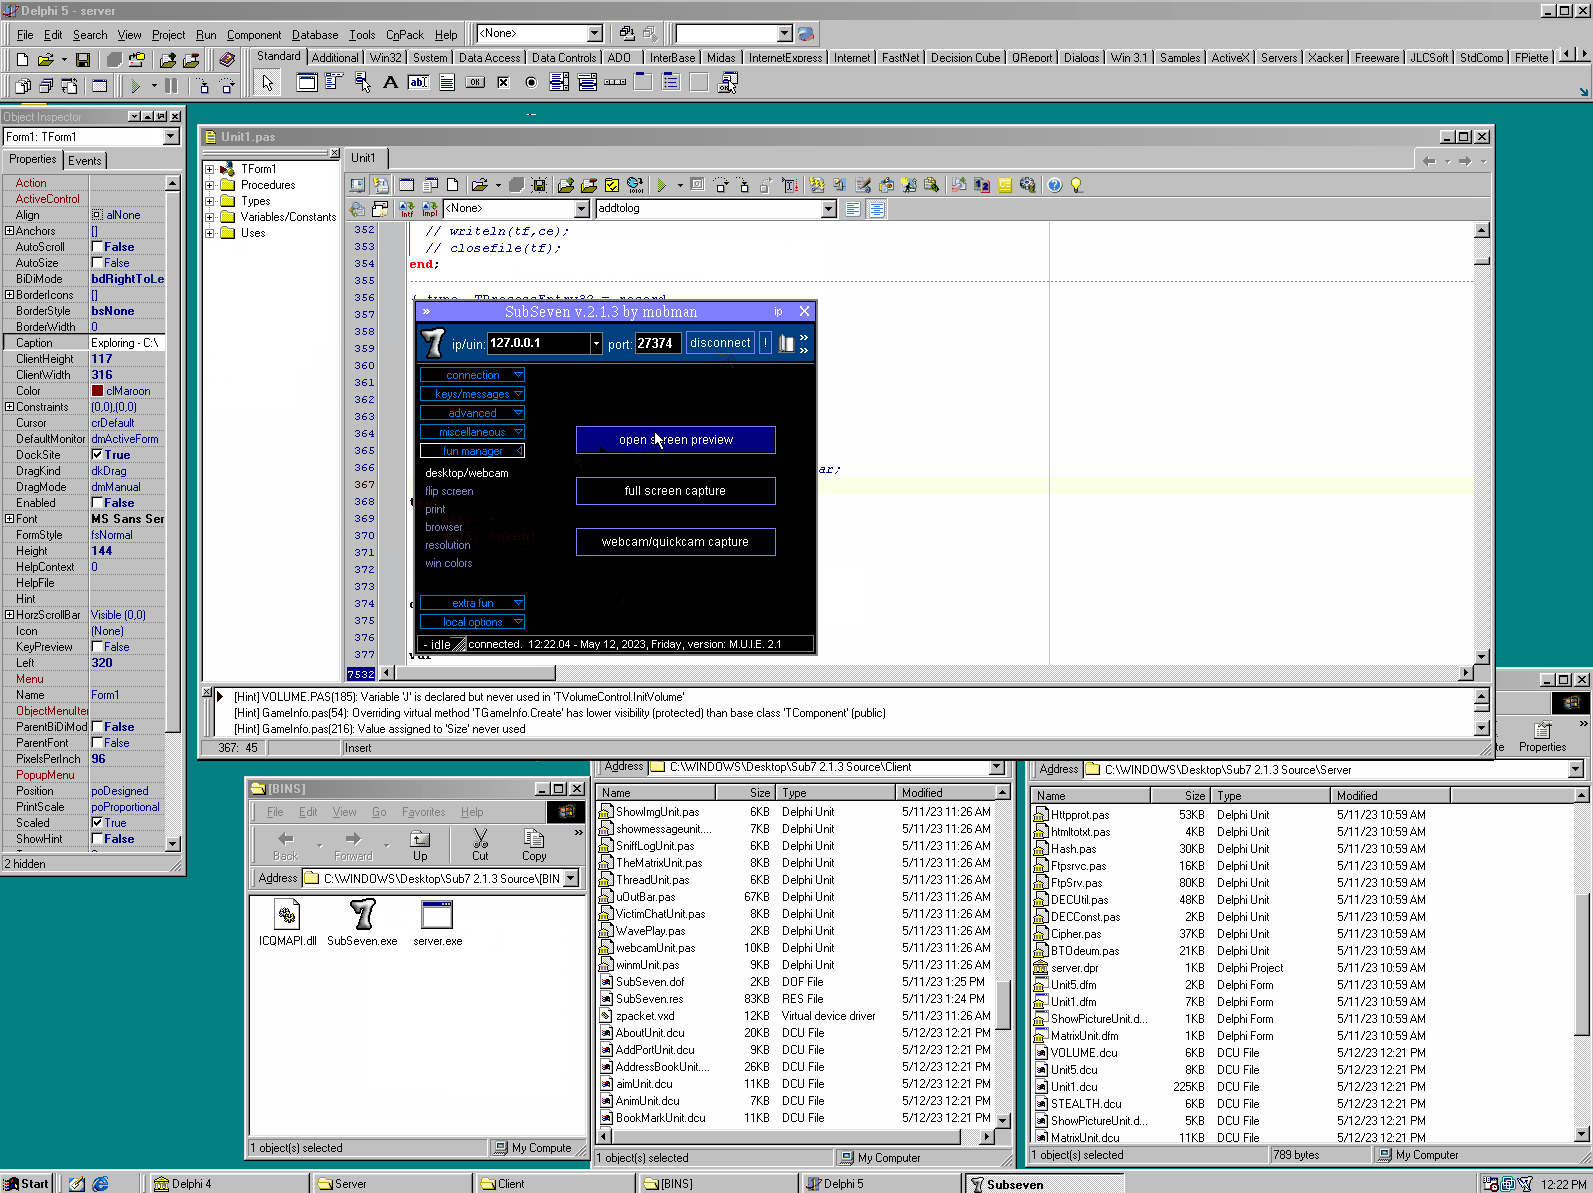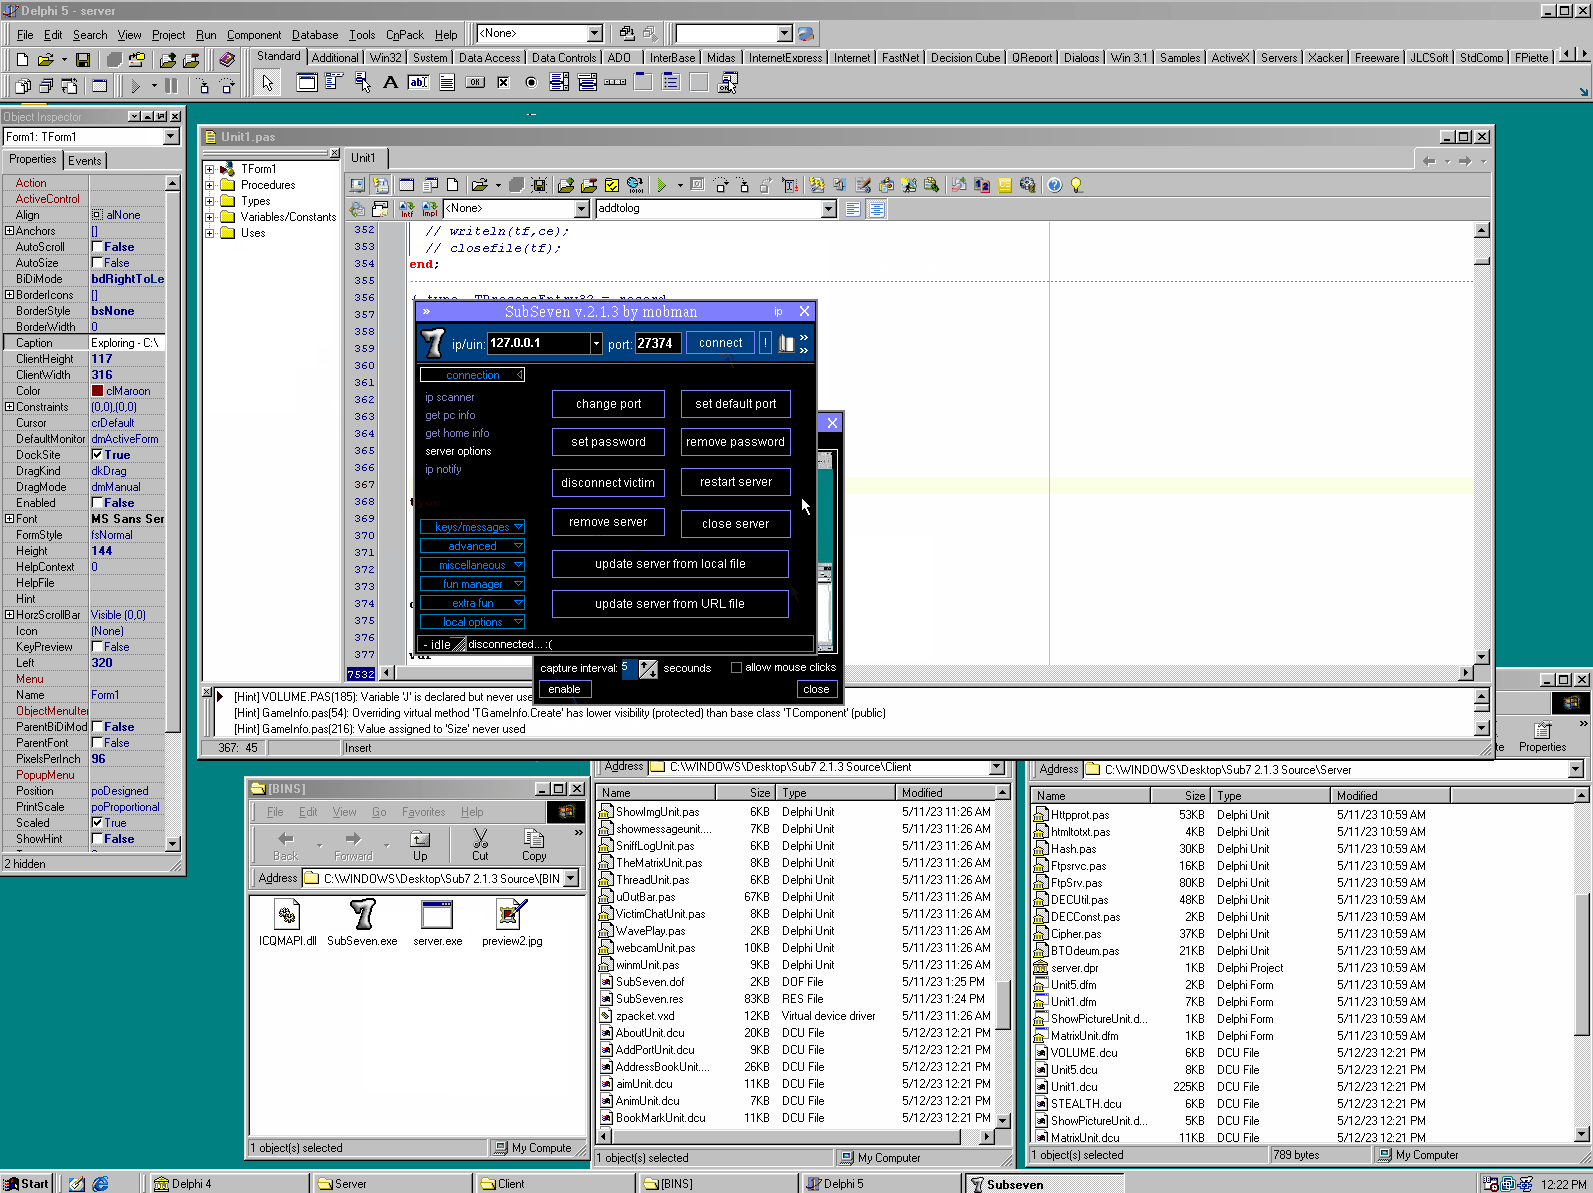
 illwill/sub7
Source code for SubSeven 2.1.3
 ilhomjonr/cve-2026-67595
CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.
 colocation/rockloader-source
RockLoader AKA Bart Malware control panel source
 x0rz/eqgrp_lost_in_translation
Decrypted content of odd.tar.xz.gpg, swift.tar.xz.gpg and windows.tar.xz.gpg
 azurit/modsecurity-backdoor
This is a proof-of-concept of malicious software running inside of ModSecurity WAF.
 corelight/pingback
A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 corelight/zeek-netsupport-detector
A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.
 corelight/zeek-spicy-facefish
A Zeek protocol analyzer for the Facefish rootkit, based on Spicy.
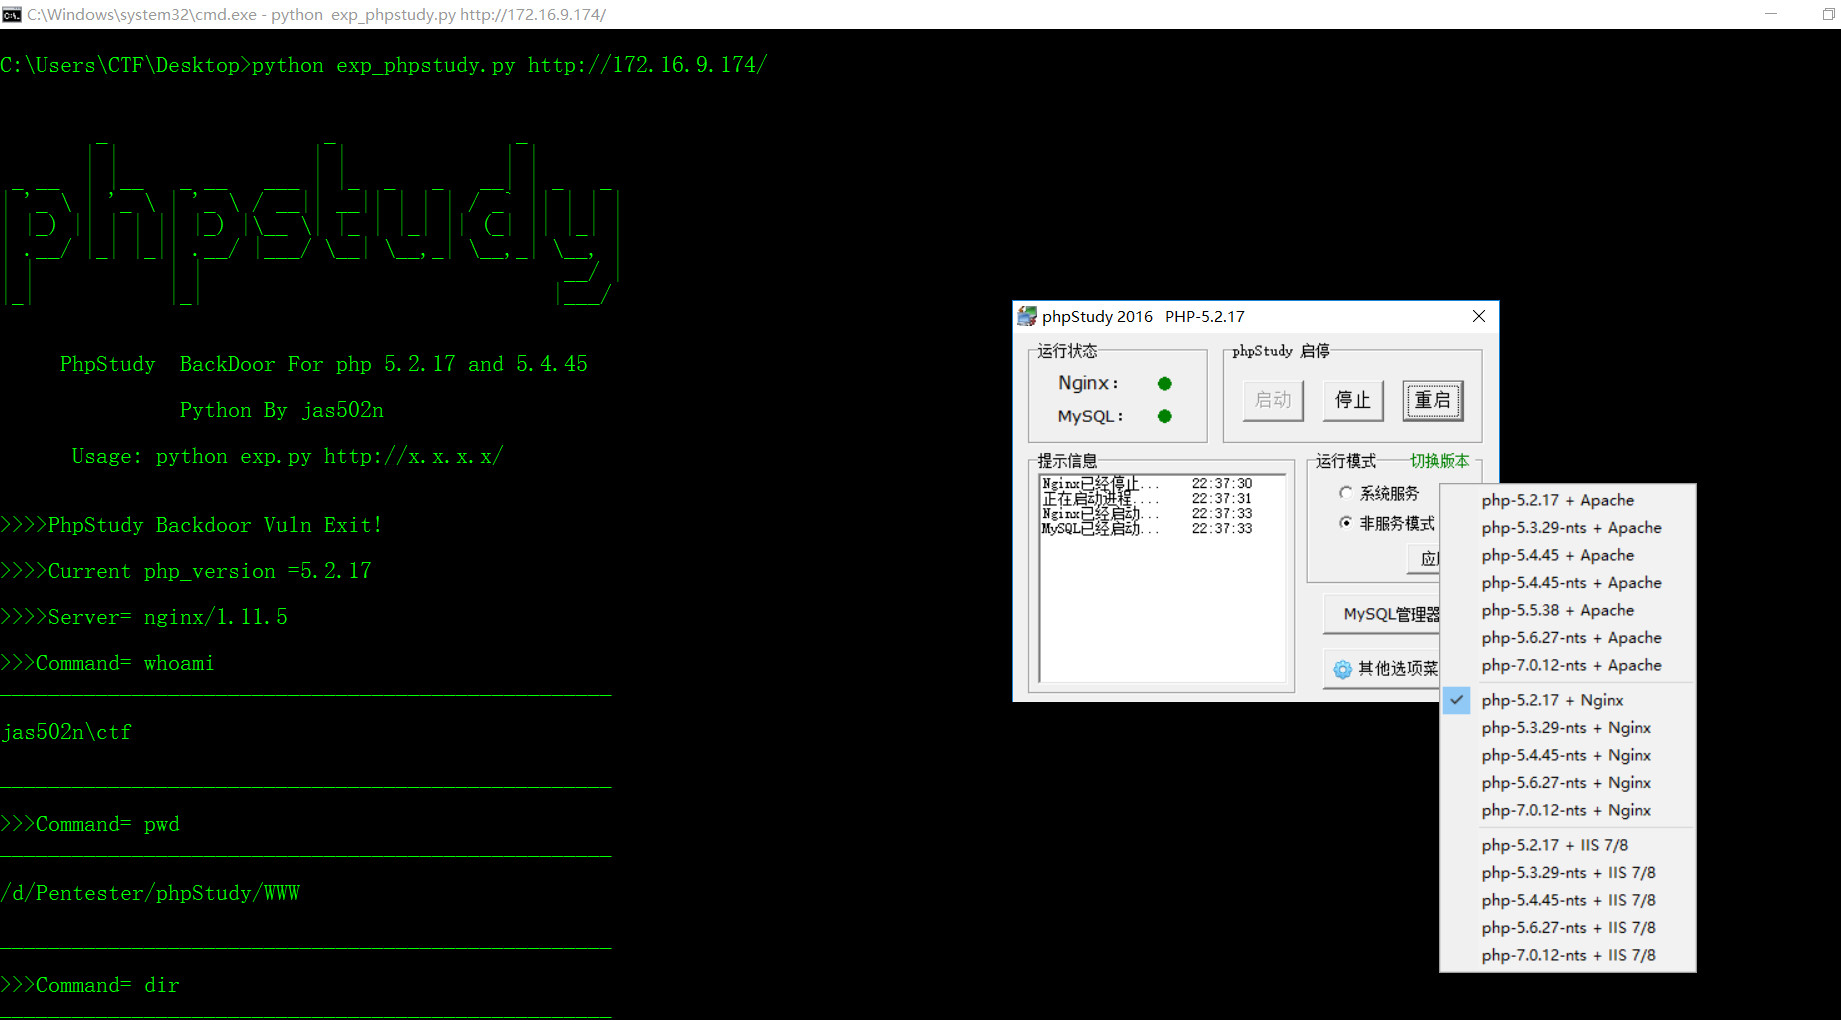 jas502n/phpstudy-backdoor
phpstudy dll backdoor for v2016 and v2018
 malwaremorghulis/sunburst
Detection for SUNBURST C2 Stage-1 using Shannon Entropy