Phantom-Evasion-Loader

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…

Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…

Command & Control-Framework created for collaboration in python3

Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻

A pure python, post-exploitation, remote administration tool (RAT) for macOS / OS X.

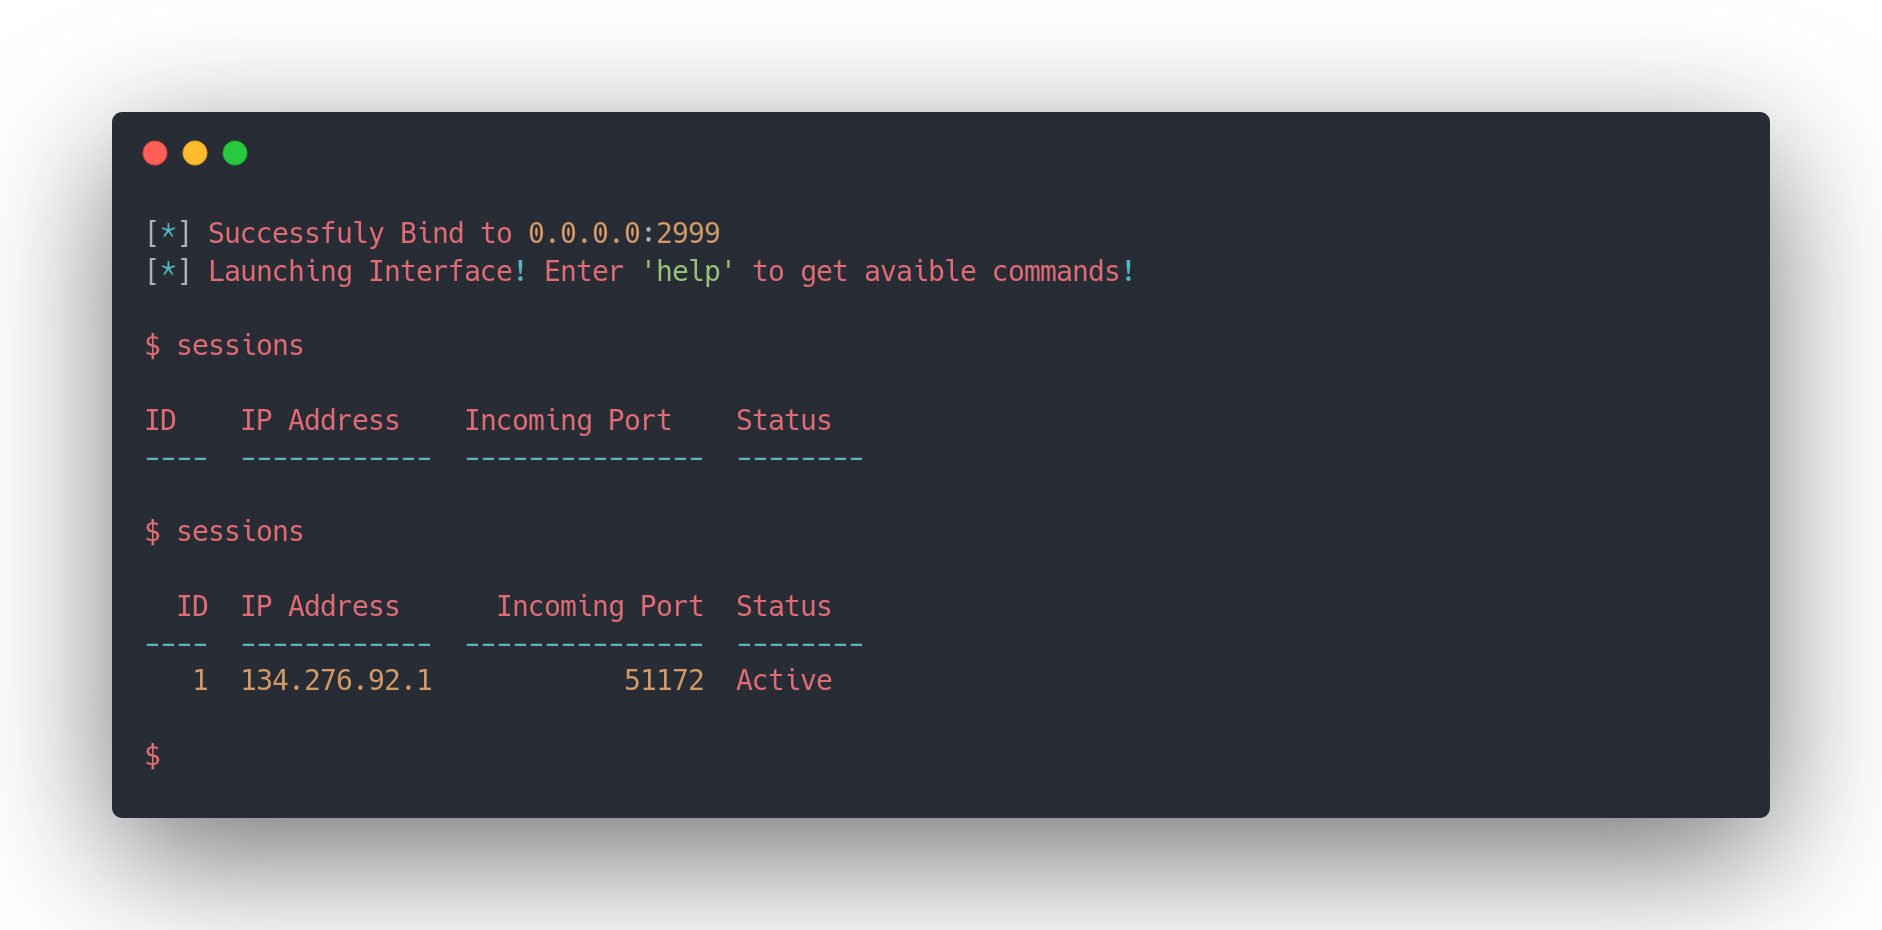
A Python based RAT 🐀 (Remote Access Trojan) for getting reverse shell 🖥️

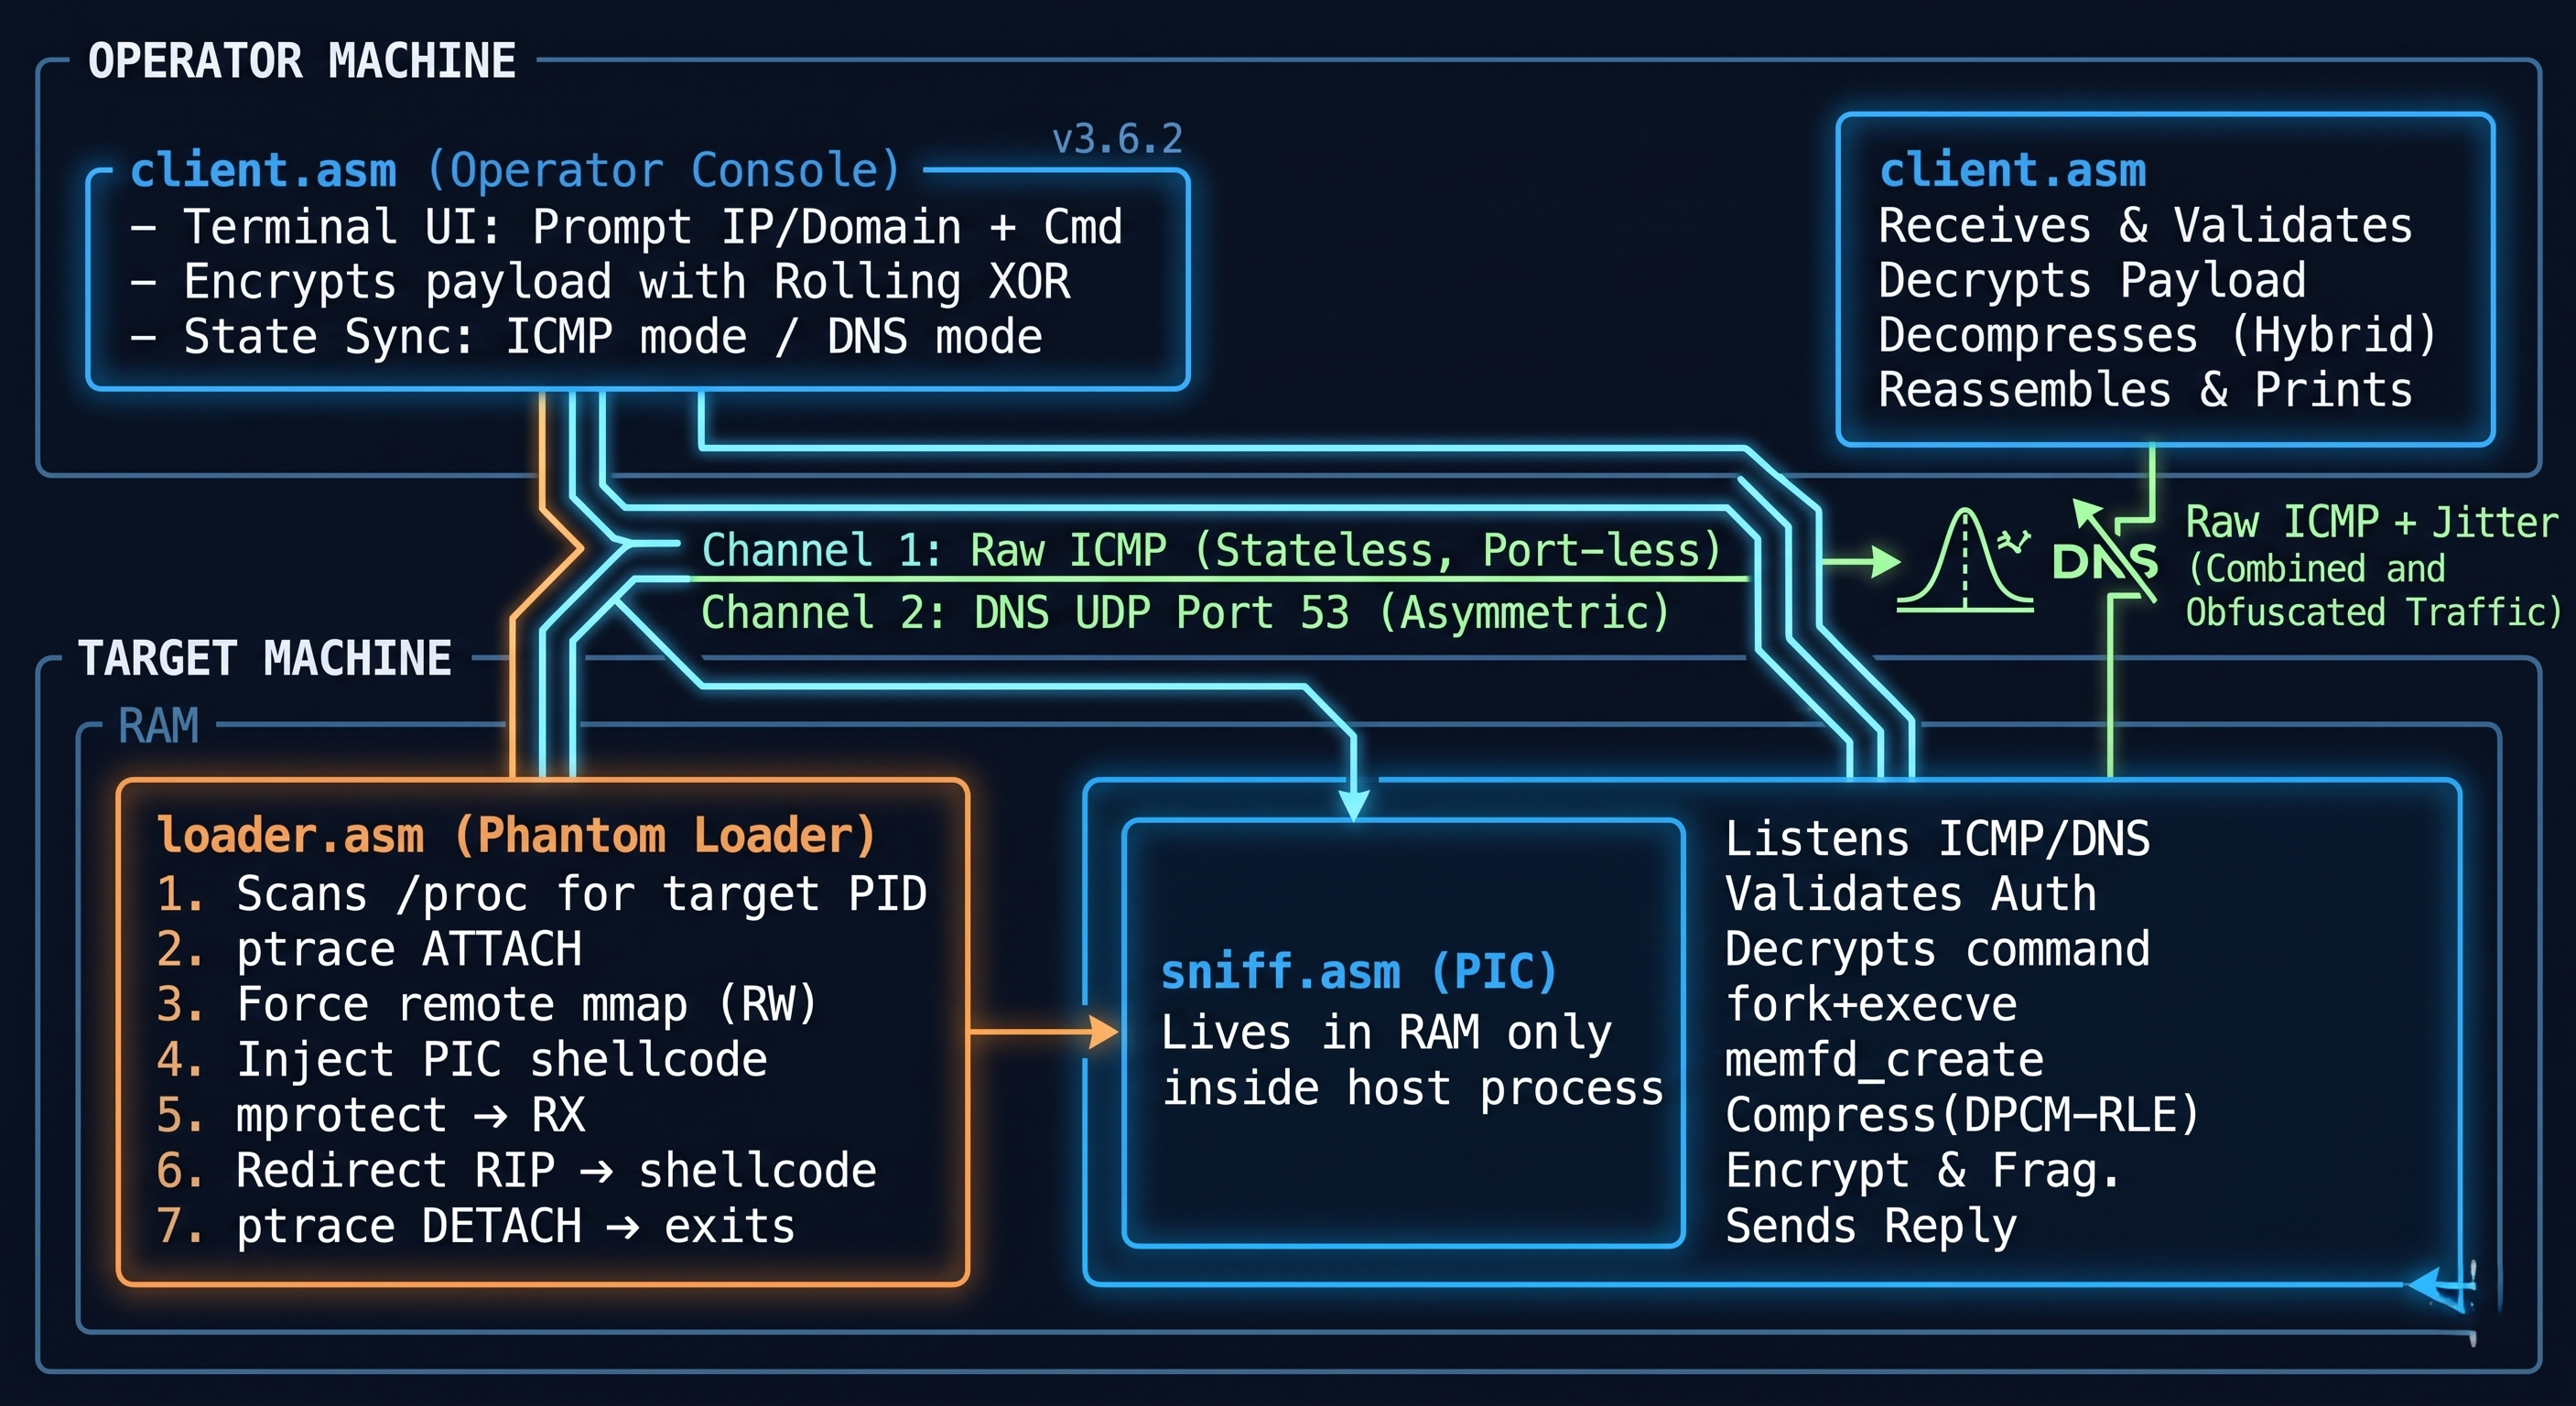
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

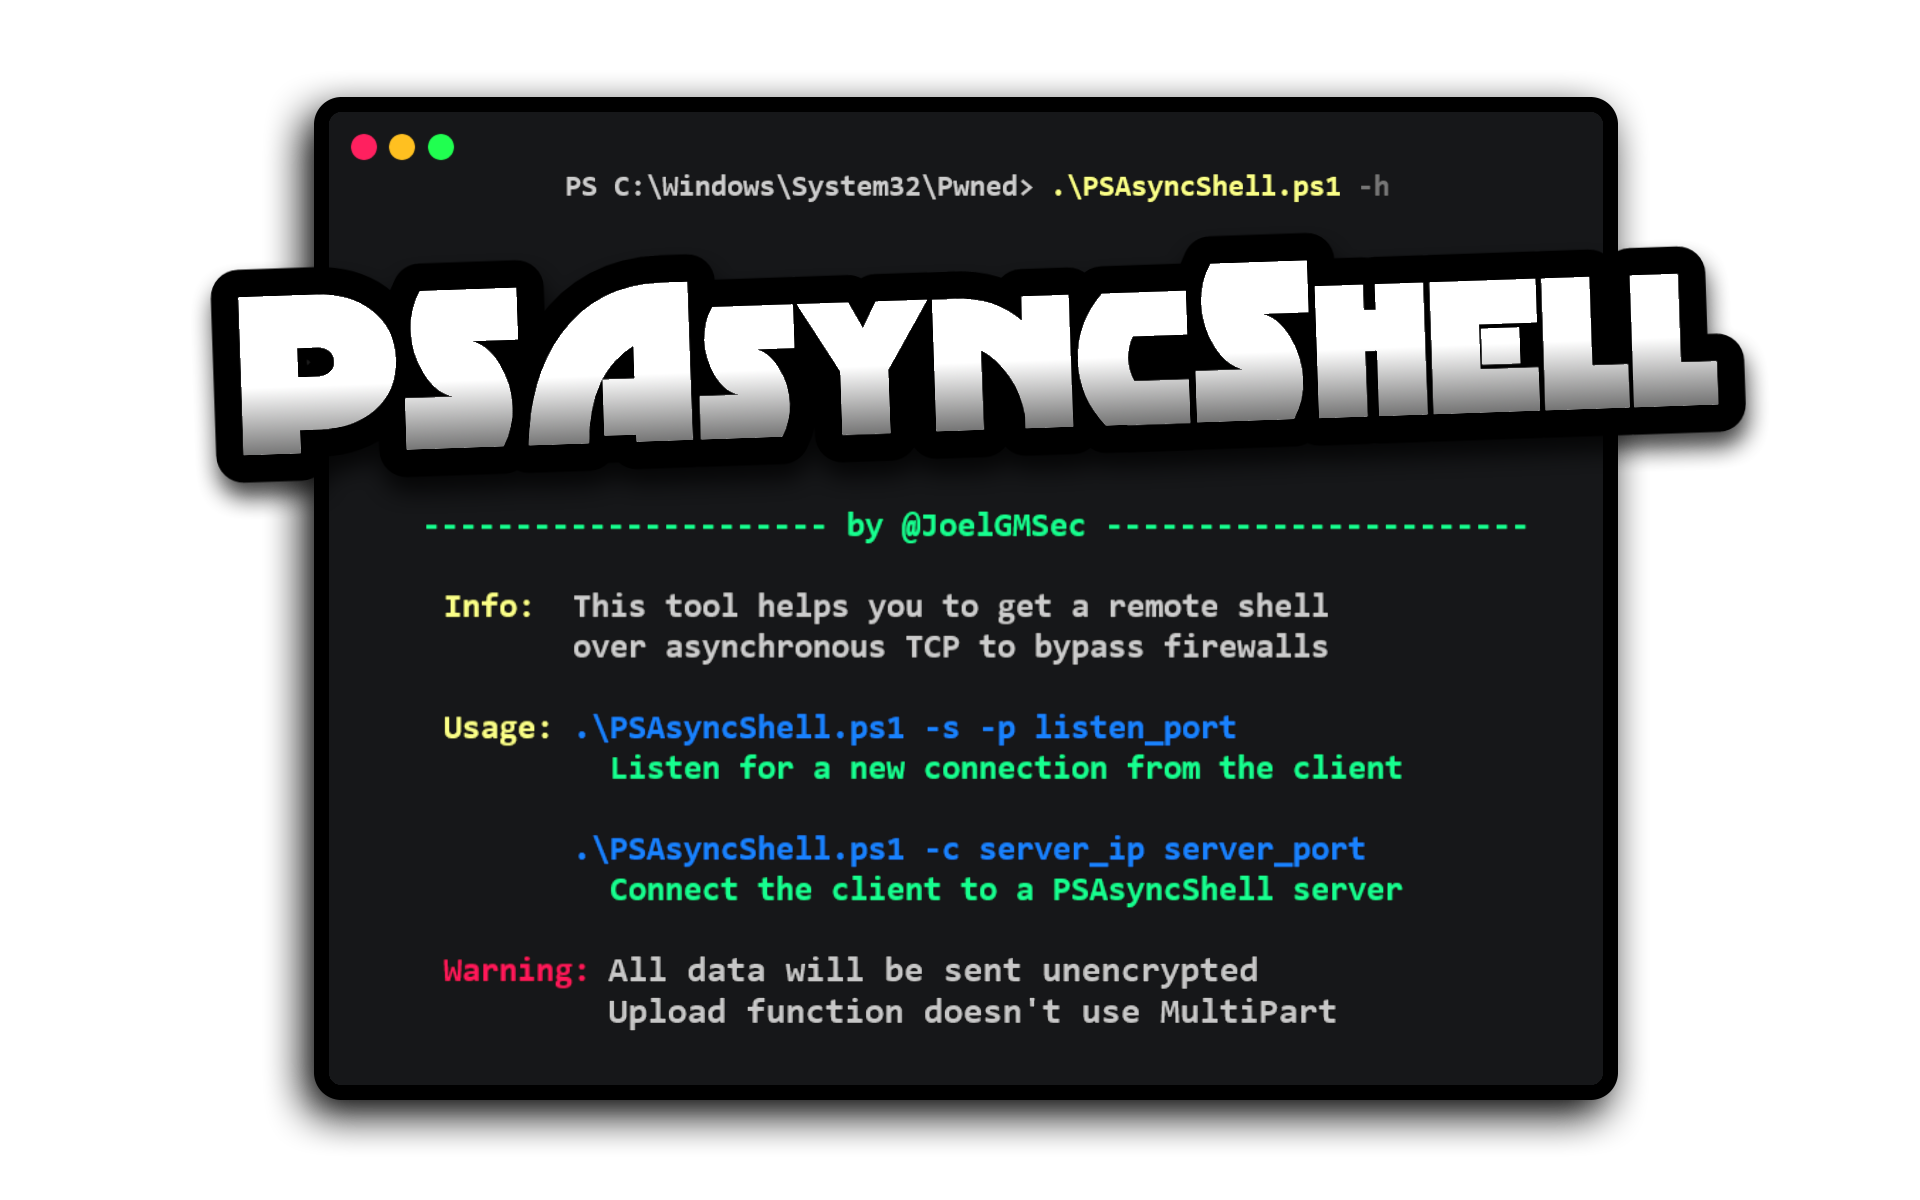
Asynchronous TCP reverse shell in pure PowerShell that bypasses firewalls via non-blocking I/O, with command history, file upload/download, and…

An All-In-One Pure Python PoC for CVE-2021-44228