Purple-Team-Automation

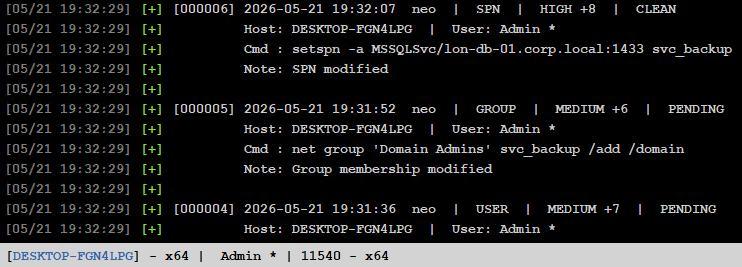
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.

An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…

Botnet command & control monitor

XZ-Utils工具库恶意后门植入漏洞(CVE-2024-3094)

Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles

Automated Adversary Emulation Platform

A collection of Tools and Rules for decoding Brute Ratel C4 badgers

Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…

A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks

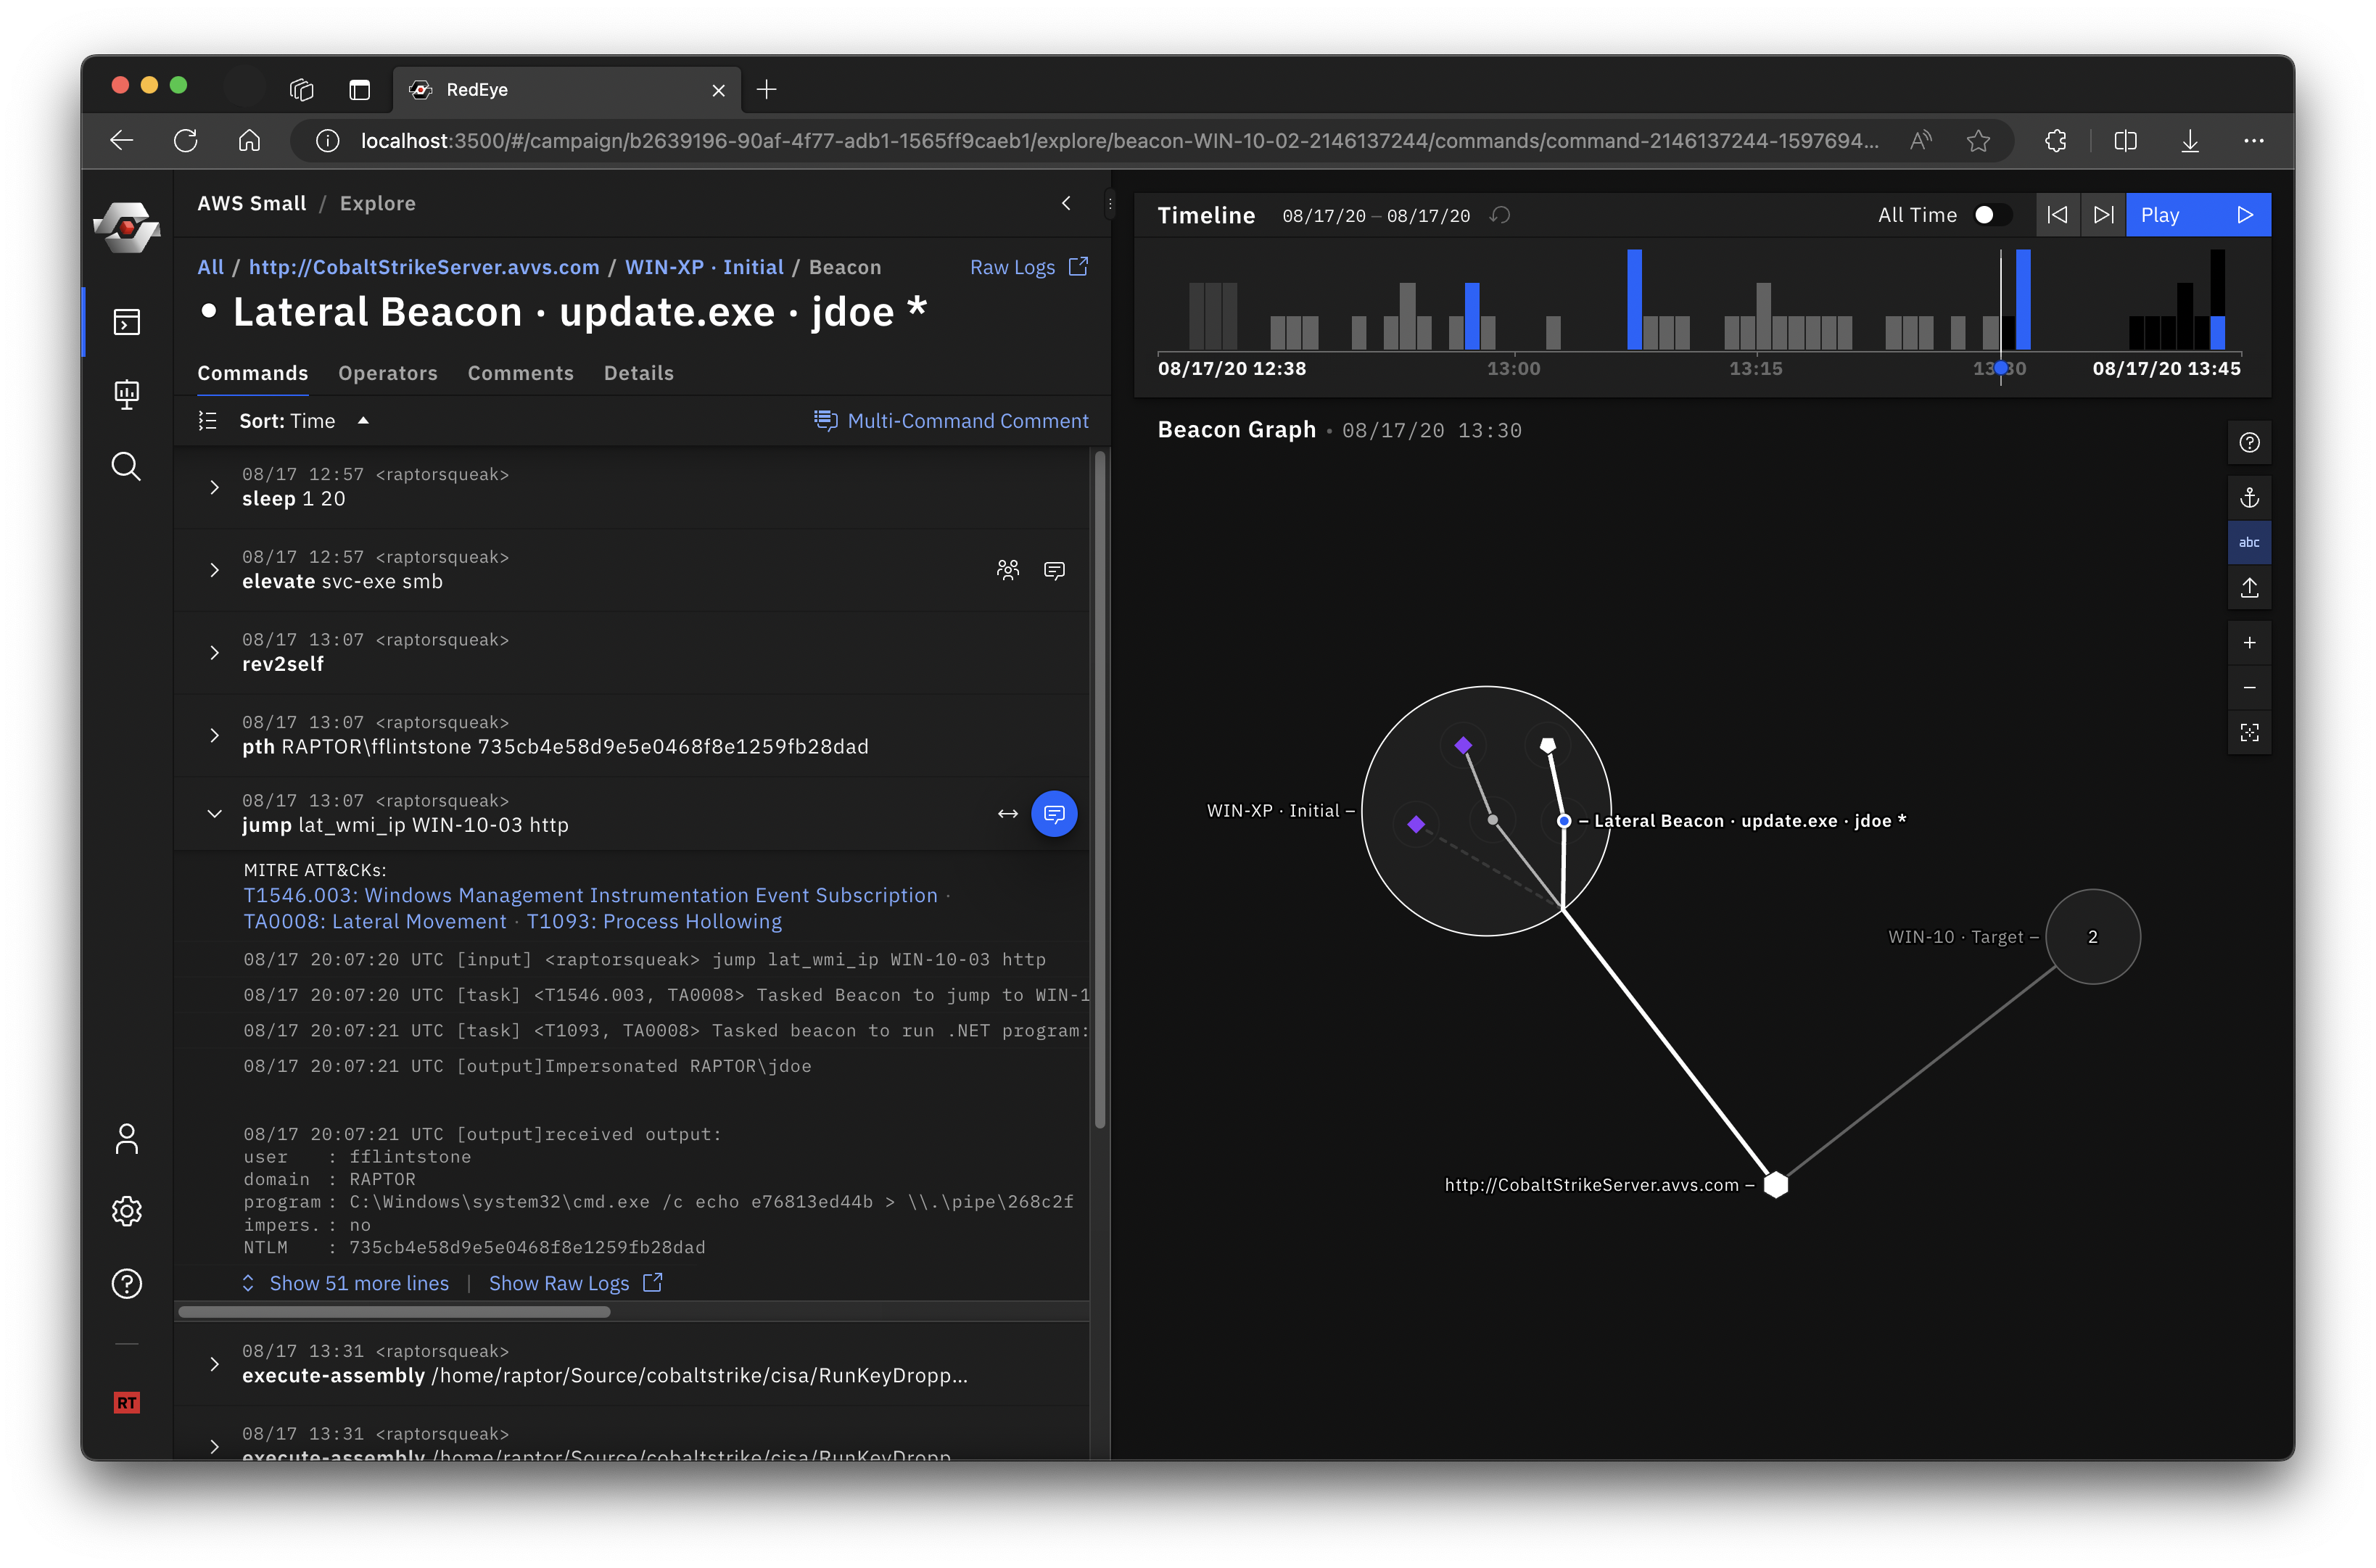
RedEye is a visual analytic tool supporting Red & Blue Team operations

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…

A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…

Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…

Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…

analyze a web-based network traffic 🕶 to detect central command and control servers

Parsing Ramnit's traffic